
FortiGate 3800G Series Tanzania
The FortiGate 3800G Series is a high-end next-generation firewall platform designed for data centers, large enterprises, service-provider networks and other environments where security inspection must keep pace with very high network capacity. Fortinet positions the FG-3800G in its high-end data-center firewall portfolio. For Tanzanian organizations evaluating a new core firewall, data-center security refresh, internet-edge consolidation or high-capacity segmentation project, the important question is not simply the headline firewall rate. Procurement teams should map real traffic, enabled security services, VPN demand, interface speeds, resilience requirements, rack and power design, logging, subscriptions and expected growth before selecting the final configuration.
FourTeck Tanzania can use those project inputs to help structure a product and quotation discussion. Buyers can start with the FourTeck Tanzania technology shop to understand related firewall, switching, server and infrastructure requirements, review broader IT and network services, or send the final requirement through the verified FourTeck Tanzania contact page.
Designed for demanding data-center and enterprise environments where inspection performance, interface density and scale are central design factors.
The FG-3800G provides 400GE, 200GE, 50GE and 10GE management connectivity, supporting modern high-bandwidth network designs.
FortiOS brings firewall, IPS, application control, VPN, segmentation and secure networking functions into one operating environment.
FortiGate 3800G Series overview
Fortinet’s current product matrix lists the FG-3800G with firewall throughput of 1.89/1.88/1.129 Tbps for 1518/512/64-byte UDP traffic, IPsec VPN throughput of 630 Gbps, IPS throughput of 675 Gbps using the enterprise mix, NGFW throughput of 550 Gbps, and threat-protection positioning at the high end of the FortiGate portfolio. These figures are vendor test results and should be interpreted using Fortinet’s published test conditions rather than treated as guaranteed application performance in every deployment. Real results depend on traffic profile, enabled services, packet sizes, policy complexity, encryption, software release and architecture.
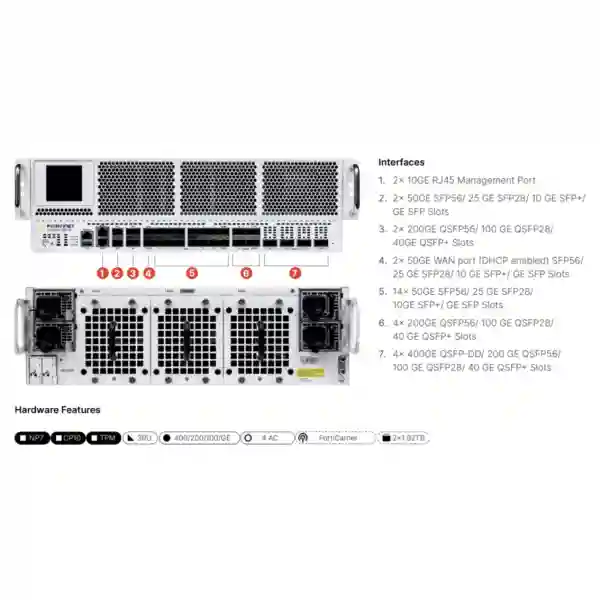
The interface configuration listed by Fortinet includes four 400GE ports, six 200GE QSFP56 ports, eighteen 50GE SFP56 ports and two 10GE RJ45 management ports. The appliance is a 3RU platform with four power supplies. Fortinet also lists the 3801G storage variant with two 1.92 TB local storage devices and a DC variant for deployments requiring that power option. This combination makes the series relevant when the firewall must sit inside a fast data-center fabric, aggregate multiple high-capacity links, segment east-west traffic, protect north-south internet or WAN flows, or support secure connectivity between sites and workloads.

Verified FG-3800G technical highlights
| Area | Fortinet-published value | Planning relevance |
|---|---|---|
| Firewall throughput | 1.89 / 1.88 / 1.129 Tbps | Useful baseline for very high-capacity packet forwarding; validate the security profile actually required. |
| IPsec VPN | 630 Gbps | Relevant to encrypted site, data-center and interconnect architectures. |
| IPS | 675 Gbps | Important when intrusion prevention is a major inspected-traffic requirement. |
| NGFW | 550 Gbps | A more useful sizing reference than raw firewall throughput for many security deployments. |
| Interfaces | 4×400GE, 6×200GE, 18×50GE, 2×10GE RJ45 management | Supports high-speed uplinks, aggregation and modern data-center fabrics. |
| Form factor | 3RU, four power supplies | Rack, cooling, power feeds and redundancy should be planned before ordering. |
What the FortiGate 3800G Series can solve
Large networks often reach a point where the security gateway becomes a design constraint. Faster internet circuits, private-cloud workloads, GPU clusters, virtualization, encrypted inter-site traffic and dense server fabrics can create inspection requirements far beyond a branch firewall. The 3800G is aimed at this higher tier. A deployment can be considered for data-center perimeter security, internal segmentation, high-capacity internet edges, large campus cores, service-provider security zones, hybrid-cloud connectivity and consolidated VPN termination. Fortinet introduced the platform as part of its Secure AI Data Center direction, highlighting ASIC acceleration and 400 GbE connectivity for demanding AI infrastructure.
That positioning does not mean every large organization automatically needs a 3800G. Correct sizing should compare peak and sustained traffic, security inspection profiles, TLS inspection requirements, session scale, VPN encryption, redundancy, interface types and future growth. A lower model may be more appropriate for some environments, while a high-growth or multi-tenant design may justify additional headroom. FourTeck’s role in the buying process is to turn those operational inputs into a clearer bill of materials and quotation request rather than treating one throughput number as the complete answer.
Integration, licensing and deployment planning
FortiGate deployments can combine firewall policy, application control, intrusion prevention, VPN and Secure SD-WAN with Fortinet’s wider security ecosystem. The exact FortiGuard services and FortiCare support level should be selected according to the organization’s threat-protection, support and lifecycle requirements. Procurement should confirm the precise hardware variant, support term and security-service bundle on the quotation. Subscriptions should never be assumed from the appliance name alone because bundle contents and service periods can differ.
Physical planning is equally important. A 3RU high-end firewall belongs in an environment with appropriate rack depth, cooling, power redundancy, optical modules, fiber types, upstream and downstream switching capacity and documented failover behavior. The high-speed ports only create value when the surrounding switching and optics support the intended rates. Network teams should document VLANs or VRFs, routing, HA topology, management access, logging destinations, IP addressing, VPN peers, security zones and migration sequencing before the change window.
For related regional Fortinet expertise, buyers can review the FourTeck Fortinet specialist portal for FortiGate, FortiGuard, VPN and Secure SD-WAN context. Organizations coordinating East African projects can also reference FourTeck Kenya when a deployment spans neighboring markets.
FortiGate 3800G Series Tanzania
For organizations in Tanzania, the FortiGate 3800G Series is most relevant where firewall design has moved beyond ordinary office-edge requirements into data-center, carrier-scale, high-capacity enterprise or multi-site aggregation territory. A Tanzanian bank, telecom environment, large public or private institution, cloud operator, hosting facility, industrial group or national enterprise may need to protect traffic that crosses several trust zones while maintaining substantial bandwidth. The buying process should therefore begin with an architecture worksheet rather than a simple request for a firewall price. Record internet and private-circuit capacity, data-center uplinks, east-west traffic, user and server segments, encrypted traffic, remote sites, public services, cloud connectivity and the security controls that will actually be enabled.
Power and infrastructure deserve special attention. The 3800G is a 3RU high-end appliance with four power supplies, so the rack design should account for redundant feeds, UPS strategy, cooling, cable routing and service access. High-speed 400GE, 200GE and 50GE interfaces also require deliberate optics and fiber planning. Confirm the transceiver type, link distance, switch compatibility and redundancy design rather than assuming that a port speed alone guarantees interoperability. For procurement, specify whether the requirement is the standard FG-3800G, a storage variant, a DC-powered variant or a service bundle, and identify the desired FortiCare and FortiGuard term.
A useful Tanzania quotation request should include the current firewall model, target topology, required high-availability arrangement, peak bandwidth, security profiles, VPN throughput, expected growth, interface quantities, optics, rack environment and subscription term. This gives the supplier enough information to distinguish between hardware cost, support, security services and deployment dependencies. It also reduces the risk of comparing quotations that appear similar but include different licensing or accessories. FourTeck Tanzania’s contact workflow specifically asks customers to describe users, devices and operating context so product selection can be discussed against the real environment.
FortiGate 3800G Series Dar es Salaam
Dar es Salaam organizations considering the FortiGate 3800G are likely to be planning a major security edge, data-center refresh, high-capacity headquarters, hosting environment or multi-site network rather than a conventional small-office firewall. In these projects, connectivity can arrive from several providers or private links, and the security platform may need to handle internet access, partner networks, branch VPNs, public applications and internal segmentation simultaneously. Design the firewall around traffic classes and trust boundaries. Identify which flows require deep inspection, which are encrypted, which must be isolated, and which services need predictable latency.
For a Dar es Salaam data center, interface mapping should be completed before the purchase order. The FG-3800G’s high-speed ports can connect to modern core and spine-leaf switching, but optics, breakout requirements, fiber standards and peer-device capabilities must match. High availability should be planned together with upstream routing so a firewall failover does not leave stale paths or create asymmetric traffic. Administrators should also define out-of-band management, centralized logging and change-control procedures. If the project is a migration from another FortiGate or firewall vendor, document objects, policies, NAT, routing, VPNs and dependencies before cutover.
Procurement teams in Dar es Salaam should request a quotation that separates appliance hardware, support, FortiGuard security subscriptions, optics and professional services. Ask for exact part references and subscription periods rather than comparing only total price. If the firewall will protect customer-facing or revenue-critical systems, include the required maintenance windows, rollback plan and acceptance tests in project planning. FourTeck Tanzania lists Dar es Salaam on its contact page, providing a direct path for customers to submit the technical requirement and request product guidance without assuming stock or delivery commitments that have not been confirmed.
FortiGate 3800G Series Mwanza
In Mwanza, the FortiGate 3800G Series can be evaluated for organizations whose security architecture serves a large regional operation, data-processing environment, critical enterprise hub or aggregation point for multiple branches. The first sizing question is whether the workload genuinely requires this high-end class. Measure current bandwidth and sessions, but also examine traffic growth, encrypted application use, backup replication, cloud connectivity and inter-site VPN demand. Security services such as IPS and application inspection change the relevant performance metric, so raw firewall throughput should not be the only figure used in the decision.
A regional hub may connect remote facilities over several WAN technologies. In that scenario, routing and resilience are as important as security policy. Document primary and backup paths, route preference, failover expectations and which applications must continue during a carrier outage. If Secure SD-WAN is part of the design, define application steering and health-check objectives before configuration. If the 3800G is used mainly for data-center segmentation, identify server groups, management networks, storage traffic and application dependencies so policy can be built around business flows instead of broad network ranges.
Mwanza procurement teams should also review the physical environment. High-end security equipment requires stable rack, power and cooling conditions, plus suitable high-speed transceivers and cabling. Include these dependencies in the bill of materials so the appliance does not arrive before the supporting infrastructure is ready. A complete request should state interface speeds, required quantities, redundancy, support term, security subscription, VPN needs and target deployment date. FourTeck Tanzania can use this information to structure a clearer quotation discussion while the buyer retains responsibility for validating final technical suitability against the approved network design.
FortiGate 3800G Series Arusha
Arusha enterprises assessing the FortiGate 3800G should focus on whether their environment combines high-capacity connectivity with demanding security inspection. Large hospitality groups, regional headquarters, institutions, service providers and organizations coordinating many remote sites may have complex traffic patterns, but complexity alone does not require the largest firewall. Establish an evidence-based sizing baseline: internet bandwidth, private WAN capacity, VPN encryption, concurrent sessions, inspected traffic, server publishing, remote access, segmentation and forecast growth. Compare those requirements with Fortinet’s published enterprise-mix figures and preserve reasonable design headroom.
For organizations with distributed locations, the firewall can form part of a broader secure networking architecture. Branch connectivity, centralized policy, VPN and SD-WAN should be designed with application behavior in mind. Voice, video, cloud applications, backups and business systems can have very different latency and bandwidth requirements. The central security device should not become a bottleneck because all traffic is forced through one path without architectural justification. Document which traffic must traverse the data center, which can break out locally, and which security controls are required at each boundary.
Before ordering in Arusha, confirm rack space, redundant power, cooling, optics and peer switch interfaces. If the design calls for 400GE or 200GE, validate the complete link from the FortiGate port through the transceiver and fiber to the connected switch. Licensing should be documented separately from hardware, with the exact FortiCare and FortiGuard term shown. FourTeck Tanzania’s verified contact page lists Arusha among its contact locations, so buyers can submit architecture and quotation details through the existing enquiry path while avoiding assumptions about inventory, lead time or installation scope until those items are explicitly confirmed.
FortiGate 3800G Series Dodoma
For Dodoma, a FortiGate 3800G project should be treated as an infrastructure decision with security, resilience and lifecycle implications. Large institutions and centralized environments may need to secure data-center workloads, public services, private applications and connections to many sites. Start by classifying systems and data flows. Determine which networks require isolation, where internet-facing services terminate, how administrators connect, which applications use encrypted traffic and what logs must be retained. This produces a policy architecture that can be sized and tested instead of a collection of firewall rules created after installation.
High availability deserves a complete design. Redundant firewalls are only one layer; upstream and downstream switching, routing, power and carrier paths must also avoid single points of failure. Define failover tests and acceptable interruption before deployment. The FG-3800G’s interface capacity is suited to large networks, but the surrounding infrastructure must be able to use it. Check rack and cooling requirements, four-power-supply feeds, optical modules, cable types and management access. Where local storage or a DC power option is needed, identify the exact variant in procurement documentation.
Dodoma buyers can improve quotation accuracy by providing a topology diagram, current and target bandwidth, interface schedule, HA requirement, FortiGuard service needs, FortiCare term, VPN count and migration expectations. Include any requirement for centralized management or analytics as a separate line item so it is not assumed to be part of the base appliance. The goal is a quotation that can be audited technically and commercially. FourTeck Tanzania lists Dodoma on its contact page and invites customers to describe their operational requirement, which is the appropriate starting point for a high-end firewall discussion.
FortiGate 3800G Series UAE
In the UAE, the FortiGate 3800G Series fits the requirements of large data centers, enterprises, service providers and organizations building high-throughput security architectures. Buyers in Dubai, Abu Dhabi and other emirates often operate dense cloud, colocation, campus and multi-site environments where 100GE-class and faster connectivity is increasingly relevant. The 3800G’s 400GE, 200GE and 50GE interface mix gives architects flexibility for core and data-center interconnects, but interface speed must be matched to the connected switching platform, optics and actual security throughput requirement.
A UAE procurement exercise should distinguish between the appliance, FortiCare support and FortiGuard security services. The exact bundle depends on the organization’s security controls and service period. For high-availability deployments, specify both nodes, optics, power requirements and any management or analytics platforms needed. If the firewall will secure AI or GPU infrastructure, map east-west workload flows, north-south internet traffic, management networks and data-access paths separately. Fortinet introduced the 3800G in the context of its Secure AI Data Center solution, but each project still requires its own architecture and security policy.
FourTeck maintains a dedicated Fortinet-focused UAE portal covering FortiGate firewalls, license renewal, Secure SD-WAN, VPN and related Fortinet solutions. That regional resource can support buyers comparing hardware, subscription and deployment requirements across UAE projects. A useful enquiry should include current firewall details, desired throughput under security inspection, interface quantities, routing design, VPN needs, subscription term and deployment timeline. Final availability, commercial terms and delivery scope should be confirmed in the quotation rather than inferred from general product information.
FortiGate 3800G Series Uganda
Ugandan organizations evaluating the FortiGate 3800G are generally looking at a high-end enterprise or data-center requirement. A national network, financial environment, telecom operation, hosting platform or large multi-site organization may need a firewall that can inspect substantial traffic while terminating VPNs and enforcing segmentation. Begin with the real workload: WAN and internet capacity, internal data-center flows, application publishing, branch connectivity, encrypted traffic and expected growth. Fortinet’s enterprise-mix IPS and NGFW figures are more relevant to many security deployments than the maximum raw firewall figure.
Regional projects often need resilient connectivity, so the design should include multiple carriers or paths where business requirements justify them. Document how routing changes during an outage and how sessions behave during firewall failover. If branches use IPsec, identify aggregate encrypted throughput and tunnel count. If the appliance sits in a data center, define server zones, management networks and public service segments. Central logging and administration should be part of the design from the beginning so security operations teams can investigate events and manage policy consistently.
Procurement in Uganda should specify exact hardware variant, AC or DC requirement where applicable, storage requirement, subscription package, support term, optics and deployment services. Do not assume that all bundles include the same security services. The FourTeck Uganda site provides a regional technology path for organizations coordinating wider IT and networking requirements, while FortiGate-specific technical selection should still be based on the approved architecture and current Fortinet documentation. Cross-border projects can align naming, policy standards and support terms while keeping local connectivity and infrastructure conditions explicit.
FortiGate 3800G Series Kampala
Kampala-based enterprises can consider the FortiGate 3800G when a central data center or headquarters must secure very high-capacity traffic, aggregate branch connectivity or provide segmentation between major application zones. The decision should be based on inspected throughput rather than organization size alone. A company with thousands of users may have modest internet traffic, while a smaller hosting or technology environment may move extremely large volumes between servers. Measure the flows that actually cross the firewall and determine which security profiles will apply to them.
If the Kampala site serves as a hub for branches, build a WAN and VPN inventory before sizing. Record each site, circuit capacity, encryption requirement, routing method, critical applications and backup path. This helps determine aggregate IPsec demand and whether traffic should be centralized or distributed. For data-center segmentation, identify application tiers and dependencies so policies can be specific without creating operational friction. High-speed interfaces should be mapped to redundant switching, with optics and fiber validated for both ends.
A purchase request should also cover lifecycle. Select the FortiCare level and FortiGuard services according to operational and security needs, and record renewal dates in the asset-management process. Include spare optics or maintenance strategy where the design requires them. Before cutover, test routing, HA, policy, VPN, logging and rollback procedures. Kampala buyers working through FourTeck can use the Uganda regional site for broader IT context and submit a structured requirement that makes the firewall quotation easier to compare on a like-for-like basis.
FortiGate 3800G Series Arua
For Arua, the FortiGate 3800G is appropriate only where the site or organization has a genuinely high-end security requirement. A regional facility may be part of a much larger national architecture, in which case the firewall could be deployed centrally rather than at every location. Architects should decide where inspection belongs: at the local edge, a central data center, or both. That choice affects WAN bandwidth, latency, resilience and the amount of traffic the 3800G must process.
Where connectivity is a major operational dependency, document primary and secondary links and the behavior expected when one path fails. Secure SD-WAN and IPsec can be part of the FortiGate architecture, but configuration should follow application priorities and security policy. If critical applications are hosted elsewhere, test failover with real application traffic rather than only verifying that a backup link comes online. The firewall’s capacity should leave room for security inspection and growth without creating an unnecessarily oversized local design.
Procurement teams should avoid ordering only the base appliance description. Confirm support, subscriptions, optics, rack requirements, power and any installation or migration work. If the 3800G will be installed at a central site serving Arua operations, clearly state that architecture in the request so interfaces and VPN capacity are sized correctly. A regional FourTeck enquiry can be coordinated through the Uganda technology site, while final product and licensing details should be confirmed against current Fortinet documentation and the formal quotation.
FortiGate 3800G Series Mbarara
Mbarara organizations planning a high-capacity security environment should evaluate the FortiGate 3800G against both present traffic and the architecture expected over the support lifecycle. A major enterprise hub can grow through new branches, cloud services, private circuits, data replication and additional security inspection. Build a three-to-five-year traffic forecast using known projects rather than an arbitrary percentage. Then compare the expected inspected traffic with vendor performance metrics and maintain engineering headroom for bursts and future policy changes.
The 3800G’s high-speed interfaces can simplify aggregation when the surrounding network uses compatible data-center switching. However, a 400GE port does not automatically improve an environment whose switches, optics or cabling operate at lower rates. Create an interface schedule that lists peer device, port speed, optic, fiber type, VLAN or routing role and redundancy. This becomes useful for both procurement and installation. Also identify management and logging connections so operational access is not improvised during deployment.
For a multi-site organization serving Mbarara, VPN and routing design should be reviewed alongside firewall policy. Define whether branches connect directly to the central firewall, through regional hubs, or through cloud security services. Procurement should list FortiCare, FortiGuard and any centralized management components separately, because lifecycle services can represent a significant part of the overall solution. FourTeck’s Uganda presence can provide a regional enquiry route, but stock, delivery, installation scope and final commercial terms should be verified for the specific project.
FortiGate 3800G Series Gulu
In Gulu, a FortiGate 3800G requirement may arise as part of a national enterprise, institutional network, service-provider design or centralized security architecture. The key is to distinguish the needs of the Gulu site from the needs of the whole organization. If traffic is backhauled to a central data center, the 3800G may belong at that central location. If the Gulu facility itself hosts major applications or aggregates regional connectivity, local deployment may be justified. Architecture should determine placement before procurement determines quantity.
Security policy design should classify users, servers, public services, management systems and partner connections into clear zones. This reduces broad trust and makes high-capacity segmentation useful. For encrypted traffic, decide where TLS inspection is appropriate and account for its performance and privacy implications. For IPsec, document peers, algorithms and aggregate throughput. Logging requirements should identify retention, analytics and incident-response workflows so the firewall produces data that security teams can actually use.
Gulu buyers should also consider operational readiness. A high-end firewall needs documented configuration ownership, firmware management, backup, monitoring and renewal processes. Hardware alone does not provide a complete security outcome. The quotation should therefore make support and subscriptions explicit, together with optics, power, rack and migration dependencies. Organizations coordinating Gulu and other Ugandan locations can use FourTeck Uganda as a regional technology reference and align the firewall project with the wider network plan.
FortiGate 3800G Series Kenya
Kenyan enterprises and data-center operators evaluating the FortiGate 3800G can use it as a candidate for high-throughput perimeter security, internal segmentation, VPN aggregation and hybrid infrastructure. Nairobi and other major business centers increasingly combine cloud, colocation, private WAN and internet services, which makes traffic mapping essential. Determine which flows must cross the firewall and what security functions apply. A high-capacity link does not mean all traffic requires the same inspection profile, and an efficient architecture separates requirements rather than enabling every control indiscriminately.
For data centers, the interface mix is a major design consideration. Four 400GE ports, six 200GE ports and eighteen 50GE ports provide substantial connectivity options, but procurement should include compatible optics and peer-switch validation. HA design should account for switch redundancy, routing convergence and power diversity. Where the firewall protects public applications, include DDoS architecture, load balancing and upstream provider controls in the broader security review even when those functions are delivered by separate platforms.
Kenya buyers should request exact Fortinet part references and subscription terms. Compare quotations based on hardware, FortiCare, FortiGuard services, optics and professional services rather than total cost alone. FourTeck Kenya provides a regional IT and network-security portal that can support broader project discussions. For multi-country East African environments, standardizing policy and management can simplify operations, but bandwidth, carrier design, regulatory requirements and site infrastructure should still be assessed country by country.
FortiGate 3800G Series Kuwait
Kuwait organizations considering the FortiGate 3800G are typically planning a data-center, high-end enterprise, government-scale or service-provider security environment. High-capacity circuits and dense server infrastructure can make inspection throughput and interface speed central to the design. Use the Fortinet-published NGFW, IPS and IPsec figures as sizing references under their documented test conditions, then compare them with the real traffic mix. Include encrypted applications, east-west data-center traffic, backups and disaster-recovery replication when estimating load.
The physical deployment should be treated as data-center infrastructure. Confirm 3RU rack space, redundant power feeds, cooling, optical modules and fiber routes. If a DC-powered variant is required, identify it explicitly. If local storage is required for the selected design, verify the appropriate variant. High availability should include routing and switching behavior on both sides of the firewall so the redundant appliance pair is not undermined by a single upstream component.
Kuwait procurement teams should separate the security subscription from the hardware lifecycle and confirm renewal terms before approval. Define whether centralized management, analytics or managed services are part of the project. FourTeck Kuwait provides a regional IT, networking and cybersecurity destination for organizations planning business infrastructure in the country. A detailed requirement containing topology, throughput, interface, HA, VPN and licensing information will produce a more useful quotation than a request based only on model name.
FortiGate 3800G Series Ghana
In Ghana, the FortiGate 3800G can serve organizations that need a high-end firewall for large data centers, national enterprise networks, hosting, financial infrastructure or substantial VPN aggregation. The model should be evaluated in context. If the primary requirement is a moderate office internet edge, a smaller FortiGate may provide a better fit. If the organization must inspect hundreds of gigabits, connect high-speed core switches or segment large server environments, the 3800G’s performance class becomes more relevant.
A Ghana data-center design should document north-south and east-west traffic separately. Internet-facing application traffic, user internet access, replication, storage, management and backup flows have different security and performance characteristics. Define zones and policies before selecting interfaces. For VPN, include remote sites and disaster-recovery connectivity. For HA, validate carrier, switching, routing, power and rack redundancy. These details determine whether the architecture is resilient as a whole rather than merely containing two firewall appliances.
Commercial evaluation should identify exact hardware, support and security subscriptions, plus optics and deployment scope. Do not assume advertised reseller prices in other countries apply to Ghana; request a project-specific quotation. FourTeck’s Ghana regional site covers integrated IT, networking, servers and firewall requirements and can provide a useful route for broader infrastructure discussions. The final FortiGate design should still be validated against current Fortinet documentation and the organization’s approved security architecture.
FortiGate 3800G Series Nigeria
Nigeria’s large enterprise, telecom, financial, cloud and data-center environments can generate the scale where a FortiGate 3800G becomes a realistic candidate. A Lagos or national data-center edge may combine multiple high-capacity carriers, private WAN links, cloud connections and extensive internal segmentation. The architecture should define which traffic is inspected by IPS or other NGFW services, how encrypted sessions are handled, and where VPN termination occurs. This creates a defensible sizing model and helps avoid both under-sizing and unnecessary capacity.
The interface configuration supports modern high-speed switching fabrics, but optics and compatibility require explicit validation. Build a port map for 400GE, 200GE, 50GE and management connections, including peer switch and redundancy. For high availability, test routing convergence and application behavior during failover. Large environments should also establish configuration backup, change control, centralized logging and firmware governance before production deployment. Security performance is only one part of operating a high-end firewall reliably.
Nigeria procurement teams should compare subscription bundles carefully. FortiCare and FortiGuard services have different roles, and the desired term should be shown on the quotation. If the project includes centralized management or analytics, list those components separately. FourTeck Nigeria provides a regional IT-services presence for broader networking and cybersecurity discussions. Availability, price, import or delivery conditions and professional-service scope should be confirmed for the specific transaction rather than inferred from another market.
FortiGate 3800G Series Seychelles
Seychelles organizations evaluating the FortiGate 3800G should first determine whether their workload requires a high-end data-center firewall or whether a smaller platform would provide a more proportionate design. A telecom, hosting, government, financial or regional infrastructure environment may justify substantial capacity, particularly when multiple services, VPNs and security zones converge. Sizing should be based on inspected throughput, encrypted traffic and growth rather than internet bandwidth alone.
Because island connectivity and infrastructure resilience can be operationally important, WAN design should include primary and backup paths, routing behavior and application priorities. If the firewall terminates inter-island or international VPNs, aggregate encrypted throughput should be measured. Data-center deployments should document server segmentation, public services, management access and logging. The 3800G’s high-speed interfaces can support dense network fabrics, but connected switches, optics and fiber must be selected as one system.
Procurement should include the exact FortiGate variant, FortiCare, FortiGuard services, optics, rack and power requirements, and any migration or configuration work. For remote or cross-border support models, clarify responsibilities, response expectations and escalation paths before purchase. The quotation should state what is included rather than relying on assumptions. This disciplined approach is especially useful for a high-value platform whose lifecycle cost includes support and security subscriptions as well as the appliance itself.
FortiGate 3800G buying and sizing checklist
Record peak traffic, inspected traffic, application mix, TLS inspection, IPS, VPN, public services, session demand and growth. Use the performance metric that matches the intended security profile.
List port speeds, optics, fiber, peer switches, HA topology, routing, power feeds, rack space and cooling. Validate both ends of every high-speed connection.
Specify FortiCare, FortiGuard services, term length, management, analytics, renewal ownership, firmware process and operational support expectations.
FortiGate 3800G Series FAQs
What is the FortiGate 3800G Series designed for?
Fortinet positions the FG-3800G as a high-end data-center next-generation firewall. It is relevant to large enterprise, data-center, service-provider and other high-throughput environments requiring substantial security inspection and high-speed interfaces.
What firewall throughput does Fortinet publish for the FG-3800G?
Fortinet’s product matrix lists 1.89/1.88/1.129 Tbps for 1518/512/64-byte UDP firewall throughput. Real deployment performance depends on traffic and enabled security services, so NGFW and IPS figures should also be considered.
Does the FortiGate 3800G support 400GE?
Yes. Fortinet lists four 400GE interfaces, alongside six 200GE QSFP56 and eighteen 50GE SFP56 interfaces, plus 10GE RJ45 management connectivity.
How should a Tanzania buyer request a FortiGate 3800G quotation?
Provide topology, current and target bandwidth, security services, VPN demand, HA requirement, interface and optics needs, power option, subscription term and deployment expectations. This helps ensure the quotation reflects the intended architecture.
Is FortiGuard included automatically?
Do not assume a particular FortiGuard package from the appliance name alone. Fortinet offers different bundles and service terms. Confirm the exact services and duration on the formal quotation.
Quotation checklist and decision recap
Before requesting a FortiGate 3800G Series quote, prepare the required appliance variant, quantity, HA design, expected inspected throughput, VPN requirement, interface schedule, optics, rack and power environment, FortiCare level, FortiGuard services, subscription period, management and logging requirements, migration scope and target deployment date. The FG-3800G is a high-end platform; its value comes from matching substantial security and connectivity requirements, not simply selecting the largest headline throughput. A well-documented architecture lets technical and procurement teams compare proposals consistently and identify missing dependencies before purchase.
For Tanzania projects, use FourTeck’s verified enquiry channel to share the requirement and request product selection or quotation guidance. No stock, delivery time, price, warranty scope or service coverage should be assumed until it is stated in the project-specific offer.




Reviews
There are no reviews yet.