
Fortinet Firewall Support Services
FourTeck provides Fortinet firewall support services for organizations that need help keeping FortiGate environments secure, understandable and operational. The service can address configuration troubleshooting, firewall policy changes, VPN faults, internet failover, routing, network segmentation, security-profile review, firmware planning, backup and documentation, FortiGuard subscription questions, FortiCare entitlement guidance and migration preparation.
A support engagement begins by separating the immediate technical problem from the wider lifecycle requirement. A blocked business application may be a policy or NAT issue. Slow internet can be related to inspection settings, routing or link conditions. A failed VPN may involve peer settings, certificates, proposals, routing or an ISP change. An expired security service is different again: the firewall may still pass traffic, while specific FortiGuard protections and vendor support entitlements depend on the active subscription or support contract. Clear diagnosis prevents unnecessary configuration changes.

Investigate connectivity, blocked applications, policy behavior, NAT, DNS, routing, VPN and performance symptoms before changing production rules.
Plan controlled changes for interfaces, zones, VLANs, objects, security policies, site-to-site VPN, remote access, SD-WAN and administrative access.
Review firmware, backups, licensing, FortiCare, FortiGuard, renewal timing, hardware age, growth and migration requirements.
Support branch connectivity, policy consistency, VPN standards, segmentation and change documentation across distributed networks.
What Fortinet firewall support should cover
A FortiGate is both a network gateway and a security enforcement point. Support therefore needs to protect business continuity while preserving the security intent of the configuration. The first objective is to understand traffic flow: which source needs to reach which destination, over which interface or tunnel, using which service, and under which security policy. From there, troubleshooting can examine routing, policy order, address objects, NAT, DNS, session behavior, inspection profiles and upstream dependencies instead of relying on trial-and-error rule changes.
Operational support commonly includes internet access faults, failed or unstable IPsec VPN tunnels, remote-access problems, duplicate or conflicting firewall rules, port-forwarding questions, VLAN reachability, high-availability checks, WAN failover, SD-WAN steering, application access, web filtering, certificate warnings, administrative access and log review. Not every issue originates on the firewall. A structured support process also checks ISP handoff, switching, endpoint settings, server reachability and name resolution so the firewall is not changed when the fault sits elsewhere.
For a broader view of how FourTeck connects firewall work with switching, Wi-Fi, servers and other infrastructure, review the FourTeck Tanzania technology services page. That page is useful when a FortiGate issue is really part of a wider network design, because firewall performance and policy behavior often depend on the LAN, WAN, addressing plan and applications around it.
FortiCare, FortiGuard and configuration support are different things
Fortinet separates vendor technical support from its security services. FortiCare is the Fortinet support family, while FortiGuard provides security services and threat intelligence used by FortiGate and other Fortinet products. Current Fortinet information shows FortiCare Premium as the support level included with FortiGate security bundles and FortiCare Elite as an upgrade option. Fortinet lists web and telephone support, firmware updates, asset-management access and hardware replacement benefits within those support offerings, with different response objectives by tier. Exact eligibility always depends on the registered device, contract, region and active entitlement.
FortiGuard subscriptions enable specific security functions and updates. Depending on the selected bundle or individual service, this can include capabilities such as intrusion prevention, antivirus, web and DNS security, application control, sandbox-related protection and other FortiGuard services. The correct bundle should be checked against the FortiGate model, business security requirement and renewal record; it should not be guessed from an old invoice or another device in the same company.
Before requesting a renewal quotation, collect the FortiGate model, serial number, current contract or bundle if known, expiry date, required term and whether the organization needs only vendor entitlement renewal or also configuration assistance. This prevents a licensing request from being mixed with an engineering scope.
FourTeck can help organize this information and distinguish procurement from engineering. For a current product example, the FortiGate 30G Tanzania product page shows how hardware selection, FortiCare, FortiGuard services and deployment questions need to be considered together rather than treated as one generic “firewall license.”
Common FortiGate support requests
Trace intended traffic, review rule order, objects, services, schedules, NAT and security profiles, then make the smallest controlled change needed.
Check phase settings, peer addresses, proposals, selectors, routing, policies, NAT exclusions and link reachability for site-to-site tunnels.
Review the supported remote-access method, user authentication, certificates, address pools, split routing and access policy with least-privilege goals.
Investigate health checks, link priorities, steering rules, route behavior, failover expectations and application sensitivity before changing path logic.
Review the current release, supported upgrade path, configuration backup, known dependencies, maintenance window and rollback considerations.
Align IPS, antivirus, application control, web filtering and inspection choices with active subscriptions, traffic patterns and performance needs.
Maintain recoverable configuration copies and a concise record of interfaces, WAN details, VLANs, VPN peers, public services and administrative access.
Identify live rules and dependencies, remove obsolete objects, map interfaces, plan cutover testing and preserve a workable rollback path.
A disciplined support process
Firewall troubleshooting is safest when every change has a reason, an expected result and a recovery path. Start by describing the business impact and the last known working state. Record the FortiGate model, FortiOS version, WAN topology, affected users or sites, recent changes and the exact traffic that is failing. Back up the configuration before material changes and preserve logs or screenshots that may help explain the fault.
Who or what is affected, and what still works?
Model, FortiOS, topology, configuration backup and relevant logs.
Routing, policy, NAT, tunnel and security-profile behavior.
Modify only what the evidence supports, then retest.
Record the fix, dependencies and any follow-up action.
VPN and secure remote access support
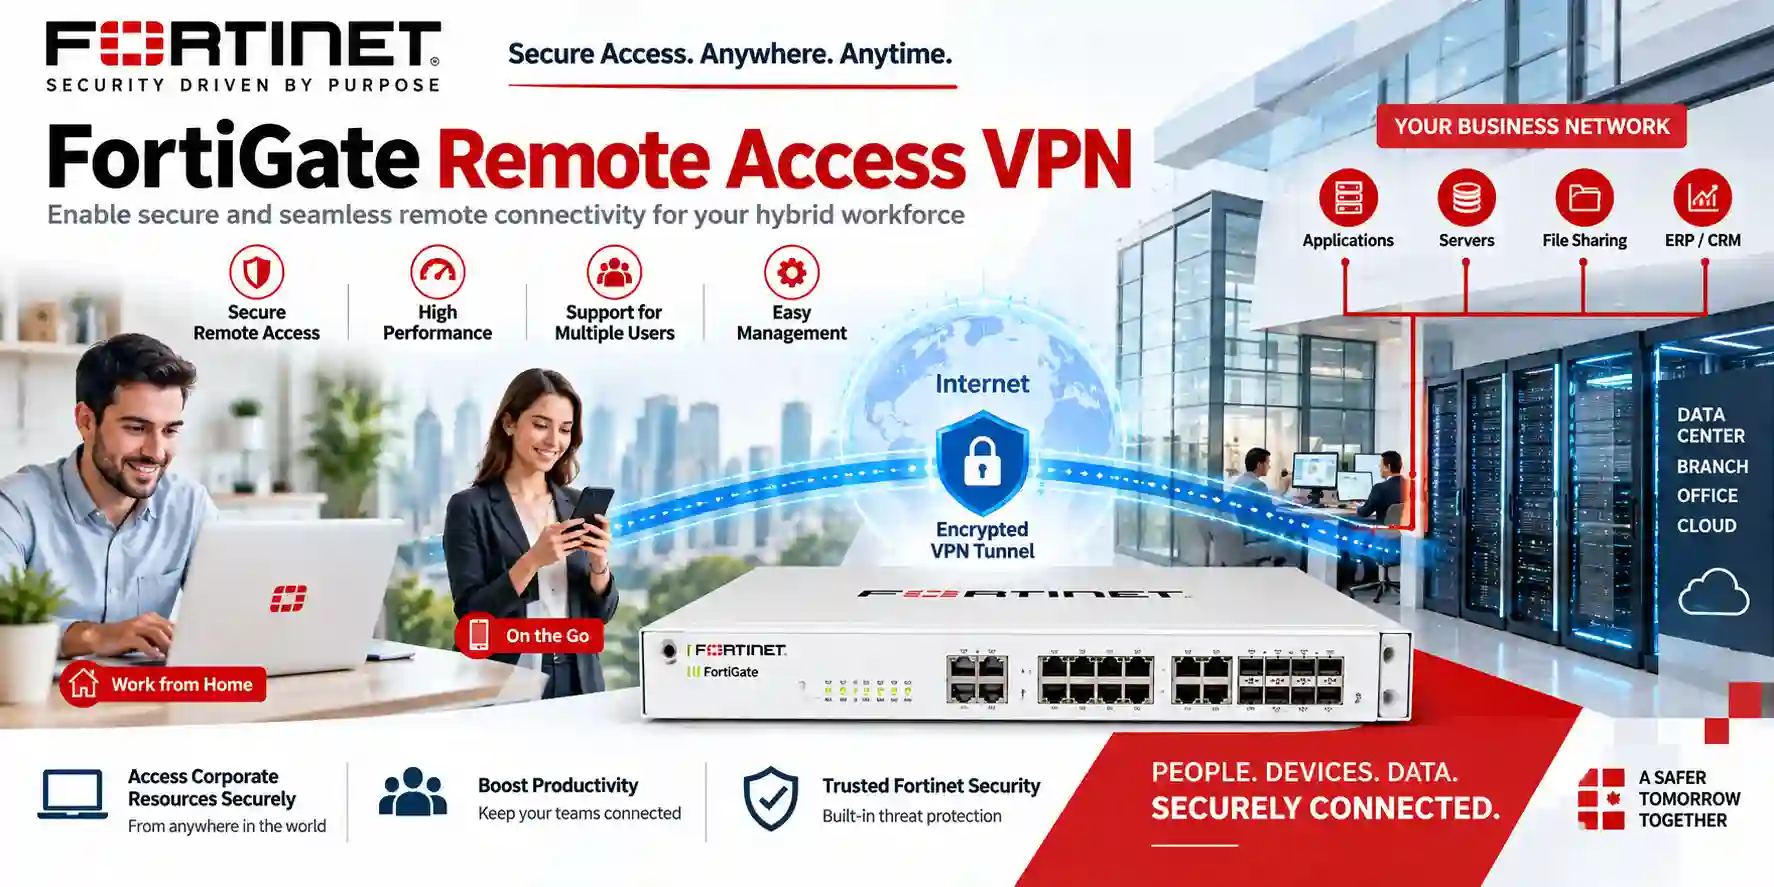
Remote connectivity problems are often described simply as “the VPN is down,” but the root cause can sit at several layers. Site-to-site IPsec depends on internet reachability, correct peer information, compatible phase settings, routes, security policies and the networks defined on both ends. Remote-user access adds identity, endpoint configuration, certificates and user-specific access requirements. Support should therefore confirm which tunnel type is involved and whether the failure affects every user or only a particular path.
Security matters as much as connectivity. Remote users should receive only the network access required for their work, and administrative management should not be exposed broadly. Authentication controls, restricted address pools, route design and logging can help reduce unnecessary access. Where a business also uses IP phones or other branch devices, firewall rules must preserve the required traffic without flattening network security. The Grandstream GXP1625 Tanzania page is one example of an endpoint category that may depend on correctly designed VLAN, SIP and firewall policies in a converged office network.
What to send before requesting Fortinet firewall support
Good support starts with useful context. Share the FortiGate model, FortiOS version, serial number only through an appropriate private support channel, current support or FortiGuard status if relevant, number of WAN links, affected site, approximate user count, problem start time, recent changes and the business service that is impacted. For VPN issues, include both peer locations and whether the public IP changed. For blocked applications, identify the source network, destination, protocol and whether the application works when bypassing the expected path.
Do not publish administrator passwords, private keys, backup files or sensitive configuration data in an open web form. Use a secure exchange method when credentials or configuration exports are genuinely needed. The FourTeck Tanzania contact page is the verified starting point for a project or support enquiry and explains the practical information that helps define a networking or firewall request.
Regional Fortinet Firewall Support Services
The technical principles of FortiGate support are consistent, but the support plan should reflect each organization’s network topology, business hours, available connectivity, local IT resources and procurement process. The following regional guidance focuses on those practical differences without assuming that every location has the same stock position, response arrangement or onsite coverage.
Fortinet Firewall Support Services Tanzania
Businesses in Tanzania use FortiGate firewalls in very different environments: small offices with a single internet connection, headquarters with multiple VLANs and applications, branch networks joined by VPN, hospitality properties serving staff and guests, warehouses with cameras and scanners, schools, clinics and organizations with cloud services or remote employees. A useful support plan begins by documenting what the firewall actually protects. That includes WAN circuits, internal networks, public services, VPN peers, critical applications and any FortiGuard features currently enabled. Once those dependencies are visible, troubleshooting becomes faster because engineers can distinguish a firewall symptom from an ISP, switch, server or endpoint problem.
Tanzania organizations should also treat firewall subscriptions and configuration as separate lifecycle items. An active FortiCare entitlement provides access to Fortinet’s vendor support benefits according to the selected service level, while FortiGuard services provide threat-protection capabilities according to the active subscriptions. FourTeck can help buyers prepare renewal details, verify which information is required for a quotation and connect that commercial step with the operational question: which security services are actually used, and which are needed for the organization’s risk profile? This is particularly important when several FortiGate models were bought at different times and have different renewal dates.
For day-to-day support, the most valuable controls are often simple: current configuration backups, documented administrator access, a list of VPN peers, known public IP addresses, clear firewall policy names and a maintenance process for firmware and major changes. These records reduce dependence on individual memory. A company with branches in Dar es Salaam, Mwanza, Arusha or Dodoma can also benefit from consistent naming, VLAN ranges and VPN standards so every site is not configured differently. Standardization makes remote diagnosis easier and reduces mistakes when a new branch is added.
FourTeck’s Tanzania technology solutions overview explains how firewalls relate to switching, Wi-Fi, servers, IP telephony and other systems. Use that broader architecture view when a FortiGate support issue spans more than one device. For product sourcing and model-selection context, the FourTeck Tanzania shop guidance helps procurement teams evaluate capacity, compatibility and lifecycle requirements before ordering replacement or expansion hardware.
Fortinet Firewall Support Services Dar es Salaam
Dar es Salaam networks often place the firewall at the center of a busy business environment where internet connectivity, cloud applications, email, voice, Wi-Fi, CCTV and branch access all share the same edge. Support therefore has to consider performance and change risk together. If an office has dual internet services, the support request should describe which link is primary, how failover is expected to work and whether inbound services depend on a particular public address. For SD-WAN deployments, health checks and steering rules should be reviewed alongside routing so failover does not unexpectedly send a sensitive application through an unsuitable path.
Head offices in Dar es Salaam may also have more complex segmentation. Staff, finance, guest Wi-Fi, servers, voice devices and surveillance systems do not necessarily need unrestricted communication. When firewall rules have accumulated over time, support can include reviewing broad policies, duplicate objects and unused access while preserving essential business flows. This work should be controlled and documented; deleting rules because they appear old can create outages if the original application owner is no longer available. A traffic-validation plan is more reliable than guesswork.
Maintenance windows are especially important for busy offices. Firmware upgrades, WAN redesign, high-availability changes and major policy cleanup should be prepared before implementation. A good change plan identifies the current version, supported upgrade path, configuration backup, console or recovery access, test cases and rollback point. For critical environments, the business should also decide who approves the change and who can confirm that ERP, email, VPN, cloud and public services work after the window. Fortinet vendor support can complement this process when the appliance has the appropriate active entitlement.
The verified Tanzania contact page lists a Dar es Salaam contact location, so organizations can begin a support or quotation discussion through the same central enquiry channel. The key is to send the firewall model, affected services, WAN details and urgency instead of only writing “internet issue.” That information allows the technical conversation to focus quickly on likely causes and on the safest next diagnostic step.
Fortinet Firewall Support Services Mwanza
Mwanza businesses may operate a local office while depending on systems hosted in Dar es Salaam, another Tanzanian city, a regional data center or a cloud platform. That makes branch connectivity a major support priority. When users report that “the branch is slow,” troubleshooting should separate local internet quality from VPN performance, DNS, packet loss, routing, application latency and firewall inspection. A FortiGate can be working correctly while an upstream circuit is unstable, or the link can be healthy while an incorrect route sends traffic across a longer path than expected. Support is more effective when both network and application symptoms are captured.
For organizations with two WAN links, failover should be tested under controlled conditions rather than assumed. The support plan can review link monitoring, route priority, SD-WAN rules and which business applications need session persistence. Some cloud services tolerate a public IP change better than others; public-facing services may require different planning. If a secondary link has lower capacity, traffic priorities may also need adjustment so essential business tools remain usable during failover rather than competing equally with backups, software updates or guest traffic.
Remote management is valuable for Mwanza sites where specialist security staff are not always onsite. That convenience should be implemented securely. Administrative access can be restricted to trusted sources or protected management paths, individual administrator accounts should be preferred over shared credentials, and configuration backups should be taken before significant changes. A concise network diagram showing WANs, LANs, VLANs and VPN peers is particularly useful because an engineer supporting the branch remotely cannot rely on seeing the physical cabling.
Procurement teams planning an upgrade should provide current internet bandwidth, user count, enabled security profiles, VPN load and expected growth. Firewall sizing should not rely on raw firewall throughput alone because inspection and VPN features affect practical capacity. If the existing unit is nearing its lifecycle or performance limit, the support discussion can become a planned migration rather than a sequence of emergency fixes. That gives the business time to clean old rules, validate dependencies and schedule a controlled cutover.
Fortinet Firewall Support Services Arusha
Arusha has many business environments where reliable internet and controlled guest access are operationally important, including hospitality, travel, professional services, education and organizations coordinating field or regional activity. A FortiGate support plan for these sites should distinguish guest traffic from internal systems and administrative networks. Guest Wi-Fi problems can tempt administrators to create overly broad rules for convenience, but this may expose internal resources unnecessarily. Support should instead confirm VLAN separation, DHCP, DNS, captive or authentication requirements, bandwidth policy and the exact internet path used by guest devices.
Remote access is another common consideration. Managers, reservations staff, finance teams or regional employees may need secure access to internal applications when they are away from the site. Troubleshooting should check the supported remote-access method, identity controls, user groups, client configuration, certificates and the internal routes users are meant to reach. Access should be limited to the systems required for each role. A working tunnel that gives excessive network access is not a complete security solution.
Arusha organizations with busy customer-facing operations should also plan changes around service hours. Firmware updates, major policy revisions and WAN migration can affect booking, payment, communication and cloud applications, so they need a defined maintenance window and test list. Configuration backup is essential before material changes. Where a FortiGate is covered by an active FortiCare service, vendor assistance may be available according to the entitlement; FourTeck can help separate that vendor-support path from local configuration and project tasks.
The Tanzania contact page lists an Arusha contact location, providing a verified route for enquiries. When requesting support, include whether the site is a standalone firewall or part of a multi-location design, the number of WAN links, approximate users, current VPN peers and the business systems most sensitive to downtime. This allows the support scope to reflect the site’s operational priorities rather than treating every firewall alert as equally urgent.
Fortinet Firewall Support Services Dodoma
Dodoma organizations may need firewall support for administrative offices, institutions, professional services, education, healthcare and distributed operations connecting to other Tanzanian locations. In these environments, change control can be just as important as the immediate technical fix. A firewall often protects shared applications, VPN links and user groups that belong to different departments. Before changing a rule, support should identify the owner of the affected service, the current access path and the expected result. That reduces the risk of solving one team’s problem while interrupting another department.
Policy documentation is particularly valuable where administrators change over time. Descriptive rule names, address groups, comments, VLAN labels and VPN peer names make the FortiGate easier to manage. Rules such as “allow all” or objects named only by IP address can become difficult to interpret months later. Support engagements can include cleanup planning, but cleanup should follow evidence. Traffic logs, application ownership and business confirmation are safer guides than deleting configuration simply because it looks untidy.
Dodoma sites connecting to headquarters or cloud applications should also review resilience. If there is a backup ISP, confirm how failover is detected and whether VPN tunnels recover correctly. If the organization depends on a single circuit, the support conversation can document that dependency so management understands the availability risk. SD-WAN can improve path control in suitable designs, but it still needs correct health checks, routing and policy. Technology cannot compensate for an undefined recovery plan.
The verified Tanzania contact page identifies Dodoma as one of its listed contact locations. For a productive support request, send the FortiGate model, FortiOS release, network diagram if available, support entitlement status, affected departments and any change made before the problem began. If the request is part of a wider IT project, the FourTeck Tanzania company overview explains the broader multi-technology approach that can connect firewall work with networks, servers, communication systems and infrastructure.
Fortinet Firewall Support Services UAE
Organizations operating between Tanzania and the UAE often want one security standard across offices even when internet providers, public IP addressing and local application dependencies differ. FortiGate support in the UAE can therefore involve more than resolving an isolated firewall fault. The goal may be to align VPN naming, address plans, security profiles, administrator roles and change procedures across regional sites. Standardization makes cross-border troubleshooting easier because an engineer can understand a new branch quickly instead of learning a completely different design every time.
UAE sites can have high-capacity internet links and demanding applications, so firewall sizing and inspection performance need careful review. A model selected only for basic firewall throughput may not provide the same capacity when advanced security inspection, VPN and logging are enabled. Support should monitor actual utilization, session patterns and enabled features before recommending an upgrade. Where high availability is required, failover tests should include upstream links, public services and application validation rather than only checking that the secondary appliance becomes active.
FortiCare and FortiGuard renewal planning is also important for regional procurement. The correct contract depends on the specific device and service requirement. Fortinet lists multiple FortiCare service levels and FortiGuard bundles, so buyers should verify serial numbers, current entitlements and renewal terms instead of assuming every FortiGate in the organization should receive the same package. For UAE-specific Fortinet information, the verified FourTeck Fortinet UAE specialist site provides a regional route for Fortinet-related product and support enquiries.
Businesses that need multi-brand firewall comparison or deployment context can also use the verified Firewall Dubai specialist site. This is useful when a support issue becomes a migration decision and the organization wants to compare lifecycle, management and integration requirements before committing to a replacement. The key principle remains the same: support should preserve security and business continuity while creating a configuration that future administrators can understand.
Fortinet Firewall Support Services Uganda
Uganda-based organizations may operate a main office, multiple branches, field locations or a regional network that also connects to Tanzania and Kenya. FortiGate support for these environments benefits from clear site standards. Each branch should have a known WAN design, documented VPN peers, consistent address objects and a defined method for configuration backup. When every location is built differently, even a simple policy change becomes harder because engineers first have to rediscover the architecture.
Branch VPN reliability is often a central requirement. Troubleshooting should identify whether a tunnel failure is caused by the local internet circuit, remote peer, changed public IP, mismatched proposals, routing, policy or a downstream LAN problem. Where two internet connections are available, failover logic should be tested with the actual VPN and application traffic. A tunnel that reconnects but sends users down an unexpected path can still create a business outage. Logs and timestamps are especially useful for intermittent faults because they show whether the issue correlates with link loss, renegotiation or configuration events.
Uganda procurement teams should also maintain a renewal calendar for FortiCare and FortiGuard services. Different models and purchase dates can create fragmented expiries. A simple asset list containing model, serial number, site, contract end date and bundle can reduce emergency renewal work. Support and security subscriptions should then be reviewed against operational need rather than automatically replicated from one device to another.
For region-specific networking and technology context, the verified FourTeck Uganda technology site provides an appropriate route for Uganda enquiries. Cross-border organizations can use the same technical documentation principles across the FourTeck regional network, which simplifies escalation when a Tanzania branch and a Uganda branch share applications or VPN connectivity.
Fortinet Firewall Support Services Kampala
Kampala offices often combine dense user populations, cloud applications, guest Wi-Fi, IP telephony, CCTV and branch communication on the same network edge. This creates many legitimate traffic flows that can become difficult to manage if the FortiGate policy set grows without structure. Support should group objects and policies according to business purpose, use clear names and separate user, server, guest and device networks where appropriate. A clean rulebase improves troubleshooting because administrators can identify the intended policy without searching through years of temporary exceptions.
Performance complaints also need evidence. If internet access is slow only at certain times, check WAN utilization, packet loss, application traffic, security inspection load and whether backups or software updates are competing with interactive services. If only one department is affected, investigate VLAN, switch and endpoint paths before assuming a FortiGate capacity problem. Support should compare the symptom with actual resource and session data rather than recommend a larger firewall prematurely.
Kampala businesses with remote users can reduce risk by defining who needs access to which internal services. Finance, management, IT and general staff may require different resources. Remote access should be designed around those roles, supported authentication and controlled routes. Administrator access deserves even stricter treatment: management interfaces should not be broadly exposed, and shared administrator credentials should be avoided where individual accountability is practical.
When a FortiGate is due for firmware maintenance, plan the window around business operations and verify the supported upgrade path. Save the configuration first, record current WAN and VPN state, and prepare application tests for after the reboot. If the device has active FortiCare, vendor support resources can be used according to the contract. FourTeck configuration assistance can complement that entitlement by helping define the change, test business traffic and update documentation after the work is completed.
Fortinet Firewall Support Services Arua
Arua branch environments may depend heavily on remote support and WAN connectivity to reach centralized applications. That makes documentation and resilient access especially important. The FortiGate configuration should clearly identify WAN interfaces, branch VLANs, VPN peers, local services and any policies required for head-office systems. If support is requested during an outage, this information allows an engineer to understand the intended design without waiting for someone onsite to trace cables or remember historical changes.
When connectivity quality varies, troubleshooting should capture packet loss, latency and link availability instead of treating every interruption as a firewall defect. IPsec tunnels naturally depend on the underlying internet path. If the WAN flaps, the tunnel may renegotiate or application sessions may need to reconnect. Where a secondary link is available, the support plan can review how failover is detected and whether the backup circuit has enough capacity for critical traffic. Nonessential traffic may need different handling during degraded conditions.
Remote configuration changes also require a recovery strategy. A routing or interface mistake can cut off the very access being used to administer the firewall. For substantial changes, consider whether someone is available onsite, whether console access exists and how the previous configuration can be restored. Backups should be taken before major work, and each change should be staged so connectivity can be tested before moving to the next step.
Support planning should also account for lifecycle. If a branch firewall is old, lacks current vendor support or cannot comfortably handle required inspection and VPN loads, repeated troubleshooting may be less effective than a planned replacement. Procurement can use current bandwidth, user count, security features, interface requirements and growth expectations to size the next platform. A planned migration gives the organization time to clean the rulebase and standardize the branch with other sites instead of copying every legacy object into a new appliance.
Fortinet Firewall Support Services Mbarara
Mbarara organizations in retail, education, healthcare, agriculture-linked business and professional services may use FortiGate to protect a mix of office users, point-of-sale systems, cloud applications, cameras and branch connectivity. The support challenge is often not a single advanced feature but maintaining predictable access among many device types. Segmentation can help separate guest traffic, user devices and operational systems so a problem in one area does not automatically expose or disrupt everything else.
When users cannot reach an application, the support process should trace the traffic methodically. Confirm the source IP and VLAN, destination, route, expected policy, NAT requirement and whether a security profile is blocking or resetting the session. For cloud services, also check DNS and upstream internet reachability. If the application is hosted at another branch, include the VPN tunnel and remote firewall policy in the trace. This evidence-based method is faster than adding broad temporary rules that may create a new security gap.
Mbarara sites with limited local IT resources benefit from clear change notes. Every significant firewall update should record why it was made, who requested it, which systems were tested and whether follow-up is required. This makes future support easier and reduces the chance that temporary access becomes permanent because nobody remembers its purpose. A quarterly or periodic rule review can focus on business ownership, not simply rule age.
Renewal preparation should be similarly organized. Maintain the FortiGate model, serial number, FortiOS version, FortiCare status, FortiGuard bundle and expiry date in an asset register. That information helps procurement request the correct service and gives technical staff visibility into which security features can receive current FortiGuard updates. If the device is approaching a lifecycle transition, combine the renewal conversation with performance and growth review so the business can decide whether to renew, upgrade or plan a migration with enough lead time.
Fortinet Firewall Support Services Gulu
Gulu sites can include education, healthcare, NGOs, commercial offices and regional operations that depend on secure links to other locations. Support should focus on maintaining essential services during imperfect network conditions. Start by identifying which applications must remain available when bandwidth is reduced: email, ERP, cloud collaboration, VPN access, voice or a specific line-of-business system. That priority list helps shape SD-WAN rules, bandwidth policies or failover decisions instead of treating all traffic equally.
VPN reliability should be measured together with the WAN. A FortiGate can report a tunnel event, but the event may be a consequence of ISP interruption rather than a configuration fault. Correlating timestamps from interface status, tunnel logs and user reports can reveal the pattern. If the peer is located at headquarters, both sides should be checked because mismatched configuration or routing can create one-way symptoms that appear local from only one site.
For security policy, avoid making emergency rules broader than necessary. If a new application needs access, define the source users or network, destination, protocol and direction. Test with logging enabled and document the business owner. This approach keeps the rulebase understandable as the site grows. The same discipline applies to published services: only required ports should be exposed, and internal systems should be protected by appropriate segmentation and authentication.
A support engagement can also review operational readiness: current backup, firmware status, administrator accounts, subscription expiry and hardware capacity. These checks turn an incident into useful lifecycle information. If the FortiGate has active vendor support, Fortinet resources can be used according to the entitlement for qualifying issues. If the problem is local configuration, routing or integration, FourTeck can help structure the diagnosis and planned change. Keeping those responsibilities clear avoids delays during urgent incidents.
Fortinet Firewall Support Services Kenya
Kenya often acts as a regional operating hub for organizations with branches across East Africa. FortiGate support in this context should emphasize consistency across Nairobi, Mombasa and other sites rather than treating every firewall independently. A standard template for interface names, VLANs, VPN objects, administrator roles and logging can significantly reduce support effort. The template should still allow site-specific internet addressing and applications, but the underlying logic should remain recognizable from one branch to another.
Multi-site organizations frequently need help with IPsec tunnels, SD-WAN and routing. Troubleshooting should map the intended traffic path first. If Kenya hosts shared services for Tanzania or Uganda branches, support must confirm both the hub firewall and the remote branch policies. One-way traffic, overlapping networks and asymmetric routing can create confusing symptoms. Clear diagrams and unique subnet planning help prevent these problems before they occur.
Security subscriptions and vendor support can also be standardized through an asset calendar. Record each FortiGate model, serial number, site, FortiOS version, FortiCare tier, FortiGuard bundle and renewal date. This makes budgeting more predictable and reveals devices that may be approaching replacement. Fortinet’s current offerings include multiple FortiCare support levels and FortiGuard security bundles, so the appropriate service should be validated per device and requirement rather than assumed from a generic “Fortinet license” description.
For businesses coordinating firewall projects beyond one country, the verified FourTeck Africa regional site provides a broader cross-market technology route. Kenya projects should still be scoped around the actual local network, ISP design, users and applications. Regional standardization is valuable, but copying a headquarters configuration without adapting public IPs, bandwidth, subnets and service dependencies can create avoidable outages.
Fortinet Firewall Support Services Kuwait
Kuwait-based offices and regional operations may use FortiGate for secure internet access, branch VPN, remote users, cloud applications and segmentation between business systems. Support should begin with a clear operational map: internet circuits, public services, user VLANs, server networks, VPN peers and critical cloud destinations. This is especially useful when the environment has been modified by several vendors over time and the firewall contains rules whose original purpose is no longer obvious.
Change windows need careful preparation when the firewall sits in front of customer-facing or always-on systems. Before firmware updates, policy restructuring or WAN migration, capture a current configuration backup and document how to regain management access if the expected path fails. Create a test list that includes internet, DNS, remote access, site-to-site VPN, published services and core applications. A technically successful reboot is not enough if an essential business workflow is still unavailable afterward.
FortiCare and FortiGuard should be reviewed as part of the device lifecycle. FortiCare provides vendor support benefits according to the active service tier, while FortiGuard services supply security intelligence and updates for the subscribed capabilities. Procurement should verify the device and contract details before renewal. If an appliance is approaching a point where performance, lifecycle or support status no longer fits the business, use the renewal period to compare replacement options rather than waiting for an urgent failure.
Organizations operating between Kuwait, the UAE and East Africa can benefit from one documentation standard across sites. Use consistent object names, VPN naming, administrator roles and change records, while keeping site-specific addressing and ISP information accurate. For broader UAE and MEA technology context, the verified FourTeck regional technology site shows how firewall support fits alongside networking, server, security and communications projects.
Fortinet Firewall Support Services Ghana
Ghanaian businesses with offices in Accra, Kumasi or distributed operational sites can use FortiGate to enforce internet policy, connect branches, protect servers and support remote access. A support plan should define which of those roles is most critical before an incident occurs. If the firewall is the only path to cloud ERP, email and branch applications, its configuration and support status deserve the same operational attention as other core infrastructure.
Rulebase quality is a frequent long-term issue. Policies added for projects, vendors and temporary access can remain after the original need ends. A structured review can group rules by business owner, confirm active traffic, tighten broad services and remove obsolete objects only after validation. This improves security and makes troubleshooting easier. The goal is not to reduce the number of rules for appearance; it is to make each important rule understandable and justified.
For multi-branch connectivity, document every VPN peer, local and remote subnet, authentication method, WAN dependency and route. Overlapping addresses should be identified before adding a new location because they complicate VPN design. If links are unstable, gather tunnel and interface timestamps so support can determine whether the issue is configuration, routing or the underlying carrier path. A secondary link can improve resilience, but it needs tested failover logic and enough capacity for essential services.
Renewal planning should be handled before expiry dates become urgent. Keep a simple asset register with model, serial number, site, active FortiCare, FortiGuard services and renewal term. This gives procurement time to validate the appropriate contract and lets technical staff assess whether the existing appliance still meets performance and lifecycle needs. If a replacement is planned, use the opportunity to clean the configuration, standardize naming and produce current documentation rather than moving every legacy setting unchanged.
Fortinet Firewall Support Services Nigeria
Nigeria organizations can have large user bases, several internet links, distributed branches and demanding cloud or data-center connectivity. FortiGate support in this environment should combine incident resolution with capacity awareness. When users report intermittent performance, inspect WAN utilization, security processing, session volume, routing and application behavior rather than assuming one bottleneck. A high-speed internet circuit does not guarantee good user experience if inspection policies, asymmetric paths or upstream loss create problems.
Multiple ISPs and SD-WAN introduce valuable resilience but also more policy logic. Health checks must measure something meaningful, steering rules should reflect application priorities, and failover behavior should be tested. Critical services may need predictable egress addresses or specific paths. Support should document these exceptions so future changes do not break them. If inbound public services exist, failover may require additional DNS, provider or addressing considerations outside the FortiGate itself.
Large environments also benefit from centralized visibility and disciplined administration. Individual administrator accounts, restricted management access, configuration backups and change tickets make it easier to understand who changed what and why. Logs should be retained according to the organization’s operational and compliance needs, with storage architecture matched to scale. If FortiManager or FortiAnalyzer is part of the environment, support should define which functions are managed centrally and which remain local to each FortiGate.
Procurement and engineering should coordinate on FortiCare and FortiGuard renewals. An asset list can expose mismatched terms, inactive services and devices nearing a migration point. Fortinet publishes current support and security-service options, but the correct combination depends on each appliance and business requirement. FourTeck can help prepare the technical and commercial information for a support or renewal discussion without assuming stock, replacement timing or service entitlement until those details are confirmed.
Fortinet Firewall Support Services Seychelles
Seychelles organizations, particularly hospitality, professional services and island operations, may place a high value on remote manageability because specialist onsite resources can be limited or require planning. FortiGate support should therefore emphasize reliable documentation and secure remote administration. A current diagram, WAN details, local contact, VPN list and configuration backup can reduce the time needed to diagnose an incident without physical access to the appliance.
Connectivity resilience deserves specific attention. If a property or office depends on one primary circuit and a secondary service, document the expected failover behavior and which applications are most important during reduced capacity. Guest internet, staff systems, payment services, cloud applications, voice and management traffic may have different priorities. SD-WAN or policy-based path control can help in an appropriate design, but it must be tested with the real applications. A backup link that technically comes online may still be inadequate if essential traffic is not prioritized.
Security changes should be conservative when remote recovery is difficult. Before modifying interfaces, routing, administrator access or VPN settings, save the configuration and confirm a recovery method. Break large changes into smaller stages, verify connectivity after each stage and avoid simultaneous unrelated modifications. This reduces the chance that troubleshooting becomes more difficult because the original fault and the new change are mixed together.
Lifecycle planning is equally important for island environments. Track FortiCare and FortiGuard expiry dates, firmware support, hardware age and performance headroom before an urgent replacement is required. If migration becomes necessary, prepare the replacement configuration, verify interfaces and VPN peers, define a maintenance window and test critical services after cutover. The support objective is not simply to restore the firewall after a fault; it is to make the entire security gateway easier to operate, recover and maintain over time.
Related FourTeck resources for firewall projects
Firewall support is frequently connected to a broader infrastructure decision. The Tanzania services page explains integrated networking and support capabilities, while the Tanzania shop page helps buyers think through capacity, compatibility, infrastructure and lifecycle before selecting equipment. The FortiGate 30G Tanzania page is relevant when the requirement includes a compact current-generation FortiGate product discussion rather than support for an unspecified installed model.
The About FourTeck Tanzania page provides company and service context, the FourTeck Tanzania home page shows the wider technology portfolio, and the Tanzania contact page is the verified enquiry route. For environments where IP telephony and firewall policy interact, the Grandstream GXP1625 Tanzania page illustrates an endpoint category that depends on correct VLAN, network and firewall treatment.
These internal resources are intentionally different: product pages help with model-specific buying questions, service pages explain integration, and the contact page is for turning the documented requirement into a quotation or technical discussion. Use the page that matches the stage of the project instead of beginning with a product model when the actual problem is still undefined.
Fortinet Firewall Support Services FAQ
What is the difference between FortiCare and FortiGuard?
FortiCare is Fortinet’s support-service family for product assistance and related support benefits according to the active tier. FortiGuard is the family of security services and threat intelligence used for functions such as IPS, antivirus, web security and other subscribed protections. A business may need both, but they solve different lifecycle needs.
Can FourTeck help when a FortiGate VPN is down?
Yes, a support scope can investigate VPN reachability, peer details, proposals, selectors, routing, policies, NAT behavior and the underlying WAN. The exact task depends on the tunnel type, current configuration and whether both VPN endpoints can be reviewed.
Should I upgrade FortiOS immediately when a new release appears?
Not automatically. Firmware planning should consider the current version, supported upgrade path, hardware model, security advisories, required features, known dependencies, maintenance window and rollback preparation. Production upgrades should be planned, backed up and tested against critical business services.
Can firewall support include rule cleanup?
Yes, but cleanup should be evidence based. Policies should be tied to business owners and observed traffic where possible. Removing apparently unused rules without confirming dependencies can break older applications, scheduled tasks or partner connections.
What information is needed for a FortiGuard renewal quotation?
Prepare the FortiGate model, serial number through a private enquiry channel, current service or bundle if known, expiry date, required term and any planned hardware changes. The correct service should be validated for the device rather than selected by a generic product name alone.
Can a FortiGate use two internet connections?
Yes, FortiGate supports multi-WAN and SD-WAN designs, but the correct setup depends on link types, routing, health checks, application requirements and failover goals. Support should define how traffic should behave when both links are healthy and when one fails.
Does active FortiCare mean every configuration task is included?
No. FortiCare provides Fortinet vendor support benefits according to the active service level, while project engineering, policy redesign, migration, local network integration or ongoing managed administration may be separate scopes. Clarifying that distinction at the start prevents delays.
How can I reduce risk before a firewall change?
Define the change, save a current configuration backup, confirm management and recovery access, identify affected applications, document the expected result, schedule an appropriate window and prepare a rollback point. After the change, test internet, DNS, VPN and critical business services.
Fortinet firewall support quotation checklist
Do not place passwords, private keys or full configuration backups in a public enquiry. Sensitive technical data should be exchanged through an appropriate secure method after the support scope is established.
Decision recap
Choose the support path according to the real need. Use FortiCare for eligible Fortinet vendor support benefits tied to the device entitlement. Use FortiGuard subscriptions for the security services your FortiGate requires. Use configuration support when the issue is policy, routing, VPN, SD-WAN, segmentation, integration or planned change. Use a migration project when the appliance no longer fits capacity, lifecycle or business requirements. Keeping these workstreams separate makes quotations clearer and incidents easier to manage.
A well-supported FortiGate environment is not defined by having many rules or features enabled. It is defined by a configuration that matches business traffic, has active services where required, can be backed up and recovered, is documented well enough for another engineer to understand, and can be changed without unnecessary risk.
Talk to FourTeck about your FortiGate environment
Send the FortiGate model, site, FortiOS release, issue description, current support or subscription status if relevant, WAN design and business impact. FourTeck can then help define whether the next step is troubleshooting, a configuration change, renewal guidance, firmware planning, migration preparation or a wider network review.
For Tanzania enquiries, use the verified FourTeck Tanzania contact page. For wider regional technology context, FourTeck’s verified regional sites provide separate market routes, but service availability, onsite scope, stock, replacement hardware and response commitments should always be confirmed for the specific request before they are treated as part of a support contract.