
FORTINET NEXT-GENERATION FIREWALL
FortiGate 51G (FG-51G) Tanzania
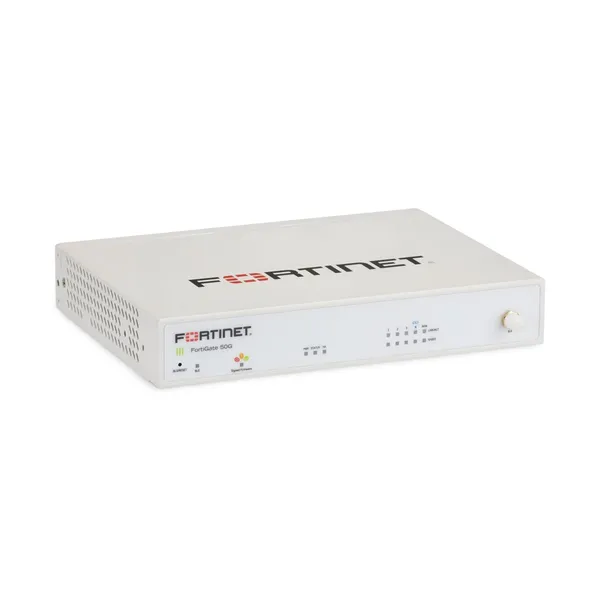
FortiGate 51G is a compact Fortinet security appliance for organisations that need a modern firewall, secure branch connectivity, VPN capability and SD-WAN in a desktop form factor. The official FG-51G configuration includes five Gigabit Ethernet RJ45 ports—four internal and one WAN—and 64GB SSD storage. For Tanzania projects, the important buying decision is not simply the appliance name: the network design, internet bandwidth, security inspection requirements, VPN load, subscription term and support expectations should be defined before the quote is finalised.
FortiGate 51G overview
The FG-51G belongs to Fortinet’s compact FortiGate family and is designed for security-driven networking at smaller sites, branches and distributed business locations. Its five GE RJ45 interfaces provide a straightforward physical layout for a WAN connection and internal network connectivity, while the 64GB SSD distinguishes this model from the storage-less FG-50G. FortiGate platforms combine firewalling with functions available through FortiOS and appropriate FortiGuard services, allowing an organisation to build policies around users, applications, threats, VPN connectivity and internet access from one security platform. Exact services depend on the purchased subscription and support package, so buyers should confirm the required bundle and term rather than assuming every security service is included with bare hardware.
Verified hardware
FG-51G has 5× GE RJ45 ports, comprising 4× internal ports and 1× WAN port, together with 64GB SSD storage.
Branch security
Use the appliance as the security gateway for internet access, segmented internal networks, site connectivity and policy-controlled branch traffic.
Subscription planning
FortiGuard and FortiCare requirements should be selected for the actual security scope, support expectation and subscription period of the project.
Why businesses consider the FG-51G
A compact firewall is often selected when a business needs stronger control than a basic internet router can provide but does not need the interface density of a larger enterprise appliance. Typical projects include a branch office connected to headquarters, a retail or service location that must separate business systems from guest access, a professional office using cloud applications, a small warehouse with centrally managed access policies, or a remote site that needs encrypted connectivity. The FG-51G can be evaluated for these situations because it combines the FortiGate software environment with a compact hardware platform and local SSD storage. Correct sizing still matters. Internet speed alone does not determine firewall suitability: encrypted traffic inspection, IPS, application control, VPN usage, concurrent sessions, logging, future growth and enabled FortiGuard functions can all influence the appropriate model.
For buyers comparing Fortinet models, the 64GB SSD is a key differentiator of the 51G. Organisations should decide whether local storage is useful for their operational and logging strategy, then compare the overall model against lower or higher FortiGate options. A procurement request should state the exact FG-51G model, required quantity, desired subscription term, FortiCare requirement, deployment country, expected internet circuits and whether configuration assistance is needed. That information produces a more meaningful quotation than asking only for a generic “Fortinet firewall price.”
Technical and deployment planning
| Model | FortiGate 51G / FG-51G |
| Ethernet interfaces | 5× GE RJ45: 4× internal, 1× WAN |
| Local storage | 64GB SSD |
| Form factor | Compact desktop-class appliance |
| Planning topics | WAN design, VLANs, VPN, SD-WAN, security inspection, subscriptions, support and migration |
Before deployment, document the current router or firewall, ISP addressing, DNS, VLANs, DHCP scopes, routing, public services, site-to-site VPN peers, remote-access requirements and any applications that need special policy handling. A migration window should include configuration backup, rollback planning and post-change testing. If two internet connections are required, verify the physical and logical design carefully because the standard FG-51G ordering configuration is listed with one dedicated WAN-labelled RJ45 port; interface roles in FortiOS and the intended topology should be reviewed by the implementation team rather than inferred from a product name.
FortiGate 51G Tanzania
Tanzania organisations evaluating the FortiGate 51G commonly need a firewall that can sit at the boundary between business users and one or more internet services while giving administrators clearer policy control than a standard ISP router. The FG-51G is relevant to compact offices, branch networks, retail environments, professional services, education administration, clinics, hospitality back offices and distributed operations where secure access to cloud applications and central systems is important. A Tanzania purchase should begin with the site requirement rather than a model assumption. Record the number of users and devices, internet circuit speeds, expected VPN traffic, guest-network needs, internal VLANs, public-facing services and the security features that will be enabled. These details help determine whether the 51G is appropriately sized or whether another FortiGate model should be considered.
Procurement teams should request the exact FG-51G hardware reference and clearly state whether they need FortiGuard security services and FortiCare support. Subscription bundles and terms can materially change the commercial scope, so compare like with like. A low hardware-only figure should not be mistaken for a complete security-service package. For multi-site Tanzania deployments, standardise the intended FortiOS policy approach, naming conventions, VPN addressing, administrator roles and backup process before rolling out appliances. This makes later support and troubleshooting easier, particularly where branches are operated by small local teams while security administration is centralised.
Connectivity conditions can vary between business sites, so implementation planning should account for ISP handoff type, static or dynamic addressing, power protection, equipment cabinet ventilation, upstream switching and wireless access points. Where business continuity is important, discuss secondary connectivity and SD-WAN design before purchase so the required ports, modem or cellular options and failover behaviour are understood. FourTeck can use a requirement-led enquiry to help structure the product, licensing and deployment discussion. Buyers can also review FourTeck Africa security solutions when planning projects that extend beyond Tanzania.
FortiGate 51G Dar es Salaam
For Dar es Salaam businesses, firewall projects often combine internet security with practical branch connectivity. Corporate offices, trading companies, logistics operations, hospitality businesses, professional firms and growing SMEs may need to protect cloud access, ERP traffic, email, web applications, remote users and links to other offices. The FG-51G can be assessed as a compact gateway where the interface count and performance profile fit the design. Start by mapping which systems are business-critical and which traffic groups should be separated. Staff, guest Wi-Fi, voice, cameras, servers, payment systems and management devices may warrant different VLANs and policies even when they share the same physical location.
A Dar es Salaam quotation should identify whether the organisation is replacing an older firewall, opening a new site or standardising several branches. Replacement projects require extra attention to existing NAT rules, VPN tunnels, DHCP, DNS forwarding and any port forwards used by business applications. New sites should define addressing and security zones before installation. If the business depends heavily on SaaS and cloud systems, include expected internet utilisation and inspection requirements in the sizing discussion. Security features consume resources differently, which is why headline internet bandwidth should not be the only selection criterion.
The FG-51G’s 64GB SSD may be attractive where local storage is part of the desired operational design, but storage should be considered alongside central logging, monitoring and retention requirements. Ask how logs will be reviewed, who receives alerts and how configuration backups will be protected. Businesses with multiple offices should also plan administrator access carefully and avoid shared credentials. For procurement, provide the exact model, quantity, subscription term, desired FortiCare level and deployment schedule. This gives the supplier enough information to return a quote that is easier for IT and finance teams to compare.
FortiGate 51G Mwanza
Mwanza buyers may be securing a regional office, distribution point, service centre, education facility, hospitality property or growing commercial site where dependable internet access and controlled connectivity are operational priorities. The FortiGate 51G can be evaluated for smaller network edges that need firewall policies, secure remote connectivity and Fortinet’s integrated networking and security approach. Before selecting it, count both users and networked devices. A location with a modest staff count can still generate substantial traffic through IP cameras, cloud backups, guest Wi-Fi, voice systems, software updates and remote management tools.
For sites connected back to a Dar es Salaam head office or another regional hub, define the VPN topology before ordering. Decide which subnets must communicate, whether traffic should route directly to the internet at the branch, which applications must traverse the tunnel and how DNS will operate during a WAN outage. If a secondary connection is planned, document its handoff and expected failover behaviour. Secure SD-WAN can be valuable in distributed networks, but the design should reflect actual circuits and business priorities rather than being treated as a checkbox feature.
Power and physical installation deserve attention as well. Place the firewall and associated network equipment in a controlled location with suitable power protection and cable management. Record the ISP device configuration and keep an approved backup of the firewall configuration after commissioning. Procurement teams should request an FG-51G quote that separates appliance, FortiGuard services, FortiCare and any professional services so commercial comparisons remain clear. If future expansion is expected, include that growth in sizing rather than buying only for today’s traffic. The goal is a security gateway that fits the network’s real inspection, VPN and availability requirements.
FortiGate 51G Arusha
Arusha has a diverse mix of tourism, hospitality, professional services, NGOs, education and regional business operations, and each environment can place different demands on a branch firewall. A hotel back office may need to isolate administrative systems from guest access; an NGO office may rely heavily on cloud collaboration and encrypted links to other locations; a professional firm may prioritise remote access and protection of client data. The FG-51G can be considered for compact deployments where its port layout and security capabilities align with the network design.
Begin with segmentation. Identify staff endpoints, servers, wireless infrastructure, guest devices, cameras, printers and management interfaces, then decide which groups actually need to communicate. Firewall policies should be intentionally narrow instead of allowing unrestricted movement between internal networks. If remote workers or support partners require access, define the approved applications and authentication approach before enabling VPN connectivity. For organisations using cloud platforms, include web and application inspection needs in the sizing conversation because enabling advanced security controls changes the workload placed on the appliance.
Arusha projects that depend on continuous internet access should document the primary ISP, any backup connection and the business applications that must remain reachable during an outage. The implementation plan should include configuration backup, administrator access controls, firmware maintenance responsibilities and a method for reviewing security events. When requesting pricing, specify FG-51G rather than simply “FortiGate,” and state the subscription and support term needed. If the requirement is uncertain, provide the current bandwidth, device count, VPN needs and growth expectation so a model comparison can be made before the purchase is approved.
FortiGate 51G Dodoma
Dodoma organisations looking at the FortiGate 51G may include administrative offices, professional firms, education sites, branch operations and service organisations that need controlled access to internet and private applications. For these buyers, a firewall decision should connect security requirements with operational simplicity. The FG-51G offers a compact FortiGate platform with five GE RJ45 interfaces and 64GB SSD storage, but successful deployment depends on the policy and network design built around the hardware.
A useful planning exercise is to list every connection that crosses the firewall. Include user web access, SaaS, email, DNS, software updates, remote administration, branch-to-head-office traffic and any public services. Then classify which flows require additional inspection or restrictions. This produces a cleaner rule set and reduces the risk of migrating old, unnecessary policies from a previous appliance. For VPN deployments, document peer addresses, subnets, authentication details and failover expectations. For a new office, establish a consistent IP and VLAN plan before devices are connected.
Procurement should also consider lifecycle operations. Determine who will apply FortiOS updates, monitor alerts, renew FortiGuard subscriptions, manage administrator accounts and retain configuration backups. A firewall that is purchased correctly but left unmanaged can quickly become an operational weakness. Request the appliance and service components clearly on the quote, and confirm the term and start conditions of any subscription or support entitlement. For multi-location deployments, use the same configuration standards where practical while allowing site-specific addressing and connectivity. This approach makes the FG-51G easier to operate as part of a broader security estate rather than as an isolated device.
FortiGate 51G UAE
UAE buyers often evaluate the FortiGate 51G for compact branches, retail points, professional offices and distributed sites that need a standard Fortinet security platform. Organisations with operations in both the UAE and East Africa may also use a common FortiGate approach to simplify policy templates, VPN design and administrator training. The model’s five GE RJ45 ports and 64GB SSD should be matched against the actual site topology, including ISP handoff, LAN switching, wireless infrastructure and any secondary connectivity requirement.
For a regional rollout, consistency is valuable but should not override local requirements. A Dubai office with high-speed connectivity and a Tanzania branch with different ISP characteristics may need different bandwidth policies or failover logic even when both use FortiGate. Standardise security objects, naming, authentication, logging and change-control processes, while documenting local WAN addressing and provider details separately. Where encrypted site-to-site connectivity is needed, define routing and application paths before deployment to avoid overlapping subnets and unnecessary hairpin traffic.
Commercially, compare the same FortiGuard and FortiCare terms across quotations. Hardware-only and bundled offers are not equivalent. Buyers can review FourTeck’s Fortinet UAE resource for wider Fortinet project context. For export or multi-country requirements, provide destination, quantity, desired subscription period and staging requirements in the enquiry. Do not assume stock, lead time, warranty route or local service coverage until these are confirmed in the formal quote. This keeps procurement decisions tied to verifiable commercial terms rather than general product-page claims.
FortiGate 51G Uganda
Uganda organisations can evaluate the FG-51G for branch security, secure internet access and connectivity between offices. The most useful selection process starts with traffic and business dependency. Identify which cloud services, internal applications, VPN links and user groups depend on the firewall, then estimate current and expected bandwidth. Consider security inspection requirements as part of sizing. An appliance handling basic routing is under a different workload from one performing multiple threat-prevention and inspection functions.
For companies operating in both Uganda and Tanzania, a standard Fortinet platform can simplify configuration conventions and support procedures. That does not mean every site should receive the same appliance. Kampala headquarters, regional branches and small field locations may have very different throughput, interface and resilience needs. Use the FG-51G where the model fits the actual design and evaluate larger or alternative FortiGate options when growth, interfaces or security load demand them. The 64GB SSD is one factor in that decision and should be considered within the wider logging and management strategy.
A procurement request should list FG-51G, quantity, deployment city, desired FortiGuard package, FortiCare term, VPN requirements and whether configuration or migration assistance is required. Buyers can use FourTeck Uganda for Uganda-focused project enquiries. Before installation, document ISP details, VLANs, routes and existing policies. After commissioning, keep a configuration backup and assign responsibility for firmware maintenance, subscription renewals and security-event review. These operational details are as important as the initial hardware purchase.
FortiGate 51G Kampala
Kampala businesses considering FortiGate 51G often need a compact security gateway for an office that relies on cloud applications, internet communications, remote users and links to other company locations. Start by separating the business requirement into security zones and traffic paths. Staff devices, servers, guest wireless, voice, cameras and management systems should not automatically share unrestricted access. A structured VLAN and policy design can reduce unnecessary lateral connectivity while making troubleshooting clearer.
If the Kampala site is a headquarters or regional hub, its firewall requirements may exceed those of a small branch. Account for inbound and outbound VPN traffic, centralised services, backup jobs and any traffic that remote offices send through the site. The FG-51G should be selected only after these workloads are considered. If it is used as a branch appliance, define how it connects to headquarters, which routes are advertised and how users continue working when the primary WAN fails. Secure SD-WAN planning should include measurable path preferences for important applications rather than simply enabling multiple links.
For purchasing, ask suppliers to identify the exact appliance and service term. FortiGuard subscriptions and FortiCare support are commercial components that should be compared consistently. Avoid comparing a bare appliance quote with a multi-year security bundle as though they were the same product scope. Provide the deployment date and any migration constraints so implementation can be planned around business operations. Once installed, review administrator privileges, backup procedures and monitoring. A firewall should be treated as an actively managed security control, not a one-time network purchase.
FortiGate 51G Arua
For an Arua branch or regional operation, the value of a compact firewall often lies in giving central IT a consistent security boundary at a site that may have limited local technical resources. The FortiGate 51G can be assessed for this role where its interfaces and capacity fit the site. Before deployment, central IT should prepare a documented configuration that covers WAN addressing, internal networks, DHCP or relay requirements, DNS, VPN, security policies and administrator access. Pre-planning reduces the amount of troubleshooting that must be done remotely during installation.
Connectivity resilience may be particularly important for sites that depend on cloud systems or central applications. If the business plans a second internet or cellular path, confirm the hardware and topology needed for that design before purchase. Define what should happen when the primary connection degrades, which applications receive priority and how the branch returns to the preferred path. The firewall can support a broader secure networking design, but availability depends on the complete solution—including circuits, power, switching and configuration—not the firewall alone.
Arua procurement enquiries should state the exact FG-51G model, quantity and required services. If the appliance is part of a nationwide Uganda rollout, include all branch locations and approximate user/device counts so the project can be checked for consistency. Some sites may justify a different model. Establish a standard handover document containing serial information, IP plan, VPN peers, support details and backup location. This makes future support easier and reduces dependency on individual installers. Confirm commercial availability and service coverage through the formal quotation rather than assuming it from general regional marketing.
FortiGate 51G Mbarara
Mbarara organisations may use a branch firewall to protect retail, education, healthcare administration, distribution, professional services or regional business networks. The FortiGate 51G is a candidate for compact deployments where the security workload and interface requirements match the appliance. The first step is to identify business-critical traffic. Cloud ERP, email, voice, payment systems, file access and remote support can have different priorities and risk profiles. Grouping these flows into sensible network segments helps administrators write clearer firewall policies.
Where the site connects to Kampala or another central office, plan VPN addressing carefully. Overlapping subnets are a common source of complexity in multi-site networks, so new branches should receive unique network ranges. Decide whether internet traffic exits locally or is sent through headquarters and document any applications that require fixed public addresses. If the organisation uses two connectivity providers, establish how failover will be tested and monitored. The firewall configuration should reflect business continuity priorities, not just technical link status.
The FG-51G’s local SSD is a model-specific hardware feature, but logging strategy should still be designed intentionally. Determine whether logs remain local, are sent to a central platform, or use another approved retention method. Define who reviews security events and how long records need to be kept for operational or compliance reasons. For quotation requests, separate hardware, FortiGuard, FortiCare and services. Confirm subscription dates and renewal responsibilities. A well-documented purchase and handover process gives the Mbarara site a clearer support path after installation and makes later expansion easier.
FortiGate 51G Gulu
Gulu branch deployments often benefit from network equipment that can be managed according to a central standard while remaining straightforward at the local site. The FortiGate 51G can be considered for offices that need secure internet access, VPN connectivity and segmented internal networks. Before choosing the model, estimate not only employee count but total connected devices and the traffic generated by them. Cameras, access points, printers, backup agents and cloud-connected systems can materially change the network load even in a relatively small office.
Installation planning should include the ISP handoff, power protection and physical location of the appliance. Keep the firewall in a controlled area rather than an exposed desk or public space, and ensure network cabling is labelled. If remote central administration is planned, restrict management access appropriately and use individual administrator accounts. Document how configuration backups are taken and where they are stored. These basic operational controls improve recoverability if the device is replaced or a configuration change causes a problem.
For multi-branch organisations, use the Gulu deployment as part of a repeatable standard: common naming, policy templates, VPN design and change procedures can reduce support effort. However, confirm local bandwidth and connectivity before copying settings from another site. Procurement teams should ask for FG-51G specifically and state the desired FortiGuard and FortiCare term. If future growth is likely, include it in the sizing discussion. The right outcome is not merely obtaining the requested model but confirming that the appliance, subscription and deployment design work together for the site’s expected security workload.
FortiGate 51G Kenya
Kenya businesses evaluating the FortiGate 51G may be planning a Nairobi office, regional branch, retail location, logistics site or distributed network that needs a consistent Fortinet security gateway. The FG-51G can be considered where its five GE RJ45 ports, 64GB SSD and FortiGate capabilities fit the design. A model decision should be based on inspected traffic, VPN requirements, sessions, interfaces and future growth rather than the number of employees alone. Branches using cloud applications and video collaboration can generate substantial encrypted traffic that must be included in sizing.
For East African organisations with locations in Kenya, Tanzania and Uganda, standardisation can reduce operational complexity. Use common policy naming, VPN templates, administrator roles and documentation while preserving site-specific WAN and addressing details. Before rollout, verify that each branch uses unique internal subnets and that routing between countries or data centres is intentional. If a site has two ISPs, define SD-WAN rules around application importance, latency and failure conditions. The network team should test both failover and recovery to the preferred path.
Buyers can review FourTeck Kenya for Kenya-focused enquiries. When requesting a quote, state the exact FG-51G model, quantity, subscription package and term, support requirement and delivery destination. Do not infer current stock or lead time from a web page; obtain those details in the commercial response. For replacement projects, include the existing firewall model and important VPN or NAT dependencies. That allows the migration scope to be discussed alongside the hardware rather than discovered at the installation stage.
FortiGate 51G Kuwait
Kuwait organisations may evaluate FortiGate 51G for compact offices, retail branches and distributed environments where internet security, VPN and consistent policy management are required. The same procurement principles apply: confirm whether the requirement is hardware-only or includes FortiGuard security services and FortiCare support, then compare identical terms. The 64GB SSD differentiates the FG-51G within its immediate family and can be considered as part of the organisation’s logging and operational design.
For businesses connecting Kuwait with East African operations, VPN architecture should be planned before appliances are shipped to remote branches. Assign non-overlapping networks, document application routes and decide where internet-bound traffic exits. A central IT team can maintain common security standards while adapting WAN settings and resilience policies to each country. If the Kuwait site acts as a hub, account for aggregated branch traffic when sizing its own firewall; the branch model and hub model do not need to be identical.
FourTeck’s Kuwait technology portal provides a regional path for project enquiries. Quote requests should specify model, quantity, term, destination and any configuration or staging requirement. Confirm availability, warranty route, licensing dates and logistics in writing. For a multi-country rollout, keep a central asset list containing serial numbers, subscription expiry dates, site contacts and configuration-backup references. This turns a collection of firewalls into a manageable security estate and helps procurement plan renewals before services expire.
FortiGate 51G Ghana
Ghana organisations considering the FortiGate 51G can approach the purchase as a combination of hardware selection, security subscription planning and network design. Compact branches often need more than basic firewalling: they may require site-to-site VPN, controlled web access, application visibility, segmented wireless networks and secure administration. The FG-51G can be evaluated for those needs where its capacity and five-port GE layout suit the environment. Its 64GB SSD should be assessed in relation to logging and management requirements.
For an Accra headquarters or larger site, verify whether the 51G has enough headroom for all enabled inspection features and expected growth. For smaller regional branches, the same model may provide a consistent platform that central IT already knows how to operate. Standardise security policies where possible but avoid blindly cloning WAN, routing and DHCP settings. Each site should have documented provider information, addressing and local dependencies. VPN designs should avoid overlapping subnets and should identify which traffic is permitted between branches.
Commercially, ask for the exact subscription and support components on the quote and confirm the service term. Hardware pricing alone does not describe the full lifecycle cost of a security appliance. Where implementation assistance is needed, provide the current network diagram or at least a list of WAN circuits, VLANs and existing firewall rules. For remote branches, pre-staging can reduce onsite complexity when properly planned. After deployment, assign responsibility for updates, backups, event review and renewals so the firewall remains an actively maintained control rather than an unmanaged edge device.
FortiGate 51G Nigeria
Nigeria deployments can range from a compact office to a nationwide branch network, so the FortiGate 51G should be assessed in the context of each site. A small office may need secure internet, remote access and a site-to-site VPN; a retail or service network may need repeatable segmentation and centrally controlled policies; a regional operation may need resilient connectivity across more than one provider. The FG-51G provides a compact FortiGate platform with 64GB SSD and five GE RJ45 ports, but model suitability depends on the security workload and topology.
Where connectivity quality varies, SD-WAN design should be based on measurable link conditions and application priorities. Identify which services must stay available during a provider outage and whether a backup link has enough capacity for essential traffic. For VPN connectivity, document tunnel peers, routes and authentication, and test failover rather than assuming it will behave as intended. Security segmentation is also important: separate user, guest, server, camera and management traffic according to business need, then permit only the required flows.
Procurement teams should compare equivalent FortiGuard and FortiCare terms and request confirmation of availability for the required destination. If the project covers several Nigerian cities or extends to Ghana, Tanzania, Kenya or Uganda, provide a site list and expected quantities so the rollout can be planned consistently. Maintain an asset register with serials and subscription dates after deployment. For replacement projects, capture the existing configuration dependencies before scheduling the cutover. A successful firewall refresh is measured by secure continuity of business services, not simply by powering on a new appliance.
FortiGate 51G Seychelles
Seychelles businesses in hospitality, professional services, retail and other sectors may need a compact firewall to secure cloud access, administrative networks, guest environments and remote connectivity. The FortiGate 51G can be considered for appropriately sized sites that want a Fortinet security platform with local SSD storage. In hospitality in particular, it is important to separate guest traffic from property administration, payment, voice, cameras and management systems. The firewall is one part of that design alongside switching and wireless infrastructure.
Island connectivity and business continuity requirements should be discussed during planning. If a property or office has more than one internet service, define how applications use those paths and what happens when one connection fails. A backup circuit is only useful if the network is configured and tested to use it correctly. For remote support, establish secure administrator access and avoid exposing management interfaces unnecessarily. Keep configuration backups and a current network diagram so changes can be reviewed without relying on memory.
When requesting an FG-51G quotation for Seychelles, state quantity, destination, subscription term, support needs and any staging or configuration requirement. Confirm logistics, availability and commercial conditions in the formal quote rather than assuming them. If the business is part of a wider regional group, align naming, VPN and policy standards with other sites while adapting to local connectivity. Review future bandwidth growth and new cloud services before finalising the model. This requirement-led approach helps ensure the selected FortiGate remains useful as the site evolves.
Licensing, FortiGuard and FortiCare planning
The appliance SKU and the security-service package should be treated as separate procurement questions. Fortinet offers support and security services in different combinations and terms, and the appropriate choice depends on the organisation’s security objectives. When comparing quotes, ensure the same model, service package, support level and subscription duration are being compared. Ask when service entitlement begins, what renewal process applies and which team will track expiry dates. Organisations operating several FortiGates should maintain a central renewal calendar so subscriptions do not lapse unnoticed.
Security services should also be reflected in operational procedures. Enabling inspection features without defining how alerts are reviewed or policies are maintained leaves part of the security value unused. Assign responsibility for firewall administration, firmware planning, change approval, configuration backups and incident response. If the business does not have internal capacity for these tasks, include management or support requirements in the procurement discussion rather than treating them as an afterthought.
FortiGate 51G buying checklist
Before requesting a quote, prepare: exact model FG-51G; quantity; deployment country and city; current and planned internet bandwidth; number of users and connected devices; VLAN and segmentation requirements; site-to-site and remote-access VPN needs; expected security inspection features; desired FortiGuard package and term; FortiCare requirement; secondary-WAN or cellular plans; existing firewall model if replacing equipment; preferred implementation date; and whether configuration, migration or post-installation support is needed.
This checklist helps sales and technical teams distinguish a simple hardware request from a complete firewall project. It also reduces the risk of receiving quotations that appear different in price because they include different subscription periods or services. For a multi-site rollout, add a branch matrix showing users, bandwidth, ISP types and critical applications at each location. The same FG-51G may not be appropriate everywhere, and documenting differences early makes model selection more defensible.
FortiGate 51G FAQs
What is the FortiGate 51G?
The FG-51G is a compact Fortinet FortiGate firewall appliance in the 50G family. The official ordering information lists five GE RJ45 ports—four internal and one WAN—and 64GB SSD storage.
What is the difference between FortiGate 50G and 51G?
A key official hardware difference is storage: the FG-51G includes 64GB SSD storage, while the standard FG-50G ordering description does not list that onboard SSD. Buyers should compare the complete official specifications and required services for their project.
Does FG-51G include FortiGuard subscriptions?
Do not assume a bare FG-51G hardware quote includes a particular FortiGuard package. Fortinet appliances can be purchased in different commercial configurations and terms. Ask for the exact bundle and subscription duration on the quotation.
Can FortiGate 51G be used for VPN and SD-WAN?
FortiGate platforms support VPN and secure SD-WAN capabilities through FortiOS. The suitability of the FG-51G for a specific VPN or SD-WAN deployment depends on traffic volume, inspection requirements, tunnel design, interfaces and other site requirements.
How should I size a FortiGate 51G project?
Provide internet bandwidth, users and devices, enabled security services, VPN requirements, concurrent traffic, application mix, interfaces and expected growth. Sizing should reflect inspected traffic rather than relying only on ISP line speed.
How do I request a FortiGate 51G quote in Tanzania?
Send FourTeck the exact FG-51G model, quantity, city, required FortiGuard and FortiCare term, deployment requirements and target timeline. Current price, availability and commercial conditions should be confirmed in the formal quotation.
Decision recap
Choose the FortiGate 51G because its verified hardware and FortiGate capabilities fit a documented network requirement—not simply because it is the newest compact model in a shortlist. Confirm the five-port layout, 64GB SSD, traffic profile, inspection needs, VPN design, subscription package, support term and future growth. For Tanzania branches, document connectivity and power considerations before deployment. For multi-country projects, standardise policy and operational processes while allowing each site’s WAN design to remain appropriate to local conditions.
Talk to FourTeck about your FG-51G requirement
Share your deployment city, quantity, internet bandwidth, users, VPN requirements, FortiGuard term and support needs. FourTeck can use those details to structure a quotation discussion for the FortiGate 51G and related Fortinet requirements. For broader regional projects, the FourTeck network can also support conversations spanning Tanzania, East Africa and selected international markets. Final availability, pricing, warranty route, licensing and service scope should always be confirmed in the formal commercial response.




Reviews
There are no reviews yet.