
FORTINET NEXT-GENERATION FIREWALL • TANZANIA
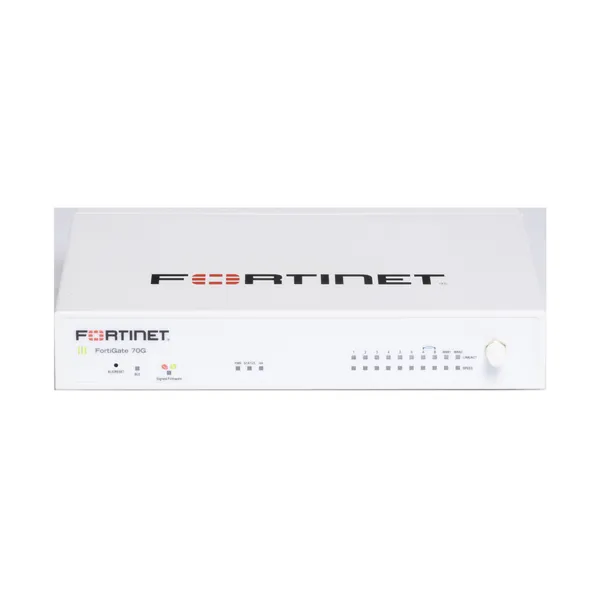
FortiGate 70G PoE (FG-70G-POE)
FortiGate 70G PoE is a compact branch next-generation firewall for organizations that want security, routing, Secure SD-WAN, VPN and powered-edge connectivity in one Fortinet platform. Fortinet positions the 70G family for distributed enterprise sites and converged networking and security. The FG-70G-POE variant adds four hardware-accelerated Gigabit Ethernet PoE/+ ports, which can simplify selected branch designs where access points, phones, cameras or other compatible powered endpoints are located near the security edge.

FortiGate 70G PoE: direct answer for buyers
The FG-70G-POE is best evaluated as a branch security platform rather than as a basic router. The official FortiGate/FortiWiFi 70G Series material describes the family as a converged NGFW and SD-WAN platform running FortiOS and designed to integrate with FortiGuard security services and the wider Fortinet Security Fabric. Published model references identify two hardware-accelerated GE WAN ports, two hardware-accelerated GE RJ45 ports, two FortiLink ports and four hardware-accelerated GE RJ45 PoE/+ ports. Published performance for the family includes up to 10 Gbps firewall throughput, 2.5 Gbps IPS throughput, 1.5 Gbps NGFW throughput and 1.3 Gbps threat-protection throughput; real deployment performance depends on traffic profile, enabled inspection, firmware, configuration and services.
For procurement, do not size a firewall from headline throughput alone. Share actual ISP bandwidth, expected growth, concurrent users, cloud applications, VPN tunnels, remote users, VLANs, public services, logging needs, security subscriptions and the PoE endpoints you expect to attach. FourTeck Tanzania’s integrated technology overview explains why firewall, switching, Wi-Fi, voice, CCTV, servers and cabling should be considered together. The Tanzania contact page also lists the information that helps turn a model request into a practical quotation.
Converged security
FortiOS combines firewalling, networking and SD-WAN functions in one operating environment, reducing the need to manage separate edge platforms for common branch requirements.
Four PoE/+ ports
The PoE variant provides four GE RJ45 PoE/+ interfaces. Validate endpoint power demand and the appliance PoE budget before treating these ports as a substitute for a dedicated PoE access switch.
Secure SD-WAN
Organizations with multiple WAN links can design application-aware connectivity and failover policies while keeping network and security policy under the same Fortinet platform.
Fortinet ecosystem
FortiLink and Security Fabric integration can support coordinated designs with FortiSwitch, FortiAP, FortiManager, FortiAnalyzer and FortiGuard services where those components suit the project.
Technical specification highlights
| Model | FG-70G-POE / FortiGate 70G PoE |
| Platform | FortiGate 70G Series next-generation firewall and Secure SD-WAN platform |
| PoE connectivity | 4 x hardware-accelerated GE RJ45 PoE/+ ports; published PoE budget 60 W |
| WAN | 2 x hardware-accelerated GE RJ45 WAN ports |
| Additional Ethernet | 2 x hardware-accelerated GE RJ45 plus 2 x hardware-accelerated GE RJ45 FortiLink ports |
| Firewall throughput | Up to 10/10/10 Gbps for 1518/512/64-byte UDP packets in published series data |
| IPS / NGFW / Threat Protection | Published series figures: 2.5 Gbps / 1.5 Gbps / 1.3 Gbps |
| Operating system | FortiOS |
| Form factor | Compact desktop appliance |
Performance values are vendor-published benchmark figures and should not be interpreted as guaranteed application throughput. Inspection mode, packet size, SSL/TLS inspection, security profiles, VPN, logging, policy complexity and traffic mix can materially affect production results.
How PoE changes the branch design
The main reason to choose FG-70G-POE instead of a non-PoE sibling is not simply the presence of extra Ethernet sockets. It is the ability to power a limited set of compatible endpoints directly from the firewall. That can be useful in a compact branch where one or more FortiAP access points, IP phones, cameras or other standards-compatible devices are positioned close enough to cable directly to the appliance. It can reduce individual power adapters and simplify a small deployment, especially when rack or desk space is constrained.
PoE still needs engineering. Add the maximum power draw of the intended endpoints, leave sensible headroom, confirm cabling quality and determine whether the 60 W published budget fits the full design. A branch with many cameras, phones or access points will normally need a dedicated PoE switch. FourTeck Tanzania’s network planning guidance covers managed switching, VLANs, uplinks and PoE design, while its Wi-Fi guidance emphasizes that wireless performance depends on radio planning and wired uplink quality as well as access-point selection.
Power resilience also matters. If the firewall powers critical endpoints, a suitable UPS strategy can keep the security gateway and those endpoints operating together through short interruptions. Cabling, rack ventilation and documented port assignments make troubleshooting easier. For larger deployments, use FortiGate as the security and control point and place endpoint density on appropriately sized access switches rather than concentrating every powered device on the firewall.
FortiGate 70G PoE Tanzania
Tanzania buyers considering the FortiGate 70G PoE commonly need more than a firewall SKU. A useful design starts with the business edge: primary and backup internet, staff and guest networks, cloud applications, branch links, remote access, IP telephony, Wi-Fi, CCTV and any servers or public services that must be protected. FG-70G-POE can become the policy point for these flows, but the model should be sized around inspected traffic rather than raw internet speed alone. A 500 Mbps connection carrying encrypted SaaS traffic with deep inspection can create a different workload from a similar-speed link used mostly for uninspected browsing.
For Tanzanian organizations with more than one ISP, Secure SD-WAN is relevant because link choice, health checks and application steering can be planned alongside firewall policy. A second circuit is not automatically a resilient design: failover criteria, DNS behavior, VPN dependencies, public IP requirements and application sessions need testing. Businesses connecting Dar es Salaam with branches in Arusha, Mwanza or Dodoma can also evaluate IPsec VPN and standardized policy so each site follows a consistent security architecture. Centralized Fortinet management and logging may become useful as the number of sites increases.
The PoE version is particularly interesting for compact Tanzanian branches where a small number of powered devices sit close to the firewall. Before procurement, identify each PoE endpoint and its maximum draw, because a 60 W budget is a finite shared resource. If the site has several cameras or multiple wireless access points, a separate managed PoE switch is usually the cleaner expansion path. This also lets the firewall focus on security and routing while the access layer handles endpoint density.
A quotation request should therefore include ISP speeds, approximate users and devices, number of WAN links, VPN requirements, security services, PoE devices, existing switches, desired support term and expected growth. FourTeck Tanzania’s verified contact page specifically asks firewall buyers to share bandwidth, VPN, branch and security-service requirements. This makes the purchase conversation more precise and helps avoid choosing a firewall from model name or price alone.
FortiGate 70G PoE Dar es Salaam
In Dar es Salaam, FG-70G-POE can suit growing offices, professional firms, clinics, retail branches, logistics teams and other sites where internet security and network control must be consolidated at the edge. Urban offices often combine Microsoft 365 or Google Workspace, ERP or accounting systems, video meetings, Wi-Fi, IP phones, cloud applications and remote support. The firewall should be configured so these services do not all share one undifferentiated trusted network. VLAN segmentation can separate staff, guests, voice, cameras and management traffic, while policies define exactly which zones may communicate.
Dar es Salaam sites may also have access to multiple connectivity options. When two internet circuits are available, FortiGate Secure SD-WAN can be used to design health-aware link behavior. The important planning questions are which applications must remain available during an outage, whether inbound services depend on a specific public address, how VPN tunnels should fail over, and whether voice or video should prefer the lower-latency path. Testing these scenarios during commissioning is more valuable than simply connecting two WAN cables and assuming resilience.
PoE can simplify a small Dar es Salaam office when only a few powered endpoints are required. For example, a compact reception or branch could connect selected access points or phones without separate injectors. Yet larger offices should map endpoint count against the published 60 W budget and plan dedicated PoE switching when device density grows. Good rack organization, UPS protection and labeled cabling are particularly helpful because firewall, switch, ISP equipment and other infrastructure often share the same communications area.
For procurement, provide the current firewall model if this is a replacement, the intended FortiGuard services, expected VPN users, branch tunnels, internet bandwidth and any requirement for centralized logging. FourTeck Tanzania’s contact page lists Dar es Salaam contact information and accepts product-selection and quotation requests. A complete requirement makes it easier to compare appliance-only purchasing with an appropriate FortiCare and FortiGuard subscription bundle without assuming that every business needs the same service package.
FortiGate 70G PoE Mwanza
For Mwanza organizations, the FortiGate 70G PoE can be considered for branch security where stable connectivity, controlled access and straightforward expansion matter. A regional office, retail operation, service business, education site or healthcare environment may have staff systems, guest wireless, cameras, phones and cloud services using the same physical network. The firewall can enforce segmentation between these groups, but the switch and wireless design must carry the VLANs correctly. Security is therefore an end-to-end architecture rather than a feature that exists only inside the firewall.
Mwanza buyers should pay particular attention to WAN design if business applications depend heavily on cloud access or links back to headquarters. If a secondary ISP or alternate connection is available, define what successful failover means. Some organizations need ordinary browsing to recover quickly, while others need site-to-site VPN, VoIP, ERP or payment connectivity to remain usable. FortiGate SD-WAN policies can support these objectives when health checks and application priorities are configured around the actual services.
The four PoE/+ ports are useful when the branch is genuinely small. They may reduce power adapters for a handful of nearby compatible endpoints, but they do not eliminate the need for capacity planning. Camera networks and multi-AP wireless deployments can exceed the firewall’s shared PoE budget or physical port count quickly. A managed PoE switch provides more ports and a clearer access-layer design when the site expands. UPS sizing should also account for every device expected to remain powered during an interruption, not only the firewall.
Before requesting FG-70G-POE pricing for Mwanza, document user count, internet circuits, critical applications, remote users, VPN tunnels, VLANs, endpoint power requirements and anticipated growth. If the site is part of a wider Tanzanian network, include the other branch locations and current firewall standards. This gives the quotation process enough context to consider consistent FortiOS policy, licensing, logging and management rather than treating Mwanza as an isolated appliance purchase.
FortiGate 70G PoE Arusha
Arusha businesses in hospitality, tourism support, professional services, education, healthcare, retail and general commerce can evaluate FG-70G-POE when they need a compact security edge with room for structured policy. Guest access is an important example. A hotel office, training facility or customer-facing site should not place visitor devices on the same trusted segment as finance systems, management workstations or infrastructure administration. FortiGate policies can help isolate guest traffic while still allowing internet access, and managed switching plus properly designed Wi-Fi carries that segmentation throughout the site.
Remote access and branch connectivity may also matter in Arusha. Teams that need secure access to office resources should define who requires VPN, what applications they may reach and how authentication will be managed. Site-to-site VPNs should be planned with subnets, routing and failover in mind. Avoid broad rules that allow every remote network to reach every internal resource. A cleaner design maps access to business roles and keeps management interfaces restricted.
The PoE capability can be attractive in compact properties or satellite offices because it can power selected network endpoints without additional injectors. Still, wireless coverage should be determined by building layout and client density rather than by the number of PoE ports on the firewall. Thick walls, multiple floors, outdoor areas and busy guest zones can require several access points and dedicated switching. In those cases, use FG-70G-POE as the security gateway and size the LAN independently.
FourTeck Tanzania’s verified contact information includes Arusha and its general enquiry form can be used for firewall quotations. When contacting sales, include whether this is a new site, an upgrade or a replacement; specify ISP bandwidth, user count, Wi-Fi and camera environment, VPN, PoE endpoints and the FortiGuard services you expect. That information allows a more useful discussion of appliance, subscriptions and implementation scope while avoiding unsupported assumptions about stock or delivery timing.
FortiGate 70G PoE Dodoma
Dodoma organizations can use the FortiGate 70G PoE as the security edge for a compact headquarters department, branch office or distributed business site that needs policy-based internet access, VPN and SD-WAN. The first design task is to identify trust zones. Staff endpoints, guest wireless, servers, cameras, IP phones and infrastructure management should not automatically have unrestricted access to one another. VLANs and firewall policies can create clearer boundaries, helping reduce lateral exposure and making troubleshooting easier.
Where a Dodoma office connects to Dar es Salaam or other branches, standardization has operational value. Consistent naming, address plans, VPN templates, security profiles and backup procedures reduce the amount of site-specific knowledge technicians must retain. FortiGate’s common FortiOS platform can support that consistency. For larger multi-site environments, centralized management and analysis can be considered so policy changes and logs are not handled independently on every appliance.
PoE should be treated as a design convenience rather than unlimited access-layer power. Four ports can work well for a small number of compatible endpoints, while larger deployments should use appropriately sized PoE switches. Include power consumption, cable distance, UPS runtime and future endpoints in the calculation. If the firewall and attached PoE devices are all expected to survive short power interruptions, the UPS must support the combined load and not merely the firewall’s own consumption.
FourTeck Tanzania’s contact page identifies Dodoma among its office contacts and advises firewall buyers to provide bandwidth, VPN, branch and security-service details. A Dodoma quotation request should add current topology, WAN providers, expected growth and whether installation or migration assistance is needed. For replacement projects, configuration review is important: copying an old rule set unchanged can preserve years of obsolete objects and overly broad policies. A refresh is an opportunity to simplify the security design as well as upgrade hardware.
FortiGate 70G PoE UAE
UAE buyers can evaluate the same FG-70G-POE platform for branch offices, clinics, retail sites, professional firms and distributed operations that need FortiOS security and integrated PoE. The UAE-specific FourTeck Fortinet site already publishes a dedicated FortiGate 70G-POE page, which is useful for regional product comparison. For organizations operating in both Tanzania and the UAE, using the same firewall family can simplify policy templates, administrator training and branch-to-branch VPN planning, provided each site is independently sized for its traffic.
A UAE branch often has high-speed internet and heavy SaaS usage, so inspection throughput deserves more attention than raw firewall throughput. Teams should model encrypted web traffic, cloud productivity, video meetings, VPN and any published services. Dual-WAN designs should define application steering and failover behavior rather than simply balancing traffic. If a business has a central data center or cloud hub, routing and VPN topology should be designed consistently across all branches.
PoE can reduce adapters for selected access points, phones or cameras, but the same 60 W shared-budget principle applies. A busy UAE office with several Wi-Fi access points and many IP phones should normally use dedicated PoE switching. The firewall’s PoE ports are more compelling for compact branches or edge devices where four powered interfaces are enough. Confirm standards and endpoint consumption before finalizing the bill of materials.
For UAE-specific Fortinet information, visit FourTeck’s FortiGate 70G-POE UAE page or the broader Fortinet products UAE catalog. Cross-border procurement teams should still confirm the exact hardware, subscription term, deployment country and support expectations on each quotation instead of assuming one regional bundle applies everywhere.
FortiGate 70G PoE Uganda
Uganda organizations comparing Fortinet branch firewalls can consider FG-70G-POE when integrated PoE is useful and the published 70G performance class matches the inspected workload. For companies with operations in both Uganda and Tanzania, standardizing on FortiOS can simplify site-to-site VPN, administrator skills and policy design. Standardization should focus on architecture, not blindly on identical hardware; a larger headquarters and a small branch may require different models even when they use the same security platform.
Branch planning should cover internet resilience, internal segmentation, remote access and the services that remain critical during an ISP problem. If a site has two WAN connections, test health checks and failover for business applications. If the office depends on a tunnel back to a data center, confirm that the tunnel re-establishes over the alternate link and that routing behaves as intended. Logging and monitoring should also make it clear when a branch is running on backup connectivity.
PoE endpoints should be counted before purchase. A small office with a few access points or phones may benefit directly from the firewall’s four PoE/+ ports. A site with a camera estate or many desks should use dedicated switching. The security gateway can still control VLANs and inter-zone policy while the access switch provides port density and power. This separation generally gives a cleaner growth path.
FourTeck’s Uganda technology channel can support Uganda-facing product discussions, while Tanzania requirements can be routed through the verified Tanzania contact page. For regional companies, include all branch locations, WAN speeds, VPN topology, desired subscription term and management approach in the enquiry so the firewall design can be coordinated across borders.
FortiGate 70G PoE Kampala
Kampala offices frequently combine cloud applications, IP telephony, wireless access, guest connectivity and remote work. FG-70G-POE can provide the branch security edge for these services when the model is correctly sized. Separate business-critical networks from guest and IoT traffic, restrict administrative access and avoid broad any-to-any rules. A clear zone model makes future changes easier because new applications can be added to defined policy paths rather than to an unstructured flat LAN.
For businesses with multiple ISP circuits, Secure SD-WAN can help steer applications according to link quality and availability. A finance application, VoIP service and ordinary web browsing may have different sensitivity to latency or packet loss. Define the business priority first, then create health checks and rules around it. VPN and inbound services need additional attention because a change in public IP can affect connectivity even when outbound internet failover appears successful.
The PoE ports can be practical in a compact Kampala branch, especially where a few network devices need power and cabling simplicity is valuable. However, calculate total wattage and consider growth. If the business plans more wireless access points, IP phones or cameras later, install a managed PoE switch with adequate budget instead of designing to the firewall’s maximum from day one. UPS runtime should be calculated with the powered endpoints included.
A useful Kampala quotation request includes ISP bandwidth, users, remote workers, VPN tunnels, Wi-Fi AP count, PoE endpoints, VLANs, current firewall, desired FortiGuard services and expected growth. This also helps distinguish between appliance-only replacement and a project that needs configuration migration, policy cleanup, SD-WAN setup or broader LAN work.
FortiGate 70G PoE Arua
For an Arua branch, the value of FG-70G-POE may be the combination of compact security, VPN and limited PoE at one edge device. Smaller regional sites often need to connect securely to a head office while keeping local internet access available for cloud services. The design should decide whether traffic goes directly to the internet under local security policy, travels through a central site, or uses a hybrid approach. That choice affects bandwidth, resilience and the user experience.
WAN reliability should be treated as an application requirement. If a backup connection is available, test it under realistic conditions and document how the branch behaves when the primary circuit fails. VPN tunnels, DNS, authentication and cloud sessions can respond differently. FortiGate SD-WAN can provide the policy framework, but the correct thresholds and priorities depend on the links and applications used at the Arua site.
Integrated PoE can reduce equipment for a very small branch, but endpoint power demand and cable quality still matter. Four powered interfaces do not mean every connected device can consume maximum PoE+ power simultaneously. Use the shared budget as the design constraint. If a branch needs several cameras plus wireless and phones, a dedicated switch is the better access layer and gives more flexibility for future devices.
When Arua is part of a larger Uganda or East Africa deployment, consistent documentation is especially valuable. Record WAN addressing, VPN peers, VLANs, firewall objects, administrator roles, firmware and configuration backups. A standardized branch template can reduce troubleshooting time without forcing every site to have identical hardware. Include these multi-site requirements in the quotation so licensing and management can be planned at the same time as the appliance.
FortiGate 70G PoE Mbarara
Mbarara businesses evaluating a Fortinet firewall should begin with the traffic that must be protected. User count alone is not enough. A smaller team can generate substantial encrypted traffic through backups, cloud storage, video conferencing and line-of-business applications, while a larger team may have lighter usage. FG-70G-POE’s published security performance should therefore be compared with expected inspected throughput and future ISP upgrades, leaving operational headroom rather than sizing to the exact current peak.
Segmentation is another important branch requirement. Put guest Wi-Fi, cameras, voice, user devices and management interfaces into appropriate zones and permit only the flows they need. This improves security and makes troubleshooting more predictable. If the site uses FortiAP or FortiSwitch, Fortinet integration can support coordinated management, but compatibility and design should be confirmed for the exact models and firmware planned.
The PoE variant is useful when a handful of compatible endpoints can be served directly. For anything beyond a compact setup, calculate the total power budget and choose dedicated PoE switching. Consider UPS and environmental conditions as well. A security gateway that powers access points or phones becomes part of their power chain, so a power failure or overloaded budget can affect several services at once.
For a Mbarara quotation, provide the exact model reference FG-70G-POE, quantity, preferred subscription term, ISP speeds, WAN count, VPN needs and any installation or migration scope. If the firewall will connect back to Kampala or another headquarters, include the remote peer details and addressing plan. This helps the project team distinguish hardware supply from a complete branch-security deployment.
FortiGate 70G PoE Gulu
Gulu branch environments can use FG-70G-POE where a compact Fortinet security edge fits the network and a few PoE endpoints are useful. The firewall can protect direct internet access, establish VPN connectivity and enforce segmentation between user, guest and device networks. For branch operations, simplicity is valuable: policies should be named clearly, unused rules removed and configuration backups maintained so support does not depend on one administrator’s memory.
If connectivity is variable or a secondary link is available, define which services receive priority. Cloud ERP, voice, payment systems or VPN may deserve different treatment from software downloads or general browsing. SD-WAN can make those preferences explicit. Monitor link health and record failover events so recurring ISP problems can be separated from firewall or LAN issues.
For PoE, confirm both port count and wattage. The integrated ports can be a good fit for a small number of access points, phones or other compatible endpoints, but a growing site should not be constrained by the firewall’s access-layer capacity. Dedicated PoE switching allows more ports, easier endpoint expansion and potentially more flexible placement. Keep management access protected and use VLANs consistently across the switch and firewall.
Gulu buyers should include current network diagrams or a simple list of devices when requesting a quote. State ISP bandwidth, number of users, remote-access needs, branch VPN, PoE devices and security subscriptions. For multi-site organizations, also describe how Gulu relates to the rest of the network. This gives the supplier enough context to discuss FG-70G-POE as part of an architecture instead of quoting an appliance without understanding its workload.
FortiGate 70G PoE Kenya
Kenya businesses can consider FG-70G-POE for branch security when the PoE variant fits the physical design and the 70G performance class matches inspected traffic. The FourTeck FortiGate Firewall Kenya guide discusses model selection in terms of throughput, users, VPN and growth. For organizations with branches in Kenya and Tanzania, a common Fortinet architecture can simplify VPN and policy operations, while each branch remains sized for local bandwidth and device count.
Nairobi and other high-connectivity business sites may have fast fiber circuits, which makes security-service throughput important. Do not choose a firewall only because its raw stateful firewall figure exceeds the ISP speed. Consider IPS, application control, web filtering, malware inspection and encrypted traffic. Future bandwidth upgrades should be included so the appliance does not become the bottleneck soon after installation.
PoE planning follows the same rule: use the integrated ports where they simplify a compact branch, but move endpoint density to dedicated switching as the site grows. A business with multiple APs, IP phones and cameras can still benefit from the PoE model for a few strategic endpoints while a managed switch handles the rest. Confirm the total power requirement and UPS runtime as one system.
Cross-border businesses should also plan centralized logging, administrator access and configuration standards. Use named objects, consistent VLAN purposes and documented VPN addressing. Procurement requests should identify the deployment country for each appliance, subscription term and required support. This avoids ambiguity when a regional company is purchasing several Fortinet units for different jurisdictions.
FortiGate 70G PoE Kuwait
Kuwait buyers evaluating FG-70G-POE may be looking for a compact firewall that combines FortiOS security, SD-WAN, VPN and limited PoE connectivity. Branches with high-speed internet should model inspected traffic carefully. Cloud applications, encrypted web traffic, video meetings and remote access can place a different load on the security engine than ordinary routing. Leave headroom for growth and for security profiles that may be enabled after initial deployment.
Dual-WAN design can be valuable for offices that depend on continuous cloud access. Define link-health criteria and application priority, then test actual failover. Public-facing services and site-to-site VPN can require additional planning because they may depend on provider addressing. A successful design documents how users, tunnels and critical applications behave when each circuit is unavailable.
The four PoE/+ ports can serve a small number of compatible endpoints, but the published 60 W budget should be checked against device consumption. In a larger Kuwait office, dedicated PoE switches are usually more appropriate for phones, cameras and access points. The firewall can remain the policy and routing point while managed switching provides endpoint scale.
For regional procurement, FourTeck maintains a Kuwait technology channel. Include the exact FG-70G-POE model, quantity, license term, WAN speed, VPN and PoE requirements in the enquiry. If the same project includes Tanzania, keep country-specific delivery and support expectations explicit rather than assuming a single regional fulfillment model.
FortiGate 70G PoE Ghana
Ghana organizations can assess FG-70G-POE for secure branch connectivity, particularly where Fortinet is already used elsewhere in the business. A common platform can make site-to-site VPN, administrator training and policy templates easier to maintain. The hardware choice should still reflect each branch’s inspected bandwidth, interface needs, remote users and growth. A standard architecture is more useful than forcing one model into every site.
For Accra or other cloud-dependent offices, define application priorities and WAN resilience before deployment. If two internet links are available, FortiGate Secure SD-WAN can be configured around measured quality and business importance. VPN and DNS behavior should be tested during failover, and monitoring should alert administrators when the branch is using a backup path.
PoE is most useful in a compact branch with a few nearby endpoints. The integrated ports can reduce adapters and cabling complexity, but the shared power budget and four-port limit make dedicated switching more appropriate for larger camera, voice or Wi-Fi estates. Plan UPS capacity for the entire powered chain and keep switch/firewall VLAN configuration documented.
FourTeck’s Ghana channel provides a regional route for technology enquiries. Buyers should provide the exact model, subscription duration, users, ISP bandwidth, VPN, security services and endpoint requirements. For businesses operating in Ghana and Tanzania, include both sites in the design discussion so addressing and VPN architecture are coordinated from the start.
FortiGate 70G PoE Nigeria
Nigeria businesses with distributed branches can evaluate the FortiGate 70G PoE as a compact NGFW and SD-WAN edge. The most important sizing inputs are inspected traffic, WAN speed, user and device count, VPN, public services and future growth. Security subscriptions can change the workload materially, so compare the intended security profile with published threat-protection and NGFW performance rather than relying only on the 10 Gbps firewall figure.
Multi-link connectivity is often part of branch resilience planning. FortiGate SD-WAN can monitor links and steer applications, but configuration should reflect business priorities. Payment, ERP, voice, collaboration and general web traffic may have different tolerance for latency and loss. Test failover for VPN and inbound services as well as outbound browsing, and document which path is primary for each critical workload.
The PoE model is attractive when a small branch wants to power a few compatible devices from the firewall. Larger sites should use managed PoE switches to avoid port and wattage constraints. Segment cameras, guest Wi-Fi, phones and user networks so endpoint categories do not share unrestricted access. This also makes policy review easier as the branch expands.
For Nigeria-specific enquiries, use the FourTeck Nigeria channel. A procurement request should state FG-70G-POE, quantity, desired FortiCare/FortiGuard term, WAN links, users, VPN and PoE requirements. If appliances are being sourced for several African countries, list each destination separately so configuration, licensing and logistics expectations remain clear.
FortiGate 70G PoE Seychelles
Seychelles organizations in hospitality, professional services and distributed operations can consider FG-70G-POE where a compact security gateway and a few powered network interfaces fit the site. Hospitality environments in particular benefit from clear separation between guest access, staff systems, management networks, cameras and operational devices. The firewall can enforce inter-zone policy, while the switching and wireless layers must preserve the same VLAN structure across the property.
Internet resilience can be important for cloud booking, payment, communications and remote administration. If more than one WAN path is available, Secure SD-WAN can help define link health and application preference. The configuration should be tested under real failover conditions because VPN, DNS and cloud sessions may react differently. For remote islands or sites where technical visits require planning, good monitoring and configuration backups are especially valuable operational practices.
PoE can simplify a small office or communications room by powering a limited number of compatible endpoints. Larger properties with many access points, cameras and phones should use dedicated PoE switching with sufficient power and port density. UPS design should include firewall, switches and the endpoints that must stay available, and equipment should be installed with adequate ventilation and cable organization.
For a Seychelles quotation, include site type, users, guest-device expectations, internet links, VPN, Wi-Fi and camera environment, PoE endpoints and subscription requirements. If the organization also operates in Tanzania or other regional markets, describe the wider network so VPN addressing and security policy can follow a consistent template while still accommodating the unique connectivity and physical conditions of each site.
Licensing, FortiGuard and lifecycle planning
The hardware appliance and the security-service plan are separate procurement decisions that should be considered together. FortiGate can provide firewalling and networking functions as an appliance, while FortiGuard subscriptions add continuously updated security services according to the selected bundle. FortiCare plans provide support entitlements according to the purchased service level. Bundle names and inclusions can change, so the quotation should state the exact service package, term and support level instead of using a generic phrase such as “licensed firewall.”
Renewal planning should begin before expiry. Record contract numbers, registration ownership, expiry dates and the administrator responsible for renewal. For a multi-branch environment, aligning renewal dates can reduce administrative overhead, although commercial feasibility should be confirmed at quotation time. Also review whether the current security profile still matches the business. New cloud applications, additional branches, remote users or compliance requirements may justify a different service package or hardware review.
Firmware is part of lifecycle management as well. Maintain supported releases appropriate to the environment, back up configurations before changes and test important VPN or application workflows after upgrades. For critical branches, schedule changes during a controlled window and retain a rollback plan. Lifecycle discipline protects the value of the firewall long after the initial purchase.
Deployment and migration checklist
Before installation
Document WAN addressing, ISP handoff, VLANs, DHCP, DNS, public services, VPN peers, remote users, current policies, authentication, logging and PoE endpoints. Export the existing firewall configuration and record dependencies that may not be obvious from the rule base.
During cutover
Validate internet, DNS, critical SaaS, site-to-site VPN, remote access, inbound publishing, voice, guest access and management. Test both WAN paths if SD-WAN is used. Confirm that segmentation blocks traffic that should not cross between zones.
After handover
Save a known-good configuration, document firmware and subscriptions, define administrator roles, schedule backups and reviews, and record renewal dates. Monitor resource usage and inspected throughput so future capacity decisions are based on evidence.
Related FourTeck resources
Use the FourTeck Tanzania technology overview to understand how firewall, switching, Wi-Fi, voice, CCTV, servers and infrastructure fit together. Browse the Tanzania shop for published product listings, and use the Tanzania sales contact page for a tailored requirement. For regional Fortinet research, FourTeck also maintains dedicated resources for FortiGate 70G-POE in the UAE, FortiGate firewalls in Kenya, Uganda, Ghana and Nigeria.
FortiGate 70G PoE FAQs
Does FG-70G-POE include PoE ports?
Yes. Published model specifications identify four hardware-accelerated GE RJ45 PoE/+ ports with a 60 W PoE budget. Confirm the power requirement of every intended endpoint before final design.
What is the difference between FortiGate 70G and 70G PoE?
The PoE variant is intended for deployments that benefit from powered Ethernet interfaces. Port allocation and power characteristics differ, so compare the official model-specific hardware table rather than assuming the two appliances are physically identical.
Can FortiGate 70G PoE replace a PoE switch?
Only in small designs where four powered ports and the available shared PoE budget are sufficient. Larger phone, camera or Wi-Fi deployments generally need dedicated PoE switching for port density, power capacity and expansion.
Does it support SD-WAN and VPN?
The FortiGate 70G Series is positioned by Fortinet as a converged NGFW and Secure SD-WAN platform. FortiOS also supports VPN capabilities. Exact topology and performance should be validated for the intended configuration.
How should I size FG-70G-POE for Tanzania?
Provide ISP bandwidth, user and device count, security profiles, encrypted traffic, VPN, VLANs, public services, PoE endpoints and expected growth. Compare the resulting workload with vendor-published inspected-throughput figures, leaving operational headroom.
What should I include in a quote request?
Include model and quantity, deployment city, WAN speeds, number of links, users, VPN requirements, PoE endpoints, existing firewall, desired FortiCare/FortiGuard term, installation scope and target timeline. Avoid assuming current stock or price until FourTeck confirms the quotation.
Quotation checklist and decision recap
Before requesting FortiGate 70G PoE pricing, prepare: exact quantity; ISP bandwidth and expected upgrades; primary and backup WAN details; users and devices; remote-access users; site-to-site VPN peers; VLANs; public services; required security inspection; FortiGuard and FortiCare term; PoE endpoint models and wattage; switching and Wi-Fi environment; logging requirements; current firewall; migration window; and whether configuration, installation or post-deployment support is required.
FG-70G-POE is most compelling when a branch needs Fortinet NGFW and Secure SD-WAN functions plus a small number of powered Ethernet endpoints. The four PoE/+ ports can simplify compact installations, while larger networks should pair the firewall with managed PoE switching. Published performance makes the platform relevant to substantial branch workloads, but the correct decision depends on inspected traffic and enabled services rather than the headline firewall number.
For Tanzania, the next practical step is to send FourTeck the network requirement and request a current quotation. Pricing, availability, subscription bundles, delivery and implementation scope should be confirmed at the time of enquiry because they are commercial variables, not fixed product specifications.
Plan your FG-70G-POE deployment with FourTeck Tanzania
Share your users, internet bandwidth, WAN links, VPN, PoE endpoints, current firewall and required security services. FourTeck can use those inputs to prepare a more relevant product and project discussion for your Tanzania branch or multi-site environment.




Reviews
There are no reviews yet.