
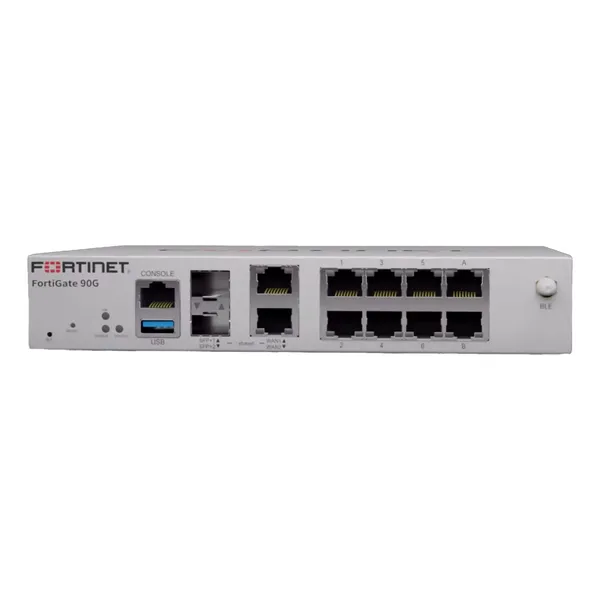
FortiGate 90G (FG-90G) Tanzania
FortiGate 90G is a Fortinet next-generation firewall and Secure SD-WAN appliance designed for distributed enterprise sites that need security and networking functions in one platform. Fortinet positions the 90G series around converged networking and security through FortiOS, FortiGuard AI-powered security services and Security Fabric integration. For Tanzania organizations, the practical buying question is not simply whether the appliance has a high headline firewall figure; it is whether its inspected throughput, VPN capacity, interfaces, subscription package and management approach fit the real network.
FortiGate 90G Overview and Verified Capabilities
Fortinet introduced the FortiGate 90G as an SP5-accelerated secure networking appliance. Official Fortinet material lists firewall throughput of up to 28 Gbps, IPsec VPN throughput of up to 25 Gbps, IPS throughput of 4.5 Gbps, NGFW throughput of 2.5 Gbps and threat-protection throughput of 2.2 Gbps. These values are laboratory performance figures under defined test conditions, and actual deployment performance varies with traffic mix, enabled security services, inspection depth, logging, encryption, policy design and FortiOS configuration. Buyers should therefore size the appliance against the services they plan to enable rather than comparing only raw firewall throughput.
The 90G is particularly relevant where a branch or regional office needs internet-edge protection, multiple WAN connectivity, site-to-site IPsec VPN, application-aware policies, web and DNS security, intrusion prevention, malware protection, segmentation and centrally coordinated security. Secure SD-WAN capabilities can help organizations use multiple connectivity links more intelligently, while Fortinet’s Security Fabric approach can connect the firewall with compatible management, switching, wireless, endpoint and analytics components.
Secure Branch Edge
Use policy control, application visibility, intrusion prevention and FortiGuard services to protect users and business applications at an office internet edge.
Secure SD-WAN
Plan multiple WAN links around application priorities, link health and branch connectivity while maintaining security policy on the same FortiOS platform.
VPN Connectivity
Build encrypted IPsec connectivity between branches, headquarters, data centres and compatible cloud environments, with design based on real tunnel and traffic requirements.
FortiGate 90G Technical Specifications
| Specification | FG-90G | Buying Consideration |
|---|---|---|
| Firewall throughput | Up to 28 / 28 / 27.9 Gbps | Raw firewall performance is not the same as full threat inspection. |
| IPsec VPN throughput | Up to 25 Gbps | Actual performance depends on encryption, packet sizes and design. |
| IPS throughput | 4.5 Gbps | Useful sizing figure where intrusion prevention is continuously enabled. |
| NGFW throughput | 2.5 Gbps | Relevant for firewall, IPS and application-control workloads. |
| Threat protection | 2.2 Gbps | A more useful reference for security-heavy internet traffic than raw firewall speed. |
| Platform | FortiOS / SP5 architecture | Confirm supported FortiOS release and required features before deployment. |

FortiGuard, FortiCare and Licensing Planning
A FortiGate purchase should be scoped as hardware plus the services required by the security policy. FortiGuard services can provide capabilities such as intrusion-prevention intelligence, web and DNS security, malware protection and other subscription-based protections depending on the selected bundle. FortiCare provides support entitlements according to the chosen service level and term. Bundle names, service inclusions and order codes can change, so a quotation should state the exact hardware model, support term, security-service package and any cloud management or logging requirement rather than using a generic phrase such as “licensed firewall.”
Organizations replacing an older FortiGate should also review configuration migration, unsupported legacy objects, VPN settings, interface mapping, policy cleanup, firmware compatibility and whether the new deployment needs additional headroom. A replacement is an opportunity to remove obsolete rules and document the intended network zones rather than copying every historical setting without review.
FortiGate 90G Tanzania
For organizations sourcing FortiGate 90G in Tanzania, the strongest procurement process starts with the network requirement. A company may have a headquarters internet edge, several branch offices, cloud-hosted applications, remote staff, IP telephony, guest Wi-Fi, CCTV, ERP access and VPN connections sharing the same gateway. These workloads have different security and availability needs. Before requesting an FG-90G quotation, document the primary and backup internet speeds, expected growth, number of VLANs, public services, branch tunnels, remote-access requirements and whether encrypted traffic inspection will be used. This gives the supplier enough information to discuss whether the 90G has suitable security-performance headroom.
Tanzania deployments may also need to account for varied connectivity. A site can combine fibre, fixed wireless, microwave or other provider links depending on the location and business. Secure SD-WAN can be useful when more than one WAN circuit is available because policies can be designed around link health and application needs. That does not eliminate the need for good ISP diversity, power protection or sensible routing design. For critical sites, buyers should separately evaluate high availability, redundant upstream connectivity and operational procedures for outages.
Licensing deserves equal attention. Buyers should decide which FortiGuard protections are required, how long the subscription should run and whether centralized logging or management is part of the project. Organizations with multiple FortiGate appliances may benefit from a consistent policy and renewal strategy rather than purchasing each branch independently. FourTeck can help structure the quotation around appliance, service term and deployment requirements without implying stock or delivery commitments before supplier confirmation.
FortiGate 90G (FG-90G) Dar es Salaam
Dar es Salaam businesses often operate dense, internet-dependent environments where a firewall protects much more than ordinary web browsing. Corporate offices, logistics companies, financial operations, hospitality groups, retailers and professional-service firms can have cloud applications, payment traffic, video meetings, voice systems, remote support sessions and partner VPNs crossing the same edge. The FortiGate 90G can be evaluated as a consolidated security gateway where the organization needs application-aware controls, threat inspection, encrypted site connectivity and multi-WAN policy in a compact appliance.
A Dar es Salaam buyer should provide peak internet utilization rather than only contracted ISP speed. If a business has two WAN links, explain whether the second circuit is intended purely for failover or should carry active production traffic. Also identify business-critical applications that need preferred routing. Secure SD-WAN policies can then be planned around actual application and link requirements. For organizations using cloud ERP, Microsoft 365, hosted voice or regional data centres, latency and route quality can matter as much as nominal bandwidth.
Network segmentation is another practical reason to consider a capable NGFW. Separate staff, server, guest, voice, CCTV, payment and management networks can reduce unnecessary lateral access when policies are designed carefully. The FG-90G should be sized with these inspection requirements in mind. If the site is expected to expand substantially, the quotation process should compare future inspected throughput and interface requirements before purchase, rather than relying on a user-count rule alone.
FortiGate 90G (FG-90G) Mwanza
Mwanza organizations considering the FortiGate 90G may be protecting a regional office, trading operation, healthcare facility, educational network, hospitality site, warehouse or multi-branch business. In these environments, reliable connectivity to cloud systems and headquarters can be as important as perimeter protection. An FG-90G deployment can combine firewall policy, IPsec VPN and secure SD-WAN so that branch traffic is governed through one FortiOS platform rather than separate routing and security devices.
The procurement discussion should identify whether Mwanza is an independent site or part of a wider Tanzania network. For a branch, define where internet traffic should exit, whether business applications are local or centralized, and whether tunnels terminate in Dar es Salaam, another country or a cloud environment. This determines routing, VPN and resilience requirements. Where two internet connections are available, health checks and failover behaviour should be tested against actual business applications instead of assuming that every session will move transparently during a provider outage.
Operational simplicity also matters. A firewall is only useful when policies, subscriptions, firmware and logs are maintained. Buyers should plan who will administer the appliance, how configuration backups will be handled, how alerts are reviewed and how FortiGuard and FortiCare renewals will be tracked. For organizations without a dedicated security team at every site, centralized administration and documented change control can make a multi-branch deployment easier to support over time.
FortiGate 90G (FG-90G) Arusha
Arusha has a diverse mix of tourism, hospitality, professional, education, NGO and commercial networks. These environments can place unusual demands on an edge firewall because guest internet, staff systems, reservation platforms, payment applications, voice services, cameras and remote administration may coexist at the same property or campus. The FortiGate 90G can be considered when the security design needs stronger segmentation and inspected throughput than a basic branch router provides.
Hospitality and guest-facing sites should separate public access from operational systems and should avoid treating the firewall as a substitute for proper wireless design. If FortiAP or other managed wireless infrastructure is part of the project, the security policy can be coordinated with VLANs and access rules, but radio coverage, PoE capacity and switching still need separate planning. Similarly, CCTV networks can create substantial continuous traffic, so the path of camera traffic and remote viewing should be understood before applying inspection policies indiscriminately.
For Arusha offices connecting to Dar es Salaam or international headquarters, IPsec VPN design should document tunnel endpoints, encryption requirements, routing, failover and which subnets are permitted. Organizations should also consider how DNS, web filtering and application control policies affect cloud services used by staff. A good quotation therefore includes more than the appliance model: it identifies the FortiGuard package, support term, required transceivers or accessories and the expected configuration scope.
FortiGate 90G (FG-90G) Dodoma
Dodoma buyers may be evaluating the FortiGate 90G for administrative offices, education, professional services, public-facing organizations and enterprises that need secure connectivity between the capital and other locations. The appliance is relevant where firewall policy, VPN, application visibility and WAN resilience need to be consolidated. Procurement teams should begin by separating mandatory security requirements from optional future capabilities so the selected subscription and deployment scope are clear.
If the network carries sensitive administrative data, segmentation should be designed around trust boundaries rather than convenience. User networks, servers, management interfaces, guest devices and externally reachable services should have explicit policy relationships. Security profiles can then be applied according to risk and performance requirements. This is preferable to enabling every inspection feature identically on every flow without understanding the business purpose.
Dodoma sites that rely heavily on connections to other Tanzania offices should also plan the WAN as part of the security project. Document primary and backup providers, public addressing, VPN dependencies and acceptable outage behaviour. For important services, test failover and recovery rather than waiting for an incident. The FG-90G offers substantial vendor-rated IPsec performance, but tunnel design, ISP quality and application behaviour remain important factors in real-world results.
FortiGate 90G (FG-90G) UAE
UAE-based headquarters and regional IT teams frequently manage branches across Africa, making the FortiGate 90G relevant as a standardized branch-security platform. A company can use consistent FortiOS policy concepts across sites while adapting interfaces, WAN providers, local addressing and security profiles to each location. For procurement teams coordinating Tanzania from the UAE, the key is to keep hardware, FortiGuard term, FortiCare entitlement and deployment responsibilities clearly documented for every site.
Cross-border projects should avoid assuming that one configuration can be copied unchanged everywhere. ISP handoffs, public IP arrangements, local applications, voice systems and cloud routes differ. Use templates where they improve consistency, but validate site-specific routing and security needs. Central management and analytics may also be worth evaluating when the organization operates several FortiGate appliances.
FourTeck’s UAE technology portal and Fortinet UAE specialist site provide regional routes for organizations coordinating Gulf and Africa security procurement. These links are useful for UAE-led projects, while Tanzania requirements should still be scoped against the actual branch environment.
FortiGate 90G (FG-90G) Uganda
Uganda organizations can evaluate the FortiGate 90G for secure branch internet, VPN, application control and multi-WAN deployments. For businesses operating both Uganda and Tanzania, using the same firewall family can simplify policy concepts and support procedures, but each site should still be sized independently. Bandwidth, user activity, encrypted traffic, local applications and the number of security services enabled determine the practical workload.
Before procurement, identify whether the appliance will terminate site-to-site tunnels, support remote users, inspect web traffic, segment internal networks and control guest access. If multiple WAN providers are planned, specify whether active-active usage or standby failover is desired. This helps define SD-WAN rules and monitoring expectations. A branch with moderate raw bandwidth but heavy security inspection can have a different sizing requirement from a site with faster internet and minimal inspection.
Organizations coordinating East African sites can use the FourTeck Uganda portal for Uganda-focused procurement discussions while maintaining a consistent regional security plan. Subscription renewal dates should be recorded centrally so FortiGuard protection and support entitlements do not become fragmented across branches.
FortiGate 90G (FG-90G) Kampala
Kampala offices often depend on cloud applications, inter-branch VPNs, online transactions and collaboration services. A FortiGate 90G project can address these needs through one security gateway, but design should begin with traffic and business priorities. Identify the applications that cannot tolerate poor link quality, the systems that require inbound access and the departments that should be segmented from one another.
For multi-link Kampala deployments, Secure SD-WAN can monitor WAN conditions and apply application-aware steering policies. The implementation should still include sensible DNS design, routing, provider diversity and documented failover tests. Security teams should decide where SSL inspection is appropriate and account for its performance and certificate-management implications. Vendor throughput figures provide useful comparison points but are not a substitute for workload sizing.
A complete quotation should state the FG-90G appliance, exact service bundle, subscription term and any management, logging or installation requirement. If the Kampala site is part of a Tanzania-Uganda network, include tunnel topology and expected inter-site traffic so the VPN design can be reviewed before purchase.
FortiGate 90G (FG-90G) Arua
For an Arua branch, firewall procurement may be driven as much by connectivity resilience as by threat protection. A distributed organization should document which applications must remain available when the primary WAN degrades and whether a secondary link is available. The FortiGate 90G’s Secure SD-WAN capabilities can form part of that design, allowing security and WAN policy to operate on the same appliance.
Remote branches benefit from standardized configuration and clear administration. Define VLANs, permitted management sources, VPN peers, security profiles and backup procedures before deployment. Where technical staff are centralized elsewhere, remote management must itself be secured and change procedures should be documented. Logging and alerting should provide enough visibility to distinguish an ISP issue from a firewall or application problem.
The FG-90G provides significant performance headroom for many branch scenarios, but the appropriate model should be confirmed against actual inspected traffic and growth. Procurement should also include the correct FortiCare and FortiGuard term rather than treating subscriptions as an afterthought.
FortiGate 90G (FG-90G) Mbarara
Mbarara businesses looking for a Fortinet firewall may need to protect retail, education, healthcare, hospitality, distribution or professional-service networks. These sites can combine cloud applications, guest connectivity, payment systems, IP cameras and branch VPNs. The security architecture should separate these workloads logically so a device in one zone does not receive unnecessary access to another.
The FortiGate 90G can enforce segmentation policies while also providing internet security and VPN services. Buyers should map required physical and logical interfaces before installation, including WAN circuits, LAN trunks and management access. If the network will grow, include planned switches, access points, new branches and internet upgrades in the sizing discussion so the appliance is not selected only for today’s minimum load.
Licensing should match the organization’s operational capacity. Advanced security services are valuable when they are configured, monitored and renewed correctly. A quotation discussion should therefore include who will manage policy, how alerts are handled and whether centralized reporting is required, in addition to the firewall hardware itself.
FortiGate 90G (FG-90G) Gulu
Gulu deployments may involve branch connectivity to a central office, protected internet access for staff and secure access to hosted systems. The FG-90G can support this role with firewall, VPN and security inspection capabilities. For remote locations, the design should emphasize recoverability: configuration backups, documented WAN settings, secure administrative access and tested VPN failover are often as important as the initial installation.
Where two providers are available, define the business purpose of each link. Some organizations want automatic failover, while others want both links active with application-based routing. Secure SD-WAN policies should reflect these goals and should be tested under realistic conditions. Voice and interactive applications may react differently to link changes than ordinary web sessions.
A Gulu quotation should identify appliance and subscription details precisely. If the firewall is part of a larger East African rollout, standard naming, address plans, policy templates and renewal tracking can reduce administrative complexity while still allowing local network differences.
FortiGate 90G (FG-90G) Kenya
Kenya buyers frequently compare FortiGate models for branch offices, headquarters and distributed business networks. The 90G sits in a performance class that can be attractive where organizations want substantial IPsec capability and stronger inspected throughput than entry-level appliances. Selection should nevertheless be based on enabled services and traffic profile rather than a simple model hierarchy.
For companies linking Kenya and Tanzania, IPsec tunnels can protect inter-site traffic while SD-WAN policies can help manage multiple internet connections. The network team should document whether applications are hosted in Nairobi, Dar es Salaam, a public cloud or another regional data centre. This influences routing, latency and failover decisions. Security policies should also account for local breakout versus centralized internet access.
The FourTeck Kenya portal is relevant for Kenya-focused procurement, while cross-border buyers can align appliance bundles and renewal terms across both markets. Price comparisons should always confirm whether a listing is hardware-only or includes FortiGuard and FortiCare services, because those are materially different commercial configurations.
FortiGate 90G (FG-90G) Kuwait
Kuwait-headquartered organizations with Africa operations may use a standardized FortiGate architecture for branch security and encrypted connectivity. The FG-90G can be considered for offices where secure internet, VPN, segmentation and SD-WAN are required in one appliance. Central IT teams should define a baseline configuration while retaining enough flexibility for each country’s ISP and application environment.
Cross-regional procurement should state exact support and subscription terms, because a hardware model alone does not describe the complete security service. Management, logging and renewal ownership should be assigned before rollout. If high availability is required, that must be designed and quoted explicitly rather than assumed from the base appliance.
The FourTeck Kuwait portal offers a regional route for Kuwait-linked projects. Organizations coordinating Tanzania branches from Kuwait should provide the local WAN, VPN and security requirements for each site so the final configuration is technically appropriate.
FortiGate 90G (FG-90G) Ghana
Ghana organizations evaluating the FG-90G may be looking for stronger branch security, secure remote connectivity or a replacement for an older firewall. A proper assessment should review current WAN bandwidth, peak traffic, VPN usage, security subscriptions and expected growth. If the organization is replacing an existing FortiGate, migration planning should include policy cleanup and interface mapping rather than blindly importing every historical rule.
Distributed businesses can use IPsec VPN to connect Ghana with Tanzania or other regional sites. The design should document tunnel topology and decide whether internet access breaks out locally or traverses a central location. For multi-WAN sites, SD-WAN can provide policy-based path selection, but provider diversity and tested failover remain essential.
The FourTeck Ghana portal supports Ghana-focused technology enquiries. Regional organizations can use a consistent procurement checklist covering appliance, FortiGuard, FortiCare, management and deployment scope across locations.
FortiGate 90G (FG-90G) Nigeria
Nigeria’s large and varied enterprise market creates many possible FortiGate 90G use cases, from regional offices and professional services to retail, logistics and distributed corporate networks. The appliance can combine NGFW controls, VPN and Secure SD-WAN, but network teams should establish the required security posture before choosing a bundle. A site using extensive threat inspection and encrypted traffic inspection should be sized differently from one using mostly routing and basic firewall policy.
Multi-provider internet is common in resilience-focused designs. SD-WAN can help steer applications according to link conditions, yet the implementation should account for public addressing, inbound services, DNS and session behaviour during failover. Business-critical cloud and voice applications should be tested across expected outage scenarios.
The FourTeck Nigeria portal is a relevant regional resource for Nigeria procurement discussions. Companies operating in Nigeria and Tanzania can align model selection, subscription terms and policy standards while still validating each site’s unique connectivity and traffic requirements.
FortiGate 90G (FG-90G) Seychelles
Seychelles organizations may need a compact but capable security gateway for hospitality, professional services, government-related operations, education or multi-site businesses. Connectivity characteristics and the cost of resilient links can make careful WAN planning particularly important. The FortiGate 90G can combine firewall security and SD-WAN functions so multiple links can be managed through one policy framework.
Hospitality and guest environments should keep public access separated from operational systems, payment networks, management interfaces and staff resources. The firewall can enforce policy boundaries, while switching and wireless design must provide the corresponding VLAN structure. If VPN connections link Seychelles to Tanzania or other regional offices, document bandwidth expectations and which services traverse the tunnel.
Procurement should include subscription and support planning from the start. The correct quote depends on security services, term length, management needs and accessories as well as the appliance. Regional availability and logistics should be confirmed at quotation time rather than assumed from a generic product listing.
FortiGate 90G Deployment and Integration Guidance
A successful deployment starts with a network diagram and a policy objective. Record WAN circuits, public IPs, internal VLANs, servers, wireless networks, voice systems, cameras, branch peers and cloud destinations. Decide which traffic requires inspection and which systems need inbound access. Define administrator roles and secure management paths. Where existing firewalls are being replaced, review policies for obsolete objects and duplicate rules before migration.
For multi-WAN designs, establish measurable service-level criteria such as latency, jitter and packet loss for applications that need them. Avoid designing failover around a single ping target. For VPN, document routing and overlapping address issues early. For segmentation, use clear zones and least-necessary access rather than broad any-to-any rules. For logging, decide how long information needs to be retained and whether local, cloud or centralized analytics are required.
Fortinet Security Fabric integration can extend visibility and coordination with compatible Fortinet products. This can be useful for organizations that want the firewall to work with switching, wireless, endpoint, management or analytics components, but each integration should be chosen because it solves a real operational need. The FourTeck Africa portal can support broader regional security discussions for multi-country projects.
Who Should Consider the FortiGate 90G?
The FG-90G is worth evaluating for growing branches, regional offices and distributed enterprise sites that need more than basic perimeter filtering. It can be suitable where organizations require site-to-site IPsec, multiple WAN links, application-aware controls, intrusion prevention, web security and centralized Fortinet integration. It may also be a logical refresh candidate for an older FortiGate when the existing appliance no longer provides enough inspected throughput or current platform capability.
It should not be selected from a generic user-count chart alone. A small organization with very high bandwidth and deep inspection can demand more firewall capacity than a larger office with light internet use. Conversely, a site with modest bandwidth but complex segmentation and many VPN relationships may care more about policy and interface requirements. Share these details during quotation so the model can be reviewed in context.
FortiGate 90G Quotation Checklist
For a useful quotation, provide the destination country and city, number of appliances, current firewall model if this is a replacement, primary and backup WAN speeds, approximate peak traffic, number of sites, site-to-site VPN requirements, remote-user requirements, number of VLANs, required security services, preferred FortiCare/FortiGuard term, logging and management needs, high-availability requirement, rack or mounting requirement and any SFP/SFP+ connectivity. Also state whether configuration migration or new policy design is expected.
FortiGate 90G FAQs
What is the FortiGate 90G?
It is a Fortinet next-generation firewall and Secure SD-WAN appliance designed for distributed enterprise and branch security use cases, running FortiOS and supporting FortiGuard security services.
What is the FG-90G firewall throughput?
Fortinet publishes up to 28 Gbps firewall throughput for the 90G series. Security-service throughput is lower: official figures include 4.5 Gbps IPS, 2.5 Gbps NGFW and 2.2 Gbps threat protection. Real performance depends on configuration and traffic.
Does FortiGate 90G support IPsec VPN?
Yes. Fortinet publishes up to 25 Gbps IPsec VPN throughput under its specified test conditions. Tunnel architecture, encryption, WAN quality and traffic mix affect real deployments.
Does FortiGate 90G include Secure SD-WAN?
The FortiGate platform integrates Secure SD-WAN capabilities with FortiOS. Organizations can use these capabilities in multi-WAN designs, subject to correct configuration and network planning.
Do I need FortiGuard and FortiCare?
The required package depends on the security and support functions your organization needs. Confirm the exact service bundle and term on the quotation because hardware-only and bundled configurations are different purchases.
Can the FG-90G replace an older FortiGate?
Potentially, but replacement should be based on current traffic, inspection, interfaces, VPN, policy and future-growth requirements. Configuration migration should include a review rather than an automatic copy of obsolete settings.
Decision Recap
Choose the FortiGate 90G discussion when you need a modern branch or distributed-enterprise firewall with high raw firewall and IPsec performance, meaningful inspected-security capacity, Secure SD-WAN and Fortinet ecosystem integration. Before purchase, validate the expected threat-inspected traffic, WAN architecture, VPN topology, interface requirements, subscription package, management approach and growth horizon. This produces a more defensible firewall decision than selecting by price or headline throughput alone.
Consult FourTeck About FG-90G Tanzania
Share your internet bandwidth, user environment, branch count, VPN requirements, security-service expectations and preferred subscription term. FourTeck can use these details to prepare a more relevant FortiGate 90G quotation discussion and identify configuration items that should be confirmed before procurement.




Reviews
There are no reviews yet.