
FortiGate 901G (FG-901G) Tanzania
FortiGate 901G is built for organizations that need enterprise-scale firewalling, encrypted connectivity, application visibility and security inspection without turning the network edge into a bottleneck. Fortinet positions the 900G family for enterprise campus, data-center and large distributed-network requirements. The FG-901G combines purpose-built NP7 and CP9 security processors with high-speed interfaces and onboard storage, making it a practical platform for headquarters, internet edges, aggregation points and security architectures where throughput, session scale, redundancy and operational visibility all matter.

FortiGate 901G verified platform highlights
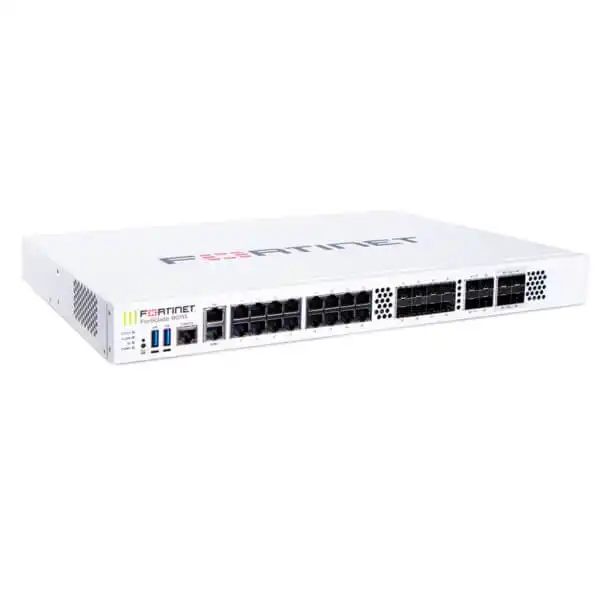
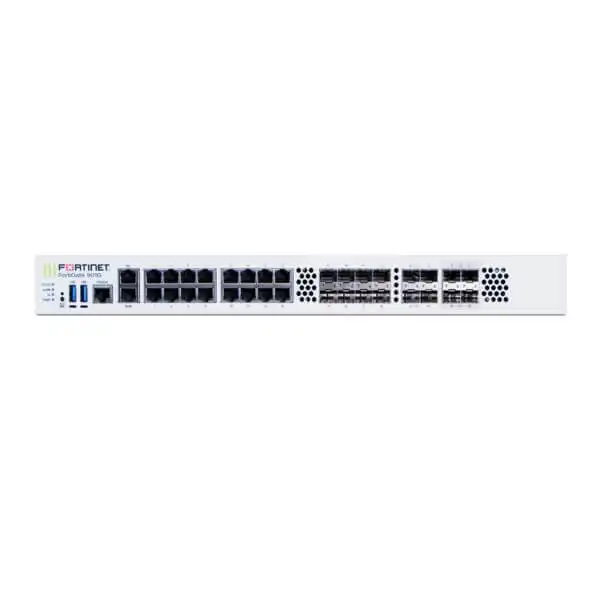
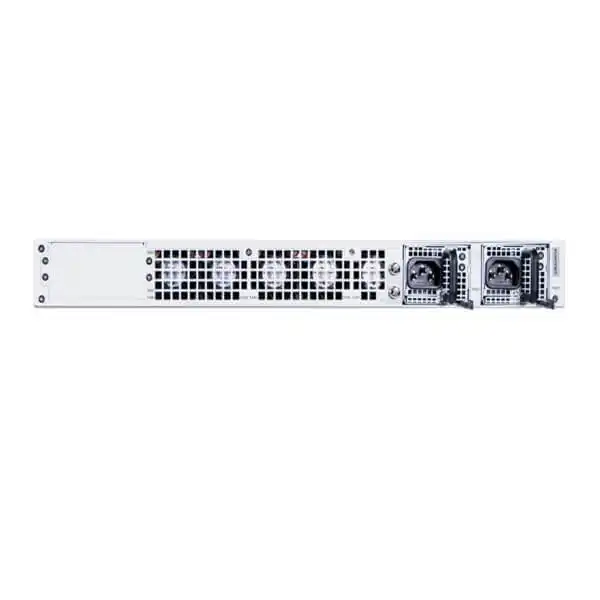
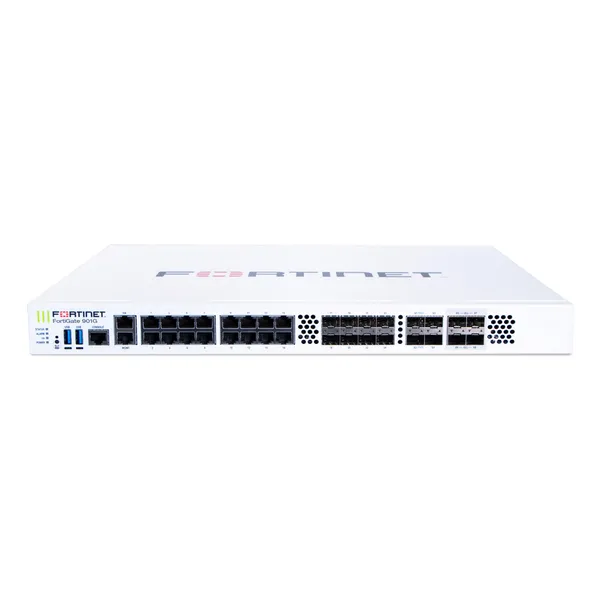
Fortinet’s published FortiGate 900G Series data identifies FG-901G as the storage-equipped model in the family. It provides four 25GE SFP28 slots, four 10GE SFP+ slots, seventeen GE RJ45 ports including one management port and sixteen switch ports, one 2.5GE HA port, and eight GE SFP slots. The appliance uses Fortinet NP7 and CP9 acceleration, includes two 480 GB onboard SSDs and dual AC power supplies. Fortinet also publishes a DC-powered FG-901G-DC variant. These physical characteristics make the platform particularly relevant where a firewall must connect multiple network zones, high-speed uplinks, server segments, WAN circuits or switching infrastructure while retaining dedicated management and high-availability connectivity.
Published Fortinet performance material for the 901G lists firewall throughput up to 164 Gbps, IPsec VPN throughput up to 55 Gbps, SSL inspection throughput up to 16.7 Gbps, 16 million concurrent sessions and up to 720,000 new connections per second under Fortinet’s stated test conditions. Current Fortinet product material should always be checked against the exact FortiOS release, enabled inspection functions, packet profile and security-service configuration because real deployments differ from laboratory tests. Procurement teams should therefore size the appliance around inspected traffic rather than relying only on raw firewall throughput.
Published maximum firewall throughput under Fortinet test conditions.
Published IPsec VPN throughput for high-capacity encrypted links.
Onboard SSD storage distinguishes the FG-901G from the FG-900G.
Four SFP28 slots support high-speed network and aggregation designs.
What the FG-901G solves
Large networks rarely have a single security problem. They have fast internet circuits, east-west segmentation, remote branches, cloud applications, partner VPNs, remote users, public services, compliance logging and business systems competing for reliable connectivity. A high-capacity next-generation firewall can consolidate policy enforcement around these flows. FortiGate uses FortiOS to combine firewall policy, application control, intrusion prevention, VPN, secure SD-WAN and integration with the wider Fortinet Security Fabric. Organizations can use this architecture to reduce separate network and security control points while keeping segmentation and inspection close to the traffic path.
The 901G is particularly relevant when local storage is useful for logging or operational requirements and when the interface mix must accommodate high-speed fiber, Gigabit fiber and copper segments. It can also participate in high-availability designs. A correct deployment should consider redundancy beyond the appliance itself: dual power feeds, upstream and downstream switch diversity, ISP diversity, routing design, transceiver compatibility, rack power, cooling, configuration backups, monitoring and subscription continuity.
Technical specification guide
| Model | FortiGate 901G / FG-901G |
| High-speed interfaces | 4 × 25GE SFP28 and 4 × 10GE SFP+ |
| Gigabit interfaces | 17 × GE RJ45 and 8 × GE SFP |
| HA interface | 1 × 2.5GE HA port |
| Acceleration | Fortinet NP7 and CP9 |
| Local storage | 2 × 480 GB onboard SSD |
| Power | Dual AC PSU; separate FG-901G-DC model published by Fortinet |
| Firewall throughput | Up to 164 Gbps, subject to Fortinet test methodology |
| IPsec VPN | Up to 55 Gbps, subject to Fortinet test methodology |
| Concurrent sessions | Up to 16 million in published Fortinet material |
Secure SD-WAN, VPN and enterprise segmentation
The FG-901G can serve as more than an internet firewall. Fortinet Secure SD-WAN capabilities can combine security and application-aware WAN steering, which is useful when a headquarters or data center terminates multiple carrier circuits or aggregates branch connectivity. IPsec VPN can protect site-to-site traffic, while segmentation can separate users, servers, guest networks, voice, operational systems and administrative zones. Organizations should design policies around least privilege and business dependency rather than simply reproducing old flat-network rules on new hardware.
For multi-site deployments, central management and logging can become as important as appliance throughput. FortiManager and FortiAnalyzer can be considered where administrators need centralized policy workflows, configuration governance, analytics or longer-term reporting. The exact architecture should reflect the number of FortiGates, retention requirements, administrator roles and compliance obligations. Buyers should include these operational requirements in the quotation stage instead of treating management and logging as afterthoughts.
FortiGuard subscriptions and lifecycle planning
The hardware appliance provides the platform, while many advanced security functions depend on appropriate FortiGuard services and FortiCare support. Subscription selection should be based on the controls the organization intends to operate, the required support level and the desired term. Procurement teams should request a quote that clearly identifies hardware, service bundle, FortiCare term, any central management or analytics components, transceivers, implementation scope and renewal dates. This avoids a common problem where a project compares appliance prices without comparing the security services included in each proposal.
Renewal planning matters because threat-intelligence and security-service continuity affects the value of a next-generation firewall. Keep contract ownership, serial information, renewal dates and support contacts documented. Before a major FortiOS upgrade, review release notes, compatibility, backups, high-availability procedure and change windows. For broader Fortinet regional information, buyers can review FourTeck’s Fortinet security resource for UAE deployments, while African projects can also reference FourTeck IT Solutions Africa for related infrastructure context.
FortiGate 901G Tanzania
For Tanzania organizations, the FortiGate 901G is most relevant where the security gateway must protect a substantial user population, fast internet links, data-center services, a large campus or multiple connected sites. Procurement should begin with measured traffic rather than a simple user-count rule. Document current and expected WAN bandwidth, peak traffic, TLS inspection requirements, VPN load, public applications, internal segmentation, number of branches, logging needs and growth over the planned hardware lifecycle. The FG-901G has considerable raw firewall capacity, but security design should focus on the throughput of the inspection features that will actually be enabled.
Tanzania deployments may involve headquarters connectivity, branch VPNs, cloud services, Microsoft 365 or Google Workspace traffic, ERP systems, voice, CCTV, remote access and internet-facing services. These workloads should be classified before migration so that the new firewall policy is understandable and auditable. Where two or more ISP circuits are used, Secure SD-WAN can be evaluated for application-aware path selection and resilience. Where business continuity is critical, a high-availability pair can reduce dependence on one appliance, but the surrounding switches, power feeds and carrier paths also need redundancy to avoid moving the single point of failure elsewhere.
A Tanzania quotation should identify the exact FG-901G appliance, subscription bundle, support duration, AC or DC requirement, compatible optics, rack and power dependencies, implementation work and any FortiManager or FortiAnalyzer requirement. Do not assume that all security services are perpetual with the appliance. Teams replacing an older firewall should also prepare interface maps, VLANs, routing tables, NAT rules, VPN parameters, authentication dependencies and a rollback plan. FourTeck can use this information to make the commercial discussion more precise. The supplied FourTeck Tanzania contact page is the appropriate starting point for a product and licensing enquiry.
FortiGate 901G Dar es Salaam
Dar es Salaam buyers considering FG-901G are commonly dealing with enterprise headquarters, service-provider connectivity, larger commercial facilities, data rooms or organizations with many remote locations. The firewall decision should account for how traffic enters and leaves the site, not just the nominal ISP speed. A company may have several internet links, private circuits, cloud tunnels and branch VPNs that all converge on the same security edge. The 901G’s mix of 25GE, 10GE, Gigabit fiber and copper interfaces gives architects flexibility, but port type alone does not determine a good design. Transceiver standards, upstream switching, routing protocols and physical path diversity must be checked.
For a head office in Dar es Salaam, it is useful to separate internet-edge, server, management, user, voice, guest and partner zones. Security policies can then follow the actual trust boundaries. TLS inspection, IPS, application control and web security should be introduced with testing because deeper inspection can affect performance and application behavior. If the organization hosts public services, DMZ design and inbound protection deserve their own policy set rather than being mixed with outbound user browsing. If remote branches connect to the site, VPN and SD-WAN policy should be planned with route control, failover behavior and monitoring.
Before requesting a Dar es Salaam quote, provide the current firewall model, peak bandwidth, ISP count, number of branches, VPN requirements, required security subscriptions and preferred support term. If the 901G will replace an existing FortiGate, migration can be easier than a cross-platform change, but configuration review is still important: old rules, unused objects and historical exceptions should not automatically be carried forward. If the project includes switching and wireless, FortiSwitch and FortiAP integration can be considered as part of the broader Security Fabric rather than as an automatic requirement. The result should be a firewall design matched to the business network, not a generic appliance installation.
FortiGate 901G Mwanza
Mwanza organizations evaluating FortiGate 901G may include larger corporate offices, education environments, healthcare networks, logistics operations, financial services, manufacturing or regional hubs that connect several sites. The key sizing question is whether the network genuinely requires an enterprise mid-range platform with high session capacity and fast interfaces. If the requirement is substantially smaller, another FortiGate may be more economical; if the environment aggregates many services and branches, the 901G can provide valuable headroom. A technical discovery process should therefore precede procurement.
Connectivity resilience can be important for a regional hub. When multiple WAN links are available, Fortinet Secure SD-WAN can apply health checks and steering rules so business-critical applications can use appropriate paths. This should be tested against the actual providers and applications. Site-to-site IPsec VPN can protect traffic to headquarters or other branches, while segmentation can separate administrative systems, operational devices, staff endpoints and guest access. For environments with large numbers of users or devices, session scale and logging volume should be considered alongside bandwidth.
A Mwanza deployment plan should document rack space, power, cooling, UPS capacity, grounding, fiber and copper presentation, optics, cable labeling and maintenance access. The dual power supplies are useful only when connected to a resilient power design. If high availability is required, each firewall should have appropriate upstream and downstream connectivity and the failure behavior should be tested during commissioning. Buyers should also determine where logs will be retained and who will monitor them. A FortiAnalyzer design may be appropriate where centralized analytics or longer retention is required. For quotation, share the expected traffic profile, required FortiGuard services, support duration, implementation scope and any central-management requirements so the proposal reflects the complete operational need.
FortiGate 901G Arusha
In Arusha, the FG-901G can suit larger hospitality groups, institutions, enterprises, multi-site operations and organizations that need a robust security edge with significant capacity. Hospitality and campus-style networks often combine staff traffic, guest access, voice, CCTV, cloud applications, payment or booking systems and remote administration. These workloads should not share unrestricted trust. A FortiGate design can use VLANs, zones and policy controls to separate them, while application visibility and licensed security services can provide additional inspection at the perimeter.
Guest-heavy environments can create large session counts and unpredictable bandwidth patterns. Rather than sizing only by the number of employees, planners should account for all connected devices and the traffic they generate. If the network uses high-speed aggregation switches, the 25GE and 10GE interfaces on the 901G can be useful for avoiding unnecessary interface constraints. The exact topology should still be based on real switching capacity, fiber standards and redundancy. For organizations operating multiple properties or branches, IPsec VPN and Secure SD-WAN can support protected connectivity and policy-based path selection between locations.
Arusha procurement teams should include the security subscription in the commercial comparison. Web filtering, intrusion prevention, malware protection and other FortiGuard capabilities depend on appropriate services, so a hardware-only price does not describe the full security outcome. Request a clearly itemized quote with the exact model, subscription bundle and term, FortiCare support, optics, implementation, migration and training or handover expectations. During deployment, establish named administrators, multi-factor authentication where appropriate, configuration backup, change control and a firmware-maintenance process. This operational discipline is as important as appliance performance. FourTeck can use a detailed requirement to help determine whether FG-901G is appropriately sized or whether another FortiGate platform would better fit the Arusha environment.
FortiGate 901G Dodoma
Dodoma organizations planning enterprise network security may need to protect administrative campuses, institutional networks, corporate offices, service environments and distributed users. The FortiGate 901G is relevant where traffic volumes, segmentation needs and encrypted connectivity justify a high-capacity platform. Selection should be based on documented technical requirements and procurement policy. Start by mapping internet connections, internal network zones, remote sites, cloud dependencies, externally published services and security controls that must remain active during peak load.
For environments with formal governance, the firewall project should include more than installation. Define administrator roles, approval procedures for rule changes, logging and retention, backup frequency, incident escalation and firmware maintenance. FortiOS provides a broad security and networking platform, but governance determines how consistently those capabilities are used. If centralized administration is required across several FortiGate appliances, FortiManager can be evaluated. If reporting and log analysis are priorities, FortiAnalyzer may be included. These components should be sized separately according to device count, log rate and retention objectives.
High availability can support continuity, but procurement should validate the complete design. Two firewalls connected to the same single switch, power source or carrier still leave common failure points. A resilient Dodoma architecture can consider dual power, diverse switching, multiple WAN paths and documented failover testing. The FG-901G’s dedicated HA interface supports clustering design, while its high-speed interfaces provide flexibility for core and edge connectivity. For an accurate quote, state whether the project is a new installation or migration, the desired subscription duration, required FortiGuard services, support level, optics, rack environment, VPN count and implementation expectations. This produces a more useful proposal than asking for the appliance price alone.
FortiGate 901G UAE
UAE enterprises considering FortiGate 901G often operate high-bandwidth internet edges, data centers, headquarters, cloud-connected campuses and multi-branch networks. The platform’s 25GE and 10GE connectivity is useful when the firewall must integrate with high-speed switching or carrier services, while the onboard SSD storage differentiates the 901G from the non-storage 900G model. The right choice still depends on inspected traffic, not simply raw firewall throughput. Teams should model IPS, application control, TLS inspection, VPN and logging requirements together.
Multi-branch UAE networks can evaluate Secure SD-WAN for application-aware path selection and integrated security, especially where offices use several carriers or connect to cloud services. Data-center deployments should consider north-south traffic, partner connectivity, public-service DMZs and internal segmentation. High availability, routing convergence and upstream/downstream redundancy should be validated in a staging or controlled change window. The appliance’s dual power supplies should be connected to independent resilient power paths where the facility design supports it.
For regional procurement, FourTeck maintains a dedicated Fortinet UAE resource covering FortiGate, license renewal, SD-WAN and related security requirements, and FourTeck UAE provides broader IT solution context. Buyers should request the exact FG-901G SKU, subscription bundle, support term, optics and implementation scope. Where DC power is required, confirm the separate FG-901G-DC variant rather than assuming the standard AC model can be changed in the field. For multinational organizations, align policy standards and support ownership across countries so the firewall becomes part of a consistent security architecture rather than an isolated appliance.
FortiGate 901G Uganda
Uganda enterprises looking at FG-901G are typically beyond small-branch firewall requirements. Suitable scenarios include a central headquarters, data center, large campus, financial or institutional network, ISP-connected enterprise edge or a hub that aggregates many branches. The decision should be driven by bandwidth with security services enabled, session demand, VPN scale, interface requirements and expected growth. Organizations should compare these requirements with Fortinet’s published performance definitions and avoid selecting a model only because its maximum firewall number appears attractive.
For a multi-site Uganda network, the 901G can terminate IPsec tunnels and participate in Secure SD-WAN designs. Branch traffic can be steered according to link health and application policy, while central security controls can inspect traffic where the architecture calls for it. Large deployments should consider how routing, DNS, identity, authentication and logging behave during WAN or firewall failover. Testing should include not only whether traffic passes but whether critical applications recover within acceptable time.
FourTeck’s Uganda regional site provides local product context, including smaller FortiGate options for branch deployments. This can be useful when a 901G is used at the hub while compact FortiGates secure remote offices. Procurement teams should itemize FortiGuard subscriptions, FortiCare, central management, analytics, optics and professional services. If the project includes a high-availability pair, ensure both units and required accessories are included. A clean bill of materials, configuration plan and renewal schedule make the deployment easier to operate after handover and reduce the risk of security services expiring unnoticed.
FortiGate 901G Kampala
Kampala headquarters and enterprise campuses may use the FG-901G as a high-capacity perimeter or aggregation firewall where multiple business systems converge. A typical environment can include primary and backup internet links, private WAN connectivity, cloud applications, branch VPNs, remote access, server networks, staff networks and public-facing services. Each flow has different risk and availability requirements. During design, document which traffic must be inspected, which zones may communicate, which applications are business critical and how failover should work.
The high-speed interface mix gives architects options for connecting core switches, server fabrics and carrier equipment. However, compatible optics and cabling should be specified in the bill of materials. Do not assume every SFP or SFP28 module is appropriate. Network teams should also reserve management connectivity and plan out-of-band access where operational policy requires it. If high availability is deployed, synchronize the design with switch and routing configuration so the cluster can fail over predictably.
Kampala buyers may pair a central 901G with smaller branch FortiGates. FourTeck’s Uganda catalog includes models such as FortiGate 30G for compact branch sites and FortiGate 60F for established small and mid-sized branches. These links are useful for understanding hub-and-branch planning rather than implying that every location needs the same appliance. For the Kampala hub, request a 901G quote based on measured traffic, required subscription term, support level, VPN scale, logging architecture and implementation scope. Include migration testing and rollback procedures if replacing a production firewall.
FortiGate 901G Arua
For Arua, the first question is whether the site itself needs FG-901G capacity or whether it will connect to a larger central 901G deployed elsewhere. A regional branch may be better served by a smaller FortiGate, while a major hub, service facility or aggregation point could justify the larger platform. This distinction matters because good firewall sizing balances capacity, security functions, redundancy, cost and operational simplicity. Over-sizing every branch can create unnecessary capital and subscription expense, while under-sizing a central hub can constrain inspection and VPN performance.
If Arua operates as a regional hub, document all WAN links, connected sites and critical applications. Secure SD-WAN can help manage multiple paths, and IPsec can protect site-to-site communication. Network segmentation can separate administrative systems, user endpoints, guest access, operational devices and other trust zones. Where bandwidth is constrained or variable, application policy should prioritize business traffic based on measured needs rather than arbitrary assumptions. Monitoring should distinguish carrier problems from security-appliance problems so troubleshooting is efficient.
A procurement request should specify whether AC or DC power is required, whether a high-availability pair is planned, which optics are needed and how long the FortiGuard and FortiCare term should run. Operational planning should include configuration backups, named administrators, secure management access, firmware policy and log retention. If the Arua location is a branch connected to a Kampala or other central 901G, FourTeck can help compare compact FortiGate models and align VPN, SD-WAN and security policy with the hub design. The objective is a consistent architecture in which each appliance is sized for its role rather than selected by a single standardized model across every site.
FortiGate 901G Mbarara
Mbarara businesses and institutions evaluating FG-901G should consider the appliance as part of an end-to-end network architecture. A large firewall can process significant traffic, but user experience still depends on ISP quality, LAN switching, wireless design, DNS, application hosting and endpoint health. During discovery, measure peak internet utilization, internal traffic crossing security zones, VPN usage and growth. Identify which traffic will use IPS, application control, web security or TLS inspection. This provides a realistic basis for model selection.
Where the site connects to several branches, warehouses or service locations, Fortinet Secure SD-WAN and IPsec VPN can create a common security and connectivity framework. Policies can use health information and application awareness to choose links, but failover should be tested against real business services. Voice, ERP, cloud applications and transactional systems may react differently when paths change. The network team should define expected behavior and monitoring before production cutover.
The FG-901G’s local SSD storage can support designs where onboard storage is desirable, while centralized FortiAnalyzer can be evaluated for broader analytics and retention. These are different design choices and should not be conflated. For Mbarara procurement, include subscription services, support term, optics, rack requirements, power, HA accessories if needed, implementation and documentation. If the 901G is a central appliance serving Mbarara alongside other Ugandan sites, align branch firewall models with expected local traffic. A well-designed hierarchy can use high-capacity security at the hub and appropriately sized appliances at branches, with consistent policies and centralized visibility. This generally produces a more supportable network than deploying oversized equipment without a clear role.
FortiGate 901G Gulu
Gulu organizations with regional operations can evaluate the FG-901G where the site functions as a major hub or where enterprise traffic volumes demand substantial inspection capacity. The planning process should identify business services that cannot tolerate prolonged outages, then map their network dependencies. This may include internet access, branch connectivity, cloud services, voice, server access and remote administration. High availability can protect against appliance failure, while dual WAN or diverse carrier services can address connectivity failure; neither replaces the other.
Security policy should be organized around zones and business purpose. A flat rule base that allows broad internal access can reduce the benefit of an advanced firewall. Segment server systems, user groups, guest networks, management traffic and operational devices where practical. Apply security inspection according to risk and performance requirements. If TLS inspection is planned, test application compatibility and certificate deployment carefully. Fortinet publishes specific SSL inspection performance figures, and these are more relevant to such a design than raw firewall throughput.
For Gulu procurement, prepare a technical schedule showing interfaces, optics, routing, VLANs, VPN tunnels, subscriptions, support term and required professional services. Determine whether logs remain on the appliance, are forwarded to FortiAnalyzer or integrate with another monitoring platform. Define backup and change-management responsibilities. Where Gulu is a branch rather than a hub, compare smaller FortiGate models instead of assuming the 901G is necessary. FourTeck can use the site’s user count, bandwidth, application mix, branch role and inspection requirements to guide the model discussion. This role-based sizing approach protects budget while keeping enough capacity for expected growth and security functions.
FortiGate 901G Kenya
Kenya enterprises can deploy the FG-901G at data centers, headquarters, large campuses or central hubs where high-speed interfaces and significant firewall capacity are required. Organizations should compare the 901G with adjacent FortiGate platforms using inspected throughput, interface needs, storage requirement, VPN scale and future growth. The 901G’s two 480 GB SSDs are a key differentiator from the 900G, so buyers who do not need onboard storage should confirm whether another family member better matches the requirement.
For Nairobi or other large business networks, the firewall may sit between several connectivity domains: internet, private WAN, cloud, branches, server networks and partner links. A good design defines security zones, routing ownership and failover behavior before rules are migrated. FortiGate Secure SD-WAN can help manage multi-link connectivity, while FortiManager and FortiAnalyzer can support centralized operations where the environment includes multiple Fortinet devices. The exact components should be selected based on management and reporting needs rather than automatically bundled.
FourTeck’s FortiGate Firewall Kenya guide covers broader firewall buying considerations, and the FortiGate Kenya product category helps teams compare other models for branches and smaller sites. A Kenya 901G quote should clearly list the appliance, FortiGuard bundle, FortiCare term, optics, power model, high-availability quantity, management or analytics components and implementation. This prevents a misleading comparison between proposals that include different service levels or subscription scopes.
FortiGate 901G Kuwait
Kuwait organizations evaluating FortiGate 901G may need a high-performance perimeter for headquarters, data centers, government or enterprise environments, multi-branch networks and cloud-connected infrastructure. The appliance’s high-speed interface mix supports modern switching and carrier connectivity, but the design should be driven by security requirements. Raw throughput is only one metric. Teams using deep inspection, intrusion prevention, application control and encrypted VPN should size against the relevant published performance figures and maintain headroom for traffic growth.
Environmental and data-center planning also matters. Confirm rack position, power feeds, UPS design, cooling, cable routing and transceiver requirements. The standard FG-901G uses dual AC power, while Fortinet publishes a separate DC variant. Procurement should therefore specify the required power model explicitly. High-availability pairs should be connected so that a single upstream switch, downstream switch or power event does not defeat the redundancy objective. Planned failover tests should verify routing and application recovery.
FourTeck maintains a Kuwait regional technology site for local enquiries and broader IT requirements. For an FG-901G quotation, include the required FortiGuard services, FortiCare level and duration, optics, management tools, logging needs and implementation scope. Organizations with multiple sites should also identify branch models and VPN topology so the central firewall is sized for aggregate encrypted traffic. When comparing offers, check that each proposal includes equivalent subscriptions and support; a hardware price alone does not show the operational security package that will be available after deployment.
FortiGate 901G Ghana
Ghana enterprises can consider FG-901G for large network edges, data centers, campuses and central sites that need high-capacity firewalling and encrypted connectivity. A requirements workshop should capture peak WAN traffic, branch count, remote access, application mix, TLS inspection, public services, internal segmentation and log retention. This information helps determine whether the 901G is correctly sized and which subscription services are necessary. A high-performance appliance without a clear policy and lifecycle plan will not by itself create an effective security program.
Organizations with Accra headquarters and regional branches can evaluate Secure SD-WAN and IPsec for protected multi-site connectivity. The hub should be sized for aggregate branch traffic and failure scenarios, including what happens when one WAN path fails and traffic shifts to another. Network segmentation can reduce unnecessary trust between users, servers, guests and operational devices. Where the business handles sensitive or regulated information, logging, administrator accountability and change control should be designed from the start.
For procurement, identify the exact FG-901G model, AC or DC requirement, quantity, FortiGuard bundle, FortiCare term, optics, high-availability design and central management or analytics requirements. If the firewall replaces an existing platform, include configuration discovery and migration effort. FourTeck’s regional network includes FourTeck Ghana for Ghana-focused enquiries and FourTeck IT Solutions Africa for broader infrastructure context. Buyers should use the quotation process to confirm current availability, commercial terms and service scope rather than assuming stock, delivery or warranty details from generic product information.
FortiGate 901G Nigeria
Nigeria enterprises with large headquarters, data centers, financial networks, industrial operations or multi-branch environments may require a firewall in the FG-901G performance class. The platform is designed for substantial traffic and session volumes, but the correct selection depends on the actual security profile. Teams should measure internet and inter-zone traffic, determine which flows require IPS or TLS inspection, quantify VPN demand and plan for growth. Where a firewall is used as a central SD-WAN hub, failure scenarios can increase traffic concentration and should be included in sizing.
High-speed 25GE and 10GE connectivity can integrate with enterprise switching, but the network architecture must account for optics, cabling, routing and redundancy. For data centers, consider whether the firewall protects north-south internet traffic, east-west segmentation, partner connections or a combination. These roles can create different throughput and policy requirements. For headquarters, identity-aware policy, remote access, web security and application control may be more prominent. One appliance model can support different designs, but the configuration should reflect the business role.
Nigeria buyers can use FourTeck Nigeria for regional enquiries. A complete request should state the FG-901G quantity, required subscription bundle and duration, FortiCare level, power model, optics, HA requirement, management and logging architecture, migration needs and destination. Avoid treating FortiGuard services as an unspecified add-on: the chosen bundle affects available security capabilities and recurring cost. For organizations standardizing across several African countries, document a common baseline for policy, logging, administrator access and renewal ownership while allowing each site’s bandwidth and topology to determine the appropriate FortiGate model.
FortiGate 901G Seychelles
Seychelles organizations considering FG-901G should pay particular attention to the relationship between local site size, available connectivity and the role of the firewall. A large hospitality group, government environment, service provider, enterprise campus or centralized infrastructure site may justify an enterprise platform, while smaller properties or branches may be better served by lower FortiGate models. The goal is to match inspected traffic, VPN requirements, session scale and interface needs to the appliance rather than selecting by brand family alone.
Where multiple internet paths are available, Secure SD-WAN can help manage link health and application steering. For organizations with several islands, properties or remote sites, IPsec VPN can protect inter-site communication over available carriers. Network design should account for the behavior of critical cloud and business applications when a link changes. Because remote connectivity can be operationally important, monitoring, alerting and documented failover procedures should be part of the project. Local storage on the 901G may be useful, while centralized logging can still be considered for broader visibility.
A Seychelles quote should identify shipping destination, exact model, power requirement, subscription bundle, support term, optics and professional-services scope. Current availability, lead time and commercial terms should be confirmed at quotation rather than assumed. If high availability is required, specify two appliances and design the surrounding network and power paths accordingly. For a distributed hospitality or enterprise environment, also document guest networks, staff systems, payment or reservation services, CCTV, voice and management traffic so segmentation can be planned. FourTeck can use this information to assess whether FG-901G is appropriate and to structure a solution around the actual network instead of a generic firewall bill of materials.
Related Fortinet and infrastructure resources
A 901G project often connects to a broader network rather than operating alone. For Kenya deployments, the Fortinet Kenya brand resource explains related Fortinet product families, while FourTeck’s Kenya firewall category gives broader multi-vendor firewall context. Uganda branch planners can review FortiGate 30G Uganda for compact sites and FortiGate 60F Uganda for larger branch requirements. These related pages are useful when the 901G is the central hub and remote locations need proportionately sized appliances.
For specialist Fortinet content, FourTeck Fortinet UAE covers FortiGate, Secure SD-WAN, VPN, licensing and related security services. FourTeck IT Solutions Africa provides context around networking, servers, Wi-Fi and infrastructure that may sit around the firewall. These links help procurement and technical teams consider the complete environment rather than isolating the security appliance from switching, wireless, power, server and connectivity dependencies.
FG-901G buying and sizing checklist
Record peak WAN traffic, expected growth, TLS inspection, IPS, application control and web-security requirements.
List WAN circuits, 25GE/10GE/Gigabit interfaces, optics, VLANs, routing, branch tunnels and remote-access needs.
Decide whether HA is required and review power, switching and carrier diversity so redundancy has no obvious common failure point.
Choose FortiGuard and FortiCare services and term according to required security functions and support expectations.
Plan administrators, MFA, backups, firmware maintenance, logging, monitoring, documentation and change control.
Inventory policies, objects, NAT, routes, VPNs, authentication, certificates and dependencies before the cutover window.
Frequently asked questions
What is the difference between FortiGate 900G and 901G?
Fortinet’s ordering information shows the same main interface and acceleration platform, while FG-901G adds two 480 GB onboard SSDs. Buyers should verify the exact current datasheet and required power variant before ordering.
Is FG-901G suitable for a data center?
It is positioned for enterprise-scale use and offers high-speed interfaces and substantial published firewall, VPN and session capacity. Suitability for a specific data center depends on inspected traffic, topology, redundancy, segmentation and growth requirements.
Does FortiGate 901G support high availability?
The platform includes a dedicated 2.5GE HA interface and can be used in FortiGate high-availability designs. The complete design should also remove common failure points in power, switching and WAN connectivity.
Does FG-901G include FortiGuard subscriptions permanently?
Security-service and support entitlements depend on the bundle and term purchased. Request an itemized quotation that identifies FortiGuard services and FortiCare duration rather than assuming all services are perpetual.
What information is needed for an FG-901G quote?
Provide quantity, destination, users, bandwidth, security inspection requirements, branch and VPN count, subscription term, HA requirement, AC or DC preference, optics, management/logging requirements and implementation scope.
Decision recap
Choose the FortiGate 901G when the design calls for a high-capacity Fortinet enterprise firewall with onboard SSD storage, 25GE and 10GE connectivity, large session scale and support for FortiOS security and networking capabilities. Do not select it from raw throughput alone. Validate inspected traffic, VPN, SD-WAN, segmentation, subscriptions, logging, power, optics and redundancy. If those requirements are materially smaller, compare lower FortiGate models; if they are larger or unusually inspection-heavy, compare higher platforms. Correct sizing protects both security performance and project budget.
Consult FourTeck about FortiGate 901G
Send the technical requirement rather than only the model name. Include current firewall, users, internet capacity, number of branches, VPN users, security services, preferred support term, HA requirement and deployment location. FourTeck can then structure the FG-901G discussion around the right appliance, subscription and implementation scope. Availability, pricing, delivery terms and warranty should be confirmed in the formal quotation.




Reviews
There are no reviews yet.