
FORTINET NEXT-GENERATION FIREWALL
FortiGate 120G Series Tanzania
The FortiGate 120G Series combines Fortinet FortiOS, ASIC-accelerated security, Secure SD-WAN, VPN and advanced inspection for organizations that need a capable security edge without separating networking and cybersecurity into unrelated appliances. Fortinet publishes 39 Gbps firewall throughput, 35 Gbps IPsec VPN throughput, 3 Gbps SSL inspection and 2.8 Gbps threat protection for this platform. Those figures are useful reference points, but correct sizing should also consider enabled security services, encrypted traffic, user and device counts, interfaces, branch connectivity, application mix and future bandwidth growth.

Published firewall throughput for the FortiGate 120G Series.
Published IPsec VPN throughput for site connectivity and encrypted networking.
Published SSL inspection throughput for visibility into encrypted traffic.
Published threat-protection throughput for security-service sizing reference.
What the FortiGate 120G Series solves
A modern business edge has to do much more than permit or block internet traffic. Users depend on SaaS applications, branches exchange sensitive information, remote workers need controlled access, guest and operational networks require separation, and encrypted traffic must be inspected without creating an avoidable bottleneck. FortiGate 120G brings firewalling, routing, Secure SD-WAN, VPN and security inspection into FortiOS, helping IT teams operate networking and security through a common platform. The series is particularly relevant when an organization is moving beyond entry-level firewall capacity but still wants a compact appliance suited to branch, campus and mid-sized enterprise requirements.
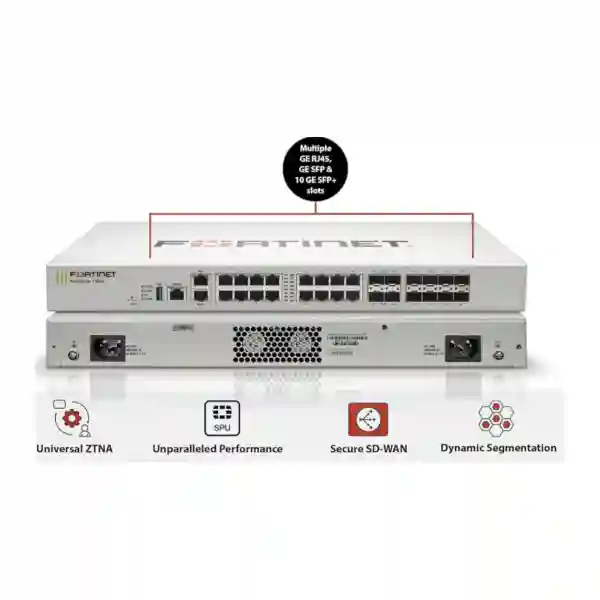
Fortinet lists 4 x 10 GE SFP+, 18 x GE RJ45 and 8 x GE SFP interfaces for the FortiGate 120G platform. This mix can support designs that combine copper access, fiber connectivity and higher-speed uplinks. Interface count alone should not determine the purchase: buyers should map WAN circuits, LAN trunks, DMZs, HA requirements, switching architecture and transceiver needs before ordering. For broader infrastructure planning, review FourTeck Tanzania’s integrated IT and security portfolio, which explains how firewall, switching, Wi-Fi, servers and other business systems should be considered together.
Key FortiGate 120G capabilities
NGFW security
FortiOS provides next-generation firewall functions and can use FortiGuard security services for controls such as intrusion prevention, web filtering, application control and malware protection according to the selected subscriptions.
Secure SD-WAN
Organizations with multiple WAN circuits can use Secure SD-WAN policies to steer traffic according to application and link conditions while maintaining security at the branch edge.
VPN connectivity
IPsec VPN supports protected site-to-site connectivity. Remote-access architecture should be selected according to FortiOS version, FortiClient requirements, identity controls and the organization’s access model.
Segmentation
Firewall policies and VLAN-aware design can separate users, servers, guests, voice, CCTV, Wi-Fi and operational devices, reducing unnecessary lateral communication.
FortiGate 120G or 121G?
The 120G family includes closely related appliance options. A key procurement distinction is local storage: the FortiGate 120G is commonly selected as the diskless option, while the FortiGate 121G adds internal storage. Buyers should confirm the exact model, bill of materials, FortiCare level, FortiGuard bundle, transceivers and any central-management or logging requirements on the quotation rather than treating “120G Series” as a complete order specification. Where local logging requirements are important, also assess whether FortiAnalyzer or another approved logging architecture is part of the design.
Deployment and sizing guidance
Firewall sizing should begin with measured and expected traffic rather than employee count alone. Record current internet bandwidth, planned upgrades, peak concurrent users, cloud applications, VPN tunnels, remote users, east-west segmentation requirements and whether deep inspection will be enabled. A site with a 1 Gbps internet service can still place substantial demands on a firewall when it carries multiple VPNs, internal routing, security inspection and high session counts. Conversely, a larger user population with lightweight traffic can have a different profile. FourTeck Tanzania’s network-security guidance emphasizes sizing around enabled security services rather than relying only on headline firewall throughput.
The surrounding network matters as well. Managed switches, fiber uplinks and VLAN design determine how effectively a FortiGate can segment traffic. Business Wi-Fi should map SSIDs to appropriate security zones instead of placing staff, guests and devices into one flat network. Server and application segments may need more restrictive rules than ordinary user networks. For multi-site designs, consistent addressing, naming, VPN templates and policy standards make later support easier. Relevant Tanzania resources include the FourTeck Tanzania technology shop, the site’s networking guidance, Wi-Fi planning, structured cabling, server infrastructure and integrated lifecycle-service sections.

FortiGate 120G Series Tanzania
For organizations evaluating FortiGate 120G Series in Tanzania, the strongest procurement approach is to treat the firewall as part of the complete network edge rather than a standalone box. A buyer in Tanzania may be replacing an older firewall, consolidating several branch gateways, introducing dual internet links, creating secure connectivity to cloud workloads, or segmenting a growing office network. Each scenario changes the design. Before requesting a quote, document the current WAN services, public IP requirements, VLANs, servers, hosted applications, VPNs, remote-access population, existing switches and any expected internet upgrade. This gives the supplier enough context to distinguish hardware capacity from subscription and implementation requirements.
The FortiGate 120G is attractive where organizations need substantial firewall and VPN performance together with FortiOS security functions. Tanzania deployments should also account for physical infrastructure. Rack space, ventilation, clean power and UPS protection influence long-term reliability. If the site has fiber from the service provider or between network rooms, confirm the exact optic and connector requirements instead of assuming that all SFP or SFP+ modules are interchangeable. If the firewall will connect to multiple switches, decide whether those links are routed, aggregated or trunked and document the VLAN ownership clearly. These details are especially important when a firewall replacement must happen with limited downtime.
Subscription selection is another major part of a Tanzania quotation. FortiGate hardware can be paired with FortiCare and FortiGuard service bundles; the correct term and service level should match the security functions the organization expects to use. A customer asking for web filtering, IPS, application control, malware protection and ongoing security intelligence should make those requirements explicit. Organizations that already operate Fortinet equipment should provide existing serial and support information so renewal and migration planning can be separated from new hardware purchasing. For a wider Tanzania infrastructure discussion, use FourTeck Tanzania contact and quotation support to share the technical scope.
FortiGate 120G Series Dar es Salaam
Dar es Salaam organizations commonly operate internet-heavy business environments where cloud applications, VoIP, video meetings, ERP access, branch connectivity and guest Wi-Fi all converge at the same security edge. When evaluating a FortiGate 120G Series for Dar es Salaam, map the real traffic flows before choosing policies. A head office may have several internet circuits, a server VLAN, user networks, voice, CCTV, wireless guests and management devices. Putting every system behind a single broad LAN policy may be easy initially, but it reduces visibility and makes later security changes difficult. The 120G’s interface options and FortiOS segmentation capabilities provide a basis for a more structured architecture when the surrounding switching is designed correctly.
For offices that depend on two internet providers, Secure SD-WAN can be considered for path selection and resilience. The business requirement should define whether the second circuit is only for failover, whether selected applications should prefer one link, and what health checks determine that a circuit is genuinely usable. A link can remain electrically up while upstream connectivity is degraded, so the policy should test meaningful destinations and applications. Public services, inbound NAT and provider-assigned addressing can complicate failover, which is why dual-WAN design should be reviewed before migration rather than added after the firewall is live.
Dar es Salaam procurement teams should request a bill of materials that separates appliance, support/security subscriptions, optics or cables, installation, migration and optional management/logging components. This makes competing quotations easier to compare. It also reduces the risk of buying hardware without the services needed for the intended security controls. Where the project includes switches, Wi-Fi, servers, CCTV or IP telephony, document those dependencies so firewall rules and VLANs can be prepared before cutover. The goal is a controlled migration with tested internet, DNS, business applications, VPN and failover rather than a hurried replacement that reproduces old configuration problems.
FortiGate 120G Series Mwanza
A FortiGate 120G Series deployment in Mwanza can suit organizations that need a strong security gateway for a regional office, campus, hospitality property, healthcare environment, warehouse, financial operation or multi-site business. The design should start with the applications that cannot tolerate interruption. If users depend on cloud ERP, hosted email, remote databases, payment systems or communications platforms, internet resilience and DNS behavior can matter as much as raw firewall throughput. Identify which services must continue during a primary-link outage and which can wait. This creates a practical basis for SD-WAN and failover policies.
Mwanza sites with multiple buildings or large premises should also examine how traffic reaches the firewall. Fiber uplinks between network rooms, managed switching and clear VLAN boundaries can prevent the security appliance from becoming part of an undocumented flat network. CCTV, guest Wi-Fi and operational devices should not automatically receive the same access as employee computers. Where servers or recorders are hosted locally, define which user groups and remote sites need to reach them and permit only those flows. This policy-led approach makes the firewall configuration easier to audit and troubleshoot.
For procurement, send the expected internet speeds, number of sites, approximate endpoint count, VPN requirements, desired security services and current firewall model with the request. If the project will reuse existing fiber modules, rack accessories or WAN equipment, verify compatibility before the installation date. Power continuity is also relevant: the firewall, ISP equipment and core switches should be considered together when sizing UPS runtime. A firewall that remains powered while the provider handoff or core switch shuts down does not preserve connectivity. Building the bill of materials around the complete path helps Mwanza buyers avoid these overlooked dependencies.
FortiGate 120G Series Arusha
Arusha businesses often need secure connectivity for offices, hospitality operations, travel businesses, institutions and organizations that collaborate with users or systems outside the local site. FortiGate 120G Series can be evaluated as the security edge where those requirements include multiple network zones, VPN connectivity, application-aware policy and Secure SD-WAN. The first design question should be what must be protected and separated. Staff devices, guest wireless users, property or operational systems, CCTV and servers can have very different trust levels, even when they share the same physical switching infrastructure.
For hospitality and visitor-facing environments, guest internet should be designed so guests cannot reach administrative networks or infrastructure-management interfaces. Where business systems are hosted locally, remote access should be limited to authorized users and appropriate authentication controls. For branch or partner connectivity, site-to-site IPsec VPN can provide encrypted tunnels, but address planning must avoid overlapping subnets. Overlap is a common migration problem when several independently built sites all use the same private network ranges. Discovering that issue before deployment allows a cleaner addressing or translation strategy.
Arusha customers should also think beyond day-one bandwidth. Internet services, cloud use and encrypted traffic typically grow during the life of a firewall. The 120G’s published performance provides headroom for many mid-market scenarios, but the final choice should be based on the security profile that will actually run. Ask whether SSL inspection, IPS, application control and web filtering will be applied broadly or selectively, and whether central logging is required. A quotation should identify subscription term, support level and any optional Fortinet management components. This provides a more meaningful total-cost view than comparing appliance prices alone.
FortiGate 120G Series Dodoma
Organizations considering FortiGate 120G Series in Dodoma may include government-adjacent operations, professional offices, education, healthcare, NGOs and growing commercial sites. These environments often place a premium on controlled access, dependable site connectivity and clear documentation. A firewall project should therefore include an agreed network-zone map, naming standards, administrative-access policy and configuration-backup process. The device is only one part of the control framework; operational discipline determines whether policies remain understandable as staff, applications and service providers change.
If the Dodoma site connects to Dar es Salaam or other branches, define the VPN topology before configuration. Some organizations need a simple hub-and-spoke design, while others need selected branch-to-branch communication or internet breakout at each location. Secure SD-WAN can combine connectivity and security policy, but the design should reflect application paths and business continuity goals. Consider what happens when a WAN circuit fails, how long the organization can operate on the secondary link, and whether the backup circuit has enough capacity for all traffic or only priority applications.
Procurement documentation should also include rack and power details. Confirm available rack units, grounding and ventilation, UPS capacity, provider handoff type and required patching. If fiber interfaces are planned, identify speed, fiber type and optics on both ends. For a replacement project, export and review the existing rules rather than blindly recreating them; unused objects, broad any-to-any policies and obsolete NAT entries can accumulate over years. Migration is an opportunity to validate business owners for each rule. A structured Dodoma deployment can therefore improve both security and maintainability while introducing the new FortiGate platform.
FortiGate 120G Series UAE
For UAE projects, the FortiGate 120G Series can serve branch, campus and mid-sized enterprise security requirements where high firewall throughput, IPsec VPN, encrypted-traffic inspection and Secure SD-WAN are needed. UAE buyers frequently compare firewall platforms around internet capacity, cloud adoption, branch connectivity and subscription terms. The useful comparison is not only hardware price: examine the security services included, FortiCare level, subscription duration, required optics, implementation scope and logging architecture. FourTeck’s dedicated Fortinet UAE resource covers FortiGate purchasing, licensing, renewal, VPN, Secure SD-WAN and related Fortinet products, while FourTeck UAE provides broader IT and network-security context.
A UAE deployment may involve high-speed fiber internet, multiple service providers, cloud-hosted applications and branch VPNs. The 120G’s 10 GE SFP+ connectivity can be relevant where faster uplinks or aggregation are needed, but interface planning must match the actual handoffs and LAN architecture. Where high availability is required, quote and design the HA pair as a complete solution, including corresponding subscriptions, links, rack space and power. Confirm which state and sessions need to survive a failover and test the HA behavior as part of acceptance.
For organizations operating between UAE and East Africa, standardizing FortiOS policy objects, VPN templates, naming and security profiles can simplify cross-border support. Standardization should not mean identical appliance sizing at every branch; each site should still be matched to bandwidth and workload. Instead, use consistent architecture and documentation so teams can understand how a Tanzania, Kenya, Uganda or UAE site is built. This reduces configuration drift and makes future central management more practical.
FortiGate 120G Series Uganda
Uganda organizations evaluating FortiGate 120G Series should define whether the appliance will protect a single major site or form part of a multi-branch architecture. Businesses with offices, warehouses, clinics, education sites or distributed operations may need secure internet, branch VPN, controlled guest access and centralized visibility. FortiGate can combine these roles, but the policy design should begin with an inventory of networks and applications. Identify internal systems that must be reachable between sites and services that should remain local. This prevents the VPN from becoming an unrestricted extension of every LAN.
When primary and backup internet services are available, Secure SD-WAN can help prioritize business traffic and provide failover. The secondary circuit should be tested under realistic load because a low-capacity backup may need to carry only essential services. Voice, transaction traffic and critical cloud applications can be prioritized while large downloads or guest traffic are constrained during an outage. Health checks should measure usable connectivity rather than only the local gateway. For regional IT context, FourTeck Uganda describes business communication, networking and security solution requirements.
A Uganda quotation should state whether the request is for FG-120G or the storage-equipped family variant, the desired support/security bundle, subscription duration and any installation or migration work. Include current firewall details, internet speeds, number of VPN sites and any planned growth. If the organization expects centralized management or long-term log retention, include that requirement at the start rather than treating it as an afterthought. This makes the proposed architecture easier to evaluate and avoids an appliance-only quote that does not represent the operational solution.
FortiGate 120G Series Kampala
Kampala offices can place diverse traffic demands on a security gateway: cloud collaboration, business applications, voice, video, remote users, guest Wi-Fi and branch links may all share the same internet circuits. A FortiGate 120G Series project should categorize these traffic types and decide which need inspection, priority or isolation. Staff and server networks can be separated from guest and IoT-style devices, while management interfaces should be reachable only from controlled administrative networks. This reduces exposure and gives troubleshooting teams clearer boundaries.
For a head office in Kampala, consider whether the firewall will terminate many site-to-site tunnels from smaller branches. The aggregate VPN traffic, session load and inspection requirements should be included in sizing. If branches use different providers, design tunnels around stable endpoint addressing or an appropriate dynamic approach. DNS, time synchronization and identity dependencies should also be documented because security services and authentication can behave unexpectedly when these supporting systems fail. During migration, test each tunnel and application path against an agreed checklist.
Kampala buyers comparing suppliers should request line-item clarity. Hardware, FortiCare, FortiGuard bundle, optics, installation, configuration, migration and training or handover should be visible rather than combined into an ambiguous description. If the organization already owns FortiSwitch, FortiAP, FortiManager or FortiAnalyzer, disclose versions and topology so compatibility can be checked. A well-prepared request produces a more accurate quote and gives technical reviewers enough information to confirm that the FortiGate 120G Series is being proposed for the right role.
FortiGate 120G Series Arua
For an Arua deployment, the business-continuity plan may be as important as maximum firewall capacity. A branch can have a powerful security appliance yet still lose service if its only WAN circuit, provider equipment or power path fails. When considering FortiGate 120G Series in Arua, document primary and backup connectivity options, the applications that must remain available and the minimum bandwidth they need. If a secondary link is available, Secure SD-WAN policies can be designed so essential traffic continues while noncritical usage is limited during degraded conditions.
Remote support should be designed securely. Administrative interfaces should not be exposed broadly to the internet, and management access should use controlled source networks, strong authentication and organization-approved procedures. Configuration backups and change records are especially valuable for sites where on-site intervention may take time. If the firewall serves as a branch endpoint to Kampala or another hub, keep the addressing plan and VPN parameters documented centrally so replacement or troubleshooting does not depend on one person’s memory.
Arua procurement teams should include environmental and physical details in the project scope. Confirm whether the firewall will be installed in a secure rack, whether cooling is adequate, and whether the ISP device, firewall and switching layer share protected power. Label WAN and LAN links clearly. If the project uses fiber, record optic type and spare strategy. These practical controls are inexpensive compared with downtime caused by an undocumented cable or incompatible transceiver. The FortiGate 120G Series can provide a capable security foundation, but resilient operation comes from combining the appliance with disciplined network and site design.
FortiGate 120G Series Mbarara
Mbarara businesses planning a FortiGate 120G Series deployment should begin with a simple traffic and dependency map. List internet services, internal servers, cloud platforms, voice systems, CCTV, Wi-Fi networks and branch connections. Then identify which systems need to communicate and which should be isolated. This exercise turns firewall policy into a reflection of business requirements rather than a collection of rules added whenever something stops working. For growing sites, it also creates a repeatable framework for adding new departments or services without expanding one unrestricted LAN.
If the site operates retail, hospitality, healthcare, education or warehouse systems, consider separating operational devices from ordinary user endpoints. Guest wireless access should normally have internet access without visibility into internal resources. Servers can be placed in dedicated zones with tighter inbound and outbound policies. Management access to switches, access points and the firewall itself should be restricted. FortiOS supports the policy framework for this segmentation, while the switches and wireless platform must carry the corresponding VLAN design correctly.
For quotation accuracy in Mbarara, provide expected internet capacity over the next few years rather than only today’s circuit speed. Include the number of branch tunnels, whether SSL inspection is planned, the FortiGuard security functions required and expected support term. If the site has a narrow maintenance window, mention migration constraints and whether the existing firewall configuration is available for review. A replacement project should include rollback planning and acceptance testing for business applications, VPNs, printing, DNS and internet access. These details make deployment more predictable and help determine whether the 120G is appropriately sized.
FortiGate 120G Series Gulu
Gulu organizations can evaluate FortiGate 120G Series when they need a security platform with capacity for protected internet access, VPN and multiple network zones. The model’s published performance is substantial for many branch and mid-market designs, but procurement should still be based on the enabled security profile. Threat protection, SSL inspection and VPN each consume resources differently. A sizing discussion should therefore describe how much traffic is encrypted, which applications are business critical and whether inspection will apply to all users or selected networks.
Where a Gulu site is part of a national network, establish common standards with the central IT team. Use consistent VLAN naming, IP addressing conventions, firewall object names and VPN documentation. Standard security profiles can be adapted for local needs while keeping the overall architecture recognizable. This is particularly useful when support is provided remotely or by several technicians. Centralized logging and management may also be worth assessing for organizations with many FortiGate appliances, because troubleshooting and policy review become more efficient when each branch is not treated as an isolated configuration.
Physical resilience remains essential. Include ISP routers or ONTs, core switches and wireless controllers in the UPS plan rather than protecting only the firewall. Keep spare patch leads and document the WAN handoff. If the appliance connects to fiber, identify transceiver specifications on both sides. A clear rack diagram and port map can reduce restoration time after maintenance or equipment changes. For Gulu buyers, these operational details can deliver more practical value than simply selecting the highest headline throughput available.
FortiGate 120G Series Kenya
Kenya businesses considering FortiGate 120G Series may be securing headquarters, branches, campuses, logistics operations or hybrid-cloud environments. The platform is relevant where organizations want to combine next-generation firewall controls with Secure SD-WAN and VPN rather than operating separate edge devices. Start by documenting internet and private WAN links, expected cloud traffic, number of branch tunnels and the security services that will be enabled. This allows the hardware to be evaluated against real inspected traffic rather than only the vendor’s maximum firewall number.
Organizations with Nairobi and regional branches can use a consistent FortiOS architecture while sizing each site individually. A larger hub may terminate many VPNs and carry centralized internet traffic, while smaller branches may break out locally. The topology should be selected according to application location, bandwidth economics and security policy. Where multiple providers are used, Secure SD-WAN can make path selection application-aware, but health checks, routing and inbound-service requirements must be designed carefully. FourTeck Kenya provides regional context for firewall security and enterprise networking requirements.
A Kenya procurement request should specify exact appliance model, subscription bundle and term, support level, optics, HA requirement, central logging and implementation scope. If the firewall will integrate with existing FortiSwitch or FortiAP equipment, include model and software information. If another vendor is being replaced, list the existing VPNs, public services and authentication dependencies. This enables a migration plan that preserves required business functions while allowing obsolete policies to be removed instead of copied automatically.
FortiGate 120G Series Kuwait
FortiGate 120G Series in Kuwait can be considered for organizations requiring high-performance branch or enterprise-edge security, especially where encrypted traffic, multiple WAN services and VPN connectivity are important. The appliance should be evaluated as part of the full security architecture. Define whether the project needs NGFW inspection, Secure SD-WAN, site-to-site VPN, remote access, network segmentation and centralized logging. Each requirement influences subscription, configuration and operational planning even when the underlying hardware remains the same.
Kuwait sites with high-speed internet should pay particular attention to inspected throughput. A firewall can forward traffic at one rate while performing advanced threat inspection at another, so security-enabled performance is the more meaningful reference for protected internet access. The 120G Series publishes 2.8 Gbps threat protection and 3 Gbps SSL inspection. Actual results depend on traffic and configuration, so the final design should include reasonable capacity margin. If faster WAN services are expected during the appliance lifecycle, include that growth in the initial sizing exercise.
For procurement, request a complete bill of materials and clarify subscription duration. Hardware-only pricing is not equivalent to a security solution that includes FortiGuard services and FortiCare. Confirm transceivers and cabling for any SFP/SFP+ links and identify whether HA is required. Organizations operating across Kuwait, UAE and Africa can also benefit from standardized policy and documentation. FourTeck’s regional network, including its Fortinet-focused UAE resource, can help frame consistent requirements across multiple markets without assuming every site needs identical hardware.
FortiGate 120G Series Ghana
Ghana organizations evaluating FortiGate 120G Series can use the platform for a security edge that combines firewalling, VPN, segmentation and SD-WAN functions. The design should be driven by business services: cloud applications, branch connections, hosted systems, guest access and remote administration all create different policy requirements. Begin by identifying critical applications and data paths. Then create network zones that reflect trust levels instead of relying on one broad internal network. This makes policies easier to explain and reduces unnecessary lateral access.
For multi-site organizations, VPN design should consider both bandwidth and routing. If all branch internet traffic is backhauled through a central firewall, the hub must be sized for aggregate traffic and inspection. If branches use local internet breakout, consistent security profiles and DNS controls become important at every location. Secure SD-WAN can help choose among available WAN links, but it should be configured around measurable service-level objectives rather than a simple primary/secondary label. For wider regional IT context, FourTeck Ghana is part of the verified FourTeck network.
A Ghana quote request should include user/device estimates, current and planned bandwidth, VPN tunnel count, security services, subscription term and implementation expectations. If the organization needs long-term security logs or reporting, include FortiAnalyzer or the chosen logging destination in the architecture review. For HA, budget for the complete pair and associated service coverage. Clear procurement requirements reduce the chance that two suppliers quote materially different solutions under the same “FortiGate 120G” description.
FortiGate 120G Series Nigeria
Nigeria enterprises and distributed businesses can evaluate FortiGate 120G Series for secure internet, branch VPN, SD-WAN and segmented access. In a multi-provider environment, WAN design should reflect link quality, latency, packet loss and application needs rather than bandwidth alone. Secure SD-WAN policies can direct traffic according to measured conditions, but critical applications should be identified and tested. A backup link may be suitable for transactional systems and voice while being insufficient for unrestricted guest traffic or large cloud backups.
For headquarters and regional hubs, the number of branch tunnels and aggregate sessions can influence sizing. Fortinet publishes 3 million concurrent sessions and 140,000 new connections per second for the 120G Series, alongside the throughput figures already noted. These are vendor test figures and should be treated as sizing references, not guarantees for every production workload. SSL inspection, threat profiles, traffic mix and software configuration influence real performance. FourTeck Nigeria provides a regional path for broader IT service enquiries.
Nigeria procurement teams should compare the total proposed solution: appliance model, FortiCare, FortiGuard services, term, optics, HA, central management/logging and deployment. If an existing firewall is being replaced, prepare a list of public IPs, NAT rules, VPN peers and business owners for important policies. Migration should include a rollback plan and tests for internet, SaaS, DNS, email, voice and branch connectivity. This turns the firewall refresh into a controlled security improvement rather than a like-for-like configuration copy.
FortiGate 120G Series Seychelles
Seychelles organizations evaluating FortiGate 120G Series may place particular value on reliable remote administration, secure connectivity and careful business-continuity planning. Offices, hospitality properties and distributed operations can depend heavily on internet and cloud services, so the security gateway should be designed with provider handoffs and failover behavior clearly documented. If multiple WAN links are available, Secure SD-WAN can help steer traffic, but the policy should define which applications receive priority when capacity is constrained.
Segmentation is useful for environments that combine administrative users, guests, operational devices, cameras and servers. Guest traffic should be isolated from business systems, and management interfaces should be restricted. Where properties or offices connect back to a central site, IPsec VPN can protect inter-site traffic. Addressing should be coordinated across all locations to avoid overlapping networks, which can complicate routing and VPN deployment. If support teams manage sites remotely, configuration backups, secure management access and accurate diagrams become essential operational controls.
For a Seychelles quotation, provide internet speeds, expected growth, number of locations, VPN requirements, security-service expectations and desired support term. Include any fiber or transceiver needs and whether the appliance will be deployed as a single unit or HA pair. Consider the complete power chain as well: firewall, provider equipment and core switching should remain available together if UPS-backed continuity is required. The FortiGate 120G Series offers significant capability, but a resilient island deployment depends on matching that capability with connectivity, power and support planning.
Related FourTeck Tanzania infrastructure
A FortiGate deployment works best when the surrounding infrastructure is designed coherently. The verified FourTeck Tanzania home and solutions page covers firewall and VPN security, network switching, business Wi-Fi, servers and storage, structured cabling and UPS, integrated IT lifecycle services, IP telephony and CCTV. These related areas matter because firewall segmentation depends on managed switching; secure wireless depends on VLAN and policy design; server access depends on correctly defined zones; branch voice and video depend on WAN quality; and reliable security equipment depends on suitable rack and power infrastructure. The Tanzania shop is the verified product browsing destination, while the contact page is the verified quotation destination.
FortiGate 120G licensing and subscription planning
Do not treat the subscription as a minor accessory. Decide which FortiGuard security capabilities are required and for how long, and include the appropriate FortiCare support level. Renewal dates should be tracked as part of the asset lifecycle. If several FortiGate appliances are purchased at different times, organizations may want a renewal strategy that simplifies budgeting and administration. Before ordering, verify the exact bundle SKU and included services on the vendor or distributor quotation because service bundles and naming can change.
Organizations should also decide where logs will be retained and how they will be reviewed. Local appliance storage, centralized FortiAnalyzer, SIEM integration or other logging approaches serve different requirements. The 121G family option with storage can be relevant to some designs, but local disk does not automatically replace a centralized logging and retention strategy. Define operational objectives first: troubleshooting, incident investigation, reporting, audit retention and multi-site visibility can each drive different choices.
Quotation checklist
Existing firewall, internet circuits, public IPs, VLANs, switches and major applications.
Current and planned bandwidth, users, devices, VPN tunnels and expected growth.
IPS, web filtering, application control, malware protection, SSL inspection and other required controls.
Single appliance or HA, migration window, optics, rack, UPS and installation requirements.
Central management, logging, reporting, backups, administrator access and handover documentation.
Exact model, subscription bundle, term, FortiCare level, accessories and implementation scope.
FortiGate 120G Series FAQ
What is the firewall throughput of FortiGate 120G?
Fortinet publishes firewall throughput up to 39 Gbps for the FortiGate 120G Series. Security-enabled throughput is lower and should be used when sizing protected production traffic; Fortinet publishes 2.8 Gbps threat protection and 3 Gbps SSL inspection for the series.
Does FortiGate 120G support Secure SD-WAN?
Yes. FortiGate uses FortiOS to converge security and networking functions including Secure SD-WAN. The actual design should define WAN links, application priorities, health checks and failover behavior.
What is the difference between FortiGate 120G and 121G?
The family variants are closely related, with local storage being an important distinction: 120G is the diskless option and 121G adds internal storage. Confirm the exact vendor bill of materials before ordering.
How should I size a FortiGate 120G for Tanzania?
Provide current and future internet bandwidth, user/device counts, VPN requirements, enabled security services, SSL inspection plans, interfaces, branches and application profile. Sizing should use inspected-traffic requirements rather than firewall throughput alone.
Can FortiGate 120G be used with two internet connections?
Yes. Multiple WAN links can be incorporated into routing and Secure SD-WAN designs. The implementation should define failover tests, application steering, inbound-service behavior and backup-link capacity.
Do I need a FortiGuard subscription?
The required subscription depends on the security functions you intend to use. Buyers seeking ongoing threat-intelligence-backed services such as IPS, web filtering and related protections should select the appropriate FortiGuard bundle and FortiCare term on the quotation.
Decision recap
FortiGate 120G Series is positioned for organizations that need a substantial step above entry-level firewall capacity while retaining a compact FortiOS security edge. Its published 39 Gbps firewall, 35 Gbps IPsec VPN, 3 Gbps SSL inspection and 2.8 Gbps threat-protection figures make it relevant to many mid-sized office, branch, campus and distributed-enterprise designs. The purchasing decision should still be based on inspected traffic, WAN growth, VPN topology, interfaces, subscriptions, HA, logging and operational requirements. Confirm the exact 120G/121G model and complete bill of materials before ordering.
Plan your FortiGate 120G deployment
For a useful quotation, send FourTeck your current firewall model, internet bandwidth, expected growth, user/device estimate, number of branches, VPN requirements, required FortiGuard services, HA preference and deployment location. The team can use that information to frame the hardware, licensing and implementation scope rather than quoting an incomplete appliance-only requirement.




Reviews
There are no reviews yet.