
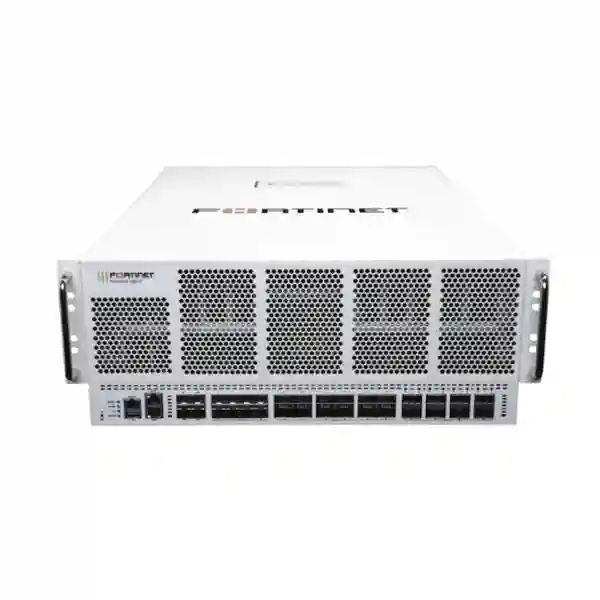
FortiGate 4800F Series
FortiGate 4800F Series is Fortinet’s high-end firewall platform for hyperscale data centres, large enterprise cores, cloud interconnects and service-provider environments that require exceptionally high throughput, dense high-speed connectivity and security inspection at scale. FourTeck Tanzania can help organizations translate traffic, interface, HA, subscription and migration requirements into a procurement-ready design.

FortiGate 4800F Series overview
Fortinet positions the FortiGate 4800F Series for high-performance data-centre, hybrid IT and hyperscale security. The current Fortinet series data sheet identifies FG-4800F and FG-4801F and lists 87 Gbps IPS, 77 Gbps NGFW and 75 Gbps threat-protection performance. It also lists multiple high-speed interface families including 400GE/200GE QSFP-DD, 200GE/100GE/40GE and 50GE/25GE/10GE connectivity. These published figures are useful planning references, but production sizing should account for FortiOS version, enabled inspection, traffic profile, packet sizes, VPN use, SSL inspection and vendor test conditions.
Fortinet documentation describes the 4800F architecture with sixteen NP7 network processors and specific NPU-group and hyperscale VDOM considerations. That makes topology planning important. A project should map upstream and downstream links, routing, segmentation, VDOM boundaries, high availability, logging and management before equipment is ordered. FortiGuard services, FortiManager and FortiAnalyzer requirements should be treated as part of the operating architecture rather than afterthoughts.
Key buying and deployment considerations
Begin with measured peak traffic, concurrent sessions, new connections per second, encrypted traffic share, IPsec VPN demand, NAT requirements and the inspection services that will be enabled. Then document physical interface speeds, optics, redundant carrier handoffs, routing protocols, segmentation, HA mode, rack power, cooling and change windows. A high-end platform should be justified by real workload and growth rather than selected only from headline throughput.
For licensing, identify required FortiGuard security services and support term. Confirm centralized management, analytics and log-retention needs. For migration, capture the current firewall configuration, routing, objects, NAT, VPNs, public services, identity dependencies and maintenance windows. A staged migration plan with rollback criteria is safer than treating replacement as a simple hardware swap.
Related FourTeck resources
Use FourTeck Tanzania technology solutions to coordinate firewall, switching, servers, Wi-Fi and infrastructure; browse the Tanzania technology shop; and use the verified Tanzania contact page for quotation requests. The Tanzania site also covers firewall and VPN planning, servers and storage, switching and LAN infrastructure, Wi-Fi, structured cabling, and integrated IT lifecycle services, all relevant dependencies for a data-centre firewall project.
For multi-country projects, related FourTeck resources include FourTeck Uganda, FourTeck Kenya, Fortinet UAE by FourTeck, FourTeck Ghana and FourTeck Nigeria.
FortiGate 4800F Series Tanzania
For Tanzania data-centre, telecom, financial-services, cloud, research and large-enterprise environments, the FortiGate 4800F Series is best evaluated as a high-end security platform rather than a routine branch firewall. National-scale projects may need resilient internet edges, inter-site aggregation, high-capacity VPN, segmentation and inspected traffic at very large scale. Procurement teams should document WAN and data-centre speeds, east-west and north-south traffic, VPN demand, segmentation boundaries, redundancy objectives, rack power, cooling and optics before finalizing a bill of materials.
The published performance figures should be mapped to the actual security profile. IPS, NGFW, threat protection and SSL inspection create different workloads. High availability also affects quantity, rack space, power, optics and cabling. FortiGuard subscriptions, management and analytics should be quoted with the hardware so the lifecycle cost is visible. Where multiple Tanzanian sites feed a central facility, branch traffic concentration and failover behavior should be modeled rather than estimated from user count alone.
FourTeck can use a requirements brief to structure the model and deployment discussion without assuming stock, delivery or a fixed bundle. Include existing firewall model, peak utilization, carrier links, interface media, routing, public services, VPNs, security services, HA expectations and growth. The objective is enough inspected capacity and interface headroom for the intended architecture while keeping operations, licensing and migration manageable.
FortiGate 4800F Series Dar es Salaam
Dar es Salaam projects can include carrier-facing facilities, corporate data centres, internet-edge environments and high-volume digital businesses. Dense connectivity and redundant upstream links make interface and routing design especially important. Buyers should map current and planned carrier handoffs, interface speeds, HA topology, change windows and migration dependencies so the platform is sized around real inspected traffic rather than headline bandwidth alone.
A useful design separates internet edge, public services, internal application zones, management and cloud connectivity. Where encrypted traffic inspection is required, teams should model its effect and define certificate, exception and privacy policies. Logging destinations and retention should be decided early. If FortiAnalyzer or another SIEM receives logs, bandwidth, storage and event-handling requirements become part of the solution.
For quotation preparation, include optics, cabling, redundant power, rack position, FortiGuard services, support term and management components. A maintenance-window and rollback plan should be agreed before migration. This turns the 4800F purchase from a hardware transaction into a controlled data-centre security project.
FortiGate 4800F Series Mwanza
Mwanza organizations considering the 4800F may be regional enterprise hubs, service platforms or multi-site businesses consolidating branch traffic. The key questions are how much traffic terminates locally, how much traverses WAN links, what security inspection is enabled and what must remain available during carrier or node failure. Secure aggregation, VPN scale, segmentation and resilient internet design should be quantified.
A hyperscale firewall can be appropriate when aggregate workload and growth justify it, but smaller FortiGate classes may be more efficient for ordinary branch requirements. Model selection should therefore compare inspected throughput, interface density, session scale, routing, VPN and HA requirements. This avoids oversizing while preserving a growth path.
For procurement, document branch count, peak aggregate traffic, critical applications, public services, cloud destinations, VPN tunnels, security subscriptions and logging. The resulting bill of materials should include the dependencies needed to make the platform operational, not only the appliance.
FortiGate 4800F Series Arusha
Arusha organizations may include hospitality groups, regional headquarters, international organizations, education and distributed enterprises. A 4800F-class platform is most relevant where traffic aggregation or data-centre scale exceeds ordinary campus requirements. Segmentation between staff, guest, server, voice, IoT and management networks can be combined with secure internet edge, partner connectivity and remote access.
Teams should identify critical SaaS and private applications, internet and WAN diversity, encrypted traffic, VPN requirements and growth. High availability should be designed around actual failure scenarios, including links, upstream routers, power and maintenance. Policy design should minimize unnecessary complexity and use clear zones and object naming so future administrators can understand the environment.
A quotation request should state whether the project is a new build, replacement or consolidation. Include existing configurations, routing, address plans, required interfaces, subscriptions and management tools. This helps determine whether the 4800F is architecturally justified and what migration effort is required.
FortiGate 4800F Series Dodoma
Dodoma government-scale environments, institutions and national organizations may value policy consistency, resilient inter-site connectivity, high-throughput inspection and scalable segmentation. Procurement should capture compliance requirements, administrative domains, logging retention, HA expectations, change-control procedures and the number and speed of connected networks.
Where multiple departments or tenants share infrastructure, VDOM and segmentation design should be planned carefully. Management roles, configuration approval, logging and backup procedures should be documented. Security subscriptions should reflect the controls actually required rather than being chosen solely by bundle name.
For a structured tender or quotation, include measurable acceptance criteria such as interface connectivity, routing convergence, VPN operation, policy migration, logging, HA failover and agreed security services. This creates a clearer technical basis for commissioning and support.
FortiGate 4800F Series UAE
In the UAE, the 4800F Series fits hyperscale data centres, cloud interconnects, service-provider networks and large enterprise cores requiring very high interface density and security throughput. Design teams should validate optics, breakout requirements, rack and power planning, FortiGuard services, support terms and whether FG-4800F or FG-4801F aligns with the logging architecture.
High-speed 400GE/200GE connectivity can influence the surrounding switching and routing design, so the firewall should not be specified in isolation. HA, routing convergence, segmentation, cloud connectivity and maintenance procedures should be validated end to end. For carrier or hyperscale uses, current Fortinet guidance for NPU groups and hyperscale VDOMs should be reviewed during detailed design.
FourTeck’s Fortinet UAE specialist resource can support regional procurement discussions. Current price, stock, support and delivery should be confirmed at quotation time rather than assumed from a static product page.
FortiGate 4800F Series Uganda
Uganda national enterprises, service providers and financial networks can evaluate the 4800F where branch aggregation, high-capacity VPN, resilient internet edge and centralized policy create a genuinely large workload. Buyers should quantify aggregate traffic from branches, inspection profiles, routing, logging and failover requirements.
A hyperscale platform should be justified by measured or forecast workload. Interface requirements, session scale and future carrier upgrades can be as important as current internet bandwidth. Centralized management can help multi-site teams maintain consistent objects, policies and firmware processes.
A complete request should include the existing firewall estate, branch count, VPN design, public services, FortiGuard requirements and HA expectations. This supports an architecture comparison rather than a model-only quote.
FortiGate 4800F Series Kampala
Kampala large headquarters, data-centre facilities, banks, telecom environments and digital services may need dense enterprise connectivity, redundant carrier links, SSL inspection and centralized security operations. A useful quotation includes interface speeds, current firewall utilization, session peaks, VPN throughput, security profiles, HA mode and management requirements.
Migration planning should identify routing, NAT, VPNs, public applications, certificates and identity integrations. Logging should be tested alongside traffic forwarding. Where availability is critical, failover testing should cover links and upstream dependencies as well as the firewall pair.
This level of preparation helps procurement distinguish hardware cost from the complete operational solution, including subscriptions, optics, analytics and implementation work.
FortiGate 4800F Series Arua
Arua deployments are more likely to involve regional aggregation and distributed institutions than hyperscale data centres, so architecture fit is central. Teams should compare aggregate workload with the 4800F class and avoid oversizing where a smaller FortiGate can meet inspected-throughput, interface and resilience requirements.
Where a central platform serves many remote sites, secure site-to-site connectivity, centralized policy and reliable failover become important. Carrier diversity, remote support and spare strategy should be considered alongside security performance.
Provide measured bandwidth, branch count, tunnel requirements, growth and critical application paths for a useful model-selection discussion. The result may confirm the 4800F or point to another FortiGate class that better matches the workload.
FortiGate 4800F Series Mbarara
Mbarara enterprises, education, healthcare and financial operations may require secure aggregation, segmentation, VPN and continuity across multiple links. A 4800F is appropriate only where those requirements reach high-end data-centre scale.
Requirements should include user and device growth, data-centre or cloud destinations, critical application paths, expected security services and recovery behavior when a WAN circuit or firewall node fails. Operational teams should also define logging, backup and change-control practices.
By documenting these inputs before quotation, buyers can compare the 4800F with other models on relevant criteria and avoid paying for unused scale or, conversely, selecting insufficient inspection headroom.
FortiGate 4800F Series Gulu
Gulu organizations with distributed sites may prioritize secure connectivity, centralized controls and resilient branch-to-core communication. Traffic concentration points, remote-site dependencies, carrier diversity and operational support processes should be documented before considering a hyperscale platform.
If a central data centre aggregates many branches, VPN and session scale can become significant. If the requirement is mainly a regional office internet edge, another FortiGate may be a better fit. Sizing should be based on inspected traffic and future growth rather than location or user count alone.
A procurement brief should therefore include topology, bandwidth, tunnels, security services, HA, management and logging. This provides a practical basis for selecting hardware and subscriptions.
FortiGate 4800F Series Kenya
Kenya large enterprise, carrier, cloud, financial and data-centre deployments can use the 4800F for high-capacity internet edge, east-west segmentation, cloud interconnect, VPN scale and security consolidation. Procurement should coordinate interface media, optics, routing, HA, FortiGuard subscriptions, centralized management and migration planning.
Where regional traffic is concentrated through major data-centre sites, peak aggregate throughput and session creation can matter more than individual branch bandwidth. The design should model failure states so backup links and nodes can carry the required inspected load.
FourTeck Kenya provides a regional route for related enquiries, while current Fortinet documentation should remain the technical authority for model specifications and configuration guidance.
FortiGate 4800F Series Kuwait
Kuwait enterprise data centres, service providers and government-scale networks may require high-speed interfaces, large connection scale, SSL inspection, segmentation and resilient perimeter design. Buyers should validate rack, power, upstream connectivity, security subscriptions, support term and logging architecture.
Integration with routing and identity systems should be included in the design. Where a firewall pair protects critical applications, maintenance and failover procedures should be tested under representative traffic. Optics and cabling should be treated as engineered components, especially at very high interface speeds.
A complete commercial request should distinguish appliance, subscriptions, support, transceivers, management, analytics and implementation so procurement can compare total scope rather than incomplete hardware prices.
FortiGate 4800F Series Ghana
Ghana large enterprises, financial services and service providers can evaluate the 4800F for secure internet edge, data-centre segmentation, VPN scale and policy consistency across growing networks. A project brief should state current and planned bandwidth, session peaks, critical applications, HA objectives, inspection features and management requirements.
If multiple sites aggregate through one security edge, growth should include branch expansion and cloud usage. Logging, analytics and incident-response workflows should be considered during design because visibility is part of the operational value of a high-end firewall.
FourTeck Ghana can support regional technology enquiries, while product specifications should be checked against current Fortinet material at the time of procurement.
FortiGate 4800F Series Nigeria
Nigeria high-volume digital businesses, telecom environments, financial platforms, cloud-connected enterprises and large data centres may need massive connection handling, high-speed interfaces, encrypted traffic inspection and resilient scale. Teams should model peak rather than average traffic, growth, NAT and VPN demand, logging, routing convergence and failure scenarios.
For very large services, connection rate and concurrent sessions can be as important as Gbps throughput. Security controls should be defined by application and risk, and the operational team should plan policy governance, firmware, backups and analytics. High availability should be tested with upstream and downstream devices so failover behavior is understood.
FourTeck Nigeria provides a regional route for related enquiries. A current quote should confirm exact model, subscription, support, optics, implementation and availability rather than relying on static assumptions.
FortiGate 4800F Series Seychelles
Seychelles service providers, hospitality groups, financial organizations and enterprises with concentrated international connectivity may prioritize secure internet edge, VPN, segmentation, controlled remote access and continuity. Buyers should align firewall capacity with actual carrier bandwidth and future upgrades, then define HA, subscriptions, remote management and change procedures.
Because international connectivity can be operationally critical, failure-state design deserves special attention. Teams should document primary and backup links, routing, DNS dependencies, cloud applications and remote administration. A hyperscale appliance should be selected only where workload, interfaces or growth justify the class.
Quotation preparation should include logistics, support expectations, spare strategy, optics and licensing as well as the appliance. This creates a more complete lifecycle plan for an island deployment.
FortiGate 4800F Series FAQs
Is FortiGate 4800F a branch firewall?
Fortinet categorizes it as a high-end data-centre platform. It is generally evaluated for very large enterprise, hyperscale, cloud, carrier and service-provider workloads rather than ordinary branch use.
What models are in the series?
Fortinet’s series data sheet identifies FG-4800F and FG-4801F. Confirm the exact model and current orderable configuration with the quotation.
What should a quotation request include?
Include quantity, HA, current and future traffic, interface speeds and media, routing, VPN and NAT requirements, security services, FortiGuard term, management or analytics needs, rack and power constraints, and migration window.
Quotation checklist and decision recap
Prepare required quantity, model preference, HA topology, current and planned throughput, session and connection-rate data where measured, VPN demand, NAT requirements, interface speeds, transceivers, segmentation, FortiGuard services, support term, FortiManager or FortiAnalyzer needs, log retention, rack space, power, cooling, routing protocols and migration dependencies. If values are unknown, provide the existing firewall model and topology.
The decision should be based on architecture fit, not the largest published number. The 4800F Series is relevant where a network genuinely needs high-end data-centre interfaces, hyperscale connection handling and substantial inspected throughput. Where requirements are smaller, another FortiGate class may be more appropriate.




Reviews
There are no reviews yet.