
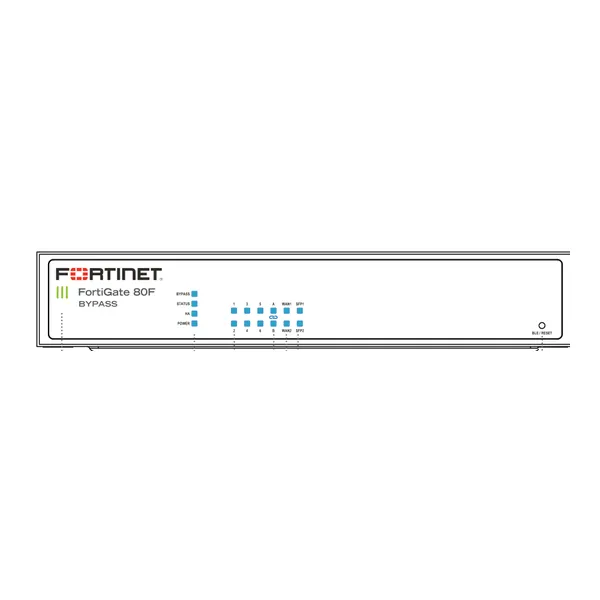
FortiGate 80F Bypass (FG-80F-BP) Tanzania
FortiGate 80F Bypass, model FG-80F-BP, brings Fortinet next-generation firewall protection to networks that also require a physical fail-open path. Fortinet documents a copper bypass pair formed by WAN1 and port 1, identified as internal1 in FortiOS. When bypass conditions apply, those ports can connect directly so traffic continues to flow without traversing the FortiOS firewall. That characteristic makes the model particularly relevant where continuity of an inline network path must be considered alongside firewall inspection, VPN, segmentation and threat protection. FourTeck helps organizations in Tanzania evaluate the appliance in the context of topology, Internet circuits, VLAN design, security subscriptions, FortiSwitch and FortiAP integration, VPN requirements and operational support.
What makes the FG-80F-BP different?
The principal distinction is the bypass pair. Fortinet specifies WAN1 and internal1 as a copper bypass pair on this model. If the appliance loses power, experiences a relevant failure, or bypass is deliberately enabled under supported conditions, the pair can operate as a direct path. In bypass state the firewall and NP6XLite processing path are not inspecting that traffic, so continuity and security policy must be considered together. This is not simply a second WAN feature: it is a hardware-oriented continuity function intended for an inline path. The SFP1 interface is not part of that bypass pair.
Verified performance
Fortinet rates the 80F series at up to 10 Gbps IPv4 firewall throughput, 1.4 Gbps IPS throughput, 1 Gbps NGFW throughput and 900 Mbps threat-protection throughput. Real performance varies with configuration, traffic and enabled security services.
VPN capacity
The datasheet lists up to 6.5 Gbps IPsec VPN throughput and 950 Mbps SSL-VPN throughput. Buyers should size remote access and site-to-site VPNs around actual cipher suites, user concurrency, inspection requirements and WAN capacity.
Interfaces
The platform provides two GE RJ45/SFP shared-media pairs, six GE RJ45 internal ports, two default FortiLink GE RJ45 ports, USB 3.0 and an RJ45 console. Shared-media pairs require choosing the copper or SFP member of each pair.
FortiGate 80F Bypass technical overview
| Model | FG-80F-BP / FortiGate 80F Bypass |
| Bypass | WAN1 and port 1/internal1 copper fail-open pair |
| Firewall throughput | Up to 10/10/7 Gbps for 1518/512/64-byte UDP |
| IPS / NGFW / Threat Protection | Up to 1.4 / 1 / 0.9 Gbps |
| IPsec VPN | Up to 6.5 Gbps |
| Concurrent TCP sessions | Up to 1.5 million |
| Architecture | SOC4 with NP6XLite and CP9XLite acceleration |
Performance figures are vendor-published maximums and vary by system configuration, traffic profile, inspection features and software version.
Deployment, integration and buying guidance
A sound FG-80F-BP deployment begins with topology. Determine whether the firewall will operate routed or transparent, which physical path requires bypass behavior, how WAN1 and internal1 connect to adjacent equipment, and whether VLAN tags must traverse the bypass state. Fortinet notes that network extensions such as VLANs continue only when connected equipment is configured appropriately. Teams should therefore document switch trunks, native VLANs, addressing, routing, DHCP, DNS, SD-WAN policy, VPN peers and monitoring before cutover.
Security sizing should go beyond headline firewall throughput. IPS, malware protection, SSL inspection, application control and logging alter effective capacity. Procurement teams should capture user count, peak Internet bandwidth, encrypted-traffic percentage, branch-to-head-office VPN demand, expected growth and the required FortiGuard service bundle. If FortiSwitch or FortiAP management is planned, include device counts and topology. For resilient designs, also evaluate high availability, power protection, circuit diversity and configuration backup rather than treating bypass as a substitute for a complete continuity strategy.
For broader Fortinet planning, visit FourTeck Tanzania technology solutions. Organizations with cross-border requirements can also review FourTeck Uganda, FourTeck Kenya, Fortinet solutions in the UAE and FourTeck Africa for related regional solution context.
FortiGate 80F Bypass (FG-80F-BP) Tanzania
For organizations evaluating the FortiGate 80F Bypass in Tanzania, the important question is not only whether the appliance can meet a bandwidth figure, but whether its bypass architecture fits the operational design. The model is relevant to businesses, institutions, distributed offices, service environments and network edges where an inline firewall is expected to inspect normal traffic while a defined copper path can fail open under bypass conditions. Tanzania deployments can range from a single business site to multi-branch networks linking offices through IPsec VPN, SD-WAN or private connectivity. In each case, requirements should identify the circuits terminating on the appliance, the internal segmentation plan, expected security inspection, remote-user needs and the consequence of a firewall outage.
A quotation request should state current and planned Internet bandwidth, number of users and sites, whether SSL inspection will be used, VPN tunnel counts, remote-access requirements, logging expectations and desired FortiGuard services. Where the firewall will be inserted into an existing path, document the devices immediately upstream and downstream of WAN1/internal1 and whether that path carries tagged VLANs. This makes it easier to validate how fail-open behavior interacts with the network rather than assuming bypass automatically preserves every service.
Tanzania buyers should also plan lifecycle operations: FortiOS upgrades, configuration backups, administrator authentication, log retention, security-profile tuning and subscription renewals. The appliance supports centralized Fortinet ecosystem integration, but the operational model should match the skills and monitoring processes available to the organization. FourTeck can help translate those requirements into a bill of materials and deployment scope without treating the published maximum throughput as guaranteed application performance. This procurement-led approach is particularly useful when the FG-80F-BP is part of a larger refresh involving switches, wireless, VPN connectivity or branch standardization.
FortiGate 80F Bypass (FG-80F-BP) Dar es Salaam
Dar es Salaam organizations often concentrate headquarters, customer-facing systems, Internet breakout and inter-branch connectivity in the same network edge. The FG-80F-BP can be considered where a compact FortiGate platform is needed together with a fail-open copper pair. For an office, retail operation, professional-services environment, logistics company or distributed enterprise, planning should begin by mapping primary and secondary Internet circuits, LAN segmentation, public services, cloud access and VPN connections. The bypass pair is specifically WAN1 and internal1; therefore cabling and port assignment should be deliberate from the design stage.
If the appliance is being introduced into a live Dar es Salaam network, the change plan should record current gateway addresses, static routes, NAT rules, inbound publishing, DHCP roles, VLANs and any IPsec peers. Security profiles can then be introduced according to application and risk requirements. SSL inspection deserves special sizing attention because encrypted application traffic is now common, while threat-protection throughput is lower than raw stateful firewall throughput. Buyers comparing appliances should therefore use the workload that will actually run in production rather than selecting solely by the largest headline number.
For multi-site companies, the 80F platform can participate in Fortinet SD-WAN and VPN designs, but branch count, tunnel count, routing design and central logging should be specified before purchase. Bypass is useful for a particular continuity objective, yet it does not replace redundant circuits, HA where required, UPS planning or tested recovery procedures. A useful Dar es Salaam quotation brief includes ISP speeds, public IP requirements, user count, server and cloud dependencies, FortiSwitch/FortiAP integration needs, subscription term and implementation expectations. With those inputs, FourTeck can frame the FG-80F-BP around the actual network instead of a generic firewall bundle.
FortiGate 80F Bypass (FG-80F-BP) Mwanza
In Mwanza, the FG-80F-BP may suit organizations that need a secure branch or campus edge while maintaining a defined fail-open path between two copper interfaces. This can be relevant when business applications, cloud services, voice, ERP access or connections to another site depend on the inline network path. The design objective should be explicit: decide which traffic needs FortiGate inspection in normal operation and what traffic behavior is acceptable if the appliance enters bypass. Because bypass traffic does not pass through normal FortiOS inspection, continuity planning must be balanced with security requirements.
A Mwanza deployment can also use the platform for IPsec site-to-site connectivity, remote-user access, application control, IPS and segmentation. Fortinet publishes up to 6.5 Gbps IPsec throughput for the series, but actual performance depends on encryption, packet sizes and concurrent security functions. If the site connects to a head office, data center or cloud gateway, document tunnel peers, routing, failover rules and overlapping networks before configuration. If dual Internet links are planned, distinguish SD-WAN failover between circuits from the physical fail-open bypass function; they solve different availability problems.
Procurement should include the correct FortiGuard subscription strategy, support entitlement and any transceivers or complementary switching required by the final topology. The FG-80F-BP offers two shared RJ45/SFP media pairs, so the design should account for the shared nature of those interfaces rather than counting copper and SFP members as simultaneously independent ports. A good request for quotation identifies bandwidth, users, VLANs, VPNs, security services, deployment mode and expected growth. FourTeck can use that information to help Mwanza customers determine whether the bypass model is the appropriate 80F variant and how it should fit into a broader security architecture.
FortiGate 80F Bypass (FG-80F-BP) Arusha
Arusha businesses considering the FortiGate 80F Bypass may include hospitality groups, offices, education environments, service businesses and organizations connecting several sites. The appliance is most compelling when the network requires FortiGate inspection under normal conditions while a specific copper segment must have a fail-open option. Before selecting it, identify whether that requirement genuinely exists. If the objective is simply dual-ISP resilience, FortiGate SD-WAN may address circuit failover without relying on the bypass pair. If the objective is to keep an inline physical path conducting traffic during appliance power loss or failure, the FG-80F-BP’s WAN1/internal1 pair is the relevant feature.
For hospitality and guest-facing environments, segmentation between corporate systems, staff networks, guest access, IoT devices and payment-related services can be more important than raw port count. For offices, priorities may include secure Internet access, Microsoft 365 or cloud application performance, remote VPN and branch connectivity. The security policy should be designed around those traffic classes, with logging and inspection appropriate to each. If FortiAP or FortiSwitch products are used, FortiLink-based management can be part of the design, subject to model and topology limits.
Arusha procurement teams should request a solution based on measured or contracted bandwidth and realistic growth. Include the number of sites, VPN peers, users, public services and any requirement for SSL inspection. Subscription selection should reflect the security services the organization intends to operate, while renewal dates should be recorded as part of lifecycle management. FourTeck can assist with a configuration and quotation discussion that considers bypass placement, network interfaces and related Fortinet components, helping buyers avoid choosing a model based only on the product family name.
FortiGate 80F Bypass (FG-80F-BP) Dodoma
Dodoma organizations can evaluate the FG-80F-BP for branch, institutional and enterprise-edge networks where continuity and security must be planned together. Government-adjacent offices, professional organizations, educational institutions and distributed enterprises may have different compliance and operational requirements, so the firewall should be sized from documented traffic and security policy. The bypass model’s defining capability is a fail-open pair between WAN1 and internal1. When bypass operates, connectivity can continue across that pair without normal FortiOS firewall processing, an important behavior to understand during risk assessment.
Deployment planning should identify which systems depend on the path, how VLANs are transported, and what upstream/downstream equipment expects. If transparent mode is considered, Fortinet documents specific configuration requirements before manually enabling bypass, including removing internal1 from the default internal hardware switch. Production changes should follow an approved implementation and rollback plan rather than copying commands without topology validation. FortiOS version, configuration syntax and organizational change controls should be checked at deployment time.
Beyond bypass, the 80F series provides the core functions expected of a FortiGate NGFW: firewall policy, IPS, application control, VPN and integration with the Fortinet ecosystem. For a Dodoma quotation, buyers can prepare ISP details, bandwidth, VLAN inventory, address ranges, site-to-site VPN peers, remote-user counts, security subscriptions and required support term. If the network has future expansion plans, state expected branch and user growth. FourTeck can then discuss whether the FG-80F-BP has an appropriate performance and interface profile or whether another FortiGate model should be considered during solution sizing.
FortiGate 80F Bypass (FG-80F-BP) UAE
For UAE deployments, the FG-80F-BP is relevant to branch and inline security designs that specifically require a copper fail-open path. Organizations operating across the UAE and East Africa may also seek a consistent FortiGate architecture for branches, VPN connectivity and security policy. Standardization can simplify templates and operations, but each site should still be sized according to local circuit speed, application mix and inspection load. The bypass feature should be mapped to a precise physical segment rather than enabled as a general availability measure.
A cross-regional design may use IPsec VPN or SD-WAN to connect UAE offices with Tanzania or other locations. In that case, route design, tunnel topology, centralized logging, DNS, identity integration and security profiles should be agreed before appliance staging. Fortinet’s rated throughput values provide useful comparison data, while production sizing should account for SSL inspection, IPS, application control and malware protection. For encrypted traffic, inspection policy can materially affect throughput and should be tested against expected workloads.
Buyers should also determine FortiGuard subscription term, support entitlement and whether FortiManager or FortiAnalyzer is part of the operational model. For organizations managing many appliances, centralized policy and reporting may be more important than the configuration of any single branch firewall. The UAE-focused Fortinet resource at FourTeck Fortinet UAE provides a regional route for related requirements. A quotation should identify the exact FG-80F-BP model, desired subscription bundle, quantity and implementation scope to prevent confusion with the standard 80F, 81F or PoE variants.
FortiGate 80F Bypass (FG-80F-BP) Uganda
Uganda organizations assessing the FG-80F-BP can use the same procurement discipline: define the need for a fail-open copper path, then size the security platform around actual traffic. A business with multiple branches may need IPsec VPN, SD-WAN, centralized policy and secure Internet access, while an inline service environment may prioritize the bypass function. These requirements should be separated because bypass, WAN failover and HA address different failure scenarios.
When the firewall is placed between existing network devices, confirm interface speed, VLAN tagging, routing and the behavior expected during bypass. Fortinet explains that WAN1 and internal1 are directly connected in bypass mode, allowing traffic to continue while bypassing the FortiOS firewall and acceleration processor. That means security controls normally enforced by the firewall are not active on that bypassed traffic. Organizations should incorporate this behavior into their risk and incident procedures.
For regional companies with Tanzania and Uganda operations, consistent FortiGate policies can simplify administration, provided site-specific needs are retained. Consider management access controls, MFA for administrators, logging, configuration backups, firmware lifecycle and subscription renewal. The FourTeck Uganda site can support Uganda-oriented solution discussions. Procurement teams should include circuit bandwidth, user count, VPNs, VLANs, desired FortiGuard bundle and installation expectations in the RFQ so the appliance and services can be scoped accurately.
FortiGate 80F Bypass (FG-80F-BP) Kampala
Kampala deployments may involve head offices, branch aggregation, cloud connectivity and remote users. The FG-80F-BP offers a useful combination when those security requirements coexist with a need for an inline fail-open path. Before purchase, the network team should decide whether WAN1/internal1 will sit between a carrier device and core network, between internal network segments, or in another transparent inline design. That physical decision influences routing, policy and bypass behavior.
Capacity planning should use the security services that will be enabled. Fortinet publishes 1.4 Gbps IPS, 1 Gbps NGFW and 900 Mbps threat-protection figures for the series under defined test conditions. A Kampala office with a high proportion of encrypted cloud traffic may have different effective throughput from a site dominated by simple stateful firewall traffic. SSL inspection policy, logging and VPN encryption should therefore be included in the design conversation.
For multi-branch environments, consider how the firewall will be monitored and updated. Central management, consistent object naming, standardized VPN templates and configuration backups can reduce operational errors. If a bypass event occurs, monitoring should make the condition visible so teams do not assume normal inspection is still active. A Kampala quotation can include hardware, FortiGuard term, support, configuration, migration and testing as separate scope elements. Clear scope makes it easier to compare proposals and understand which recurring licenses or services are required after the initial purchase.
FortiGate 80F Bypass (FG-80F-BP) Arua
For an Arua branch or regional office, the FG-80F-BP can be assessed as a compact edge firewall with a specialized bypass capability. Remote sites often depend heavily on a small number of WAN circuits, so the design should distinguish between circuit failure and firewall-appliance failure. SD-WAN can help select among available links, while the physical bypass pair can preserve the defined inline path when the firewall itself is unavailable under supported bypass conditions.
The branch design should inventory business-critical applications, cloud services, voice, remote desktop, ERP and site-to-site traffic. From that inventory, security profiles and QoS or SD-WAN rules can be developed. If the site is managed from another city, secure administrative access and centralized logging become important. The bypass state should also be monitored because traffic passing directly through WAN1/internal1 is not receiving normal FortiGate inspection.
A practical Arua RFQ should state whether the unit is a new deployment or replacement, the existing firewall model, WAN bandwidth, internal switch topology, VLANs, VPN peers and required subscription duration. If remote staging is needed, provide addressing and configuration requirements in advance while protecting sensitive credentials through appropriate channels. FourTeck can use this information to scope the appliance and related implementation work, while the customer retains a clear record of the security functions and continuity behavior expected at the site.
FortiGate 80F Bypass (FG-80F-BP) Mbarara
Mbarara businesses and institutions can consider the FG-80F-BP where secure branch connectivity must be combined with an intentional fail-open design. The model supports the wider FortiGate feature set while adding the WAN1/internal1 bypass pair. This makes the product different from choosing a standard branch firewall solely for throughput. The network team should document what happens to applications if the appliance is powered off, what traffic would continue through the bypass path, and whether that behavior is acceptable from a security perspective.
If the site uses multiple Internet links, define the SD-WAN policy independently from bypass. Link health checks, preferred application paths and failover thresholds can improve WAN resilience, but they operate while the FortiGate is functioning. The bypass pair addresses a different condition. Similarly, high availability using two firewalls can provide stateful resilience in designs that justify it, whereas a single bypass appliance trades inspection for continuity on its defined pair during bypass.
Mbarara procurement teams can improve quote accuracy by listing the number of employees, devices, VLANs, wireless networks, VPN tunnels and public services. Include current bandwidth and expected upgrades. Ask for clarity on subscription bundle, support term and any installation or migration service. This gives decision makers a complete view of first-year and renewal considerations. FourTeck can then discuss the FG-80F-BP in relation to the branch architecture rather than positioning bypass as a universal solution to every availability requirement.
FortiGate 80F Bypass (FG-80F-BP) Gulu
Gulu sites that need centralized security policy, VPN connectivity and an inline fail-open path can evaluate the FG-80F-BP as part of a broader network design. The appliance uses Fortinet’s SOC4 architecture with NP6XLite and CP9XLite processing. For buyers, the practical benefit is a platform designed to accelerate network and security processing while providing the FortiOS feature set. The bypass model adds the specific WAN1/internal1 physical continuity behavior.
Before deployment, confirm whether the firewall will be routed or transparent, which interface pair carries the critical path, and how addressing and VLANs are handled. Fortinet documents manual bypass enablement in transparent mode under particular conditions; configuration should always be validated against the FortiOS release used at deployment. Operational teams should avoid treating an old configuration example as universally applicable to future firmware.
For a Gulu branch connected to a central office, define IPsec encryption, routing, tunnel failover and DNS dependencies. For local Internet breakout, identify application categories, web filtering, IPS and malware-protection requirements. Logging and alerting should show link, tunnel and device status. The RFQ should also state whether the project includes migration from an existing firewall, because policy conversion, VPN coordination and cutover testing can be significant parts of the work. With a complete brief, the FG-80F-BP can be evaluated against real operational requirements instead of a generic product checklist.
FortiGate 80F Bypass (FG-80F-BP) Kenya
Kenya organizations may consider the FG-80F-BP for distributed offices, inline network security and regional standardization. Companies operating in both Kenya and Tanzania can benefit from a common FortiGate policy framework, but each location should still be sized individually. ISP capacity, cloud usage, local applications and user density can vary significantly. The bypass feature should be used only where the physical topology and continuity objective justify it.
The 80F series supports substantial stateful firewall and VPN performance for its class, but security-service throughput is the more useful metric when IPS, application control and malware protection are active. Procurement should therefore specify which services will be enabled and the expected encrypted-traffic load. If SSL inspection is required, certificate deployment, application exceptions and endpoint trust should be part of the implementation plan as well as appliance sizing.
For cross-border networks, IPsec or SD-WAN design should include routing, link health, latency-sensitive applications and centralized monitoring. Bypass does not automatically preserve remote connectivity if an upstream circuit, router or downstream switch fails, so resilience should be considered end to end. The FourTeck Kenya site provides a regional point for related requirements. A complete Kenya quotation request should identify the exact FG-80F-BP model, quantities, subscription term, implementation scope and any complementary Fortinet products needed for the project.
FortiGate 80F Bypass (FG-80F-BP) Kuwait
For Kuwait offices and regional enterprises, the FG-80F-BP can be considered when a FortiGate branch platform is needed with a dedicated fail-open copper pair. The product may be relevant to an inline security segment where continuity of the physical path is an explicit design requirement. As with every bypass deployment, the organization should understand that traffic flowing through the bypass pair is not being inspected by normal FortiOS security policy during that state.
Regional enterprises may use the appliance as part of a consistent Fortinet architecture spanning multiple countries. That can simplify policy templates, VPN design and administration, while licensing and support should still be tracked per device and region. For sites using high-speed Internet and extensive encrypted traffic, compare expected security-service load with vendor-rated IPS, NGFW, threat-protection and SSL-inspection performance rather than relying on the raw 10 Gbps firewall figure.
A Kuwait procurement brief should include current firewall, WAN circuits, number of users, site-to-site and remote-access VPN needs, VLANs, public services, FortiGuard subscription expectations and implementation timing. If the unit will be inserted into an existing inline path, include the adjacent equipment and cabling details. This reduces surprises during staging. FourTeck can use those inputs to help define a bill of materials and scope that reflects the exact FG-80F-BP variant and its role within the customer’s regional network.
FortiGate 80F Bypass (FG-80F-BP) Ghana
Ghana businesses evaluating FortiGate can select the FG-80F-BP when a branch-class NGFW must also provide a defined copper fail-open path. The bypass pair is useful only when it aligns with the topology, so design should start with a physical and logical network diagram. Identify Internet circuits, routers, switches, VLANs, servers, cloud services and remote sites, then decide where the firewall sits and what should happen during a bypass event.
For normal operation, FortiOS can provide firewall policy, IPS, application control, VPN and other security capabilities according to the licenses and configuration in use. Capacity should be based on expected inspected traffic. If the site runs substantial cloud collaboration, video or SaaS traffic, encrypted-session load can be important. If the organization uses site-to-site VPN, document encryption and tunnel count. These details matter more to sizing than a simple user-count rule.
Procurement should also define who will administer the device, how logs are retained, how firmware is maintained and when subscriptions renew. If several branches are involved, centralized management and reporting may reduce operational effort. The request for quotation should separate hardware, subscription, support and professional services so buyers can understand recurring costs. FourTeck can discuss the FG-80F-BP as part of that complete security lifecycle and help ensure the bypass requirement is technically intentional rather than an accidental model selection.
FortiGate 80F Bypass (FG-80F-BP) Nigeria
Nigeria organizations with branch offices, distributed operations or inline network-security requirements can evaluate the FG-80F-BP for FortiGate security combined with fail-open connectivity on WAN1/internal1. The platform can support secure Internet access, IPsec VPN, remote access, application visibility and threat inspection, while the bypass pair provides a different continuity mechanism for its physical segment. Buyers should define which problem each feature solves.
A multi-site Nigerian enterprise may place strong emphasis on SD-WAN and centralized policy. Link quality, circuit diversity, application steering and VPN topology can be designed independently of bypass. If a firewall outage occurs, the bypass pair may keep the defined path conducting traffic, but it cannot compensate for failures elsewhere in the network. Monitoring should therefore cover device state, links, tunnels and security events, and the organization should know when traffic is no longer receiving normal inspection.
For accurate procurement, specify peak bandwidth, user and device counts, number of branches, VLANs, VPN tunnels, public applications and expected security profiles. Confirm the FortiGuard package and term required, along with support and implementation. Where SSL inspection is part of policy, include its operational impact and certificate deployment. FourTeck can help frame the FG-80F-BP within a wider regional security architecture and provide a quotation based on the exact model and requested service scope rather than an assumed generic FortiGate configuration.
FortiGate 80F Bypass (FG-80F-BP) Seychelles
Seychelles deployments can have particular sensitivity to WAN continuity because business applications and cloud services may depend heavily on external connectivity. The FG-80F-BP can be evaluated where the network design calls for a FortiGate NGFW and a fail-open copper segment. Its bypass function is specific: WAN1 and internal1 can be directly connected during bypass, allowing traffic to flow without normal firewall processing. That behavior should be explicitly accepted in the security design.
For hospitality, professional services and distributed businesses, segmentation may separate guests, staff, servers, IoT and operational systems. The firewall can enforce policy between appropriate zones in normal operation, while VPN can connect remote offices or administrators. If bypass is used on a path carrying tagged VLANs, the surrounding network equipment must be configured so those extensions can continue appropriately. This is a topology issue that should be validated during staging and testing.
A Seychelles RFQ should identify ISP capacity, secondary connectivity, users, VLANs, VPNs, required FortiGuard services and any central-management platform. Include expected growth and critical applications. If the firewall is replacing another vendor or FortiGate model, provide a migration inventory so rules and tunnels can be reviewed rather than blindly copied. FourTeck can then help assess the FG-80F-BP against the real site requirements, with clear separation between vendor-rated performance, security subscriptions and implementation services.
FortiGate 80F Bypass selection checklist
Network facts
Record WAN bandwidth, circuit types, VLANs, routing, public IPs, DHCP/DNS roles, user and device counts, critical applications, existing switches and wireless infrastructure.
Security load
Define IPS, application control, malware protection, web controls, SSL inspection, VPN encryption, remote-access users, logging and reporting requirements.
Bypass objective
Identify the exact physical path using WAN1/internal1, acceptable security behavior during bypass, VLAN requirements and monitoring or incident-response expectations.
Frequently asked questions
What is special about the FortiGate 80F Bypass?
The FG-80F-BP includes a copper bypass pair using WAN1 and port 1/internal1. Under supported bypass conditions the pair can connect directly, maintaining the physical traffic path while bypassing normal FortiOS firewall processing.
Is bypass the same as dual-WAN failover?
No. Dual-WAN or SD-WAN failover selects among available WAN links while the FortiGate is operating. The FG-80F-BP bypass pair is a fail-open physical path associated with WAN1 and internal1. They address different availability scenarios.
Does traffic remain protected when the appliance is in bypass?
Traffic crossing the bypass pair bypasses the FortiOS firewall and NP6XLite processing path, so the normal FortiGate security inspection is not applied to that traffic. This is why bypass behavior should be included in risk and continuity planning.
What performance does Fortinet publish for the 80F series?
Fortinet publishes up to 10 Gbps IPv4 firewall throughput, 1.4 Gbps IPS, 1 Gbps NGFW, 900 Mbps threat protection, 6.5 Gbps IPsec VPN and 950 Mbps SSL-VPN throughput. Actual results depend on traffic, configuration and enabled services.
What information should I provide for a quote?
Provide the exact FG-80F-BP model, quantity, WAN bandwidth, users, sites, VLANs, VPN requirements, security services, subscription term, current firewall and desired installation or migration scope. For bypass planning, include the upstream and downstream devices on the intended inline path.
Decision recap and consultation
Choose the FG-80F-BP when the design calls for the FortiGate 80F security platform and the specific WAN1/internal1 fail-open bypass capability. Validate performance against inspected traffic rather than raw firewall throughput, document the behavior expected during bypass, and select subscriptions around the security services you will actually operate. FourTeck can help prepare a quotation and deployment discussion from your topology, bandwidth, VPN, licensing and integration requirements.




Reviews
There are no reviews yet.