
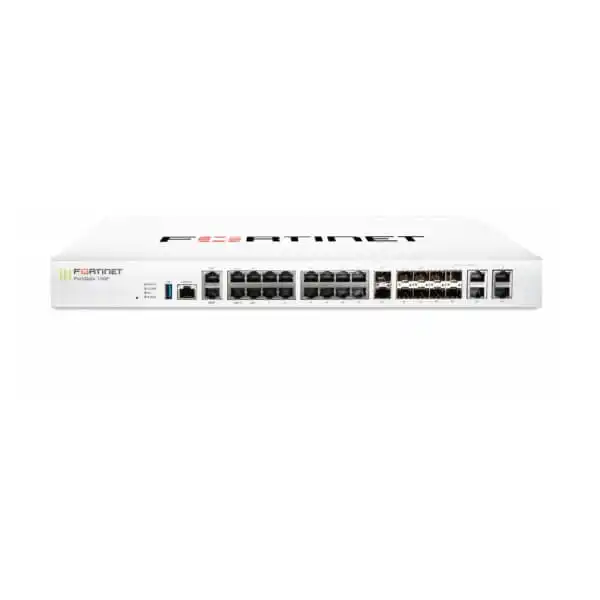
FortiGate 100F (FG-100F) Tanzania
FortiGate 100F (FG-100F) is a Fortinet next-generation firewall designed for organizations that need a strong combination of network security, secure SD-WAN, VPN connectivity, application visibility and flexible enterprise interfaces. For Tanzanian businesses evaluating an internet-edge firewall, branch hub, campus gateway or multi-site security platform, the important decision is not simply whether the appliance can route traffic. The project should consider inspected bandwidth, encrypted traffic, VPN demand, number of network segments, WAN links, logging strategy, FortiGuard services, availability design and expected growth. FourTeck Tanzania helps customers turn those requirements into a clearer procurement and deployment plan.
FortiGate 100F Overview and Verified Capabilities
Fortinet positions the 100F series for next-generation firewall and secure SD-WAN deployments. Published Fortinet specifications for the FG-100F include 20 Gbps firewall throughput, 2.6 Gbps IPS throughput, 1.6 Gbps NGFW throughput and 1 Gbps threat-protection throughput. The platform provides multiple GE RJ45, GE SFP and 10GE SFP+ connectivity options. These figures are laboratory performance references rather than promises for every production environment; real throughput depends on packet size, enabled security profiles, SSL inspection, traffic mix, firmware, policy design and other network conditions.
The FG-100F is particularly relevant when a business needs more than a simple perimeter router. FortiOS combines firewall policy, routing, SD-WAN, IPsec VPN, application control, intrusion prevention and other security functions within one operating environment. FortiGuard services can extend protection with continuously updated security intelligence, while FortiCare options address vendor support. Subscription selection should be matched to the services the organization actually intends to enable rather than treated as an afterthought.
A notable model distinction is storage: the base FG-100F does not include the local storage available on the FG-101F variant. Organizations with detailed logging and retention requirements should therefore plan an appropriate logging destination such as FortiAnalyzer or a supported cloud/logging approach. That difference matters during procurement because two models with similar names can support different operational requirements.
Secure SD-WAN
Use multiple WAN paths with policy-driven steering, performance monitoring and failover planning. This can help branches and head offices make better use of fiber, broadband or other available links while maintaining security controls.
VPN and Segmentation
Plan encrypted site-to-site connectivity, controlled remote access, VLAN separation and policy boundaries for departments, servers, guest networks and operational systems.
Security Inspection
Apply appropriate intrusion prevention, application control, web/DNS controls and malware-focused services according to the selected FortiGuard subscription and security policy.

How to Size the FG-100F
Firewall sizing should begin with the workload, not a user-count shortcut. Record current and planned internet bandwidth, peak concurrent traffic, encrypted traffic percentage, number of VPN tunnels, remote users, VLANs, public services, WAN links and the security profiles that will be enabled. A company using only stateful firewalling has a different performance profile from one enabling IPS, application control and deep inspection on most outbound traffic. Growth matters as well: internet circuits, cloud adoption and branch connectivity can increase faster than the number of employees.
Interface design is another reason buyers consider the 100F class. The combination of copper, SFP and 10GE connectivity can support WAN, LAN, DMZ, uplink and aggregation designs without forcing every connection through the same media type. Before purchase, confirm transceiver requirements, switch uplinks, ISP handoff, rack and power arrangements, high-availability objectives and whether the design needs local storage. A quotation should identify the exact appliance, subscription term, support level and any accessories so procurement can compare complete solutions rather than hardware-only prices.
FortiGate 100F Tanzania
Organizations searching for FortiGate 100F Tanzania commonly need a firewall for a head office, larger branch, campus, hotel, professional-services network, logistics operation, education environment, healthcare facility or multi-site business. The practical Tanzanian buying question is how the firewall will behave with the available internet links and the organization’s real security policies. A deployment may need two ISPs for resilience, segmented networks for staff and guests, protected server access, VPN links to branches, application visibility for cloud services and controlled administrative access. Those requirements should be documented before the appliance and subscription are finalized.
For Tanzania deployments, WAN diversity can be especially valuable where business continuity depends on internet access. The FG-100F can form part of a secure SD-WAN design that evaluates available links and applies routing decisions according to configured policies and performance criteria. This does not eliminate the need for sound ISP design; it gives the network team a platform for using multiple connections more deliberately. Organizations should document which applications are business critical, what should happen when the primary circuit degrades and whether VPN traffic must move automatically to another path.
Security policy should also reflect the business structure. Finance systems, guest Wi-Fi, IP cameras, servers, employee devices and management interfaces should not automatically share unrestricted access. VLANs and firewall policies can create clearer boundaries, while FortiGuard services can add security inspection where appropriate. Buyers should discuss logging retention, administrator authentication, firmware maintenance and configuration backup as part of the project. FourTeck Tanzania’s integrated IT and security solutions explain how firewalls fit with switching, Wi-Fi, servers and other infrastructure. For a formal requirement, use the verified FourTeck Tanzania contact page and provide bandwidth, users, sites, VPN needs and preferred license term.
FortiGate 100F Dar es Salaam
Dar es Salaam businesses evaluating the FortiGate 100F often operate busy internet edges where cloud applications, email, video meetings, remote access, ERP traffic and branch connectivity compete for bandwidth. The FG-100F can be considered for offices that need policy enforcement and security inspection without relying on a basic ISP router as the primary security boundary. A good design begins by mapping internet circuits, public IP requirements, internal subnets and business-critical applications. That map becomes the basis for firewall policies, NAT, SD-WAN rules, VPN design and monitoring.
Companies with warehouses, branches or remote facilities can use site-to-site IPsec VPN to connect locations securely, while remote-user access should be planned around identity, authentication and least privilege. Where multiple providers are available, SD-WAN can help the business use the links according to application and performance needs. The deployment should include test cases for ISP failure, DNS availability, VPN recovery and critical SaaS access rather than assuming failover works because two cables are connected.
Procurement teams in Dar es Salaam should request an exact bill of materials. Confirm whether the quote is appliance-only or includes FortiGuard and FortiCare services, the duration of those services, transceivers or accessories, configuration scope and any migration work. If replacing an older firewall, export and review the existing rule base instead of blindly recreating obsolete policies. FourTeck’s Tanzania network-security capability can be combined with switching and wireless planning where segmentation crosses the entire LAN. This approach is useful for offices that want staff, servers, voice, guest Wi-Fi and security devices separated cleanly while still allowing approved application flows.
FortiGate 100F Mwanza
For Mwanza organizations, FortiGate 100F selection can center on resilient connectivity, secure branch access and manageable security operations. A regional office may need protected access to systems hosted in Dar es Salaam, another country or a public cloud. A distribution business may need reliable ERP and inventory connectivity. An education or healthcare environment may need stronger segmentation between staff, guests, servers and specialist devices. These are architecture questions first and product questions second.
The FG-100F’s VPN and SD-WAN capabilities can support multi-site designs when configured around clear routing and security requirements. Before deployment, document each subnet, the applications that must cross site boundaries, expected tunnel bandwidth and what happens during link failure. Avoid broad any-to-any rules between sites simply because the traffic is encrypted; a VPN protects traffic in transit but does not replace access control. Logging should make it possible to investigate denied traffic, authentication events and security detections without depending solely on short-lived local memory.
Mwanza buyers should also consider operational ownership. Decide who will approve firewall changes, how configuration backups are stored, how firmware upgrades are tested and how subscription renewals are tracked. If the firewall protects revenue-critical services, document a rollback plan before major changes. A quote request should include the current internet speed, expected upgrades, number of branches, VPN users, public services and required security features. This gives the supplier enough context to confirm whether FG-100F is appropriately sized or whether another FortiGate model should be considered.
FortiGate 100F Arusha
Arusha businesses in tourism, hospitality, professional services, education and distributed operations may need a firewall that protects both internal business systems and internet-facing connectivity. Guest access is a good example of why segmentation matters. Visitor Wi-Fi should not automatically share the same trust zone as finance systems, management devices, IP cameras or administrative workstations. The FG-100F can enforce policies between these networks while also serving as an internet security gateway, provided the VLAN and switching design is coordinated with the firewall.
Hospitality and service environments can also be sensitive to internet outages. A secure SD-WAN design can use multiple WAN connections, but the business should define what traffic receives priority when capacity is reduced. Payment, booking, voice and operational applications may need different treatment from guest browsing or large software downloads. Testing should include real failover scenarios and application behavior, because not every session survives a change of public path in the same way.
For an Arusha quotation, specify whether the requirement includes hardware, FortiGuard subscriptions, FortiCare, installation, policy migration, VPN configuration or ongoing support. Also identify any fiber/SFP uplinks and whether high availability is required. FourTeck Tanzania’s broader infrastructure approach can help connect firewall planning with switches, wireless access points, servers and UPS requirements. The goal is a security edge that fits the complete site rather than an isolated appliance purchased only from a throughput figure.
FortiGate 100F Dodoma
In Dodoma, the FG-100F can be evaluated for offices and institutions that require controlled internet access, secure inter-site connectivity and stronger visibility into network traffic. Environments handling administrative systems, sensitive records or multiple departments should define network trust boundaries before writing firewall rules. Separate user groups, servers, guests and management systems where practical, then allow only the flows required for business operations. This makes policies easier to understand and reduces unnecessary lateral access.
Remote access deserves equal attention. Rather than treating VPN as a universal doorway into the LAN, define which users need remote connectivity, what applications they need and how authentication will be protected. Site-to-site tunnels should similarly use deliberate routing and policy controls. For organizations with more than one internet service, SD-WAN policies can be aligned with business priorities and measured link health. Monitoring should focus on application availability as well as whether an interface is technically up.
Dodoma procurement teams should compare complete lifecycle cost: appliance, subscriptions, support, deployment, logging, renewals and future capacity. The FG-100F base model has no local disk, so logging architecture should be discussed early when retention is important. FourTeck’s contact workflow recommends sharing users, bandwidth, VPN requirements and existing infrastructure, which helps turn a model request into a technically meaningful quote. Include the planned deployment date and any change window if the firewall is replacing a live gateway.
FortiGate 100F UAE
UAE buyers considering FortiGate 100F frequently compare appliance price, FortiGuard bundles, support terms and deployment services. For a regional company with Tanzania and Gulf operations, the firewall can be used within a consistent FortiOS-based architecture across branches, but each site should still be sized independently. Internet bandwidth, inspection level, VPN traffic and application usage differ between a headquarters, warehouse and small sales office. Standardizing policy concepts is useful; forcing every location onto the same appliance size is not.
FourTeck’s FortiGate 100F UAE page provides a regional procurement path for UAE requirements, while the Fortinet firewall portfolio in the UAE helps buyers compare model classes. For multi-country projects, establish who owns licensing, renewal dates, configuration standards and escalation. Centralized governance can reduce inconsistent rules while allowing local WAN and application requirements to remain site-specific.
A UAE-led quote for Africa deployment should clearly state destination, quantity, exact SKU, subscription term, accessories and responsibility for installation. Avoid assuming that a hardware quote automatically includes security subscriptions or configuration. If the device will terminate cross-border VPNs, document addressing, routing and encryption requirements before shipment so deployment teams can prepare a repeatable configuration and test plan.
FortiGate 100F Uganda
Ugandan organizations can consider the FG-100F for medium business edges, larger branches and multi-site networks where VPN, SD-WAN and security inspection are important. The purchasing process should start with an inventory of internet connections, users, devices, applications and branch relationships. This identifies whether the firewall is mainly protecting internet access, acting as a VPN hub, steering traffic across several links or performing all of these roles together.
For East African groups with operations in both Uganda and Tanzania, consistent FortiGate policy conventions can simplify support. Use clear object naming, documented VLANs, standardized administrative controls and change records. At the same time, tune WAN behavior for the actual connectivity at each site. A branch with one primary fiber and one wireless backup has different failover priorities from a site with two comparable circuits.
FourTeck’s Uganda technology site can support region-specific enquiries. When requesting an FG-100F quote, provide license duration, expected security services, VPN count and whether configuration or migration is needed. Logging and retention should be included in the design because the FG-100F itself does not provide local disk storage.
FortiGate 100F Kampala
Kampala offices often combine cloud applications, remote workers, branch links and growing wireless networks. In that environment, the FG-100F can provide a central point for policy, VPN and secure WAN control. Before configuration, identify which traffic categories matter most to the business. ERP, voice, video meetings, backups and guest traffic may require different routing or priority decisions. Secure SD-WAN policies should reflect those priorities rather than simply balancing every flow equally.
Security profiles also need deliberate scope. Enabling every inspection feature everywhere without considering traffic type can create operational issues, while minimal inspection can leave avoidable gaps. Define security zones and apply controls according to risk, compliance requirements and application behavior. Where SSL inspection is planned, evaluate certificate deployment, application compatibility and performance implications before broad rollout.
For Kampala procurement, ask for the exact FG-100F appliance and service bundle, renewal term, support level and implementation scope. If replacing another firewall, include current interface mappings, NAT, VPNs and policy counts in the migration assessment. Testing should cover internet access, published services, branch tunnels, DNS, critical SaaS applications and failover. This reduces the risk of discovering an undocumented dependency after cutover.
FortiGate 100F Arua
Arua deployments may place a stronger emphasis on resilient branch connectivity and remote administration. Where a site depends on links back to a headquarters or cloud environment, the firewall design should prioritize predictable VPN recovery, monitored WAN health and controlled management access. The FG-100F can participate in such a design, but successful operation depends on documented routing and tested failover.
Bandwidth constraints make traffic classification important. Business applications, voice and transactional systems can be identified separately from less critical downloads or guest traffic. SD-WAN rules can then steer or prioritize traffic according to configured objectives. Security inspection should be selected with the available bandwidth and risk profile in mind. Administrators should monitor both utilization and security events so performance problems are not mistaken for attacks, or vice versa.
For an Arua quote, include the WAN types, expected bandwidth, branch destinations, VPN requirements and number of internal segments. If remote engineers will manage the appliance, define secure administrative access and multi-factor authentication where supported by the chosen architecture. Include a logging destination and backup process so troubleshooting does not depend on being physically present at the site.
FortiGate 100F Mbarara
Mbarara businesses with distributed operations can use a next-generation firewall to make branch security more consistent while maintaining secure connectivity to central systems. The FG-100F may fit environments where several VLANs, WAN links and VPNs must be handled together. Begin by defining network zones for users, servers, guests, cameras or operational devices and documenting the traffic that should pass between them.
If the organization relies on cloud applications, consider how link quality affects user experience. SD-WAN health checks and routing policies can help select paths based on configured performance criteria. For private applications hosted elsewhere, IPsec tunnels can provide encrypted transport, but application availability still depends on DNS, routing and the remote service. Monitoring should therefore include the complete service path rather than only tunnel status.
Mbarara procurement should include renewal planning from day one. FortiGuard services are time-based subscriptions, and the value of features such as updated threat intelligence depends on maintaining the appropriate service. Record renewal ownership, serial information and support contacts in operational documentation. A well-prepared quote should separate hardware, subscriptions and implementation so stakeholders understand the full project cost.
FortiGate 100F Gulu
Gulu organizations considering the FG-100F should evaluate both security requirements and supportability. A firewall can enforce sophisticated policies, but an overly complicated rule base becomes difficult to maintain. Use clear zones, descriptive objects and least-privilege rules. Remove temporary access after its business purpose ends and schedule policy reviews so obsolete rules do not accumulate.
For branch connectivity, document primary and backup WAN behavior. Secure SD-WAN can help use multiple links, while VPN can protect traffic between sites. Test how critical applications respond during failover, especially sessions that may depend on a stable public IP. If a public service is hosted behind the firewall, inbound connectivity and DNS behavior require separate continuity planning.
A Gulu quote request should identify whether the firewall will be deployed as a new edge, replacement appliance or branch hub. Share expected throughput under security inspection, not only ISP headline speed. Include any need for SFP modules, 10GE uplinks, HA, remote access or centralized management. Clear requirements help determine whether FG-100F provides appropriate capacity and interfaces for the intended role.
FortiGate 100F Kenya
Kenyan buyers often compare FortiGate appliances by price and throughput, but business fit also depends on licensing, interfaces, VPN load and inspection. The FG-100F’s published 20 Gbps firewall throughput is only one figure; the more relevant planning metrics include the security functions that will actually be enabled. Use the official datasheet values as sizing references and allow headroom for growth rather than assuming a laboratory maximum equals production capacity.
For organizations connecting Kenya and Tanzania, site-to-site VPN can create encrypted links between offices, while SD-WAN can help manage multiple internet paths. Define routes and security policies separately so a tunnel does not become an unrestricted bridge between networks. Consider centralized logging and consistent naming to simplify cross-country operations. If local teams administer each site, document a common change process and minimum security baseline.
The FourTeck Kenya site provides a regional path for Kenyan technology requirements. Procurement should specify exact model, quantity, subscription bundle and term, destination and configuration scope. Buyers should verify current availability and price at quotation time rather than relying on indexed prices from unrelated resellers.
FortiGate 100F Kuwait
Kuwait deployments can use the FG-100F for secure office edges, branch hubs and segmented business networks where multiple applications and VPN connections must coexist. High internet speeds make it especially important to size for inspection rather than raw routing. Document the security services that will be enabled, expected encrypted traffic and the number of users and devices active during peak periods.
Organizations operating between Kuwait, UAE and Africa may benefit from consistent FortiOS policy structures and centralized operational standards. Standardization can simplify troubleshooting and audit review, while each site retains its own WAN and local network configuration. For cross-region VPN, coordinate addressing carefully to avoid overlapping subnets, a common problem when independently built offices are later connected.
Use FourTeck Kuwait for Kuwait-focused enquiries. A complete request should include the FG-100F model, required FortiGuard term, support expectations, interfaces, VPN scope and whether migration from an existing firewall is required. If the organization needs extensive logging, plan external or cloud logging because the base FG-100F has no local disk.
FortiGate 100F Ghana
Ghanaian businesses evaluating FortiGate 100F can focus on secure internet access, branch connectivity, policy segmentation and visibility. The appliance can serve as part of an architecture that separates user groups and systems while applying security inspection at the network edge. Start with an accurate network diagram and business application list; this reduces the temptation to create broad firewall rules simply to make connectivity work quickly.
For multi-ISP sites, secure SD-WAN can support path selection and resilience. Define health checks around services that matter to users and decide how traffic should behave when one link degrades. For VPN-connected branches, include route failover and tunnel monitoring in the test plan. Security and continuity should be designed together because a backup path that bypasses required controls creates a different kind of outage risk.
The FourTeck Ghana site can be used for Ghana-focused project discussions. Buyers should request a current quote with the exact license term and avoid assuming advertised hardware pricing includes FortiGuard subscriptions. Include expected installation, migration and support requirements so commercial comparisons cover equivalent scope.
FortiGate 100F Nigeria
Nigeria deployments can involve high user counts, several WAN links, distributed offices and significant cloud traffic. The FG-100F can be evaluated where a business needs next-generation firewall controls together with VPN and secure SD-WAN. The right model should be selected from measured or estimated peak traffic under the intended inspection profile, with additional capacity for growth and unexpected demand.
Power and connectivity resilience should be part of the wider network design. Firewall availability depends on switches, ISP equipment, power protection and upstream services as well as the appliance itself. Document dependencies and include UPS/rack planning where appropriate. For multiple WAN links, test failure and recovery behavior. For high availability, confirm the complete HA design and licensing implications rather than assuming a second unit automatically solves every single point of failure.
For Nigeria-focused enquiries, FourTeck Nigeria provides a regional entry point. Quote requests should state model, quantity, location, bandwidth, VPN needs, security services, term and implementation scope. This information helps distinguish a straightforward appliance purchase from a larger migration or multi-site security project.
FortiGate 100F Seychelles
Seychelles organizations may place particular value on reliable connectivity, secure remote administration and efficient use of available WAN links. Hotels, service businesses, distributed operations and professional offices can have a mix of staff systems, guest networks, cloud applications and remote support requirements. The FG-100F can provide a policy point between these zones and the internet when properly sized and configured.
Where multiple internet links are available, SD-WAN can help direct traffic according to configured priorities and measured link conditions. Guest traffic can be separated from operational systems, while VPN can protect approved inter-site or remote connectivity. Administrators should avoid exposing management interfaces directly to untrusted networks and should maintain configuration backups, controlled admin roles and a documented firmware process.
For procurement, clarify shipping destination, exact appliance SKU, FortiGuard subscription, support term and any optical accessories. If the firewall is replacing an existing device, schedule discovery before the migration window so NAT rules, VPNs, public services and application dependencies can be captured. The final acceptance test should verify business applications and failover behavior, not merely confirm that users can browse the web.
Related Tanzania Infrastructure for an FG-100F Deployment
A firewall works best when the surrounding network is designed coherently. FourTeck Tanzania’s main solutions page covers firewall, VPN and network security planning, while switching and LAN infrastructure is relevant when VLANs and uplinks must align with firewall zones. Wi-Fi and access-point planning matters when guest and corporate wireless networks require different policies. server and storage planning is useful when protected internal services, backup or logging infrastructure sit behind the firewall.
Other related requirements can include structured cabling, racks and UPS for physical deployment, CCTV network integration where camera VLANs need controlled access, and IP PBX and VoIP infrastructure when voice traffic needs segmentation and QoS-aware WAN planning. These links describe related Tanzania solution areas and help buyers plan the firewall as part of the complete network rather than as a standalone box.
FortiGuard Licensing and Renewal Guidance
The hardware and security subscription should be treated as separate but connected procurement decisions. Fortinet offers service bundles and individual services that can include capabilities such as intrusion prevention, malware protection, application control, web/DNS filtering and support depending on the selected package. Requirements vary, so buyers should not assume every FG-100F quote provides the same security services. Ask for the exact service SKU, start and end term, support level and renewal path.
Renewal planning should be assigned to an owner and tracked before expiration. Security services rely on current subscriptions for relevant updates and vendor services. For organizations operating several FortiGate appliances, align renewal dates where practical and maintain a device register containing serials, sites, owners and service terms. FourTeck’s Fortinet specialist regional site can also provide broader Fortinet-focused information for regional projects.
FG-100F Quotation Checklist
For a useful quotation, provide: deployment country and city; quantity; current and planned internet bandwidth; approximate users and devices; number of WAN links; VLANs or security zones; site-to-site VPN count; remote-access requirement; public services; expected FortiGuard services; preferred one-year or multi-year term; SFP/10GE requirements; HA requirement; logging and retention needs; current firewall model; migration scope; target deployment date; and whether configuration, testing or ongoing support is required. This information helps the sales and technical teams compare the requested FG-100F against the actual workload.
FortiGate 100F FAQ
What is the FortiGate 100F firewall throughput?
Fortinet publishes firewall throughput up to 20 Gbps for the 100F series under its test conditions. Production performance depends on traffic and enabled security functions, so sizing should also review IPS, NGFW, threat-protection and SSL-inspection requirements.
Does FG-100F support secure SD-WAN?
Yes. Secure SD-WAN is a core FortiGate use case and can be used to apply policy-based traffic steering across multiple WAN links when designed and configured appropriately.
Does FG-100F have local storage?
The base FG-100F does not have local disk storage. The FG-101F is the related variant with local storage. Plan FortiAnalyzer, cloud or another supported logging approach when retention is required.
Can the FG-100F connect branches with VPN?
Yes. FortiGate supports IPsec VPN use cases for site-to-site connectivity. The design should define routes, encryption, authentication, failover and access policies for each connected network.
What information is needed for a Tanzania quote?
Share quantity, site, bandwidth, users, WAN links, VPN needs, security services, license term, interfaces, current firewall and whether installation or migration is required.
Decision Recap
FortiGate 100F is a capable next-generation firewall platform for organizations that need stronger security inspection, VPN, SD-WAN and interface flexibility than a basic branch gateway. The best purchasing decision comes from matching the appliance to inspected traffic, WAN design, segmentation, VPN, logging and subscription requirements. Confirm current Fortinet lifecycle information, service bundles and commercial availability at quotation time. FourTeck Tanzania can use your network details to prepare a more complete discussion around appliance, licensing and deployment scope.
For a consultation, send the current firewall model, internet speeds, user/device estimate, branch count, VPN requirements, preferred license term and target deployment location through the Tanzania contact page.




Reviews
There are no reviews yet.