
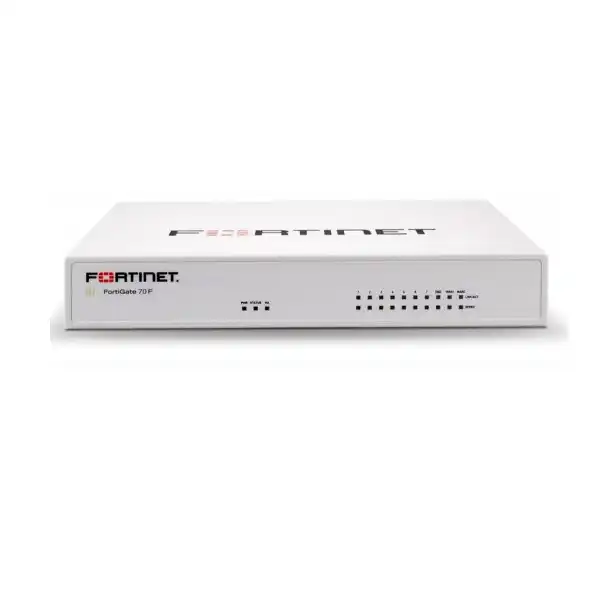
FortiGate 70F (FG-70F) Tanzania
FortiGate 70F is a compact next-generation firewall for organizations that want to converge branch security, routing, SD-WAN and controlled access on one FortiOS platform. Fortinet positions the 70F series for distributed enterprise sites and WAN transformation, with purpose-built security processing and integration into the wider Fortinet Security Fabric. For buyers in Tanzania, the practical question is not simply whether the appliance fits on a desk: it is whether the firewall, security subscription, internet links, VPN design and policy model match the real traffic profile of the site.
Fortinet-published IPS throughput for the 70F series.
Published NGFW throughput, useful as one input to sizing.
Published threat-protection throughput for the series.
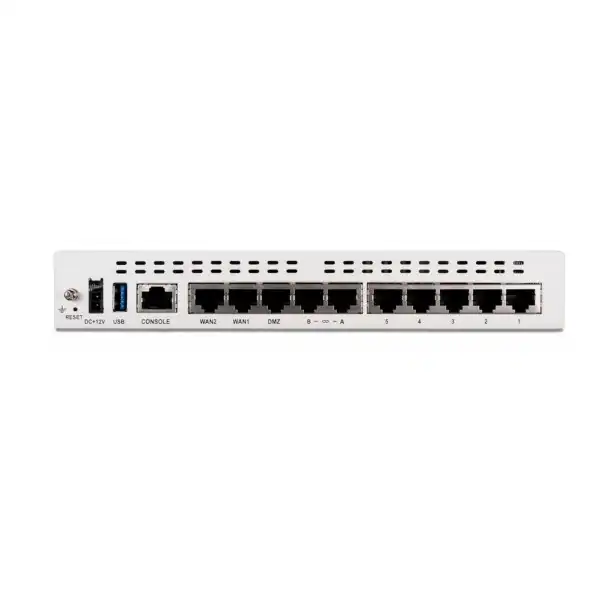
Two WAN, one DMZ, two FortiLink and five internal ports.
FortiGate 70F overview
The FortiGate 70F series brings networking and security functions together in a compact appliance. Fortinet’s current data sheet describes firewalling, SD-WAN, network-controller functions and security on the FortiOS operating system. The hardware uses Fortinet’s purpose-built architecture to accelerate security and networking tasks rather than relying only on a general-purpose CPU. That matters at branch sites because a firewall often has to inspect traffic, enforce application policy, build encrypted tunnels, steer traffic across WAN links and maintain user connectivity at the same time.
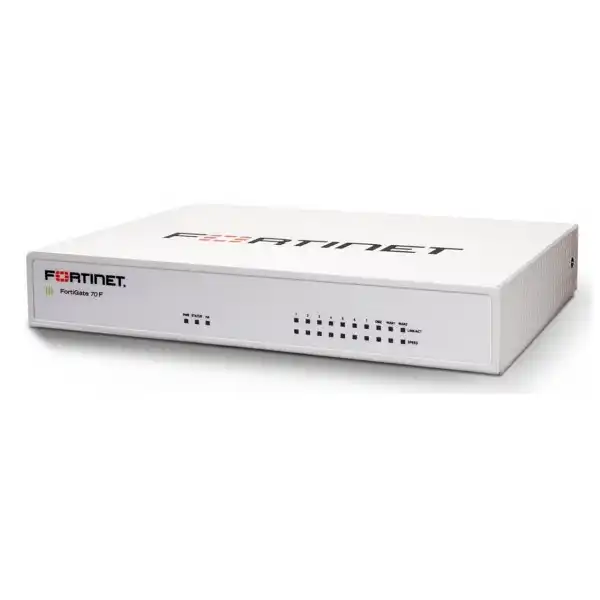
The FG-70F provides two Gigabit Ethernet WAN ports, a Gigabit Ethernet DMZ port, two Gigabit Ethernet FortiLink ports and five Gigabit Ethernet internal ports, together with USB and console connectivity. The two FortiLink interfaces can support Fortinet’s approach to integrated access-layer management and can be reconfigured as regular ports when required. The appliance is therefore useful where a business wants a compact security gateway with enough physical Ethernet connectivity for common branch segmentation patterns without adding unnecessary complexity.
Performance figures should be treated as engineering inputs, not promises about every live network. Fortinet publishes 1.4 Gbps IPS throughput, 1 Gbps NGFW throughput and 800 Mbps threat-protection throughput for the 70F series. Real results depend on policy design, enabled inspection, packet sizes, TLS inspection, logging, VPN use and traffic mix. FourTeck recommends sizing against the security profile that will actually be enabled, not against raw firewall throughput alone.
What the FortiGate 70F can solve
Secure branch internet access
Apply firewall, application and security controls at the branch edge while maintaining visibility into users, devices and traffic. This is especially useful when business applications, cloud services, voice, remote support and ordinary browsing share the same internet connection.
Multi-WAN and SD-WAN
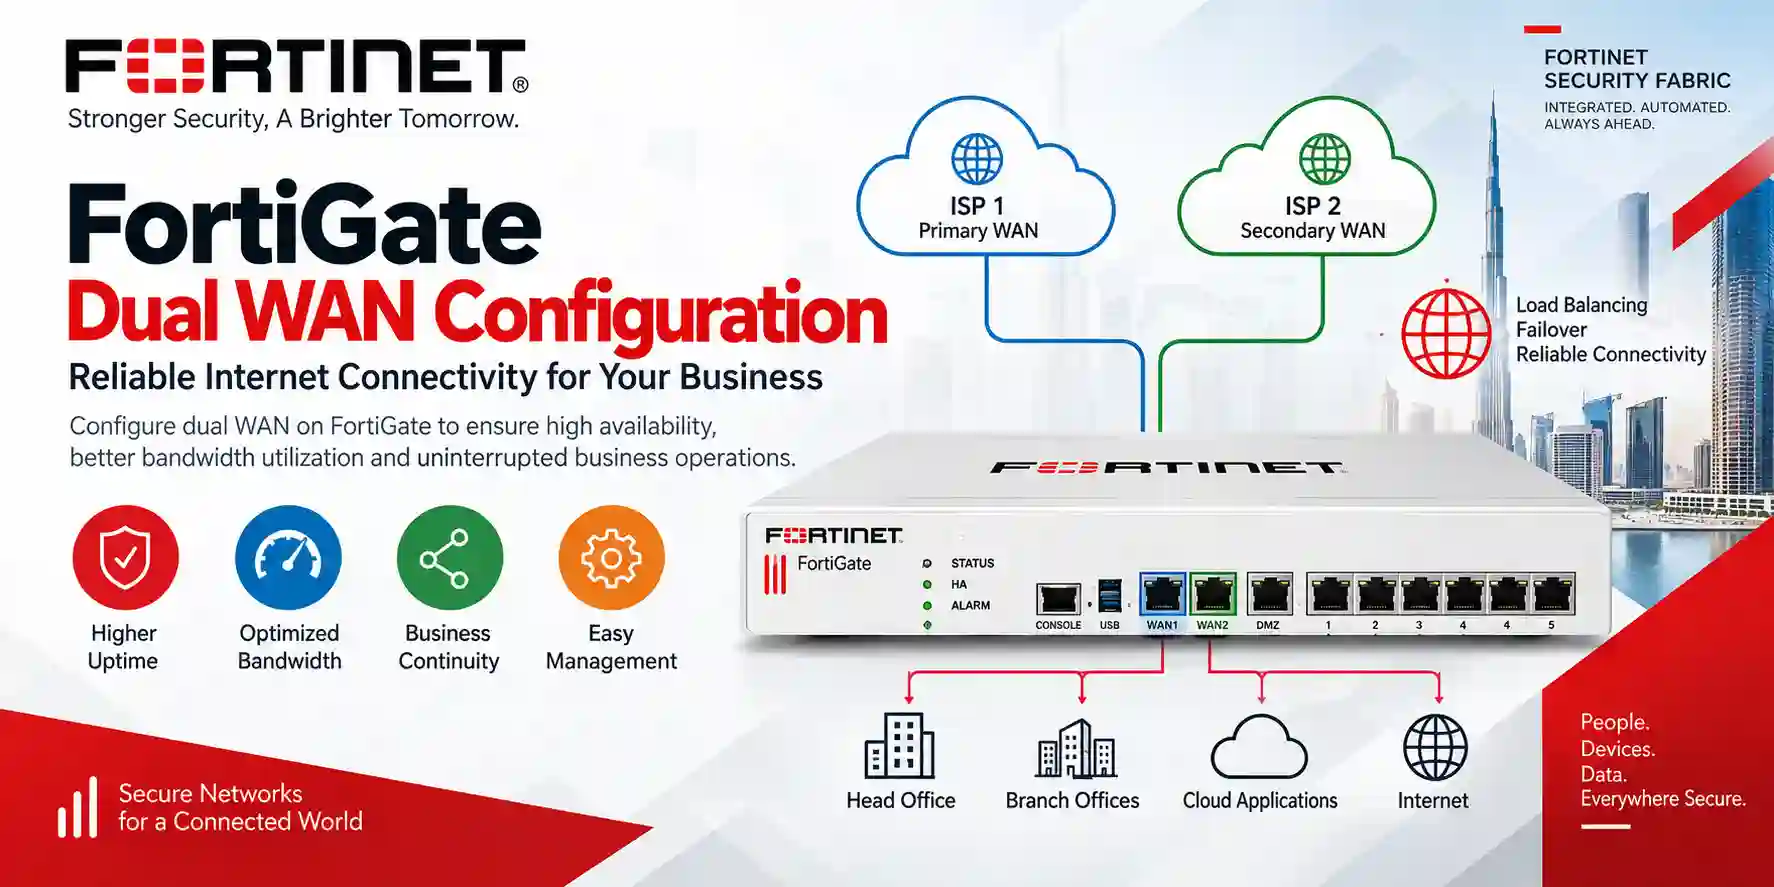
Use secure SD-WAN capabilities to steer applications across available links according to policy and measured link conditions. A dual-provider design can reduce dependence on one circuit, although resilience still depends on upstream providers, power, cabling and configuration.
Site-to-site and remote connectivity
Build controlled encrypted connectivity between offices or for authorized remote users. VPN design should account for authentication, routing, address plans, application dependencies, logging and the security posture of endpoints rather than treating the tunnel as an isolated feature.
FG-70F technical planning snapshot
| Platform | FortiOS with purpose-built Fortinet security processing |
| IPS throughput | 1.4 Gbps, vendor-published series figure |
| NGFW throughput | 1 Gbps, vendor-published series figure |
| Threat protection | 800 Mbps, vendor-published series figure |
| WAN | 2 × GE RJ45 WAN |
| LAN / access | 5 × GE RJ45 internal + 2 × GE RJ45 FortiLink |
| DMZ | 1 × GE RJ45 DMZ |
| Management connectivity | Console and USB interfaces |
FortiGuard subscriptions and buying guidance
Buying an FG-70F is not only a hardware decision. Fortinet offers security-service bundles with different coverage, and the appropriate subscription should follow the threat controls the organization intends to use. Fortinet currently describes ATP as a foundational package including capabilities such as IPS, antivirus, application control and related services; UTP adds broader web and network protection; and Enterprise Protection expands coverage further. Bundle names and inclusions can change over time, so the quotation should identify the exact Fortinet part number, term and service scope rather than relying on an informal label.
Procurement teams should also separate initial purchase from renewal planning. Security services have operational value only when they fit the security policy and remain appropriately licensed. Record the appliance serial information, contract term, renewal owner, support entitlement and renewal date in the asset register. For organizations with multiple branches, align renewal dates where practical to simplify administration, while confirming the commercial implications with the supplier.
For broader Fortinet sourcing and regional security planning, see FourTeck Fortinet UAE. Organizations comparing firewall architecture and specialist deployment topics can also review FourTeck firewall solutions. These resources complement the Tanzania-focused consultation rather than replacing model-specific sizing.
Dual-WAN, VPN and integration considerations
The two WAN interfaces make the FG-70F a natural candidate for sites that need two internet connections, but a resilient design requires more than connecting two cables. The project should define whether the second circuit is active/active or primarily a failover path, which applications receive priority, how health checks are performed, how inbound services behave after failover and whether each provider uses static addressing, NAT or another handoff model. DNS, cloud allowlists and third-party VPN peers may also need to account for both public addresses.
VPN planning starts with business flows. A site-to-site tunnel may need access only to ERP, file services or management networks, while remote users may require a different authentication and authorization policy. Avoid broad any-to-any rules merely because encryption is present. Segment access, log important events and document routes so troubleshooting remains manageable. Where identity systems, FortiSwitch, FortiAP or centralized Fortinet management are part of the environment, define integration boundaries before implementation.
FortiGate 70F Tanzania
For Tanzania organizations, FortiGate 70F procurement commonly begins with a branch-security or internet-edge requirement: protect a growing office, connect a branch to headquarters, introduce a second ISP, improve application control, or replace a basic router with a security platform. The FG-70F can address these scenarios when its capacity and interfaces fit the design. A good Tanzania quotation should therefore state more than the appliance name. It should identify the hardware, proposed FortiGuard service term, support coverage, deployment assumptions and any integration work required.
Connectivity conditions can differ widely between sites. A business may use fibre at one location, a wireless provider at another and a backup service from a separate carrier. The firewall policy should be built around those realities. For dual-WAN, confirm handoff type, public addressing, expected bandwidth and whether critical cloud services need deterministic egress. For VPN, document remote networks and overlapping address ranges before deployment. For voice and collaboration traffic, consider latency and jitter alongside bandwidth so SD-WAN decisions reflect application quality rather than simple link availability.
Tanzania buyers should size security inspection against expected growth. If an internet circuit is likely to be upgraded during the firewall’s service life, include that future bandwidth in the assessment. Likewise, estimate the number of users, simultaneous VPN sessions, VLANs, cloud applications and inspection policies. Published throughput values are laboratory references and should not be confused with guaranteed application performance in every topology. TLS inspection, logging and complex policy can change the practical load.
FourTeck’s role in a purchasing discussion can include clarifying the required Fortinet bill of materials and helping the customer frame deployment questions. Buyers who need wider regional IT sourcing can also explore FourTeck Africa technology solutions. For the FG-70F itself, request a quote with your current ISP speeds, expected user count, number of locations and required subscription term so the response can be aligned to the project rather than a generic hardware-only request.
FortiGate 70F Dar es Salaam
Dar es Salaam businesses often operate with a high concentration of internet-dependent services: cloud productivity suites, ERP access, online banking, customer portals, IP telephony, video meetings and remote support. For an office, retail operation, professional-services firm or distributed business, the FortiGate 70F can provide a single policy point for internet access, secure WAN connectivity and branch security when the site requirements fit the platform. The most useful first step is to map critical applications and traffic flows rather than simply counting employees.
A Dar es Salaam deployment may benefit from two independent internet services. The FG-70F’s dual WAN interfaces can support an SD-WAN design that monitors link quality and applies traffic-steering rules. The project should confirm whether the providers share upstream infrastructure, because two contracts do not automatically create true path diversity. Power protection also matters: firewall availability depends on the modem or ONT, switches, wireless infrastructure and any local servers remaining powered. UPS capacity should therefore be planned for the complete network edge, not the firewall alone.
Segmentation is another important design choice. Corporate users, guest Wi-Fi, IP phones, CCTV, servers and building devices should not automatically share one unrestricted network. The FG-70F provides multiple Ethernet interfaces and can enforce policy between logical networks, while managed switching can extend segmentation across the access layer. Define VLANs, DHCP responsibility, DNS paths and allowed inter-zone services before cutover. This reduces emergency rule changes after deployment.
When requesting a FortiGate 70F quote for Dar es Salaam, provide the primary and backup internet speeds, approximate users and devices, remote-access needs, site-to-site VPN requirements, public services, preferred security subscription term and whether existing Fortinet equipment will be retained. This information helps turn a product enquiry into a practical security design discussion without making assumptions about stock, delivery or site support that have not been confirmed.
FortiGate 70F Mwanza
For organizations in Mwanza, a compact branch firewall can be particularly useful when the site needs secure access to centralized applications while maintaining reliable local internet connectivity. The FortiGate 70F can serve as the security and WAN edge for a suitable branch, with firewall policies, SD-WAN and encrypted connectivity managed through FortiOS. Businesses should start by classifying which systems must remain reachable during an ISP issue and which traffic can tolerate a temporary interruption.
If the Mwanza office connects to a headquarters or data centre, document the routed networks at both ends before configuring site-to-site VPN. Duplicate private IP ranges are a common source of complexity in multi-site projects. A clean addressing plan, explicit route ownership and limited firewall rules make ongoing operations easier. Where local services such as printers, cameras or line-of-business systems need inter-VLAN communication, define those flows rather than opening broad network access.
Bandwidth sizing should include security inspection and future demand. A site may begin with modest connectivity and later add cloud backup, more video conferencing or centralized applications. The Fortinet-published threat-protection figure for the 70F series is 800 Mbps, but actual performance depends on the enabled feature set and traffic conditions. Treat that number as one reference point in a broader sizing exercise. Consider encrypted traffic inspection, VPN use, log volume and peak concurrent activity.
Procurement should also establish who will own configuration backups, firmware planning, security-service renewals and incident changes. A firewall is an operational system, not a one-time installation. Include the FortiGuard subscription term and support entitlement in the purchase review, and document administrative access carefully. For a Mwanza quotation, share the site topology and intended security controls so the proposed bill of materials can reflect the actual deployment.
FortiGate 70F Arusha
Arusha organizations ranging from offices and hospitality-related businesses to NGOs and multi-site enterprises may need a secure edge that can support cloud applications, partner access, guest connectivity and private links to other locations. The FortiGate 70F offers a compact FortiOS platform for these functions when properly sized. The key is to separate business requirements into security zones and service levels instead of treating every connected device as equivalent.
Guest networks deserve particular attention in environments where visitors or temporary users require internet access. Guest traffic should be separated from internal business systems, and access policies should reflect the organization’s security requirements. Similar separation can be applied to cameras, building systems and voice devices. The FG-70F’s Ethernet connectivity can participate in this design, while managed switches and wireless access points carry the segmentation across the site.
For organizations using multiple internet links, secure SD-WAN can help apply application-aware path selection. Before configuration, identify the applications that are sensitive to delay and packet loss, such as voice and interactive meetings, and distinguish them from bulk downloads or software updates. Define what happens when a link degrades rather than only when it goes completely offline. This creates a more useful resilience policy than a simple primary/secondary arrangement.
An Arusha procurement request should specify whether the requirement is hardware only or includes FortiGuard services, configuration, VPN integration and ongoing support. If the firewall will connect to a remote FortiGate, include the remote model and FortiOS context in the planning information. If third-party VPN peers are involved, note their platform and encryption requirements. These details reduce uncertainty and help establish whether the 70F is appropriately sized for the intended workload.
FortiGate 70F Dodoma
Dodoma deployments may involve administrative offices, professional organizations, education environments or branch operations that depend on secure access to centralized services. The FortiGate 70F can consolidate firewalling, WAN control and encrypted connectivity at a suitable site. For procurement teams, the main decision should be based on traffic, inspection and topology requirements rather than simply choosing a model by employee count.
Start with an application inventory. Identify cloud services, internal servers, SaaS platforms, remote desktops, voice systems and externally published applications. Then map which users and networks should reach each service. This information becomes the foundation for firewall rules and helps avoid a permissive configuration that is difficult to audit later. Where departments or device classes need separation, plan VLANs and access policies before installation.
For WAN resilience, consider the entire dependency chain. A backup internet circuit is useful only if its access equipment, power source and physical route provide meaningful independence. The FortiGate can make forwarding decisions between links, but it cannot eliminate common upstream failures. Document public IP behavior, DNS dependencies and VPN peer settings for both paths. If services are hosted behind the firewall, inbound failover needs special attention.
The FortiGuard subscription should be selected according to the controls the organization intends to operate. Do not compare quotations solely on hardware price when service bundles or terms differ. Ask for clear part numbers, subscription duration and support scope. For Dodoma projects, provide expected internet capacity, user/device estimates, number of VLANs, VPN requirements and any compliance-driven logging needs when requesting a quotation.
FortiGate 70F UAE
UAE buyers evaluating the FortiGate 70F often compare it with other FortiGate entry-level models for branch offices, retail sites and distributed enterprise locations. The 70F sits in Fortinet’s entry-level branch range and provides 800 Mbps published threat protection. The correct selection depends on the enabled security stack, internet speed, VPN load and growth plan. If the site is approaching the practical limits of the platform under full inspection, a larger model may be more appropriate even when the basic port count appears sufficient.
A UAE deployment frequently needs integration with centralized services, cloud workloads or multiple branches. Document routing, identity, DNS, authentication and logging requirements early. If secure SD-WAN is part of the design, measure business applications against latency, jitter and loss thresholds rather than using bandwidth alone. If IPsec tunnels connect to cloud gateways or third-party firewalls, confirm supported parameters and route design on both sides before migration.
Subscription comparison is also important. Fortinet offers multiple FortiGuard service bundles, and two quotes for the same FG-70F hardware can differ significantly because the security term and included services are not identical. Compare exact SKUs and service duration. Buyers can review FourTeck UAE technology solutions and the specialist Fortinet UAE resource when coordinating a UAE requirement.
For organizations operating between UAE and East Africa, standardizing policy conventions, object naming, VPN templates and renewal tracking can simplify administration. Standardization does not mean every branch requires the same appliance; model selection should still reflect local bandwidth and security demand. A clear multi-site design can, however, reduce troubleshooting time and make future branch onboarding more predictable.
FortiGate 70F Uganda
Uganda organizations considering the FG-70F can use it as a compact secure-networking platform for suitable branch and office deployments. Typical requirements include protected internet access, site-to-site connectivity, remote access, segmentation and WAN resilience. The design should begin with the security policy and application flows, because a firewall that is purchased only by headline throughput can be undersized or unnecessarily complex once real inspection policies are enabled.
Where two ISP links are available, the dual WAN interfaces can support a secure SD-WAN strategy. Define which business services should prefer each link, what performance threshold triggers a path change and how sessions behave during failover. Confirm whether public IP addresses are required for inbound applications or third-party VPNs. If mobile or wireless backup is part of the plan, account for its bandwidth, addressing and data-policy characteristics separately from the primary circuit.
Branch segmentation can reduce the impact of compromised or unmanaged devices. Separate corporate endpoints from guests, cameras and other device classes where appropriate, and allow only the required inter-zone traffic. FortiLink can support integration with compatible FortiSwitch environments, but the switching architecture should be reviewed as part of the overall design rather than assumed from the firewall purchase alone.
For Uganda sourcing and regional coordination, customers can review FourTeck Uganda solutions. When requesting the 70F, provide the required FortiGuard term, expected internet speed, number of branches and VPN peers, and whether configuration assistance is required. This makes it easier to compare a complete solution rather than hardware-only pricing.
FortiGate 70F Kampala
Kampala offices often combine cloud applications, local servers, Wi-Fi, voice and remote access on the same network edge. The FortiGate 70F can consolidate security policy and WAN control for an appropriately sized site. Before deployment, classify critical traffic and establish segmentation. Finance systems, management interfaces and server networks should not automatically share the same trust level as guest or unmanaged devices.
A dual-ISP Kampala site can use SD-WAN to improve resilience and application experience, but the configuration should reflect measured link quality. Define health checks against destinations that represent real service reachability. A link can remain electrically up while upstream routing or application reachability is impaired. Path selection based on meaningful performance metrics can provide better outcomes than checking interface status alone.
For VPN connectivity, document the peer addresses, remote networks, authentication approach and routing expectations. If a branch connects to headquarters, determine whether internet traffic exits locally or is backhauled. Each approach has implications for bandwidth, inspection and policy. Remote users should receive only the access needed for their role, with authentication and endpoint controls considered as part of the broader security design.
Kampala buyers should request a quotation that clearly identifies FG-70F hardware, subscription term and service bundle. Include expected growth, especially if higher-speed connectivity is planned. The 70F’s published security figures provide a useful reference, but sizing should be based on the actual feature mix and peak workload expected during the service life of the appliance.
FortiGate 70F Arua
For an Arua branch that depends on connectivity to central systems, the firewall project should prioritize service continuity and straightforward operations. The FortiGate 70F can combine secure internet access, VPN and WAN control on one platform when the site fits its performance envelope. A branch design should identify what employees can continue doing if the primary WAN fails and which applications require immediate failover.
Where connectivity choices are limited or variable, application prioritization becomes important. Business-critical interactive traffic may need different treatment from backups, operating-system updates or large downloads. Secure SD-WAN policies can use link conditions to guide path selection, but the thresholds should be tested against real circuits. Avoid overly sensitive rules that cause unnecessary path changes during normal fluctuations.
Physical and operational resilience also deserves attention. Use appropriate power protection for the firewall, provider equipment and access switches. Keep configuration backups, document administrator access and establish a change process. If the branch has no dedicated IT staff, remote manageability and clear escalation procedures are particularly valuable. Security subscriptions and support entitlements should be tracked before renewal deadlines.
For an Arua FG-70F request, include the current ISP handoff, bandwidth, number of local networks, VPN destination and security-service expectations. If the site is part of a larger Uganda deployment, provide information about the central firewall and management approach. This helps maintain consistent policy without assuming every branch has identical traffic or capacity needs.
FortiGate 70F Mbarara
Mbarara businesses looking for a Fortinet firewall may be replacing a basic router, adding security inspection or connecting a branch to other locations. The FortiGate 70F is designed for branch use and combines FortiOS security with SD-WAN capabilities. The purchase should be tied to a network plan that identifies internet bandwidth, application mix, remote users, VLANs and any services exposed to the internet.
If the existing network is flat, the firewall migration is an opportunity to improve segmentation. Corporate devices, guest Wi-Fi, cameras and servers can be placed into separate networks with explicit policy between them. This can reduce unnecessary lateral access and make logs more meaningful. The switching and wireless infrastructure must support the planned VLAN architecture, so check those components before setting the cutover date.
For two-WAN designs, test both normal operation and failure scenarios. Verify DNS resolution, VPN reconnection, cloud allowlists and any inbound services after a path change. Document which circuit is preferred for each application class and how quickly the system should react to degraded quality. Resilience is a design property of the complete edge, not merely a checkbox on the firewall.
When comparing Mbarara quotations, verify that the same FortiGuard bundle and term are being compared. A lower hardware figure may not include the security services expected by the organization. Ask for exact part numbers and renewal information, then align the purchase with an operational owner who will maintain firmware, policies, backups and subscription records.
FortiGate 70F Gulu
A Gulu branch may need a secure connection to headquarters, controlled local internet access and a backup path for essential services. The FortiGate 70F can support these requirements in a compact platform when properly sized. Begin by defining the branch’s critical services and deciding whether they are accessed locally through the internet, through a private VPN path or through both depending on availability.
Site-to-site VPN design should use a clear IP addressing scheme and least-privilege policies. If the Gulu network overlaps with another branch, resolve that issue during planning rather than after tunnels are built. Decide how routes are advertised or configured, where DNS queries are resolved and which traffic should remain local. These choices affect both security and user experience.
The firewall can also support separation between user groups and device types. For example, guest wireless traffic does not need access to internal management networks, while cameras may require communication only with specific recording or management systems. Explicit policy improves control and can simplify incident investigation. Use meaningful object names and policy descriptions so future administrators understand the intent.
For Gulu procurement, share the expected bandwidth, number of users and devices, VPN requirements and preferred security term. If remote administration will be important, define how management access is protected and logged. Plan subscription renewals and configuration backups from the beginning so the branch does not depend on undocumented knowledge after deployment.
FortiGate 70F Kenya
Kenya organizations can evaluate the FortiGate 70F for branch and office security where the platform’s performance and Gigabit Ethernet interfaces fit the intended workload. Public commercial search patterns around the model commonly include appliance pricing, UTP or Enterprise Protection licensing, renewal cost, VPN, SD-WAN and branch-firewall suitability. These are useful buying questions because the complete cost and capability depend on the hardware plus the chosen security services and deployment scope.
For a Nairobi or regional branch, compare expected inspected traffic rather than only ISP headline speed. Cloud backup, video meetings, SaaS traffic and encrypted web use can create very different loads at different times of day. If a faster circuit or more users are planned, include that growth in sizing. The 70F has a vendor-published 800 Mbps threat-protection figure, but production performance depends on enabled functions and traffic conditions.
Multi-site Kenya deployments benefit from consistent naming, segmentation and VPN standards. A template can define common networks and policy principles while allowing each branch to use the model that matches its load. Centralized management may be considered where the operational scale justifies it. Avoid forcing one hardware model across every site solely for uniformity.
For regional technology sourcing, visit FourTeck Kenya. When requesting the FG-70F, specify whether the quote should include FortiGuard services and for what duration. Also provide VPN, WAN and implementation requirements so competing proposals can be compared on equivalent scope.
FortiGate 70F Kuwait
Kuwait buyers considering the FG-70F should match the appliance to branch bandwidth, inspection needs and service-term requirements. The compact form factor is useful for smaller sites, but model selection should be driven by the workload under the intended security profile. If a branch has high-speed internet and extensive TLS inspection, a larger FortiGate may offer more headroom even when the 70F has enough physical ports.
For offices using two internet providers, document whether each circuit has static public addressing, how VPN peers will reach the branch and what happens to inbound services during failover. Secure SD-WAN can steer outbound traffic, but external dependencies must be designed as well. Test failover with real business applications before considering the project complete.
Subscription scope should be explicit in the purchase order. Compare exact Fortinet part numbers, bundle names and durations, and record renewal ownership. If the organization has several FortiGate sites, align operational practices such as backups, administrator roles and change control. Consistent management is often as important as initial configuration quality.
A Kuwait quotation request should include current and planned WAN capacity, VPN peers, user/device estimates, security-service expectations and any integration with FortiSwitch, FortiAP or centralized Fortinet management. This gives the supplier enough context to identify whether the 70F is appropriate and what additional components or services may be required.
FortiGate 70F Ghana
Ghana businesses can consider the FortiGate 70F for branch-edge security, protected internet access and secure connectivity between sites. The device’s combination of FortiOS, SD-WAN and FortiGuard integration is most valuable when deployed as part of a defined security architecture. Start with the applications and networks that need protection, then determine inspection, VPN and logging requirements.
For sites with variable WAN quality, measure more than link uptime. Latency, packet loss and jitter can affect voice, meetings and interactive cloud applications before a circuit fails completely. SD-WAN policies can account for these conditions when health checks and thresholds are configured appropriately. Backup connectivity should also be tested under realistic load so expectations are understood.
Segmentation helps limit unnecessary trust. Place guest access and device networks into suitable zones, and allow only required traffic toward business systems. If the branch uses local servers, determine whether they belong in a dedicated server or DMZ segment. If services are published externally, review inbound NAT and security policy carefully and avoid exposing management interfaces to the public internet.
Ghana procurement should compare equivalent subscription terms and support scope. Include future bandwidth growth and the expected service life in sizing discussions. For organizations with several African locations, a consistent policy framework can simplify operations, but each site still needs its own capacity assessment and connectivity plan.
FortiGate 70F Nigeria
Nigeria organizations with branch offices, retail locations or professional-service sites may evaluate the FortiGate 70F as a secure edge platform. The model can combine firewalling, SD-WAN, VPN and FortiGuard-enabled security controls for suitable workloads. Because business connectivity can be mission critical, the network design should include both security and resilience requirements from the outset.
Where multiple WAN technologies are available, decide which link should carry each application class and what conditions trigger a switch. Consider the addressing behavior of each provider, especially if VPNs, cloud allowlists or published services depend on known public IP addresses. The firewall can automate path selection, but upstream carrier design and power availability remain external dependencies.
Security inspection should be sized for peak traffic and future demand. The 70F series publishes 800 Mbps threat protection, 1 Gbps NGFW and 1.4 Gbps IPS performance, but these are vendor test references. Real networks use different packet sizes, encryption levels and policies. If the organization expects rapid bandwidth growth or heavy encrypted inspection, include that headroom in the model comparison.
A Nigeria quotation should clearly distinguish hardware from FortiGuard service terms and implementation scope. If several branches are involved, provide the topology and central firewall details so VPN and policy standardization can be considered. Maintain configuration backups and subscription records as part of normal operations rather than waiting for a fault or renewal deadline.
FortiGate 70F Seychelles
Seychelles businesses that rely heavily on internet connectivity for reservations, cloud applications, communications or remote administration may need a compact security gateway with strong WAN-control capabilities. The FortiGate 70F can be considered for suitable offices and branches, with secure SD-WAN, firewall policy and VPN integrated through FortiOS. Capacity planning should reflect the actual internet service and inspection profile at the site.
Resilience planning is particularly important where alternative connectivity may have different performance or cost characteristics. Define which applications must remain available during primary-link failure and whether lower-priority traffic should be restricted on a backup service. Test DNS, authentication, VPN and cloud applications during failover. A backup path that works for basic browsing may not automatically support every business workflow.
Remote management should be designed securely. Restrict administrative access, use strong authentication practices and maintain configuration backups. If external support teams need access, create a controlled process rather than leaving broad management exposure. Logging and time synchronization also help when investigating connectivity or security incidents across geographically separated teams.
When requesting an FG-70F quotation for Seychelles, state the internet speeds, user/device count, number of network segments, VPN requirements and preferred FortiGuard subscription term. If the branch is part of a larger regional organization, include information about central security platforms and addressing. This allows the product discussion to focus on compatibility and operational fit instead of treating the firewall as a standalone box.
Related secure-networking resources
FortiGate works best when the firewall is considered together with WAN, switching, wireless, remote access and operational support. For cross-border projects, FourTeck Africa provides a broader regional technology context; FourTeck Kenya and FourTeck Uganda support country-specific exploration; and Fortinet UAE by FourTeck is relevant for Fortinet-focused requirements in the UAE. Tanzania buyers should use the local contact page for the current FG-70F quotation and scope discussion.
FortiGate 70F quotation checklist
Current and planned primary/backup bandwidth, handoff type and public addressing.
Required FortiGuard bundle, subscription duration, inspection and logging expectations.
Peak concurrent users, endpoints, guest devices, cameras, phones and servers.
Site-to-site peers, remote users, remote subnets and third-party gateway requirements.
VLANs, DMZ, guest access, server networks and inter-zone access requirements.
Migration window, existing firewall, switch/wireless integration and support expectations.
FortiGate 70F FAQs
What is the FortiGate 70F designed for?
Fortinet positions the 70F series for secure networking at distributed enterprise sites and branch environments. It converges next-generation firewall functions, SD-WAN and network-control capabilities through FortiOS. Suitability for a specific site still depends on traffic, inspection, interfaces and growth requirements.
What is the FortiGate 70F threat-protection throughput?
Fortinet currently publishes 800 Mbps threat-protection throughput for the 70F series, together with 1 Gbps NGFW and 1.4 Gbps IPS figures. These are vendor test figures; production performance varies with configuration and traffic conditions.
Does the FG-70F support dual WAN?
Yes. The hardware includes two GE RJ45 WAN interfaces, and FortiOS supports secure SD-WAN capabilities. A successful dual-WAN design also requires appropriate ISP diversity, health checks, routing, DNS and failover planning.
How many Ethernet interfaces does the FG-70F have?
The Fortinet data sheet lists two GE RJ45 WAN ports, one GE RJ45 DMZ port, two GE RJ45 FortiLink ports and five GE RJ45 internal ports. The FortiLink ports can be reconfigured as regular ports when needed.
Do I need a FortiGuard subscription?
The hardware can perform core firewall and networking functions, while FortiGuard service subscriptions provide additional security intelligence and services according to the selected bundle. Choose the service package based on the controls your organization intends to operate and confirm exact inclusions on the current quote.
Is the FortiGate 70F suitable for VPN between branches?
It can support IPsec VPN use cases, but the complete design should consider tunnel count, encrypted traffic volume, routing, authentication and policy. Share the number of sites and expected traffic when sizing a deployment.
How should I compare FG-70F quotations?
Compare exact hardware and subscription part numbers, FortiGuard bundle, service term, support entitlement and implementation scope. Hardware-only and bundled quotes are not equivalent, even when both mention FG-70F.
Can FourTeck quote FortiGate 70F for Tanzania?
Use the FourTeck Tanzania contact page to submit the required model, subscription term and project details. Availability, commercial terms and delivery expectations should be confirmed on the current quotation rather than assumed from a web page.
Decision recap
FortiGate 70F is a compact branch-focused NGFW with secure SD-WAN, FortiOS and FortiGuard integration. Its published 800 Mbps threat-protection, 1 Gbps NGFW and 1.4 Gbps IPS performance make it a strong candidate for appropriately sized sites, while its two WAN ports and multiple internal/FortiLink interfaces support practical branch designs. The right purchase decision depends on inspected bandwidth, future growth, VPN load, segmentation and the chosen FortiGuard subscription. Build the quotation around the complete deployment, not the appliance name alone.
Plan your FortiGate 70F deployment
Send FourTeck your primary and backup internet speeds, user/device estimate, VPN requirements, preferred FortiGuard term and current firewall details. A better input brief leads to a more useful product and deployment discussion.




Reviews
There are no reviews yet.