
FortiGate 121G (FG-121G) Tanzania
The FortiGate 121G is a rack-mount next-generation firewall designed for organizations that need strong security inspection, flexible copper and fiber connectivity, secure SD-WAN, VPN services and local onboard storage in one platform. For Tanzania deployments, the FG-121G can form the secure edge of an office, campus, branch hub, data environment or multi-site network where performance must be considered together with inspection, segmentation and operational resilience.

FortiGate 121G overview and verified hardware
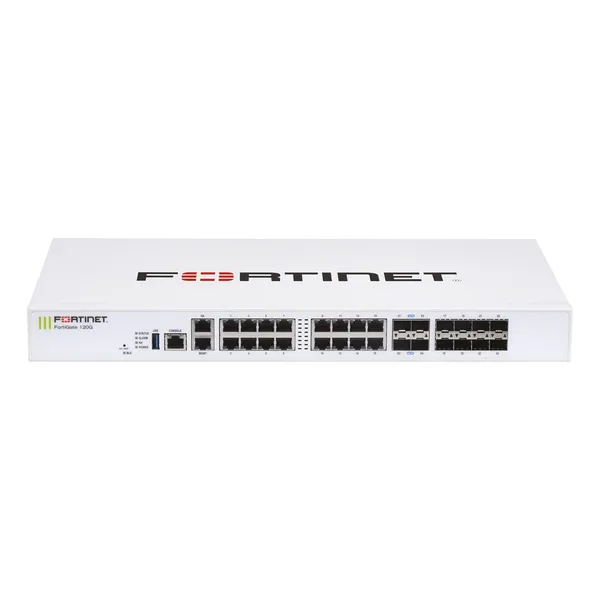
Fortinet positions the FortiGate 120G Series as a converged networking and security platform. The FG-121G model adds 480GB onboard SSD storage to the series hardware. Its front-panel connectivity includes sixteen hardware-accelerated GE RJ45 switch ports, one GE RJ45 management port, one GE RJ45 HA port, eight GE SFP slots and four 10GE SFP+ slots that operate as FortiLink interfaces by default and can be used according to the supported configuration. The appliance uses Fortinet SP5/SOC5 hardware acceleration and is supplied with dual AC power supplies. This combination gives network architects a practical mix of access, fiber and higher-speed uplink interfaces for security edge designs.
Onboard storage distinguishes the 121G from the diskless 120G and can support local logging and storage-dependent operational requirements.
Fortinet hardware acceleration is designed to help process networking and security workloads efficiently.
Copper access, SFP fiber and 10GE SFP+ connectivity support varied WAN, LAN, aggregation and FortiLink designs.
Default dual non-swappable AC power supplies provide 1+1 power redundancy for suitable installations.
Performance planning
Published Fortinet figures for the series include firewall throughput up to 39/39/28 Gbps for 1518/512/64-byte UDP traffic, 5.3 Gbps IPS throughput, 3.1 Gbps NGFW throughput and 2.8 Gbps threat-protection throughput. These are laboratory performance references, not a promise of identical production performance. Real sizing should consider enabled security profiles, encrypted traffic, application mix, concurrent sessions, VPN use, logging, WAN speeds, segmentation, growth and high-availability design.
For procurement, avoid choosing a firewall from internet bandwidth alone. A 1 Gbps circuit can require substantially different firewall capacity depending on whether traffic is simply routed or inspected using IPS, application control, web security and encrypted-traffic inspection. FourTeck can help translate business requirements into a bill of materials and configuration plan.
Security, SD-WAN, VPN and network integration
The FG-121G runs FortiOS and can participate in Fortinet Security Fabric designs. Depending on selected services and configuration, organizations can use firewall policy, intrusion prevention, application control, web security, VPN, secure SD-WAN and segmentation capabilities to build a controlled network edge. The important design question is how these functions map to business traffic: internet access, SaaS, cloud applications, branch-to-branch links, remote users, guest networks, servers, voice, CCTV and operational devices can each require different policies.
The four 10GE SFP+ ports are useful when the firewall must connect to higher-capacity switching or aggregation layers. Eight GE SFP slots support fiber-oriented designs, while the sixteen GE RJ45 switch ports offer flexible copper connectivity. For LAN planning, see FourTeck Tanzania’s network switching and infrastructure guidance, which explains VLANs, fiber uplinks and managed switching as part of an integrated environment. The same site also covers IT assessment, installation and lifecycle services for projects where firewall configuration must be coordinated with the wider network.
Licensing should be specified deliberately. The base appliance and Fortinet support/security service bundles are separate procurement considerations. Buyers should define required FortiCare level, FortiGuard security services, term length and renewal strategy before ordering. A quotation should identify the appliance, service bundle, optics or transceivers, rack/power dependencies, high-availability requirements and professional services rather than treating “FG-121G” as a complete deployment by itself.
Related FourTeck resources
Review the broader product catalogue when building a firewall, switching and infrastructure bill of materials.Technology Services
Useful for installation, configuration, documentation, troubleshooting and lifecycle planning around the firewall.Contact FourTeck Tanzania
Share WAN speeds, users, sites, VPN requirements and preferred security services for quotation planning.About FourTeck Tanzania
Understand the integrated IT, telecom, security and infrastructure approach behind solution planning.
Regional buyers can also use FourTeck Uganda, FourTeck Kenya, FourTeck’s Fortinet UAE specialist site, FourTeck Ghana, FourTeck Nigeria and FourTeck Kuwait when coordinating requirements across multiple countries.
FortiGate 121G (FG-121G) Tanzania
Organizations evaluating the FortiGate 121G in Tanzania typically need more than a firewall specification sheet. They need to know whether the platform has enough inspected-traffic capacity for current internet links, enough interfaces for the planned LAN and WAN architecture, and a licensing approach that matches the security controls the business intends to operate. The FG-121G is especially relevant where buyers want a rack-mount appliance with onboard SSD storage, multiple fiber options and 10GE connectivity while retaining integrated NGFW, VPN and secure SD-WAN capabilities. Tanzania deployments can range from a headquarters internet edge to a branch aggregation point, campus security gateway or segmented environment protecting servers, users, voice, wireless and operational devices.
A Tanzania quotation should start with measurable inputs: primary and backup internet bandwidth, number of users, approximate concurrent sessions, public services, number of VLANs, site-to-site VPN peers, remote-access requirements, cloud applications and expected growth. Security inspection matters because headline firewall throughput does not represent every real deployment. IPS, application control, malware protection and encrypted-traffic inspection add processing requirements. Where two internet providers are available, secure SD-WAN can be considered for policy-based path selection and resilience, but circuit diversity and provider routing should be assessed separately from the firewall itself.
Physical installation also deserves attention. The FG-121G is a 1RU rack-mount appliance, so rack depth, ventilation, cable management, UPS capacity and power feeds should be included in site preparation. Fiber transceivers must match the connected equipment and media. For high availability, organizations should plan duplicate appliances, links and upstream/downstream dependencies rather than assuming two firewalls alone remove every single point of failure. FourTeck Tanzania can use this information to prepare a clearer bill of materials covering appliance, subscriptions, optics, installation and configuration without making unsupported assumptions about stock or delivery.
FortiGate 121G (FG-121G) Dar es Salaam
For Dar es Salaam businesses, the FortiGate 121G can suit security-edge projects where corporate offices, financial operations, logistics environments, hospitality properties, professional services, retail operations and multi-branch organizations depend heavily on internet and cloud access. The purchasing discussion should focus on application criticality and traffic behavior. A company using Microsoft 365, cloud ERP, video meetings, remote VPN and centralized applications has different inspection and resilience requirements from a site whose main traffic is web browsing and email. Mapping these flows before purchase helps determine whether the FG-121G should be deployed as a standalone gateway, in an HA pair or as part of a broader Fortinet architecture.
Dar es Salaam projects often benefit from separating user, server, guest, voice, CCTV and management traffic into controlled network segments. The firewall can enforce policy between appropriate zones, but the switching architecture must carry those VLANs consistently. Higher-speed SFP+ interfaces can be valuable when connecting the firewall to an aggregation or core switch, while GE SFP ports can support fiber links where copper is unsuitable. The 480GB onboard SSD is a practical differentiator for organizations that value local storage capabilities, although log-retention requirements should still be planned against the chosen management and analytics architecture.
Procurement teams should request a quotation that states the exact FG-121G hardware, subscription term, FortiCare level, required FortiGuard package, optics and professional services. If branch connectivity is part of the project, include each remote site’s bandwidth and applications so IPsec VPN and SD-WAN policy can be designed coherently. If internet redundancy is required, document both circuits and desired failover behavior. Power protection and rack cooling should also be checked. These details make the firewall project easier to budget, implement, test and support after handover.
FortiGate 121G (FG-121G) Mwanza
Mwanza organizations considering the FG-121G may be planning a secure regional office, commercial operation, hospitality environment, healthcare site, educational campus, distribution facility or branch hub that connects back to systems elsewhere in Tanzania. In such cases, WAN design is as important as firewall hardware. The network team should identify which applications must remain available during a primary-link outage, which traffic can use a secondary path, and whether branch-to-head-office connectivity uses IPsec VPN, private connectivity or a combination of services. FortiGate secure SD-WAN features can support policy-driven WAN use when configured around real business priorities.
The appliance’s combination of copper, GE SFP and 10GE SFP+ interfaces provides flexibility for sites with mixed network media. A fiber-connected distribution layer can be separated from WAN handoffs and management connectivity, while internal VLANs can be used to reduce unnecessary trust between departments or device groups. This is particularly useful when a site has business computers, wireless users, IP cameras, VoIP phones and servers sharing the same physical infrastructure. Segmentation should be documented so troubleshooting remains practical and firewall rules do not become an unstructured collection of exceptions.
For Mwanza procurement, provide current and planned WAN speeds, number of staff and devices, security-service expectations, VPN peers and any local server workloads. If the site is expected to operate with limited on-site IT resources, centralized management and clear configuration documentation become especially important. Backup configurations, firmware procedures, administrator roles and escalation paths should be agreed during deployment. The FG-121G’s capacity should be evaluated against enabled inspection rather than raw firewall throughput alone, leaving reasonable headroom for growth and new security services.
FortiGate 121G (FG-121G) Arusha
Arusha businesses can evaluate the FortiGate 121G for secure connectivity across offices, tourism and hospitality operations, NGOs, educational organizations, professional services and distributed business environments. These organizations may have a combination of staff networks, guest wireless, cloud services, point-of-sale or operational applications and remote users. The firewall design should therefore begin with trust boundaries. Guest users should not automatically share access with corporate systems, management interfaces should be restricted, and servers or critical applications may require tighter policy than ordinary user browsing.
Where an Arusha site connects to Dar es Salaam, another Tanzanian city or an overseas office, site-to-site VPN design should consider routing, overlapping address ranges, encryption requirements, failover and monitoring. Secure SD-WAN can help steer traffic across available WAN links according to policy and link health. The FG-121G’s 10GE SFP+ ports also create room for higher-capacity internal connectivity when the firewall sits between fast switching layers or handles aggregated traffic from multiple network segments. Fiber modules and cabling must be selected for the actual switch interfaces and link distances.
A complete purchase request should include the intended FortiGuard security package and support term rather than asking only for hardware price. Buyers should also define whether configuration, migration from an existing firewall, VPN recreation, rule cleanup, testing and documentation are needed. Migration planning is important because existing firewall policies may contain obsolete objects or undocumented exceptions that should not be copied blindly. A staged cutover with rollback planning can reduce disruption. FourTeck can scope the appliance and associated services from these inputs while the customer retains clear visibility into what the quotation covers.
FortiGate 121G (FG-121G) Dodoma
For Dodoma deployments, the FortiGate 121G can be assessed for government-adjacent business environments, institutions, offices, education, healthcare and organizations that require controlled internet access and secure connections to other sites. The core planning question is not simply how many employees use the network; device count, cloud adoption, VPN traffic, encrypted web traffic, public-facing services and internal segmentation all influence firewall workload. A careful assessment helps prevent both undersizing and unnecessary oversizing.
The FG-121G provides a broad physical interface mix for network architects. Sixteen GE RJ45 switch ports can serve copper-connected requirements, eight GE SFP slots support fiber interfaces and four 10GE SFP+ ports provide faster uplink options. Dedicated management and HA connectivity support operational design, while dual AC supplies provide appliance-level power redundancy when connected appropriately. For sites where availability is important, upstream ISP devices, switches, power sources and cabling should be considered alongside firewall HA so the architecture does not preserve hidden single points of failure.
Dodoma buyers should include compliance or internal policy requirements in the design brief: required web controls, intrusion prevention, application visibility, remote-access rules, administrator separation, logging and retention expectations. These requirements affect subscription selection and operational procedures. A documented implementation should cover interface addressing, VLANs, routes, policies, VPNs, SD-WAN rules, security profiles, administrator access and configuration backups. When a project is specified this way, procurement can compare quotations on equivalent scope rather than comparing an appliance-only offer with a fully configured security solution.
FortiGate 121G (FG-121G) UAE
UAE organizations evaluating the FortiGate 121G commonly need a secure edge for headquarters, branches, warehouses, retail operations, hospitality sites or multi-site businesses with substantial cloud and internet dependency. The FG-121G’s 480GB SSD, SP5 acceleration and mix of GE and 10GE interfaces make it a candidate for environments where security and networking functions converge at the perimeter. Buyers coordinating Tanzania and UAE locations can also standardize selected firewall policies, naming conventions and VPN templates while still adapting each site to its own ISP circuits, address plan and business applications.
For UAE deployments, secure SD-WAN may be relevant where multiple internet or WAN links are used for resilience and application-aware path selection. Site-to-site IPsec can connect offices across countries, but routing, latency, application architecture and provider characteristics should be evaluated before final design. Organizations with high internal bandwidth should consider how the four 10GE SFP+ ports connect to the switching layer. The firewall should not become an accidental bottleneck because a high-speed LAN is connected through underspecified links or because inspection capacity was estimated from raw firewall figures.
Procurement should identify exact support and security subscription terms, required optics, HA needs and implementation scope. For UAE-specific Fortinet requirements, the FourTeck Fortinet UAE resource provides a regional specialist path. Cross-border organizations can use a common requirements template for Tanzania and UAE sites: WAN circuits, users, applications, VLANs, VPN peers, security services, logging, rack/power and migration dependencies. That produces a more consistent architecture without assuming every branch needs identical hardware.
FortiGate 121G (FG-121G) Uganda
Uganda businesses can consider the FortiGate 121G when they need a next-generation firewall for a central office, branch hub, institutional network or distributed organization. A typical design may combine internet security, site-to-site VPN, remote access, network segmentation and SD-WAN. The FG-121G’s onboard SSD can be useful in operational designs that benefit from local storage, while its copper, SFP and 10GE interface options allow the appliance to fit different LAN and WAN topologies. Model selection should nevertheless be based on inspected traffic and growth rather than interface count alone.
Organizations linking Uganda with Tanzania, Kenya or other markets should define which applications traverse the WAN and which can break out locally to the internet. SaaS applications may benefit from local internet paths, while centralized ERP or file systems may depend on VPN connectivity to another site. SD-WAN policy can prioritize links according to performance and business importance when the underlying connectivity supports the design. Security rules should be consistent enough to manage centrally but specific enough to respect each site’s network segments and operational needs.
A Uganda quotation request should document internet speeds, user and device estimates, VPN tunnels, required FortiGuard services, support term and whether HA is needed. It should also include switching and wireless dependencies because a firewall cannot enforce clean segmentation if the LAN is not configured to carry the intended VLANs. Customers coordinating requirements in Uganda can reference FourTeck Uganda while maintaining a common regional security architecture with Tanzania projects.
FortiGate 121G (FG-121G) Kampala
In Kampala, the FG-121G can be evaluated for corporate offices, service businesses, financial operations, healthcare, education, logistics and other organizations whose productivity depends on stable internet and controlled access to applications. Dense office environments often combine wired users, Wi-Fi, voice, video meetings, cloud services and servers. The firewall therefore needs to be integrated with switching and wireless policy instead of deployed as an isolated internet box. VLAN-based segmentation can create clearer boundaries between staff, guests, servers, voice and infrastructure management.
The appliance’s four 10GE SFP+ interfaces can support higher-speed connections to suitable aggregation switches, while GE SFP and copper interfaces provide flexibility for other network segments and handoffs. If the business operates more than one internet connection, secure SD-WAN can be designed around application needs and link health. The design should specify what happens when a link degrades rather than only when it fails completely. Real-time applications such as voice and conferencing may need different path-quality thresholds from bulk downloads or backups.
Kampala procurement teams should ask for an itemized bill covering FG-121G hardware, chosen FortiGuard/FortiCare term, transceivers, HA equipment if required and professional services. For replacement projects, provide the existing firewall configuration and a list of known business-critical rules. Migration is an opportunity to remove stale objects and rationalize policies rather than reproduce years of accumulated exceptions. Testing should include internet access, VPNs, published services, DNS, critical applications, failover and administrative access before final handover documentation is accepted.
FortiGate 121G (FG-121G) Arua
Arua organizations may evaluate the FortiGate 121G where a regional site needs secure connectivity to headquarters, cloud services or partner systems. In locations where connectivity options can differ from major metropolitan sites, the firewall project should begin with a realistic WAN inventory. Document available primary and backup links, their bandwidth, addressing method and expected stability. Secure SD-WAN can use multiple links intelligently, but it cannot compensate for two circuits that share the same physical dependency if true resilience is the objective.
The FG-121G provides sufficient interface diversity to build structured WAN and LAN zones, including copper, SFP fiber and 10GE SFP+ options. The 480GB onboard SSD differentiates the 121G from the 120G and can be relevant to logging and local storage requirements. For a remote or regional site, operational simplicity is particularly valuable. Administrators should use clear interface names, documented VLANs, standardized firewall objects and controlled administrator permissions so remote troubleshooting does not depend on one individual’s memory.
When requesting a quote for Arua, include expected remote-access users, site-to-site VPN peers, security services, network segments and any need for centralized management. UPS capacity and environmental conditions should be considered because stable power and ventilation are foundational to network availability. If the firewall will replace an existing gateway, plan the change window, rollback method and remote support path in advance. A well-documented deployment can make an Arua branch easier to operate as part of a wider Uganda or East Africa network.
FortiGate 121G (FG-121G) Mbarara
For Mbarara businesses, the FortiGate 121G can provide a platform for internet-edge security, branch connectivity and internal segmentation. Suitable projects may include growing commercial offices, education, healthcare, hospitality, distribution and multi-site organizations. Buyers should define the traffic that genuinely needs security inspection and the applications that must remain available during WAN problems. This requirement-based approach is more useful than selecting a model solely from employee count because modern sites can have many non-user devices and substantial encrypted application traffic.
A practical design can place corporate users, guest wireless, servers, cameras and infrastructure management in separate security zones. The firewall then enforces only the communication required between them. If a FortiSwitch or other managed switching platform carries these VLANs, trunking and uplink capacity should be designed consistently. The FG-121G’s 10GE SFP+ connectivity offers headroom for suitable high-speed internal links, while GE SFP interfaces can support fiber runs or provider handoffs depending on transceiver compatibility.
Mbarara procurement planning should include FortiGuard and FortiCare requirements, not just the hardware SKU. Security subscriptions and support affect what the organization can operate over the appliance lifecycle. Buyers should also specify configuration backup, firmware-management responsibility, logging, administrator access and post-installation documentation. For a branch network, consistent templates across sites can simplify support while allowing local WAN and addressing differences. These operational requirements should be agreed before deployment so the final handover includes both working connectivity and maintainable security policy.
FortiGate 121G (FG-121G) Gulu
Gulu sites looking at the FortiGate 121G may need a secure gateway that supports local internet access while maintaining encrypted connectivity to other offices. Branch environments benefit from clear decisions about which traffic uses the VPN and which exits directly to cloud services. Sending every SaaS session through a distant headquarters can create unnecessary latency, while unrestricted local breakout can reduce central visibility if policy is not coordinated. FortiGate secure SD-WAN and security controls can be designed to balance these requirements according to the organization’s architecture.
Interface planning is another strength of the FG-121G. Copper ports can connect appropriate local devices or networks, SFP slots support fiber and four 10GE SFP+ interfaces provide faster connectivity for compatible switching. However, every interface should have a defined purpose and security zone; using available ports without a network model can create complexity. The onboard 480GB SSD is useful where local storage capabilities matter, while centralized analytics or management can still be considered for organizations operating multiple firewalls.
For a Gulu deployment, include remote-support practicality in the project plan. Configuration backups, diagrams, ISP details, administrator procedures and a tested recovery approach are important when specialist staff are not permanently on site. UPS-backed power for the firewall, switches and ISP equipment can help the network remain stable through short interruptions. When requesting a quotation, state whether installation, migration, VPN setup, SD-WAN configuration, security profiles, user access and documentation are required so the solution scope is clear.
FortiGate 121G (FG-121G) Kenya
Kenya organizations can assess the FortiGate 121G for enterprise branches, headquarters, campuses and secure internet-edge projects requiring a mix of NGFW security and flexible connectivity. The 480GB SSD model is relevant when onboard storage is part of the requirement. For businesses operating across Kenya, Tanzania and Uganda, standardizing on FortiOS policy conventions and management practices can simplify operations, although appliance sizing should still reflect each site’s bandwidth, users, security services and application profile.
The FG-121G supports architectures where multiple WAN connections are combined with secure SD-WAN and VPN. A Nairobi headquarters, for example, may need higher aggregate throughput and more VPN peers than a smaller branch, while a data-intensive site may value 10GE connections to internal switching. The four SFP+ interfaces provide options for high-speed uplinks, but actual design should confirm transceivers, switch compatibility and redundancy. Network segmentation should be coordinated across firewall and switch configurations so security policy is enforceable end to end.
Kenya procurement teams should compare complete lifecycle cost rather than appliance price alone. Include the selected FortiGuard bundle, FortiCare term, renewal horizon, optics, HA requirements, migration and ongoing management. If existing firewall rules are being moved, review them for relevance before cutover. Organizations coordinating Kenyan requirements can use FourTeck Kenya for the regional conversation while using the same technical questionnaire across East African sites to improve consistency.
FortiGate 121G (FG-121G) Kuwait
Kuwait businesses evaluating the FortiGate 121G may be looking for a security platform that combines high-performance firewalling, IPS, VPN and SD-WAN with 10GE-capable network integration. The model’s 480GB onboard SSD and dual AC power supplies make it suitable for rack-based business infrastructure where local storage and power resilience are desired. As with any NGFW, the sizing exercise should focus on inspected application traffic, encrypted sessions, VPN usage and growth rather than the maximum firewall number in isolation.
Organizations with multiple offices can use site-to-site IPsec and SD-WAN policies to connect branches while controlling direct internet access. Internal segmentation can separate business users, servers, guests, voice and operational systems. Where the FG-121G connects to fast switching, its 10GE SFP+ ports can reduce internal bottlenecks if the broader architecture is designed for those speeds. Optics, fiber type and switch-port compatibility should be confirmed before ordering because SFP/SFP+ requirements are part of the solution, not incidental accessories.
A Kuwait quotation should clearly state hardware, support and security subscriptions, professional services and renewal term. Buyers with regional operations can align policy standards with Tanzania or UAE sites while keeping local WAN configuration distinct. FourTeck Kuwait provides the regional path for requirements. Before migration, document public IPs, VPN peers, routing, NAT, published services and critical firewall rules to reduce uncertainty during cutover.
FortiGate 121G (FG-121G) Ghana
Ghana organizations can consider the FortiGate 121G for secure business networks that need internet protection, VPN connectivity, SD-WAN and structured segmentation. The appliance’s interface mix makes it flexible for headquarters, larger branches and sites that connect to both copper and fiber infrastructure. The 480GB SSD is the key hardware distinction of the 121G within the 120G series, and it should be selected when that onboard storage capability supports the intended operational design.
A Ghana deployment should start with application and risk mapping. Identify cloud services, internal servers, remote workers, branch connections, guest access and any public-facing systems. This allows firewall zones and policies to be designed around business flows instead of broad allow rules. Security inspection profiles can then be applied according to risk and performance needs. For multi-WAN environments, SD-WAN can monitor link quality and steer selected traffic, while IPsec can protect inter-site communication over internet links.
Procurement should include licensing, support, transceivers, rack and power dependencies and professional services. If high availability is required, the network around the firewall must also be resilient. Customers should confirm switch uplinks, ISP handoffs and power paths so the HA pair does not depend on a single upstream component. Regional buyers can use FourTeck Ghana for local project coordination while maintaining shared security standards with Tanzania and other African operations.
FortiGate 121G (FG-121G) Nigeria
Nigeria businesses evaluating the FortiGate 121G may have demanding requirements around branch connectivity, internet resilience, cloud access and network segmentation. The platform can combine next-generation firewall controls with secure SD-WAN and VPN, helping organizations consolidate security and WAN policy at the edge. Its four 10GE SFP+ interfaces are useful where a site needs faster internal uplinks, while eight GE SFP and sixteen GE RJ45 switch ports provide additional connectivity options for varied network designs.
For organizations with several ISP links, define application priorities and acceptable latency or packet-loss thresholds before configuring SD-WAN. A second circuit is most valuable when its failure dependencies are understood. Branch VPN design should also include routing, address planning and failover behavior. Large distributed businesses can benefit from standardized policy objects and centralized management, but each site should retain configuration appropriate to its bandwidth, users and local services. The 480GB SSD can support local storage-related needs as part of that architecture.
Nigeria procurement teams should request an exact FortiGuard/FortiCare bundle and term alongside the FG-121G appliance. Include HA if required, optics, migration, VPN setup, policy configuration, testing and documentation. This prevents price comparisons from mixing fundamentally different scopes. FourTeck Nigeria can support the regional requirements conversation, while cross-border IT teams can use common design standards for Nigeria, Ghana, Tanzania, Kenya and Uganda.
FortiGate 121G (FG-121G) Seychelles
Seychelles organizations can evaluate the FortiGate 121G for hospitality, corporate, professional, institutional and multi-site networks where secure internet access and reliable inter-site connectivity are important. Island and hospitality environments can place particular emphasis on guest access, staff networks, cloud applications and resilient WAN design. The firewall should be integrated with wireless and switching architecture so guest devices remain appropriately separated from business systems and infrastructure management.
If multiple connectivity services are available, secure SD-WAN can be configured to use them according to business policy and measured link health. The design should distinguish critical applications from traffic that can tolerate degradation. Site-to-site VPN can connect separate properties or offices where appropriate. The FG-121G’s copper, SFP and 10GE SFP+ connectivity provides options for varied LAN designs, and the 480GB onboard SSD adds local storage capability. Environmental planning should include a ventilated rack, UPS protection and organized cabling.
For procurement, document user and device counts, WAN bandwidth, guest-network requirements, VPN peers, security subscriptions and expected growth. Hospitality sites should consider peak occupancy rather than average usage because guest traffic can vary significantly. A complete quotation should state the firewall, support/security term, optics and deployment services. Configuration documentation and backups are especially useful for locations where remote support may be important. This approach turns the FG-121G purchase into a maintainable network-security project rather than a standalone hardware acquisition.
FortiGate 121G buying and quotation checklist
Prepare these details before requesting a quote: current and planned internet bandwidth; number of sites; approximate users and devices; required VLANs/security zones; site-to-site VPN peers; remote-access users; public services; preferred FortiGuard security bundle; FortiCare term; HA requirement; SFP/SFP+ optics; switching uplink speeds; rack and UPS environment; migration requirements; logging expectations; centralized management needs; and target implementation window.
For renewals or upgrades, also provide the current FortiGate model, serial-dependent entitlement information through an appropriate secure channel, existing subscription expiry, FortiOS version, interface utilization and configuration complexity. Do not send passwords in a quotation request. A structured requirement list helps distinguish appliance cost from the complete cost of a secure deployment.
Frequently asked questions
What is the difference between FortiGate 120G and 121G?
The main published hardware distinction is internal storage: the FortiGate 121G includes one 480GB SSD, while the 120G is the diskless model. Core interface and published series performance figures are otherwise aligned in the Fortinet datasheet.
Does the FG-121G include 10 Gigabit interfaces?
Yes. Fortinet specifies four hardware-accelerated 10GE SFP+ FortiLink slots by default, alongside eight GE SFP slots and sixteen GE RJ45 switch ports. Confirm the required SFP/SFP+ transceivers for your connected equipment and fiber type.
Can FortiGate 121G be used for SD-WAN and VPN?
FortiOS supports secure SD-WAN and VPN capabilities. The correct design depends on WAN circuits, routing, applications, VPN peers, redundancy and security requirements. Performance should be sized using the relevant inspected-traffic and VPN requirements.
Do I need a FortiGuard subscription?
Subscription requirements depend on the security services you intend to operate. Procurement should define the desired FortiGuard package and FortiCare support term rather than assuming the base hardware includes every service for the required lifecycle.
How should I size an FG-121G deployment?
Use real WAN speeds, application mix, security inspection, encrypted traffic, concurrent sessions, VPN, number of sites, growth and HA requirements. Maximum firewall throughput alone is not an adequate sizing method for an NGFW deployment.
Decision recap
Choose the FG-121G when your design benefits from the FortiGate 120G Series security and networking platform plus 480GB onboard SSD storage, and when its interface mix and inspected-traffic capacity align with your requirements. Validate subscriptions, optics, HA, management and migration scope before purchase.
Consultation panel
Send FourTeck your WAN speeds, user/device estimate, locations, VPN requirements, current firewall model and preferred security term. The resulting discussion can focus on the correct appliance, licenses and implementation scope rather than an unsupported one-size-fits-all configuration.




Reviews
There are no reviews yet.