
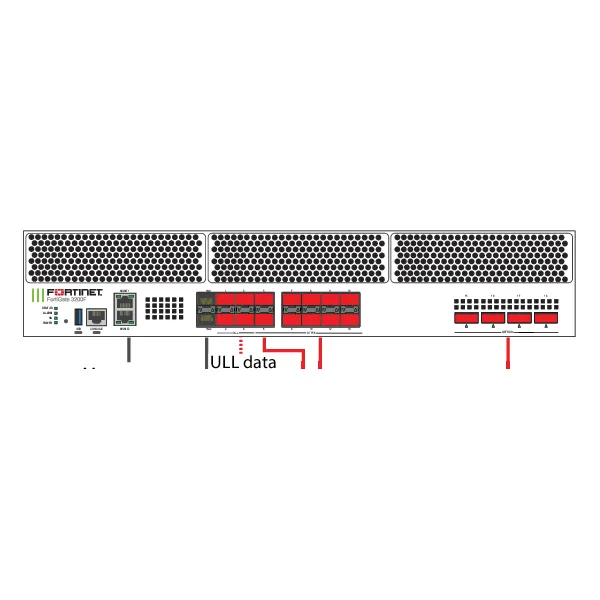
FortiGate 3201F (FG-3201F)
FortiGate 3201F is the storage-equipped member of Fortinet’s FortiGate 3200F Series, engineered for high-capacity enterprise and data-center security. It combines purpose-built NP7 and CP9 security processing, four 400GE-capable QSFP-DD interfaces, dense 50/25/10GE connectivity, dual onboard SSDs and redundant power in a 2RU appliance. For Tanzania buyers, the important purchasing question is not only peak firewall throughput: interface design, inspected traffic, encrypted traffic, session scale, high availability, logging, subscriptions and migration requirements should all be defined before quotation.
FortiGate 3201F Overview
The FG-3201F is intended for environments where security processing must coexist with very high network capacity. Fortinet’s current 3200F Series documentation identifies the 3201F with four hardware-accelerated 400GE QSFP-DD / 200GE QSFP56 / 100GE QSFP28 / 40GE QSFP+ ports, ten hardware-accelerated 50GE SFP56 / 25GE SFP28 / 10GE SFP+ slots, four ultra-low-latency 25GE SFP28 / 10GE SFP+ / GE SFP slots, two high-availability SFP56-family slots, two 10GE/GE RJ45 management ports, USB and console connectivity. The 3201F differentiates itself from the 3200F through onboard storage, making the exact model designation important during procurement.
Fortinet publishes high performance figures for the 3200F family, but real sizing should use the security profile that will actually be enabled. A data center running firewall-only traffic has a different workload from an internet edge performing IPS, application control, malware inspection and SSL inspection. Likewise, a VPN aggregation design has different requirements from east-west segmentation. FourTeck recommends sharing current and projected bandwidth, encrypted-traffic ratio, session counts, application mix, required interfaces, redundancy design and logging expectations before treating any headline number as a sizing decision.
Verified FG-3201F Technical Highlights
| Area | FortiGate 3201F |
|---|---|
| Product / SKU | FortiGate 3201F / FG-3201F |
| Acceleration | NP7 and CP9 hardware acceleration |
| High-speed ports | 4 × 400GE-capable QSFP-DD plus SFP56/SFP28 high-speed interfaces |
| Storage | 2 × 960GB SSD onboard storage |
| Form factor | 2RU rack mount |
| Power | 2 AC power supplies |
| Firewall throughput | Up to 387 Gbps in Fortinet’s published 3200F-series test profile; results depend on packet size and enabled features |
| NGFW throughput | 47 Gbps published for the enterprise-mix test profile |
| Threat protection | 45 Gbps published for the enterprise-mix test profile |
Buying and Sizing Guidance
Treat FG-3201F selection as an architecture decision. Confirm the transceiver and cabling plan for 400/200/100/50/25/10GE links, expected east-west and north-south traffic, inspection policy, VPN load, HA mode, routing requirements, virtual domains, management platform, log-retention strategy and FortiGuard/FortiCare term. If the project is replacing an existing firewall, include current interface mappings, VLANs, routing, NAT, VPNs, published services and policy objects in the migration scope. This reduces the risk of buying sufficient raw throughput while overlooking ports, optics, subscriptions or implementation effort.
FortiGate 3201F Tanzania
FortiGate 3201F Tanzania enquiries typically make sense for organizations with substantial traffic concentration rather than ordinary branch-office requirements. Large enterprises, service providers, financial institutions, public-sector environments, universities, cloud-connected operations and data-center operators may need a firewall platform capable of handling high-speed fiber interfaces while applying security controls at scale. The FG-3201F should therefore be evaluated against the actual architecture: internet edge, data-center perimeter, internal segmentation, VPN aggregation, multi-tenant security or a combination of these roles. Tanzania procurement teams should document current bandwidth, expected three-to-five-year growth, peak session behavior, encrypted traffic, critical applications and planned network-core speeds before requesting a bill of materials.
A strong Tanzania deployment plan also considers supporting infrastructure. A 2RU high-end firewall belongs in a rack with suitable power, UPS protection, cooling, cable management and correctly selected optical modules. Redundant power feeds and high availability should be discussed in the context of the site’s real resilience design rather than assumed from the appliance alone. For organizations using multiple carriers, route design and failover objectives should be agreed before configuration. If traffic crosses between data centers, branches and cloud environments, IPsec capacity, routing convergence and application dependencies need to be mapped.
Licensing is another procurement dimension. The appliance and the desired FortiGuard security services, FortiCare support term and centralized management or analytics components should be quoted as a coherent solution. Buyers should ask which subscriptions are included in the proposed SKU and for what term instead of assuming all security services are perpetual. FourTeck Tanzania can use the project brief to discuss model fit, licensing, migration, configuration and integration requirements. For broader design context, review the FourTeck Tanzania technology portfolio, which explains how firewalling connects with switching, servers, Wi-Fi and other infrastructure.
FortiGate 3201F Dar es Salaam
FortiGate 3201F Dar es Salaam projects are most credible where the firewall sits in a high-capacity enterprise or data-center path. A headquarters, colocation environment, financial platform, large campus, carrier-facing edge or centralized service hub may aggregate far more traffic than a conventional office firewall. For such sites, the first design task is to map the network zones and uplinks: internet circuits, core switching, server or virtualization fabrics, DMZs, cloud connectivity, partner links and management networks. This determines whether the FG-3201F’s 400GE-capable and dense high-speed interfaces align with the physical topology.
Dar es Salaam buyers should separate performance requirements into measurable categories. Raw firewall throughput, inspected application traffic, SSL inspection, IPsec VPN, concurrent sessions and new connections per second represent different constraints. A platform can have ample packet-forwarding capacity yet still need careful sizing for an inspection-heavy workload. Organizations hosting public applications should also document inbound services, NAT design, DDoS strategy outside or alongside the firewall, certificate handling and segmentation between public and internal workloads. If the device will terminate site-to-site tunnels from many branches, tunnel count and aggregate encrypted bandwidth matter.
Implementation planning should include a migration window, rollback plan, configuration review and post-cutover validation. High availability is valuable only when upstream and downstream switching, power and routing are designed to avoid hidden single points of failure. The two onboard SSDs on FG-3201F can support local storage use cases defined by Fortinet, but organizations with formal log-retention or SOC requirements should still determine whether centralized analytics is needed. For a quotation or technical discussion, use the verified FourTeck Tanzania contact page and include interface speeds, security services, HA requirement, current firewall and desired project timeline.
FortiGate 3201F Mwanza
FortiGate 3201F Mwanza requirements should be driven by workload, not by city name or brand preference. The platform is positioned for high-capacity security, so a Mwanza organization should first establish whether its traffic and resilience needs justify this class of appliance. Potential environments include major institutional networks, large industrial operations, service hubs, data-heavy campuses and organizations consolidating security for many remote sites. If the requirement is only a modest office internet connection, a smaller FortiGate may be operationally and commercially more appropriate; accurate sizing protects the budget as well as the network.
For a larger Mwanza deployment, WAN and branch architecture can become central. Organizations connecting distributed facilities should inventory each link, expected VPN bandwidth, latency-sensitive applications and failover priorities. Business systems such as ERP, voice, video, cloud applications and remote administration do not all respond to link degradation in the same way. Secure SD-WAN and routing policies can be designed around application needs, but the policy objective must be documented. Security inspection should similarly follow risk: server segments, user networks, guest access, operational technology and public services may require different controls.
Physical deployment deserves equal attention. Verify rack depth, power circuits, UPS capacity, cooling, fiber termination, transceiver compatibility and patching before the appliance arrives. Document management access separately from production data paths, and decide how configuration backups, administrator authentication and change control will be handled. For projects that also involve LAN upgrades, the FourTeck Tanzania shop and product catalogue can provide a starting point for related infrastructure discussions. A useful FG-3201F quotation brief should state quantity, HA design, required optics, subscription term, installation scope, migration requirements and any centralized management or reporting components.
FortiGate 3201F Arusha
FortiGate 3201F Arusha can be evaluated for large organizations that need a security gateway between high-speed networks, data-center resources, cloud connectivity and distributed sites. Hospitality groups, large institutions, regional headquarters and multi-site operators may have different traffic patterns, so the appliance should be matched to measured requirements rather than a generic user-count rule. A network with thousands of short web sessions behaves differently from one moving large data sets between servers or terminating encrypted tunnels from many sites. The security policy also affects throughput because deeper inspection requires more processing than simple stateful forwarding.
For Arusha, resilience planning can include dual internet links, diverse fiber paths, high availability and backup power, but each layer should be verified independently. Two firewalls in HA do not create full resilience if both depend on one upstream switch or one power source. Likewise, multiple WAN links do not guarantee application continuity unless routing, health checks and failover behavior are configured and tested. The FG-3201F’s high-speed interface options provide substantial design flexibility, yet optics and link speeds must match the connected switching and carrier equipment.
Procurement should define whether the request is appliance-only or includes FortiGuard services, FortiCare, deployment, migration and operational handover. Teams that need central policy control or analytics should identify those requirements early so associated components are included in the architecture. Change documentation, administrator roles, configuration backup and firmware lifecycle are also part of operating a high-end firewall responsibly. FourTeck can help translate the requirement into a quotation checklist rather than assuming a single bundle fits every Arusha environment. The goal is a design that balances inspection, availability, connectivity and maintainability while leaving sensible headroom for future traffic growth.
FortiGate 3201F Dodoma
FortiGate 3201F Dodoma discussions may arise in large public-sector, institutional, education, service-provider or enterprise environments where centralized security must protect substantial network capacity. Procurement teams should begin with a clear statement of purpose: perimeter firewall, data-center segmentation, VPN concentration, secure interconnection, or consolidation of several existing security gateways. This role determines which performance figures, interfaces and licenses are most relevant. It also prevents a specification exercise from becoming a simple comparison of the largest headline throughput number.
For governance-focused environments, operational controls can be as important as hardware. Define administrator authentication, separation of duties, configuration backup, change approval, logging, alerting and audit retention. If security events must be retained centrally, include the analytics architecture in the project. If the firewall will separate sensitive departments or server zones, design address objects, policies and routing around explicit trust boundaries. Where remote sites connect through IPsec, standard tunnel templates and naming conventions can make a national or regional deployment easier to operate.
Dodoma installations should also account for rack, power and environmental readiness. The FG-3201F is a 2RU appliance with redundant AC power supplies, so a resilient design should decide how those feeds connect to UPS and distribution equipment. High-speed optical links require compatible transceivers and fiber types. Before ordering, validate every accessory and service SKU against the final bill of materials. FourTeck’s Tanzania services information can be used to frame broader installation, configuration and lifecycle requirements. A complete quotation request should include topology, traffic, HA, interfaces, security services, support term and implementation expectations.
FortiGate 3201F UAE
FortiGate 3201F UAE is relevant to data centers, large enterprise cores, high-capacity internet edges and organizations consolidating substantial security workloads. UAE projects often involve dense fiber infrastructure, colocation facilities, cloud interconnects and multi-site networks, making interface planning especially important. The FG-3201F provides four 400GE-capable QSFP-DD interfaces plus multiple 50/25/10GE-class ports, but a successful design still depends on the exact switch ports, optics, breakout requirements and routing architecture. Buyers should confirm whether the firewall is expected to operate inline at the perimeter, segment data-center zones, terminate VPNs or perform several roles simultaneously.
Security-service selection affects both commercial scope and performance planning. IPS, application control, web security, malware protection and SSL inspection should be mapped to traffic that genuinely requires them. A blanket assumption that every packet receives every profile can either oversize the design or create unrealistic expectations. Conversely, sizing from firewall-only throughput can understate the needs of an inspection-heavy environment. Fortinet publishes separate benchmark categories for this reason. The UAE procurement brief should therefore include inspected bandwidth, encrypted traffic percentage, sessions, connection rates and growth expectations.
For regional buyers, FourTeck’s Fortinet UAE specialist site provides additional Fortinet product context, while FourTeck UAE covers broader infrastructure requirements. Availability, pricing, support and delivery should always be confirmed for the exact requested SKU and term rather than inferred from a web page. Include HA quantity, optics, FortiGuard package, FortiCare term, migration, rack location and implementation window in the request so the quotation reflects the intended deployment rather than only the base appliance.
FortiGate 3201F Uganda
FortiGate 3201F Uganda fits the upper end of Fortinet deployment scenarios, where an organization needs high-capacity firewalling for a data center, major enterprise hub, service-provider environment or centralized multi-site architecture. The model should not be selected solely because it is powerful. A Ugandan buyer should compare actual internet capacity, inter-site traffic, data-center uplinks, inspection requirements and expected growth with the published Fortinet performance profiles. This creates a defensible sizing decision and may reveal whether FG-3201F, another high-end model or a smaller platform is the better fit.
For national branch networks, the central firewall may aggregate IPsec tunnels and business traffic from many locations. Document the number of branches, peak tunnel traffic, routing design, failover behavior and applications that must remain available during WAN degradation. If branches use multiple providers, SD-WAN policy and hub design should be coordinated with the central security architecture. High availability at the hub should include redundant switching and power paths so that firewall redundancy is not undermined by surrounding infrastructure.
Operational planning should define how policies are managed, how logs are retained and who is responsible for firmware, backups and incident response. The FG-3201F includes onboard storage, but centralized reporting or analytics may still be appropriate depending on retention and compliance needs. Uganda buyers can review the FourTeck Uganda regional site for local product context and use the Tanzania contact route when the project is being coordinated through FourTeck Tanzania. Ask for a quotation based on exact quantity, subscription term, optics, HA, migration and implementation requirements; do not treat generic online pricing or stock statements as confirmation for a specific project.
FortiGate 3201F Kampala
FortiGate 3201F Kampala can serve as a high-capacity security platform for organizations concentrating internet, data-center, cloud and branch traffic in the capital. Financial services, large enterprises, technology operators, institutions and organizations running central infrastructure may need to inspect large traffic volumes without reducing the network to lower-speed links. The 3201F’s interface density supports modern high-speed designs, but topology comes first: map core switches, server fabrics, upstream providers, DMZs, management networks and inter-site connections before assigning ports.
Kampala projects often need a migration plan from an existing firewall. Capture the current configuration before procurement: physical and logical interfaces, VLANs, static and dynamic routes, NAT, VIPs, VPNs, user authentication, certificates, security profiles and policy dependencies. Decide what should be migrated as-is and what should be redesigned. Copying years of unused rules into a new high-end appliance can preserve technical debt. A structured migration can clean obsolete objects while protecting business-critical services.
The quotation should distinguish hardware from services and subscriptions. FortiGuard packages and FortiCare terms vary, and project teams may also require centralized management, analytics, professional configuration or post-cutover support. Optical modules and cabling can materially affect the bill of materials at 400/100/50/25GE speeds. Before ordering, confirm supported transceivers and link design against current Fortinet documentation. Finally, define acceptance tests: internet access, published applications, VPN tunnels, routing failover, HA failover, security logging and management access. These checks turn a hardware purchase into an operationally verified Kampala security deployment.
FortiGate 3201F Arua
FortiGate 3201F Arua is a specialized requirement because the appliance is designed for high-capacity enterprise and data-center workloads. An Arua organization considering this model should establish whether it is building a regional hub, major institutional network, service platform or aggregation point that genuinely needs high-speed interfaces and large security-processing headroom. For smaller sites, centralizing security at another hub or choosing a smaller FortiGate may be more efficient. Sizing should follow measured traffic and architecture rather than a desire to standardize on the largest appliance.
Where Arua is part of a distributed network, WAN resilience may be the dominant design issue. The local site could connect to Kampala or another data center over primary and backup circuits, with business applications hosted remotely or in cloud services. In that case, tunnel architecture, routing convergence and application priority may matter more than raw local internet throughput. Security policy should also account for branch segmentation, guest networks, server or operational systems and remote administration.
If FG-3201F is deployed locally, infrastructure readiness must match the appliance class. Verify rack space, environmental conditions, UPS and power distribution, optical connectivity, spare interfaces and secure out-of-band management. Plan how firmware and configuration backups will be handled when on-site access is limited. For procurement, request the exact appliance, support and security subscription term, optics, HA components and installation scope. Avoid assuming that a bundle advertised for another country applies unchanged to Arua. A project-specific bill of materials is the safer route, particularly for high-value infrastructure where missing optics, rails, licenses or implementation tasks can delay commissioning.
FortiGate 3201F Mbarara
FortiGate 3201F Mbarara should be considered when the security gateway protects a substantial regional or enterprise environment rather than a conventional branch. Large institutions, industrial operations, campuses or organizations aggregating several sites can evaluate the platform for high-speed perimeter security and segmentation. Start with a traffic matrix showing where data originates, where it is going, how much is encrypted and which flows require advanced inspection. This makes it easier to determine whether the published NGFW and threat-protection performance aligns with real usage.
A Mbarara architecture may also need secure connectivity to Kampala, cloud platforms or other countries. IPsec design should account for aggregate encrypted throughput, route exchange, failover and operational monitoring. If the firewall is used as an SD-WAN hub, define link-quality thresholds and application priorities before implementation. If it protects server networks, identify east-west segmentation boundaries and ensure the connected switches can support the chosen interface speeds without introducing bottlenecks.
The FG-3201F’s onboard SSDs can be useful within Fortinet-supported storage functions, but logging strategy should still be based on retention, search and compliance requirements. Organizations may choose centralized analysis for longer retention or broader visibility. Procurement should therefore ask not only for the appliance but also for the FortiGuard service bundle, FortiCare term, management and analytics components where required, transceivers, rails and professional services. The implementation scope should specify migration, testing, documentation and administrator handover. This level of detail helps Mbarara buyers compare quotations on equivalent scope instead of comparing a bare appliance against a complete security solution.
FortiGate 3201F Gulu
FortiGate 3201F Gulu is most suitable where a major network hub needs enterprise or data-center-class firewall capacity. Organizations should verify the requirement carefully because high-end appliances bring not only performance but also design considerations around optics, rack infrastructure, licensing and operations. If a Gulu site is a regional hub serving many branches or critical services, map aggregate traffic and growth. If it is a smaller branch connected to a central data center, a different FortiGate may provide better fit while the 3201F remains at the central aggregation point.
Connectivity planning should include the quality and diversity of available circuits. For critical applications, define what happens when the primary WAN fails, how quickly routes should converge and which services receive priority on a lower-capacity backup link. Security policy should remain consistent during failover. For site-to-site VPN, use clear addressing, tunnel naming and monitoring standards so operations teams can troubleshoot remotely. Remote management itself should be protected with controlled administrator access and strong authentication.
Physical and lifecycle planning is especially important when equipment is distant from the main IT team. Keep configuration backups, network diagrams, port maps, serial information and support details documented. Verify spare optics and replacement processes according to the support agreement rather than making assumptions. Before purchasing FG-3201F for Gulu, confirm the exact bill of materials and service term. Include HA if required, but remember that true resilience also depends on switching, power, WAN and operational procedures. A carefully documented design can be supported more effectively than an oversized appliance installed without a clear topology or recovery plan.
FortiGate 3201F Kenya
FortiGate 3201F Kenya can be evaluated for high-capacity enterprise, data-center and service-provider security where 100GE and 400GE-class network designs are relevant. Nairobi data centers, large corporate hubs, cloud-connected platforms and organizations consolidating branch traffic may need this level of interface and processing capacity. Buyers should compare the exact Fortinet performance profile with their intended security stack, because firewall throughput, IPS, NGFW, threat protection and SSL inspection are measured differently. The correct metric depends on what traffic the appliance will actually inspect.
Kenya deployments can involve local data centers, international cloud services, MPLS or internet-based branch connectivity and multiple carriers. Build a traffic matrix before choosing interfaces and policies. For high availability, map both appliances through independent switching and power paths where the business requirement justifies it. For VPN aggregation, document branch count, encryption requirements and aggregate bandwidth. For data-center segmentation, focus on east-west traffic and the number of security zones rather than only internet speed.
FourTeck’s Kenya regional technology site can provide additional regional context for buyers coordinating a Kenya project. Procurement should request current availability and commercial terms for the exact FG-3201F configuration rather than relying on prices shown by unrelated resellers. Include FortiGuard and FortiCare terms, optics, rails, HA quantity, migration and professional services in the request. If the organization operates in both Kenya and Tanzania, standardizing policy structure, naming, management and documentation can simplify cross-border operations while still allowing each site to use a model sized for its own traffic.
FortiGate 3201F Kuwait
FortiGate 3201F Kuwait targets demanding security roles such as data-center perimeter protection, large enterprise internet edges, high-capacity segmentation and VPN concentration. Buyers should define whether the device will connect to 400GE, 100GE, 50GE or 25GE infrastructure and identify the required optics before finalizing the hardware order. The availability of very high-speed interfaces is valuable only when the surrounding switching, cabling and traffic design can use them effectively.
Kuwait organizations may operate multiple sites, cloud services and hosted applications, creating a mix of north-south and east-west traffic. Segmenting server zones, controlling internet access and protecting remote connectivity can all occur on the same platform, but policy design should remain understandable. Use clear security zones, address objects and naming conventions. Define which traffic requires SSL inspection and how certificates will be deployed. For public services, document NAT, VIPs and upstream dependencies. For remote or site-to-site VPN, define authentication, routing and failover behavior.
Commercially, compare equivalent configurations. One quotation may contain only FG-3201F hardware while another includes a multi-year FortiGuard bundle, FortiCare, optics and deployment. Normalize those differences before comparing price. Buyers can consult the FourTeck Kuwait regional site for broader project coordination. Current stock, lead time, warranty handling and service coverage should be confirmed in the formal quotation. A complete Kuwait request should specify quantity, HA, subscriptions, support term, interfaces, transceivers, rack requirements, migration and any centralized FortiManager or FortiAnalyzer requirement.
FortiGate 3201F Ghana
FortiGate 3201F Ghana is a high-end firewall option for organizations with substantial data-center, enterprise or aggregation workloads. A buyer in Accra or another Ghana location should first identify the security role and traffic profile. If the device is protecting a large internet edge, inspect peak bandwidth and encrypted traffic. If it is segmenting a data center, measure east-west flows and interface requirements. If it is aggregating branches, focus on VPN throughput, routing, session scale and availability. These different roles can produce very different sizing outcomes even when the same appliance is considered.
Network resilience should be designed as a system. The FG-3201F includes redundant AC power supplies and supports high-availability architectures, but the surrounding switches, WAN circuits, power feeds and rack environment must also avoid single points of failure where the business requires continuous operation. High-speed links require compatible transceivers and fiber. Management access should be isolated appropriately, with configuration backup and administrator controls defined before go-live.
For procurement, distinguish mandatory components from optional enhancements. The base appliance, FortiGuard security bundle, FortiCare term, optics, rails, management, analytics and professional services can all affect total project cost. The FourTeck Ghana regional site provides a regional route for broader requirements, while Tanzania-coordinated projects can use the Tanzania contact page. Ask suppliers to state exact SKUs and terms so competing quotations can be compared fairly. For a large security platform, clarity on subscriptions, implementation and acceptance testing is more useful than a low headline hardware price that omits essential project elements.
FortiGate 3201F Nigeria
FortiGate 3201F Nigeria can support high-capacity security architectures for large enterprises, financial platforms, service providers, data centers and organizations with significant branch aggregation. Nigeria’s large multi-site business environments can create complex combinations of internet, private WAN, cloud and data-center traffic. The firewall design should therefore begin with flows and dependencies rather than a single bandwidth number. Identify which applications are business critical, which traffic is encrypted, where inspection occurs and how branches reach centralized or cloud-hosted systems.
For Lagos or other major hubs, the FG-3201F’s high-speed interfaces can align with modern core and data-center switching. Confirm the required 400/200/100/50/25/10GE connections and optics, including any breakout design. If two appliances will operate in HA, validate upstream and downstream topology, state synchronization, routing behavior and maintenance procedures. For organizations with strict logging needs, determine whether onboard storage is sufficient for the intended use or whether centralized analytics and longer retention are required.
Nigeria procurement teams should request exact service and support terms. FortiGuard subscriptions provide security services according to the selected package, while FortiCare terms affect vendor support entitlements. These are separate from implementation work such as migration, policy cleanup, VPN recreation, testing and documentation. The FourTeck Nigeria regional site can support regional coordination. For cross-border enterprises, standard management and policy conventions across Nigeria, Ghana, Kenya, Uganda and Tanzania can reduce operational complexity, but each site’s firewall model should still be sized to local traffic, availability and interface needs.
FortiGate 3201F Seychelles
FortiGate 3201F Seychelles is a specialized high-capacity option that may fit a major data center, large institutional hub, telecom environment or enterprise consolidating substantial security traffic. Because many Seychelles organizations may not require this performance tier, the sizing exercise is particularly important. Compare the actual inspected throughput, VPN load, session scale and interface requirements with the Fortinet portfolio. A smaller platform can be preferable when it meets requirements with suitable headroom, while FG-3201F becomes relevant when high-speed aggregation and enterprise-scale security justify it.
Island connectivity and remote operational support can make resilience planning important. If critical systems depend on external cloud or regional data centers, document primary and backup connectivity, tunnel design, DNS dependencies and failover priorities. If the firewall protects locally hosted services, define DMZ segmentation, inbound publishing and logging. High availability should be evaluated together with spare optics, power, UPS, cooling and access to technical support. Good documentation reduces the impact of distance when troubleshooting is performed remotely.
A Seychelles quotation should list every required component and term: FG-3201F quantity, FortiGuard bundle, FortiCare duration, optical modules, rails, HA requirements, management or analytics, configuration, migration and testing. Confirm logistics and support arrangements in the commercial proposal; do not infer them from another regional page. For organizations operating several Indian Ocean or African sites, a common Fortinet operating model can help standardize policies, VPN templates and reporting. The hardware, however, should remain site-specific so capital expenditure reflects actual traffic and business continuity requirements rather than an unnecessarily uniform appliance choice.
Related FourTeck Resources
A high-end firewall rarely operates alone. Use the Tanzania technology solutions overview to consider switching, servers, Wi-Fi, racks and power alongside the firewall. The Tanzania product catalogue is useful when a project includes related hardware. The services page provides context for installation and lifecycle work, while the FourTeck Tanzania profile gives company context. For regional Fortinet research, see Fortinet products UAE and the FourTeck high-end FortiGate family guide. These links help procurement teams compare the firewall with surrounding infrastructure and related Fortinet tiers rather than evaluating FG-3201F in isolation.
FortiGate 3201F FAQ
What is the difference between FortiGate 3200F and 3201F?
Fortinet’s ordering information identifies FG-3201F as the storage-equipped variant, with two onboard 960GB SSDs. The core high-speed interface and acceleration architecture is shared with the 3200F family. Always order by the exact model SKU.
Does FG-3201F support 400GE?
Yes. Fortinet documents four hardware-accelerated QSFP-DD interfaces capable of 400GE, with support for additional lower high-speed modes depending on the interface and configuration. Optics and breakout requirements should be verified against current Fortinet compatibility information.
Is FortiGate 3201F suitable for a normal branch office?
It is primarily a high-end platform for demanding enterprise and data-center roles. A normal branch often fits a smaller FortiGate. Selection should be based on inspected throughput, sessions, VPN, interfaces, availability and growth rather than choosing the largest model.
What should be included in an FG-3201F quotation?
State appliance quantity, HA requirement, FortiGuard bundle, FortiCare term, transceivers, rails, centralized management or analytics, migration, configuration, testing, documentation and project location. Exact scope makes competing quotations easier to compare.
How should FG-3201F be sized?
Use the expected production workload: peak bandwidth, security profiles, encrypted traffic, VPN, sessions, new connections, interfaces, segmentation and growth. Fortinet publishes different benchmark categories because firewall-only and full security inspection workloads are not equivalent.
Quotation Checklist
Send the current firewall model, peak and expected bandwidth, internet/WAN links, required port speeds, branch and VPN count, security services, SSL-inspection scope, HA requirement, preferred subscription term, logging requirement, rack and power details, migration scope, project country and target timeline. Add a topology diagram where possible.
Decision Recap
Choose FG-3201F when the project genuinely needs high-end FortiGate capacity, 400GE-class connectivity, dense high-speed interfaces and onboard storage. Validate the inspected workload and complete bill of materials before purchase. For smaller workloads, compare alternative FortiGate tiers rather than overprovisioning by default.
Discuss Your FortiGate 3201F Project
FourTeck Tanzania can review your requirement for model fit, high availability, interfaces, licensing, migration and surrounding network infrastructure. Share the intended role and topology so the conversation can focus on a complete project scope instead of a generic appliance price.




Reviews
There are no reviews yet.