
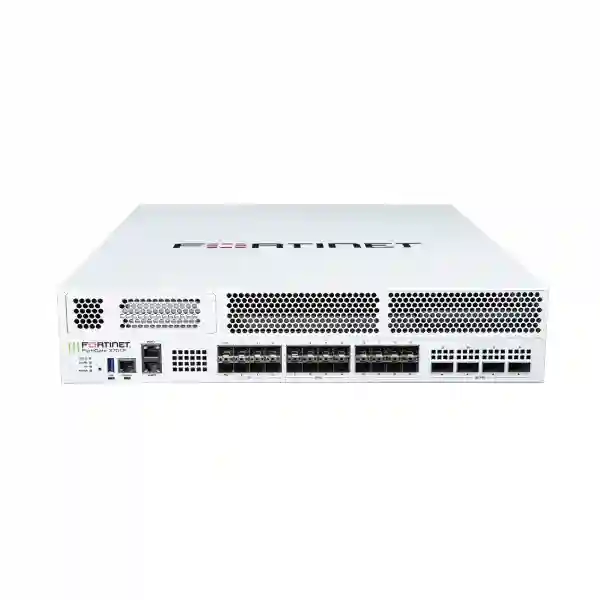
FortiGate 3700F Series Tanzania
FortiGate 3700F Series is built for organizations that need high-throughput security at data-center, core-network and hybrid-cloud boundaries. Fortinet positions the platform for security-driven networking and hybrid mesh firewall architectures, combining FortiOS, FortiGuard security services, purpose-built processing and very high-speed connectivity. For Tanzanian enterprises evaluating a firewall for large internet edges, data centers, service aggregation, multi-cloud connectivity or high-capacity segmentation, the important decision is not simply maximum firewall throughput. A successful design must account for inspected traffic, encrypted sessions, application mix, VPN demand, routing, redundancy, interface speeds, subscription services and expected growth.
Fortinet-published IPS performance for the FortiGate 3700F Series.
Fortinet-published NGFW performance, useful when comparing inspected enterprise traffic requirements.
Fortinet-published threat-protection performance for demanding secured traffic flows.
What the FortiGate 3700F Series is designed to solve
Large networks increasingly place security controls between more than users and the public internet. Data centers may need east-west segmentation, north-south inspection, application publishing, inter-site VPN, cloud connectivity, remote administration and policy enforcement between zones that operate at tens or hundreds of gigabits. FortiGate 3700F Series addresses this class of requirement with a platform designed around high performance and flexible high-speed interfaces. Fortinet also integrates ZTNA enforcement with FortiGate NGFW capabilities, allowing organizations to connect identity and application-access decisions with network security policy.
The series should be sized from the real workload rather than from a headline number. Security architects should document peak and sustained traffic, the proportion of encrypted traffic, inspection profiles, concurrent sessions, connection rates, application publishing, VPN topology, routing protocols, high-availability design and anticipated uplink upgrades. This produces a procurement specification that can be checked against the vendor data sheet and the intended FortiOS release before ordering.
Verified platform highlights
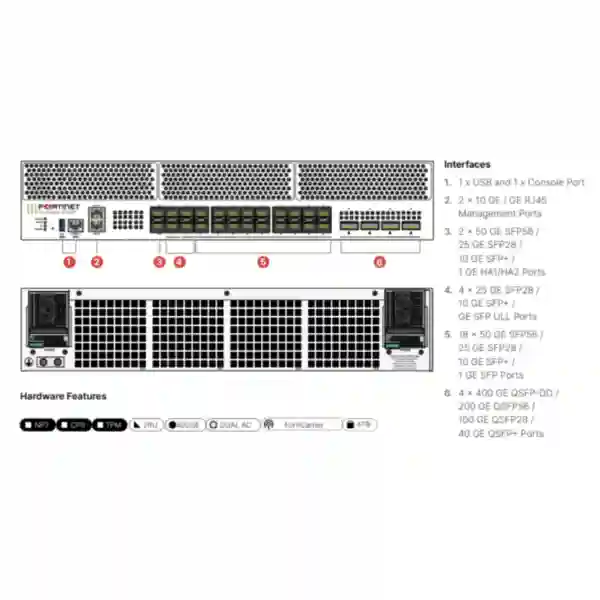
Fortinet publishes the FortiGate 3700F Series with multiple high-speed interface classes including 400 GE QSFP-DD, 200 GE QSFP56, 100 GE QSFP28, 50 GE SFP56, 40 GE QSFP+, 25 GE SFP28, 10 GE SFP+ and 10 GE/GE RJ45 connectivity. Exact port counts and hardware differences must be checked for the chosen model and current official data sheet. The family is powered by FortiOS and works with FortiGuard AI-powered security services. Fortinet describes the platform as suitable for hybrid IT and data-center security, with integrated ZTNA enforcement and Security Fabric integration.
For procurement, those capabilities translate into several practical questions. Confirm whether existing core and aggregation switches support the required optics and breakout strategy. Confirm transceiver type, fiber standard and distance. Determine whether links will run as routed interfaces, VLAN trunks, link aggregates or redundant paths. Decide which security services must be licensed and whether centralized management and analytics are part of the architecture. A high-performance firewall is most valuable when its interfaces, policy design and operational tooling are aligned with the network around it.

FortiOS, security services and operational planning
FortiOS brings firewall policy, routing, VPN, SD-WAN, segmentation, application control and security functions into one operating environment. Organizations considering a 3700F deployment should plan the operating model at the same time as the hardware. That means defining who administers policy, how changes are approved, where logs are retained, how configuration backups are protected, how firmware upgrades are tested and how alerts are handled. For multi-firewall estates, centralized management and analytics can become as important as appliance performance because consistency reduces configuration drift.
FortiGuard services can extend inspection and threat-protection functions, but the exact subscription bundle should match the organization’s risk profile and required features. Buyers should avoid assuming that every security service is permanently included with hardware. Request a quotation that clearly separates appliance, support, subscriptions, optics, accessories and any professional services. This makes renewal obligations visible and helps finance teams compare total lifecycle cost rather than only initial purchase price.
High availability and resilient design
A firewall serving a major data center or enterprise edge can become a critical dependency, so resilience planning should cover more than purchasing two appliances. The architecture should consider HA mode, physical path diversity, switch redundancy, power feeds, rack placement, upstream carrier diversity and the behavior of dynamic routing during a failure. Maintenance procedures also matter. A redundant pair is useful when administrators can upgrade, test and recover the environment without introducing avoidable outages.
Before deployment, document interface addressing, VLANs, routing adjacencies, VPN peers, NAT rules, published services, management networks and monitoring dependencies. Define a rollback plan for migration from an existing firewall. If the project replaces a lower-capacity platform, review old policies rather than automatically copying years of accumulated rules. Migration is an opportunity to remove obsolete objects, tighten access and improve naming standards.
FortiGate 3700F Series Tanzania
In Tanzania, the FortiGate 3700F Series is most relevant to organizations whose security requirements exceed the scale of a typical branch firewall. Potential environments include data centers, large enterprise headquarters, financial platforms, telecom and service-provider networks, major public-sector infrastructure, cloud-connected estates and businesses consolidating many high-bandwidth services behind a common security layer. The purchasing discussion should start with measured traffic and architecture. Internet capacity alone does not describe the load because inter-zone and data-center traffic may be substantially higher than WAN bandwidth.
Tanzanian buyers should prepare a technical requirement that includes current and planned uplinks, number of security zones, public services, remote-access demand, branch VPN topology, routing protocols, inspection policies and availability objectives. If 100GE, 200GE or 400GE interfaces are part of the design, the surrounding switching and optical infrastructure should be validated before the firewall is ordered. Rack space, cooling, redundant power and UPS strategy should also be reviewed as part of the same project.
For regulated or security-sensitive workloads, teams should determine where logs will be stored, who can administer the platform, how privileged access is controlled and how configuration changes are recorded. The firewall can provide powerful enforcement, but governance remains an organizational responsibility. A well-designed deployment combines the FortiGate platform with documented operating procedures, monitoring and regular policy review.
FourTeck Tanzania can be approached for product-selection and quotation discussions. When requesting a quote, include the exact series, preferred model if known, quantity, required subscriptions, support term, interface and optic requirements, HA expectations and target deployment environment. Providing these details reduces ambiguity and makes it easier to distinguish appliance cost from licensing and integration components.
FortiGate 3700F Series Dar es Salaam
Dar es Salaam hosts a dense concentration of corporate, financial, logistics, hospitality and technology operations, making high-capacity perimeter and data-center security a relevant design concern for larger organizations. A FortiGate 3700F Series evaluation in Dar es Salaam should begin with the topology: identify primary and secondary internet circuits, data-center interconnects, cloud paths, branch tunnels, public application zones and internal segmentation boundaries. This shows where inspection capacity is actually required.
Organizations upgrading from lower-speed firewalls should pay particular attention to link transitions. Moving to 25GE, 40GE, 100GE or faster connectivity can require new optics, fiber, switch modules and cabling standards. Firewall procurement should therefore be coordinated with core-network planning. If the appliance is installed in an HA pair, both physical paths and power arrangements should avoid a common point of failure.
Security policy migration also deserves time. Rules accumulated over many years may contain unused services, duplicate objects and temporary exceptions that were never removed. A data-center refresh is a useful moment to classify applications, document business owners and rebuild policy around current requirements. Logging and alerting should be tested before cutover so the operations team can identify abnormal traffic immediately.
For a Dar es Salaam quotation, provide expected security subscriptions, support duration, required high-speed interfaces, optics, rack and power constraints, VPN requirements and whether centralized FortiManager or FortiAnalyzer capabilities are part of the design. These inputs create a more complete bill of materials and reduce late additions during deployment.
FortiGate 3700F Series Mwanza
For large organizations in Mwanza, a 3700F-class firewall may be considered where regional operations, data-center workloads or consolidated branch connectivity create substantial throughput and security demands. The first step is to separate actual requirements from future aspirations. Measure current traffic, identify growth projects and determine which flows need full security inspection. This prevents both undersizing and unnecessary overprovisioning.
Multi-site organizations may use the platform as a hub for VPN and routed connectivity. In that role, tunnel count, encrypted throughput, routing scale and failover behavior become important. Administrators should document how branch traffic reaches shared applications, internet services and cloud platforms, then decide which flows should traverse the central security stack. Where direct internet access is used at branches, central policy and logging strategy should still be considered.
Environmental planning matters for high-end network equipment. Rack organization, cooling, clean power and UPS capacity should be assessed rather than assumed. Fiber routes and transceiver compatibility should be confirmed for high-speed interfaces, especially when the firewall connects to separate core switches or data halls. Spare optics and documented cabling can reduce troubleshooting time.
A Mwanza procurement request should state the business role of the firewall, existing network vendors, uplink speeds, HA requirements, security services and expected support term. If migration services are needed, include current firewall model, approximate rule count, VPN peers and change-window constraints. This gives suppliers enough context to prepare a solution-oriented response rather than a bare appliance quote.
FortiGate 3700F Series Arusha
Arusha organizations with large hospitality, institutional, enterprise or regional operations may need security platforms capable of handling many network segments and high-bandwidth services. FortiGate 3700F Series can be evaluated for data-center and core security roles where ordinary branch appliances are not sufficient. The key is to connect technical sizing to actual applications, users, guest networks, servers, cloud services and inter-site traffic.
A design serving hospitality or campus-style environments may contain many VLANs and trust zones. Guest access, staff systems, payment environments, building systems, cameras, voice, servers and administrative networks should not automatically share unrestricted paths. Segmentation policy can reduce unnecessary lateral access, while the firewall provides a central point for inspection and logging where architecture requires it.
High availability should be tested as an operational process. Teams should know how sessions behave during failover, how routing reconverges and how maintenance is performed. Monitoring should cover appliance health, interface state, resource utilization and security events. Configuration backups should be protected and recoverable, and administrators should use controlled privileged access.
When requesting a FortiGate 3700F Series quote for Arusha, identify whether the project is a new build, replacement or capacity upgrade. Include internet and internal link speeds, interface media, VPN needs, desired subscriptions and any requirement for centralized management. This helps align hardware, licensing and deployment scope before commercial approval.
FortiGate 3700F Series Dodoma
Dodoma enterprises and institutions considering high-end firewall infrastructure should define availability, governance and lifecycle requirements alongside performance. FortiGate 3700F Series is designed for demanding environments, but the surrounding operational controls determine how effectively the platform supports a critical network. Procurement documents should therefore include security objectives, network topology and support expectations rather than only a model name.
Where applications are hosted internally, the firewall may protect public-facing services, administrative zones and connections between infrastructure tiers. Policy should follow least-privilege principles and be mapped to business owners. Where cloud services are involved, architects should decide which traffic returns through the data center and which uses direct cloud paths. That decision affects throughput, latency and inspection design.
Large projects also benefit from formal change control. Firewall rules can affect many departments, so requests should record purpose, source, destination, service, owner and expiry where appropriate. Regular review helps remove temporary access that is no longer required. Centralized logging can support troubleshooting and security investigations when retention is planned appropriately.
For Dodoma quotation planning, include the required appliance quantity, HA topology, subscription bundle, support period, interface speeds and optics. State whether migration, installation, configuration, testing or documentation is expected. A complete scope makes technical and commercial comparison more meaningful.
FortiGate 3700F Series UAE
Organizations in the UAE often operate high-bandwidth data centers, multi-cloud platforms and regional network hubs where 100GE and faster connectivity is increasingly relevant. FortiGate 3700F Series can fit designs requiring high-performance threat inspection, segmentation, VPN and hybrid connectivity. Buyers should map traffic between internet edges, private clouds, public clouds, colocation facilities and branch networks before selecting interface and performance requirements.
The presence of multiple 400GE-capable interface options in the series is significant for modern core designs, but the complete link must support the chosen speed and optic. Verify switch compatibility, transceiver standards, fiber type and distance. Where breakout connectivity is planned, validate supported combinations using current Fortinet and switching-vendor documentation.
UAE deployments frequently emphasize resilience and continuous service. HA firewalls should connect through redundant switching and power domains where architecture permits. Carrier diversity, BGP behavior, cloud connectivity and disaster-recovery routing should be included in failover tests. Operational teams also need clear monitoring, backup and upgrade procedures.
For regional FourTeck resources, buyers can review Fortinet UAE solutions for Fortinet-focused regional context and FourTeck UAE for broader infrastructure requirements. Commercial requests should specify licensing, support, optics and professional-service expectations.
FortiGate 3700F Series Uganda
Ugandan organizations evaluating the FortiGate 3700F Series are typically considering a high-capacity security role rather than a standard office edge. Relevant scenarios can include central data centers, large institutional networks, service aggregation and enterprise hubs connecting many sites. A requirements workshop should quantify internal and external traffic separately because data-center east-west flows can be much larger than internet bandwidth.
If the firewall will terminate many IPsec tunnels, document branch count, encryption requirements and routing design. If it protects server networks, list application zones and trust relationships. If it sits at an internet edge, record carrier handoffs, public address requirements and DDoS responsibilities. Each role drives a different policy and interface design even when the same hardware platform is used.
Subscription planning should be explicit. Determine which FortiGuard security services are required and how renewals will be budgeted. Support entitlement and firmware lifecycle should be considered before production deployment. Central management and analytics can improve consistency when several FortiGate appliances are deployed across the organization.
Uganda customers can also review FourTeck Uganda for regional technology context. A quote request should include topology, link speeds, HA requirements, security services, support duration and migration scope so the proposal reflects the real deployment.
FortiGate 3700F Series Kampala
Kampala-based enterprises with centralized IT operations may use a high-end firewall as the policy and inspection point for headquarters, data-center and branch connectivity. Before selecting the 3700F Series, teams should baseline traffic during normal and peak periods. Application growth, cloud migration and planned carrier upgrades should be added to the sizing model so the platform is evaluated against future as well as current demand.
Network architecture should prevent the firewall from becoming an accidental bottleneck. Core-switch uplinks, link aggregation, routing adjacencies and VLAN design need to match the intended security zones. If high-speed ports are used, optics and fiber infrastructure must be validated end to end. Redundant paths should be physically and logically tested.
Security operations teams should define alert ownership and escalation before go-live. A firewall can generate extensive telemetry, but logs create value only when retention, review and incident workflows are established. Administrative access should be limited, authenticated strongly and separated from ordinary user networks where practical.
For Kampala procurement, prepare a bill-of-material requirements sheet covering appliance quantity, support, FortiGuard subscriptions, transceivers, cables and any centralized management components. Include migration and testing services if required. This makes lifecycle costs and responsibilities easier to understand.
FortiGate 3700F Series Arua
Arua deployments should be justified by workload and network role. For organizations operating a regional hub, critical service platform or large consolidated environment, the FortiGate 3700F Series may provide capacity for demanding inspection and connectivity. For smaller sites, architects should first determine whether a lower FortiGate model is more proportionate. Correct sizing protects budget while preserving security objectives.
Connectivity resilience may be particularly important for sites dependent on multiple WAN options. The firewall design should document primary and backup paths, routing priorities, VPN behavior and the applications that must remain available during an outage. SD-WAN functions can support path selection, but business policies and link characteristics still need to be defined.
Local site conditions should also be included in planning. Reliable power, UPS capacity, rack cooling and secure equipment access contribute to system availability. Remote administration procedures should be designed so support personnel can troubleshoot safely without exposing management interfaces to unnecessary risk.
When requesting a quote for Arua, include the network diagram if available, current bandwidth, future upgrades, required security services and expected support term. If the firewall will be managed from another city or country, specify centralized management and logging needs. Clear documentation helps turn a high-end appliance into a maintainable platform.
FortiGate 3700F Series Mbarara
Mbarara organizations planning large network consolidation should evaluate the FortiGate 3700F Series against measurable requirements such as inspected throughput, VPN traffic, session scale and interface speed. High-end firewall purchases can have long lifecycle implications, so growth in users, branches, cloud applications and bandwidth should be included in the design horizon.
Segmentation is a common reason to introduce a stronger core firewall. Server networks, user networks, guest access, operational technology and management systems can be separated into zones with explicit policy between them. The exact segmentation model should reflect business processes so security does not create unnecessary operational friction.
For migrations, teams should inventory existing objects, NAT policies, routes and VPNs. Dependencies that are not documented can cause cutover problems, particularly when legacy applications use hard-coded addresses or unusual ports. Testing should include application owners and a rollback plan. After migration, temporary rules should be reviewed and removed.
A Mbarara quote should specify whether the requirement is appliance-only or a complete project including subscriptions, optics, installation, migration and documentation. This distinction matters when comparing offers because professional services and recurring licenses can materially change the total project scope.
FortiGate 3700F Series Gulu
For Gulu enterprises and institutions, a FortiGate 3700F Series project should begin with a capacity and risk assessment. The platform is positioned for demanding networks, so buyers should identify which applications and services justify high-performance inspection. Internet edge, data-center segmentation, regional aggregation and large VPN hub roles each have different sizing inputs.
Where remote branches depend on central services, routing resilience and VPN design are central to availability. Administrators should test what happens when an ISP fails, a firewall node is unavailable or a route changes. Critical applications should have documented dependencies so recovery does not rely on trial and error during an incident.
Operational readiness includes firmware management, configuration backup, monitoring, log retention and administrator training. Security subscriptions should be tracked with renewal dates and ownership. Rule reviews should be scheduled because policy tends to grow over time as projects and temporary exceptions are added.
For procurement in Gulu, state the expected role, interfaces, security profiles, HA design and support needs. Include environmental requirements such as rack and power planning if the deployment is part of a new facility. A complete technical brief supports more accurate commercial and implementation planning.
FortiGate 3700F Series Kenya
Kenyan data centers, large enterprises and regional network hubs may consider FortiGate 3700F Series where high-speed inspection and dense connectivity are required. The design should account for cloud adoption, colocation links, internet transit, private connectivity and internal segmentation. Fortinet’s published performance figures provide a reference point, but sizing should always reflect enabled services and real traffic characteristics.
High-speed interfaces can simplify consolidation when multiple links are aggregated into a security layer, yet they also raise design questions. Confirm whether core switches, optics and fiber plant support the selected speeds. Determine whether redundant links will use routing, link aggregation or separate failure domains. Validate MTU and application requirements where large data-center frames or encapsulation technologies are used.
Security architecture should define zones around application sensitivity and administrative responsibility. Public services, databases, management systems and user networks often need different policies. ZTNA capabilities may complement application access strategies, while VPN remains important for site connectivity and specific remote-access cases.
Kenya customers can review FourTeck Kenya for related regional infrastructure. Quote requests should include support and subscription terms so recurring costs are visible alongside the hardware purchase.
FortiGate 3700F Series Kuwait
Kuwait organizations operating large data centers, energy environments, financial platforms or multi-site enterprises may evaluate the 3700F Series for high-performance security. Capacity planning should include peak encrypted traffic, data-center east-west flows, internet edge requirements and cloud connectivity. Interface design is particularly important when integrating with high-speed core networks.
Environmental and availability planning should include redundant power, cooling and secure rack placement. HA pairs should connect to redundant switching where possible, and maintenance procedures should be tested. A resilient firewall pair cannot compensate for a single upstream switch, carrier or power dependency that remains unaddressed.
Security services and support should be treated as lifecycle components. Determine which FortiGuard subscriptions are required, who owns renewal tracking and how firmware upgrades are approved. Central logging and management can reduce operational inconsistency across larger estates.
For Kuwait procurement, review FourTeck Kuwait for regional technology context. Provide a topology and interface schedule with the quotation request, especially where high-speed optics and migration services are required.
FortiGate 3700F Series Ghana
Ghanaian enterprises considering the FortiGate 3700F Series should focus on the business services that depend on the firewall. Data-center applications, internet services, branch VPNs and cloud connections may all share the platform, making change control and capacity planning essential. The firewall should be sized for the security features that will actually be enabled rather than for uninspected traffic alone.
Organizations with several branches should document hub-and-spoke and direct-site traffic requirements. Routing and SD-WAN policy can influence where traffic is inspected and how quickly applications recover when links fail. If public services are hosted behind the firewall, NAT and application-publishing rules should be documented and reviewed with application owners.
Operational processes should include secure administration, configuration backup, monitoring and log review. When security events are detected, teams need an escalation path and access to enough retained telemetry for investigation. The value of advanced security features depends on these operational practices.
For a Ghana quotation, specify required interfaces, subscriptions, support term, HA topology and implementation scope. If centralized management or analytics is planned, include it in the initial architecture rather than adding it only after operational complexity grows.
FortiGate 3700F Series Nigeria
Nigeria’s large enterprise, financial, telecom and data-center environments can generate substantial security and connectivity demands. FortiGate 3700F Series may suit architectures that need high-throughput NGFW functions and very high-speed interfaces. Sizing should be driven by measured traffic, inspection requirements, session behavior and future network expansion rather than by organization size alone.
Where multiple carriers and cloud connections converge, routing design is critical. Teams should define BGP or other routing behavior, failover priorities, asymmetric traffic considerations and security policy across each path. For data-center segmentation, application dependencies should be mapped before enforcement so policy can be restrictive without disrupting legitimate services.
Large firewall estates benefit from standardized naming, objects, policy templates and centralized administration. This reduces configuration drift between sites and makes audits easier. Renewal planning should include FortiGuard services and support, while hardware lifecycle plans should consider expected bandwidth growth.
Nigeria buyers can use FourTeck Nigeria for regional technology information. A procurement package should distinguish appliance, licenses, optics, professional services and ongoing support so commercial comparisons remain clear.
FortiGate 3700F Series Seychelles
Seychelles organizations with centralized critical infrastructure, hospitality groups, financial services or regional data requirements may evaluate high-end firewall platforms when network consolidation and resilience are priorities. A FortiGate 3700F Series design should be justified through traffic measurements, application criticality and connectivity architecture. Not every site requires this class of appliance, so centralization strategy matters.
Island connectivity can make WAN resilience a significant design consideration. Multiple links may have different latency, capacity and cost characteristics. Security policy and routing should account for these differences, particularly for cloud applications, backups and VPN traffic. Where a central firewall serves multiple properties or sites, the impact of an outage should be included in the HA design.
Remote management must be secure and reliable. Administrators should use controlled management paths, strong authentication and logging. Configuration backups and recovery procedures should be stored safely. If local technical access is limited, clear documentation, spare optics and tested out-of-band procedures can improve recoverability.
A Seychelles quotation should include the target topology, link speeds, HA requirements, security subscriptions, support duration and any remote or onsite implementation expectations. This enables a supplier to identify dependencies instead of treating the project as a single-box purchase.
Related Tanzania infrastructure planning
Quotation checklist for FortiGate 3700F Series
A useful quotation request should state the required model and quantity; whether an HA pair is needed; desired FortiGuard security bundle; support term; current and future WAN or data-center link speeds; required 10GE, 25GE, 40GE, 50GE, 100GE, 200GE or 400GE interfaces; transceiver and fiber requirements; number and type of VPN connections; routing protocols; centralized management or analytics needs; rack and power constraints; migration scope; configuration expectations; documentation; testing; and target implementation schedule. If exact technical details are not yet known, provide a current network diagram and business objective so sizing questions can be resolved before ordering.
Frequently asked questions
What performance does Fortinet publish for the FortiGate 3700F Series?
Fortinet’s current series data sheet publishes 86 Gbps IPS, 80 Gbps NGFW and 75 Gbps threat protection performance. These are vendor test figures and should be interpreted with the test methodology and intended configuration in mind. Real deployments vary with traffic profile, enabled features, packet size, encryption and policy design.
Does the FortiGate 3700F Series support 400GE connectivity?
Fortinet lists multiple 400 GE QSFP-DD interfaces among the series interface options. Exact port counts, supported optics and breakout combinations should be verified for the selected model and current Fortinet documentation before purchase.
Is FortiGate 3700F suitable for a data center?
Fortinet positions the series for high-performance data-center and hybrid IT security. Suitability for a specific data center depends on required throughput, inspection services, interface architecture, routing, availability, VPN scale and operational requirements.
Should I buy one appliance or an HA pair?
That depends on the organization’s availability objectives. For critical environments, buyers commonly evaluate redundancy, but a complete HA design also requires resilient switching, power, carrier paths and tested failover procedures. The architecture should be reviewed before ordering.
What information is needed for a Tanzania quote?
Provide model or series, quantity, desired support and FortiGuard subscriptions, HA requirement, current and planned bandwidth, high-speed interface and optic needs, VPN and routing requirements, migration expectations and deployment location. A network diagram is helpful for complex projects.
Decision recap
FortiGate 3700F Series is a high-end security platform for organizations that need substantial inspected throughput, dense high-speed connectivity and FortiOS-based security controls. The published performance and interface capabilities make it relevant to demanding data-center, hybrid IT and enterprise-core environments. The correct purchase decision depends on validated workload, security subscriptions, HA design, optics, surrounding switching, support and lifecycle requirements. Treat the firewall as part of an architecture, not as an isolated appliance.
Discuss your FortiGate 3700F Series requirement
Send FourTeck Tanzania your expected throughput, network topology, interface speeds, security-service requirements and desired support term. If you are replacing an existing firewall, include the current model, major VPN dependencies and planned bandwidth upgrades. This information supports a more accurate sizing and quotation discussion.




Reviews
There are no reviews yet.