
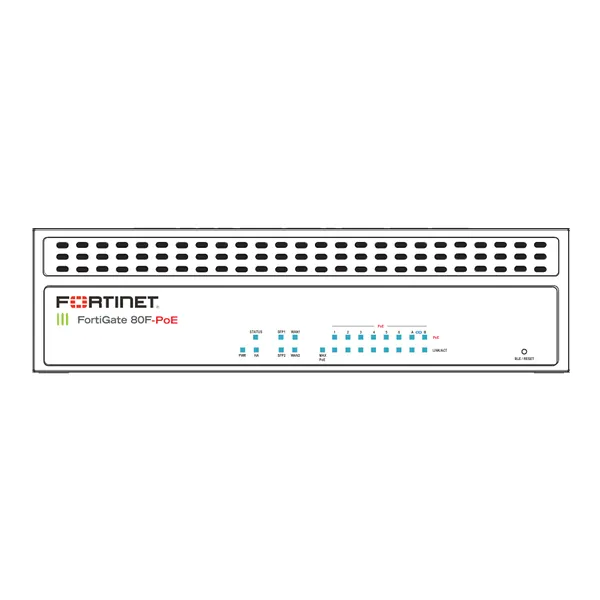
FortiGate 80F PoE (FG-80F-POE) Tanzania
FortiGate 80F PoE is designed for organisations that want branch firewalling, secure SD-WAN and powered Ethernet connectivity in a compact FortiGate platform. For Tanzanian offices, retail sites, professional environments, hospitality properties, education facilities and distributed operations, the FG-80F-POE can simplify the network edge by combining security policy enforcement with PoE/+ interfaces for compatible edge devices. The design is particularly useful when a project requires a capable security gateway while reducing dependence on a separate PoE switch for a modest number of powered devices.
FortiGate 80F PoE overview
The FortiGate 80F family is positioned by Fortinet as a converged next-generation firewall and SD-WAN platform for distributed enterprise sites. The FG-80F-POE variant adds integrated powered Ethernet connectivity. Official Fortinet data identifies six GE RJ45 PoE/+ internal ports and two GE RJ45 PoE/+ FortiLink ports, for eight powered interfaces in total. The appliance also provides two GE RJ45/SFP shared-media WAN interfaces, allowing a project designer to choose copper or supported SFP connectivity according to the WAN handoff and deployment plan.
The total available PoE power budget is 96 W, with maximum loading of 30 W on each PoE/+ port under 802.3at. This matters during design: eight physical PoE-capable ports do not mean that eight devices can each draw the maximum simultaneously. A correct bill of materials should total the expected power requirement of connected access points, phones, cameras or other compatible devices and retain sensible headroom. For larger powered-device counts, a dedicated PoE switch may remain the better architecture.
Security edge
Use FortiGate policy, VPN, application-aware controls and subscribed FortiGuard security services according to the selected service package and FortiOS configuration.
WAN consolidation
Secure SD-WAN capabilities can support branch connectivity strategies that use multiple WAN links, policy-based path selection and centralised security controls.
PoE consolidation
Eight GE PoE/+ interfaces and a 96 W aggregate budget can power a carefully sized set of compatible network edge devices without a separate PoE switch.
Verified FG-80F-POE hardware details
| PoE/+ interfaces | 6 × GE RJ45 PoE/+ internal + 2 × GE RJ45 PoE/+ FortiLink |
| Total PoE budget | 96 W |
| Per-port PoE/+ maximum | 30 W, 802.3at |
| Shared-media WAN | 2 × GE RJ45/SFP |
| Dimensions | 60 × 216 × 178 mm |
| Weight | 1.4 kg |
| Operating temperature | 0°C to 40°C |
| Mounting/form factor | Desktop / wall mount / rack tray |
Where the FortiGate 80F PoE fits
A good FG-80F-POE deployment begins with workload rather than model name. Internet bandwidth, inspected traffic, VPN usage, enabled FortiGuard services, number of users, application mix, WAN links and future growth all influence firewall sizing. PoE requirements add another dimension: count the powered endpoints, confirm their standards and expected wattage, and decide whether they should connect directly to the firewall or through managed access switching.
The appliance can be attractive for a compact branch where the firewall sits close to a handful of access points, phones or other PoE devices. It can also work as the security and SD-WAN edge while FortiSwitch or another appropriate switching layer handles broader LAN distribution. FortiLink ports are particularly relevant to designs that use Fortinet switching integration. The right topology depends on segmentation, port density, redundancy, cabling distance and operational requirements.
FortiGate 80F PoE Tanzania
For organisations evaluating the FortiGate 80F PoE in Tanzania, procurement should connect firewall selection to the actual network design. A branch with fibre or fixed wireless internet, cloud applications, remote access users, IP telephony and wireless access points has different traffic and resilience requirements from a small office that mainly uses email and web applications. Start by documenting internet bandwidth, expected growth, the number of VLANs, site-to-site VPN requirements, remote-access needs and the security services that will be enabled. This creates a more defensible sizing decision than selecting a firewall only by user count.
PoE planning is equally important. The FG-80F-POE offers eight GE PoE/+ ports but a 96 W aggregate budget. A Tanzania deployment that intends to power access points, IP phones and cameras directly should list each device and its expected power requirement. Where the total approaches the appliance budget, or where many additional wired endpoints are needed, use dedicated access switching rather than forcing all connectivity through the firewall. This also creates a clearer path for future expansion and structured VLAN design.
WAN resilience is another common buying consideration. FortiGate secure SD-WAN can be relevant where a site has more than one internet service or needs application-aware WAN policies. The exact configuration should reflect available providers, addressing, upstream equipment and business continuity objectives. For VPN-connected branches, document peer sites, required subnets and routing expectations before implementation. For cloud-heavy businesses, consider how inspection settings and subscribed security services affect effective throughput.
FourTeck Tanzania’s technology enquiry page explains the useful information to include for firewall projects: internet speed, users, VPN requirements, branch connectivity and expected security services. Supplying these details with the FG-80F-POE quantity makes a quotation discussion more productive. Buyers comparing wider Fortinet options can also review the FourTeck Fortinet specialist resource for broader solution context.
FortiGate 80F PoE (FG-80F-POE) Dar es Salaam
Dar es Salaam businesses often need network security to coexist with dense office connectivity, cloud services, wireless coverage and multiple operational systems. When evaluating FG-80F-POE for a Dar es Salaam office, showroom, professional-services site, retail environment or branch, map the firewall to the internet circuits and LAN architecture first. Identify primary and backup WAN services, public IP requirements, VPN peers, cloud applications and any inbound services that need controlled publication. This gives the security policy and SD-WAN design a concrete foundation.
The integrated PoE/+ ports can be useful in compact sites, but they should be treated as a finite power resource. With 96 W available across the PoE-capable interfaces, the bill of materials should include the power draw of each intended endpoint. A few compatible access points and IP phones may fit comfortably; a larger camera or wireless deployment may justify a separate PoE switch. Keeping the firewall focused on security and WAN routing while access switches handle scale can make expansion easier.
Environmental planning also matters. The official operating range is 0°C to 40°C, so equipment-room ventilation, dust control, stable power and UPS planning deserve attention. Avoid treating a communications cabinet as an afterthought. The firewall, ISP equipment, switches and any local server or NVR equipment need adequate power and cooling. If redundant power is part of the requirement, discuss the supported external power-adapter approach and upstream UPS design as part of the project.
For quotation preparation in Dar es Salaam, provide the exact FG-80F-POE model, quantity, preferred FortiGuard/FortiCare term if known, WAN bandwidth, number of branches, VPN needs, and the PoE endpoints you expect to attach. FourTeck’s Tanzania contact page identifies Dar es Salaam contact details and accepts product-selection and quotation requests. A complete requirement helps distinguish a hardware-only request from a security subscription, implementation and network-integration project.
FortiGate 80F PoE (FG-80F-POE) Mwanza
For Mwanza organisations, the FG-80F-POE can be evaluated as a branch-security platform where internet access, inter-site connectivity and a modest set of powered network devices need to converge. The first design question is not whether the firewall has enough physical ports; it is whether the security performance, WAN topology and subscription choice fit the workload. Record normal and peak internet utilisation, critical SaaS applications, site-to-site VPN traffic, remote users and expected security inspection. This information guides a more realistic architecture.
A Mwanza branch that uses wireless access points or IP phones can benefit from integrated PoE, particularly when the network is intentionally compact. However, powered endpoints should be budgeted by watts and by port. The 96 W total limit is shared, while each PoE/+ interface supports up to 30 W under 802.3at. Where the site is likely to add cameras, additional access points or many phones, dedicated PoE switching can preserve growth capacity and simplify cable aggregation.
Branch connectivity planning should include what happens when the primary WAN degrades or fails. If two suitable internet links are available, FortiGate secure SD-WAN policies can form part of a resilience design, but successful failover depends on correct health checks, routing, NAT, application policy and upstream service characteristics. Test failover with the applications that actually matter to the business rather than assuming that a second link automatically provides seamless continuity.
Procurement teams should also separate hardware from recurring security services. FortiGuard subscriptions enable service-dependent security functions, while FortiCare provides support entitlements according to the selected offering. Ask for a quote that clearly identifies the appliance and subscription term so renewal planning is visible from the start. Include implementation expectations, existing firewall details and any required migration window to reduce ambiguity during project scoping.
FortiGate 80F PoE (FG-80F-POE) Arusha
Arusha deployments may range from business offices and hospitality-related operations to distributed organisations that need secure connectivity to other sites. FG-80F-POE can suit projects where a compact firewall must combine secure WAN connectivity with PoE-capable LAN interfaces. Begin with application and availability requirements: reservation or ERP systems, voice, cloud collaboration, payment services, guest or staff networks and VPN connectivity may have different policy and continuity needs.
Network segmentation is particularly useful when one physical site supports several operational groups. Staff devices, guest Wi-Fi, voice, cameras and management interfaces should not automatically share the same trust level. FortiGate policies and VLAN-based architecture can support separation, while appropriate managed switching and access points extend that design across the site. The FG-80F-POE’s FortiLink PoE/+ interfaces can be relevant when the design incorporates Fortinet switching, but compatibility and topology should be confirmed for the exact project.
For wireless deployments, do not size PoE only by the number of access points. Confirm each AP model’s power requirement, radio design and intended placement. Wireless capacity depends on coverage, client density, channel planning and building characteristics; the firewall does not replace an RF design. If access points are distributed beyond practical direct cabling to the firewall, a properly placed PoE access switch is usually more logical.
Arusha buyers requesting FG-80F-POE should provide the current internet services, number of users and devices, VLAN plan if available, branch/VPN requirements, and the intended PoE endpoints. The Tanzania contact page lists Arusha contact details and supports technology enquiries. For projects extending into East Africa, the FourTeck Uganda site and FourTeck Kenya site provide regional network context without implying that every product or service has identical availability in each market.
FortiGate 80F PoE (FG-80F-POE) Dodoma
Dodoma organisations evaluating FortiGate 80F PoE should frame the purchase around security policy, WAN continuity and manageable branch operations. The appliance’s combination of FortiOS, secure SD-WAN and integrated PoE/+ interfaces can reduce device count in compact networks, but consolidation should not eliminate necessary design discipline. Document users, endpoints, applications, bandwidth, VPNs, segmentation and powered-device requirements before finalising the hardware and subscriptions.
For offices with IP phones and wireless access points, the 96 W PoE budget can reduce reliance on a separate small PoE switch when the endpoint count and wattage fit. The key is to reserve headroom. Endpoint power consumption can vary, and future additions are easier when the design is not operating at the limit from day one. Where a building has multiple floors, distant endpoints or many network drops, structured access switching is normally more scalable than home-running everything to the firewall.
Security-service selection should reflect the organisation’s risk and application profile. IPS, anti-malware, web and DNS security, application controls and other FortiGuard capabilities depend on the selected subscription and configuration. Buyers should ask for the exact service bundle and term to be identified in the quotation rather than treating “licensed firewall” as a sufficiently precise description. Renewal ownership and expiry monitoring should be assigned internally as part of operational planning.
The FourTeck Tanzania contact page identifies a Dodoma office contact and advises firewall buyers to share internet speed, VPN use, branch connectivity and expected security services. Add migration information if an existing firewall is being replaced: current subnets, VLANs, NAT rules, site-to-site tunnels, remote-access users and any published services. This can reveal dependencies before the change window and make the eventual implementation plan more complete.
FortiGate 80F PoE (FG-80F-POE) UAE
UAE buyers often compare the FG-80F-POE for branch offices, retail locations, professional environments and distributed enterprises that want Fortinet security with integrated PoE. The same sizing principles apply: evaluate inspected traffic rather than raw ISP speed alone, identify VPN and SD-WAN requirements, and calculate the powered-device load. The eight PoE/+ ports are useful, but the 96 W aggregate budget should be checked against the intended endpoint mix.
For multi-branch UAE networks, secure SD-WAN can help consolidate routing and security policy at the edge. A design may use multiple broadband, leased or other WAN services depending on the site, but link diversity should be assessed realistically. Two circuits that share the same upstream dependency may not provide the resilience expected. Define which applications require preferred paths, what constitutes link failure, and how voice or business-critical sessions should behave during impairment.
Fortinet ecosystem integration is another purchasing consideration. FortiGate can operate with FortiSwitch, FortiAP and Fortinet management/security components, but the project should confirm supported models, software versions and desired management architecture. PoE-capable firewall ports can power selected endpoints directly, while larger deployments can use dedicated FortiSwitch access layers. This allows the security gateway to remain central without constraining port density.
For UAE-focused Fortinet requirements, consult the FourTeck Fortinet UAE resource alongside the Tanzania enquiry channel when planning a cross-border project. Request a quote with the exact FG-80F-POE model, subscription term, quantity, required accessories and implementation scope. Do not assume stock, lead time or service coverage until these are confirmed for the specific order.
FortiGate 80F PoE (FG-80F-POE) Uganda
Uganda organisations can assess FG-80F-POE for secure branch connectivity where firewalling, VPN, SD-WAN and limited PoE edge connectivity need to work together. For a cross-border organisation with Tanzania and Uganda sites, standardising on a common firewall family may simplify policy concepts and operations, but each site should still be sized independently. Internet bandwidth, user count, cloud usage, VPN traffic and local powered devices can differ substantially.
When connecting Uganda branches to a central office or cloud environment, document routing and address plans before building tunnels. Overlapping private subnets are a frequent migration complication in networks that grew site by site. VLAN and IP planning can reduce future rework. If SD-WAN is used, define performance thresholds for latency, loss and jitter according to application needs rather than applying arbitrary defaults.
The PoE interfaces can support compatible APs, phones and other powered devices, but a 96 W total budget requires deliberate allocation. A small branch may connect endpoints directly; a larger office should consider a managed PoE switch for distribution, especially when devices are spread across floors or wiring closets. Direct firewall PoE is a design option, not a requirement to avoid switching infrastructure.
For Uganda procurement, confirm the exact hardware code, service bundle, term and any accessories on the quotation. Regional projects can use the FourTeck Uganda technology site for local-market enquiries while coordinating Tanzania requirements separately. Availability, logistics and implementation scope should be confirmed for each location rather than inferred from another country’s project.
FortiGate 80F PoE (FG-80F-POE) Kampala
In Kampala, the FG-80F-POE can be considered for business branches that combine cloud applications, wireless access, IP telephony and secure connectivity to other locations. Start with the WAN edge: identify ISP handoff types, addressing, bandwidth and whether a secondary service is required. The two GE RJ45/SFP shared-media WAN interfaces offer physical flexibility, but transceiver support and actual service handoff should be checked before procurement.
For offices using several PoE endpoints, calculate both port count and power. Eight PoE/+ interfaces are available, with 96 W total. If a Kampala office expects six access points plus several phones, for example, the total design may require access switching even though the firewall has eight powered ports. Port density, cable runs, VLANs and future expansion are as important as watts.
Security configuration should be tied to business flows. Finance systems, voice, guest Wi-Fi, administration devices and management interfaces can have distinct policy requirements. Use segmentation and least-privilege access rather than a single flat LAN. VPN access should be assigned to defined users and resources, with authentication and logging requirements decided during design. Subscription-backed security services should be selected according to the required protections.
A useful Kampala quotation request includes FG-80F-POE quantity, current firewall, internet links, users, VLANs, VPN peers, expected PoE devices and desired support/subscription term. If migration assistance is required, state that explicitly so configuration transfer, testing and change-window expectations can be discussed rather than assumed.
FortiGate 80F PoE (FG-80F-POE) Arua
Arua branch networks may place a premium on straightforward operation and dependable connectivity between local users and central applications. FG-80F-POE can consolidate firewall security and powered connectivity for a compact site, but the WAN design should account for the actual services available to that branch. Record primary and backup connectivity, expected throughput, public addressing and critical applications before selecting policies or failover behaviour.
Where the branch uses only a few wireless access points or IP phones, integrated PoE can reduce the number of powered devices in the cabinet. The 96 W budget still needs a device-by-device calculation. UPS runtime should also include the firewall, WAN equipment and any powered endpoints drawing energy through the firewall. A PoE endpoint remains offline if the upstream firewall loses power, so backup-power planning should consider the whole communications chain.
For inter-site VPN, confirm subnet uniqueness, DNS dependencies and which services need to traverse the tunnel. A branch may need access to ERP, file services, voice platforms or central authentication while ordinary internet traffic exits locally. These decisions affect routing and security policy. Test the design under both normal and failed-WAN conditions so operational teams understand what remains available.
Procurement should capture subscriptions and lifecycle responsibilities. Ask for the appliance, FortiCare/FortiGuard term and any required accessories as separate identifiable elements. Document who will monitor expiry, firmware maintenance and configuration backups. A technically suitable firewall can still become an operational risk if renewals and change control are unmanaged.
FortiGate 80F PoE (FG-80F-POE) Mbarara
For Mbarara organisations, FG-80F-POE can support a secure branch design that combines WAN policy, VPN connectivity and a modest PoE requirement. Rather than selecting it only because it includes powered ports, evaluate the complete topology. Determine how many wired users need switch access, how many wireless APs are required, whether IP phones or cameras need power, and where those devices are physically located.
A central firewall may be close enough to power endpoints in a compact office, while a larger building usually benefits from distributed PoE switching. The firewall’s 96 W budget is valuable but finite. Separating access switching from the security edge can improve cable management, port capacity and growth. FortiLink integration can be considered where FortiSwitch is part of the architecture, subject to exact model and software compatibility.
For WAN and VPN planning, document application criticality. Voice and interactive cloud tools respond differently to latency and packet loss than bulk downloads. If multiple WAN links are used, SD-WAN rules and health checks should reflect these differences. Security inspection must also be considered in effective performance sizing, especially as more services are enabled.
Mbarara procurement requests should identify whether the requirement is hardware supply only or includes configuration, migration and ongoing support. Provide current network information where possible. Clear scope helps prevent missing elements such as SFPs, patching, PoE switching, UPS capacity or subscription services from appearing late in the project.
FortiGate 80F PoE (FG-80F-POE) Gulu
Gulu buyers considering FG-80F-POE should look at how the branch depends on internet and central services. If business processes stop when connectivity fails, a secondary WAN may deserve more attention than adding unused LAN ports. FortiGate secure SD-WAN can support multi-link policies, but the resilience outcome depends on diverse upstream connectivity, suitable configuration and testing.
Integrated PoE can simplify small-site deployments by powering compatible endpoints from the firewall. This may reduce adapters and a separate PoE switch in a carefully sized network. However, the 96 W aggregate budget and 30 W per-port maximum must be respected. Future expansion should be included in the power calculation, and endpoint compatibility should be verified rather than assumed from the presence of an Ethernet port.
Security policy design should distinguish users and systems. Guest wireless access, staff devices, voice and management traffic should be segmented where appropriate. Remote administration should be controlled and logged. If the branch connects to headquarters by IPsec VPN, define allowed networks and services explicitly. These operational choices often matter more than simply enabling every available security feature.
For a Gulu quotation, include internet bandwidth, expected users, branch connections, required PoE devices, subscription term and whether deployment services are needed. If an existing firewall is being replaced, export or document current addressing, NAT, VPN and policy dependencies before the migration date. This reduces the chance of discovering critical rules only after cutover.
FortiGate 80F PoE (FG-80F-POE) Kenya
Kenya organisations evaluating FG-80F-POE can use it as a compact security and SD-WAN edge for suitable branch environments. A regional business with Kenya and Tanzania operations may value consistent FortiGate policy concepts across sites, but sizing must remain site-specific. Nairobi-scale headquarters requirements can differ greatly from a smaller branch, and the 80F PoE should be selected according to inspected traffic, VPN demand and endpoint design.
The integrated PoE/+ capability is most compelling when a branch has a limited number of powered devices near the firewall. For larger wireless, voice or surveillance deployments, managed PoE switching is usually easier to scale. Calculate the total endpoint power against the 96 W budget and consider physical cabling. A port that can provide PoE does not eliminate Ethernet distance limits or the need for structured cabling.
If the Kenya site uses two internet links, establish the business objective for SD-WAN: failover, load distribution, application steering or a combination. Define measurable link-quality thresholds and test the behaviour of critical applications. For site-to-site connectivity, coordinate IP addressing across countries to avoid overlapping networks and simplify routing.
For Kenya procurement and regional coordination, the FourTeck Kenya site is a relevant regional resource. Quote requests should specify FG-80F-POE, quantity, service bundle and term, and any implementation expectations. Stock, price and delivery should be confirmed at enquiry time rather than inferred from another market.
FortiGate 80F PoE (FG-80F-POE) Kuwait
Kuwait deployments can evaluate FG-80F-POE where a branch needs Fortinet security, secure SD-WAN and integrated PoE connectivity in a compact footprint. Environmental and equipment-room planning is important: the official appliance operating range is 0°C to 40°C, so network cabinets should be installed in appropriately conditioned indoor spaces rather than exposed to unsuitable heat or dust.
The 96 W PoE budget can power a selected mix of compatible endpoints, but project designers should reserve headroom and consider UPS sizing. Because powered devices draw through the firewall, the firewall power load is different from a non-PoE model. The official data lists average and maximum consumption figures that reflect this class of appliance, so power protection should be sized for the complete network cabinet rather than only the firewall nameplate.
For businesses with multiple sites, secure SD-WAN and IPsec VPN can support branch connectivity strategies. Define whether internet breakout occurs locally or centrally, which applications require inspection, and how traffic should behave if a WAN path fails. These architecture decisions should be agreed before implementation so firewall policy, routing and monitoring align with business expectations.
A Kuwait quotation request should identify hardware quantity, subscriptions, support term, SFP requirements if any, PoE endpoints and deployment scope. Cross-market FourTeck projects can coordinate requirements while treating commercial availability and services per country as items to confirm. Avoid assuming that a configuration or accessory used in another branch is automatically the correct fit for the Kuwait site.
FortiGate 80F PoE (FG-80F-POE) Ghana
Ghana branches considering FG-80F-POE should begin with connectivity and business-critical application mapping. The appliance can bring firewalling, VPN, SD-WAN and powered Ethernet together, which is useful for compact locations, but design quality depends on knowing what traffic must be protected and prioritised. List internet links, cloud services, central applications, remote users and branch-to-branch flows.
For PoE, identify every intended endpoint and its wattage. A branch with access points and phones may fit within the 96 W aggregate budget; a surveillance-heavy environment may not. When power or port requirements exceed the firewall’s practical role, add an appropriately sized PoE switch. This also makes it easier to segment users, voice, wireless and cameras across VLANs.
Operational planning should include configuration backups, firmware management, subscription renewals and incident response. FortiGuard services are subscription-dependent, so procurement and IT teams should share visibility of renewal dates. For VPN and SD-WAN, monitoring should focus on real link health and application impact rather than only whether an interface is technically up.
For Ghana procurement, request the exact FG-80F-POE hardware and the desired service term, and confirm any SFP or rack-related accessories separately. Regional FourTeck coordination can be useful for organisations standardising network security across Africa, while local availability and implementation arrangements remain subject to confirmation for the specific project.
FortiGate 80F PoE (FG-80F-POE) Nigeria
Nigeria organisations can consider FG-80F-POE for branch security where multiple internet links, cloud services, VPN connectivity and PoE edge devices converge. In locations where connectivity resilience is important, map primary and secondary WAN dependencies carefully. Secure SD-WAN can steer traffic based on policy and measured link conditions, but the business continuity result depends on the quality and independence of the underlying services.
Power planning should include both utility resilience and the firewall’s PoE role. The 96 W PoE budget means attached devices can depend directly on the firewall for power. A UPS or other appropriate power-protection design should therefore account for firewall, ISP equipment, switches and the powered endpoints required during an outage. Define which services truly need runtime rather than sizing backup power blindly.
For security segmentation, separate staff, guest, voice, management and other sensitive systems according to business needs. Use VPN policies that expose only necessary resources. If a branch supports payment, ERP or other critical systems, document those dependencies during migration. Security subscriptions should be selected according to the protections required rather than simply choosing the shortest or broadest bundle without analysis.
Nigeria quote requests should specify quantity, FortiGuard/FortiCare term, WAN links, VPN sites, PoE endpoints and desired deployment services. Confirm pricing, stock and logistics at the time of enquiry. For organisations operating in multiple African markets, standard configuration templates can help governance, but local addressing, circuits and site requirements still need individual validation.
FortiGate 80F PoE (FG-80F-POE) Seychelles
Seychelles businesses evaluating FG-80F-POE may be especially interested in a compact platform that combines branch security and powered connectivity without requiring unnecessary equipment. Hospitality, professional and distributed business environments can have strong dependence on internet access, Wi-Fi and cloud services, so the firewall should be sized around real application and inspection needs.
The eight PoE/+ interfaces can power a carefully selected set of compatible endpoints, subject to the 96 W total budget. In a small communications room, this consolidation can be convenient. In larger properties, access points and cameras may be physically distributed, making PoE access switches closer to endpoint zones more practical. Network design should follow cable topology and growth requirements rather than forcing direct connection to the firewall.
For WAN resilience, identify the available connectivity options and whether they provide genuinely independent paths. Secure SD-WAN policies can prioritise applications and react to measured path health. Test guest internet, business applications, voice and VPN behaviour separately because each may respond differently during degradation or failover.
A Seychelles procurement request should include the exact FG-80F-POE model, subscription duration, number and type of PoE endpoints, WAN design and any implementation expectations. If the project spans several islands or sites, provide site-by-site connectivity and user information. This allows the firewall and switching design to be assessed for each location rather than assuming one identical bill of materials everywhere.
Licensing, FortiGuard and support planning
The hardware is only one part of a FortiGate deployment. FortiGuard security services and FortiCare support are offered through subscription and support packages, and the exact capabilities available depend on the purchased entitlement and FortiOS configuration. When comparing quotations, verify the service package, start/end term and support level instead of comparing only appliance model numbers.
Renewal planning should begin at procurement. Record contract identifiers, expiry dates and the internal owner responsible for renewal review. If a security service is important to policy enforcement, understand the operational effect of expiry before it occurs. For multi-site organisations, align renewal dates where practical to simplify administration, while avoiding assumptions that all sites require identical service levels.
Deployment and integration checklist
WAN
Document ISP handoffs, bandwidth, public addressing, backup links, routing and SD-WAN objectives.
LAN & VLANs
Define user, voice, wireless, server, guest and management segments plus access policies between them.
PoE
List endpoint models, count and watts; keep the combined requirement within the 96 W appliance budget with headroom.
VPN
Record remote networks, users, authentication, routing and application access for IPsec or supported remote-access designs.
Frequently asked questions
How many PoE ports does the FortiGate 80F PoE have?
The FG-80F-POE has six GE RJ45 PoE/+ internal interfaces and two GE RJ45 PoE/+ FortiLink interfaces, giving eight PoE/+ ports in total.
What is the FG-80F-POE PoE power budget?
Fortinet specifies a 96 W total available PoE power budget. Maximum loading on each PoE/+ port is 30 W under 802.3at. Project designers should calculate aggregate endpoint consumption rather than relying only on port count.
Can FG-80F-POE power wireless access points?
It can power compatible PoE/PoE+ devices within the supported per-port and total power limits. Confirm the exact access-point model, required PoE standard and wattage before deployment.
Does FortiGate 80F PoE support secure SD-WAN?
Yes. The FortiGate 80F series is positioned by Fortinet as a converged NGFW and secure SD-WAN platform. Actual SD-WAN policy should be designed around the site’s WAN links, application priorities and performance objectives.
Should I connect every PoE device directly to the firewall?
Not necessarily. Direct connection can work for compact sites, but larger deployments often benefit from managed PoE switching for port density, cabling, VLAN distribution and future expansion.
What information should I provide for a Tanzania quote?
Provide FG-80F-POE quantity, internet bandwidth, user/device count, WAN links, VPN requirements, intended PoE endpoints, preferred subscription term and whether migration or configuration services are required.
Quotation checklist for FG-80F-POE
For a clearer quotation, include the exact model and quantity; primary and secondary internet bandwidth; number of users, VLANs and branches; IPsec and remote-access VPN needs; required security services; PoE endpoint models and quantities; SFP requirements; existing firewall and migration expectations; preferred support/subscription term; and target deployment timeframe. This information helps identify whether the firewall alone is sufficient or whether switching, wireless, power protection or other components should be included.
Decision recap
FortiGate 80F PoE is most compelling when an organisation needs FortiGate NGFW and secure SD-WAN capabilities plus a modest, clearly calculated PoE requirement. Its eight PoE/+ interfaces and 96 W budget can simplify compact branches, while shared-media WAN ports add handoff flexibility. It should not be chosen on port count alone: inspected traffic, VPN demand, FortiGuard services, WAN resilience, endpoint power and future switching needs all belong in the sizing decision.
For Tanzania projects, FourTeck can use your requirement details to discuss product fit and quotation scope. For broader corporate technology requirements, the FourTeck network provides additional regional context. Commercial availability, delivery, subscriptions and implementation scope should always be confirmed for the specific order.
Discuss your FortiGate 80F PoE requirement
Send the intended site, user count, internet speed, VPN needs, PoE endpoints and preferred subscription term. A requirement-led discussion makes it easier to assess FG-80F-POE against the actual branch design and identify any switching, wireless or power components that should be planned with it.




Reviews
There are no reviews yet.