
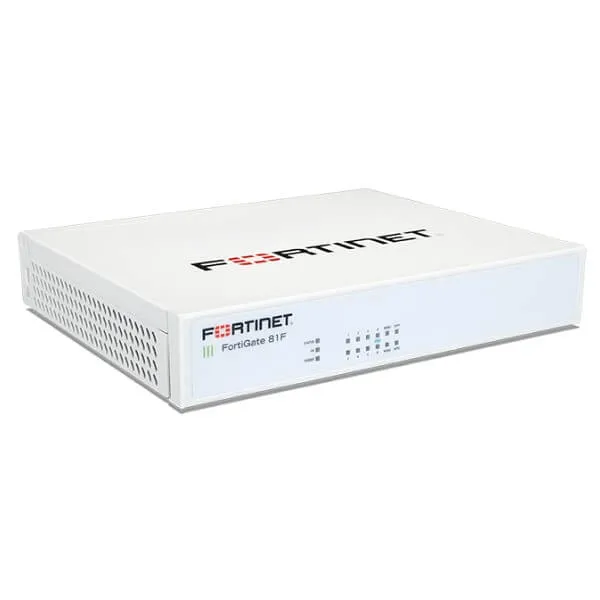
FortiGate 81F (FG-81F)
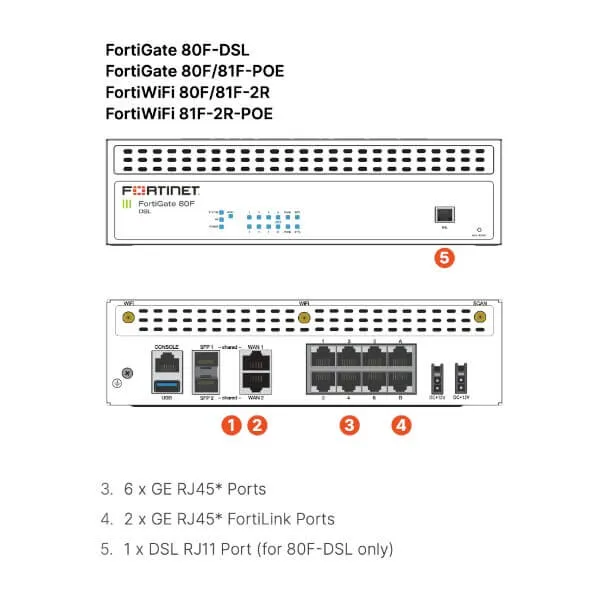
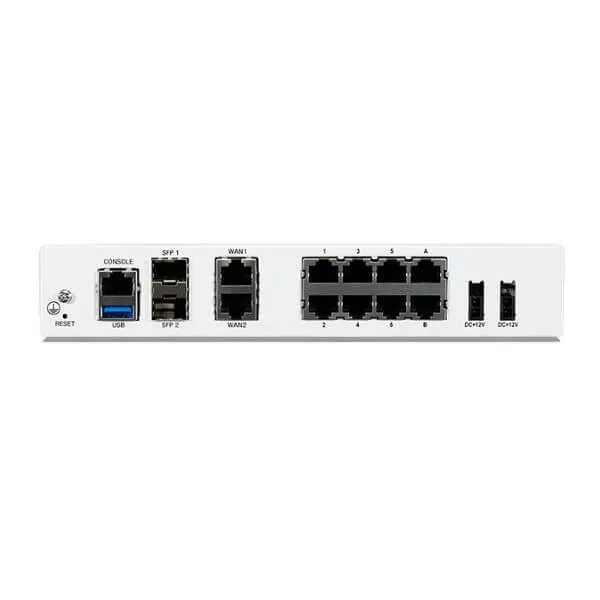
The FortiGate 81F is the storage-equipped member of Fortinet’s 80F family for organizations that want a compact security gateway with integrated networking, security inspection, VPN and secure SD-WAN capabilities. Fortinet’s official data sheet lists eight GE RJ45 ports, two RJ45/SFP shared-media WAN ports and 128GB onboard storage for the FG-81F. For Tanzania buyers, the practical purchase decision should combine the appliance with the right FortiGuard/FortiCare entitlement, internet-speed headroom, VPN requirements and a deployment plan rather than treating the firewall as an isolated box.

What is the FortiGate 81F?
FortiGate 81F, model FG-81F, is a desktop-form-factor FortiGate appliance in the FortiGate/FortiWiFi 80F Series. Fortinet positions the series for converged networking and security use cases where organizations need firewalling, application-aware controls, intrusion prevention, web and threat security functions, VPN connectivity and SD-WAN capabilities in a compact platform. The key hardware distinction between the FG-80F and FG-81F in Fortinet’s ordering information is the FG-81F’s 128GB onboard storage. That storage can be valuable for organizations that want local logging capacity, but retention and analytics requirements should still be planned rather than assumed.
A firewall should be sized for the services that will actually run. Raw firewall throughput is not the same as usable performance when IPS, threat protection, SSL inspection, application control and VPN are enabled simultaneously. Internet bandwidth, user count, encrypted traffic, number of branch tunnels, public services, VLAN count and growth all matter. FourTeck Tanzania’s integrated IT and network-security overview explains why firewall selection should be coordinated with switching, Wi-Fi, servers, cabling and business applications.
128GB onboard storage
Fortinet’s official ordering information identifies 128GB onboard storage on FG-81F, distinguishing it from FG-80F.
Flexible WAN media
Two RJ45/SFP shared-media WAN ports support practical copper or compatible SFP connectivity choices within the model’s documented interface design.
Business security stack
FortiOS and FortiGuard services can combine firewall policy, VPN, SD-WAN and subscribed security functions in one operational platform.
Verified FG-81F hardware facts and buying implications
| Item | Verified FG-81F detail | Procurement implication |
|---|---|---|
| Model | FG-81F | Confirm the exact base model versus PoE or FortiWiFi variants before ordering. |
| LAN interfaces | 8 × GE RJ45 | Map firewall ports to WAN, LAN, DMZ, management or downstream switching requirements. |
| WAN media | 2 × RJ45/SFP shared-media WAN ports | Confirm ISP handoff type and compatible optics if fiber is planned. |
| Storage | 128GB onboard storage | Useful for local logging; define retention, reporting and central-management requirements. |
| Form factor | Desktop; wall/rack-tray mounting supported for the series | Include rack tray, mounting, UPS and cable organization in the deployment bill of materials when needed. |
Security, SD-WAN, VPN and integration planning
FG-81F can serve as the security policy point between internet connections and internal business networks. A practical design may separate employee, server, voice, guest Wi-Fi, CCTV and management traffic using VLANs and controlled inter-zone policies. Site-to-site IPsec VPN can connect branches, while remote-access requirements should be defined around user identity, endpoint posture and the organization’s chosen Fortinet licensing and access architecture. Secure SD-WAN can be relevant where a site uses more than one WAN path and needs application-aware path selection or resilience.
For adjacent infrastructure, review FourTeck Tanzania’s networking and security product guidance, IT integration services, and quotation and project enquiry page. Regional buyers can also use FourTeck Fortinet UAE, FourTeck Kenya, FourTeck Uganda, FourTeck Ghana and FourTeck Nigeria for market-specific project context.
FortiGate 81F Tanzania
Organizations evaluating FortiGate 81F in Tanzania commonly need more than a firewall appliance: they need a clear design for internet edge security, branch connectivity, remote access and internal segmentation. The FG-81F can be considered for offices, professional-services firms, education environments, retail operations, hospitality administration, clinics, warehouses and distributed businesses where the selected security workload fits the platform. The 128GB onboard storage is a useful differentiator for buyers who value local logging, but storage capacity should not be confused with a complete log-management strategy. Decide which events must be retained, how long they are needed, who reviews them and whether centralized FortiAnalyzer or another logging workflow is part of the project.
For Tanzania procurement, start with the internet circuits and the traffic that must cross the firewall. Record primary and backup ISP bandwidth, public IP requirements, any fiber handoff, the number of users and devices, VPN tunnels, remote workers and applications that are sensitive to latency. Then identify the security services you expect to enable. Threat inspection, IPS, application control, web filtering and encrypted-traffic inspection consume resources differently from basic stateful firewalling, so sizing should leave sensible headroom. If the network includes guest Wi-Fi, IP phones, cameras, servers or payment systems, define VLANs and access rules before installation rather than adding them reactively.
Power and physical installation also matter. A firewall, ISP equipment and core switch should be connected to appropriately sized UPS protection where continuity is important. Rack installations should include the correct tray or shelf, ventilation and labelled patching. Configuration backups, administrator MFA where supported, restricted management access, firmware lifecycle planning and documented change control reduce operational risk after handover. When requesting a Tanzania quotation, provide the exact FG-81F model, desired FortiCare/FortiGuard term, user and device count, internet speeds, VPN needs, number of sites and expected deployment date. This produces a more meaningful comparison than asking only for a box price and helps ensure subscription, support and implementation scope are understood before purchase.
FortiGate 81F Dar es Salaam
For a Dar es Salaam office, the FG-81F may sit at the center of a busy connectivity environment where cloud applications, VoIP, video meetings, guest wireless, business systems and remote access all share one or more internet connections. Buyers should therefore model traffic by business function rather than relying on employee count alone. A fifty-person office with heavy cloud backup, video collaboration and encrypted SaaS traffic can place different demands on a firewall from a larger site using mostly lightweight applications. Document current and planned ISP speeds, peak usage periods, public services, VPN tunnels and whether a secondary internet link will be used for failover or SD-WAN.
Network segmentation is particularly valuable in mixed-use offices. Employee devices, finance systems, servers, visitor Wi-Fi, CCTV cameras, access-control equipment and IP phones do not need identical access. VLANs on managed switches can create logical zones, while FG-81F policies determine which zones may communicate. This makes firewall deployment a network-design exercise, not simply a replacement of an ISP router. Where a site already has managed switches, wireless controllers or server infrastructure, collect firmware versions, VLAN IDs, routing details and IP ranges before migration so cutover can be planned with less disruption.
Procurement teams in Dar es Salaam should also distinguish hardware-only quotes from bundles that include FortiGuard security services and FortiCare support. Confirm the subscription term, start date, renewal responsibility, included support level and whether implementation is separately priced. Ask for optics only when the selected WAN or LAN design genuinely requires SFP connectivity, and verify transceiver compatibility. If local logging is important, define how the FG-81F’s onboard storage will be used and when logs should be exported. For a quote, include the business location, rack or desktop preference, UPS situation, internet handoffs, expected security functions and migration window. FourTeck Tanzania’s contact workflow specifically encourages firewall buyers to provide internet speed, VPN requirements and enabled security services so product selection can be aligned with real operating conditions.
FortiGate 81F Mwanza
Mwanza buyers considering FortiGate 81F can approach the project around resilience, manageability and clear remote-support procedures. A branch, warehouse, healthcare office, school administration network or trading business may rely on cloud services while also operating local applications, printers, cameras and voice systems. The firewall design should identify which traffic is business critical and what happens if the primary internet connection fails. If two WAN services are available, secure SD-WAN policies can be designed around availability and application needs; however, the actual benefit depends on the quality and independence of the underlying circuits, not merely on having two cables connected.
For sites where technical support may sometimes be delivered remotely, management security deserves special attention. Avoid exposing administrative interfaces broadly to the internet. Restrict management sources, use secure administrator practices, maintain configuration backups and document how authorized support access is established. Site-to-site VPN can provide controlled connectivity to a head office, data center or another branch. Before deployment, list required subnets and applications so VPN rules can be narrow and understandable instead of creating an unrestricted bridge between networks. If remote users require access, define the user population and authentication workflow separately from branch-to-branch connectivity.
The FG-81F’s 128GB onboard storage may support local event retention, which can be useful when WAN connectivity is intermittent, but logging objectives should be explicit. Decide which security and system events matter, who reviews them and whether longer-term centralized retention is needed. Physical planning should include stable power, UPS capacity, surge protection appropriate to the site, secure placement and clean cabling. For Mwanza procurement, request a bill of materials that clearly separates the appliance, subscription/support entitlement, any SFP modules, mounting accessories and professional configuration. Provide current router/firewall details, internet speeds, number of users, VLANs, VPN destinations and security services. This allows the FG-81F to be assessed as part of a complete operational design rather than purchased solely because its headline specifications appear suitable.
FortiGate 81F Arusha
Arusha organizations may evaluate FortiGate 81F for office networks, hospitality administration, travel operations, education, NGOs, professional services and branch environments that need secure internet access plus controlled connectivity to remote systems. In hospitality and visitor-facing environments, segmentation becomes especially important because guest wireless should not share unrestricted access with finance, reservations, administration, CCTV or building systems. The firewall can enforce boundaries between these networks when the switching and Wi-Fi design carries the required VLANs correctly.
Sizing should start with the busiest realistic period. Count staff devices, shared workstations, phones, cameras, wireless clients and servers, then identify how much traffic must be inspected. Encrypted cloud applications and web traffic are now normal, so organizations planning deeper inspection should evaluate performance for that security profile rather than using only raw firewall throughput. VPN requirements should include both the number of connections and their purpose: a site-to-site tunnel carrying ERP traffic has different operational importance from occasional remote administrator access. If multiple WAN links are planned, define which applications should fail over, which may use either link and how sessions should behave during an outage.
Arusha procurement teams should request clarity on licensing. FortiGate hardware can be purchased with different FortiCare and FortiGuard service combinations and terms; the correct choice depends on the security controls and support expectations of the organization. Confirm renewal dates and ownership of the Fortinet account used for registration. The FG-81F’s onboard storage can assist local logging, but log review and retention policy still need ownership. Deployment planning should include a configuration baseline, documented administrator roles, network diagram, backup process and post-cutover test list covering internet access, DNS, business applications, VPN, guest access and inbound services. When requesting a quotation, include ISP bandwidth, user/device count, existing switches and access points, rack conditions and target security features so the proposal addresses integration as well as the appliance itself.
FortiGate 81F Dodoma
In Dodoma, organizations assessing the FG-81F may include administrative offices, professional firms, education sites, project offices and multi-branch operations that require predictable policy enforcement and secure connectivity. The strongest starting point is a simple traffic and trust map: identify internet users, internal servers, cloud applications, guest networks, voice, cameras, management devices and external partners. Decide which groups should communicate and which should remain isolated. This becomes the basis for VLANs, firewall zones and policies and is easier to audit than a large collection of broad rules added over time.
If the Dodoma site connects to Dar es Salaam or other branches, define VPN traffic carefully. Document local and remote subnets, routing, DNS dependencies and which applications cross the tunnel. Consider redundancy if the branch supports critical services. Dual internet links can improve continuity, but the design should test actual failover and not assume that every application survives a public-IP change or path transition transparently. Secure SD-WAN policy can prioritize paths based on defined criteria, while monitoring helps administrators understand whether poor application performance is caused by the WAN, the firewall or another part of the network.
The FG-81F offers local onboard storage, which can support logs close to the appliance. Procurement and IT teams should decide whether this is sufficient for their operational retention period or whether centralized analysis is required. Security subscriptions also need explicit scope. A quote should state hardware, service bundle, support term, registration details and renewal expectations. Before installation, confirm the ISP handoff, IP addressing, rack or wall placement, UPS protection, switch VLAN configuration and administrator access method. After migration, validate business applications, VPNs, printing, voice, guest Wi-Fi and any inbound services. For Dodoma buyers comparing firewall quotations, request the same licensing term and implementation assumptions from each proposal; otherwise a low hardware-only price can appear cheaper while excluding the security services, support or configuration work needed for a usable deployment.
FortiGate 81F UAE
UAE buyers searching for FortiGate 81F frequently compare appliance-only pricing with one-, three- or multi-year security bundles. The important procurement task is to normalize those offers. Confirm that every quotation refers to FG-81F rather than FG-80F, FG-81F-POE or a FortiWiFi variant; confirm the exact FortiCare/FortiGuard services, subscription duration, support level and whether VAT, shipping, installation or configuration are included. The FG-81F base model is documented with eight GE RJ45 ports, two RJ45/SFP shared-media WAN ports and 128GB onboard storage, so any additional PoE requirement should trigger a review of the correct model or external switching rather than an assumption that the base appliance supplies PoE.
For UAE branch and SMB environments, internet circuits can be fast enough that security-service throughput becomes a central sizing question. Build the requirement around actual WAN bandwidth plus growth, then add VPN, encrypted inspection and threat-prevention needs. If the firewall will protect a public server or published application, document NAT, inbound policy and segmentation separately from normal outbound user access. If the site uses two carriers, secure SD-WAN can provide policy-based path selection, but test business applications that depend on fixed public IPs or long-lived sessions.
Operationally, organizations should define who owns Fortinet registration, firmware updates, configuration backups, policy reviews and subscription renewals. The 128GB storage provides local logging capability, yet larger organizations may still prefer centralized FortiAnalyzer or SIEM integration for longer retention and cross-device visibility. Rack deployment may require the appropriate tray and clean power planning. FourTeck’s Fortinet-focused UAE site can provide regional context, while cross-border projects should keep licensing, shipping and support scope explicit for each destination. A good UAE quotation request therefore includes the exact FG-81F model, quantity, internet bandwidth, number of users and sites, VPN requirements, preferred subscription term, optics needs and whether professional configuration or migration from an existing firewall is required.
FortiGate 81F Uganda
Uganda organizations evaluating FortiGate 81F can use the appliance as part of a standardized branch-security design where internet access, VPN, segmentation and logging are managed consistently across sites. Before selecting the model, list WAN bandwidth at each location and identify whether the firewall must support headquarters traffic, direct internet breakout, cloud applications, branch VPN and remote users simultaneously. A standard model across several similar branches can simplify spares and configuration templates, but only when the bandwidth and security workload are genuinely comparable.
The FG-81F’s local storage can be attractive for branch logging, particularly when administrators want events retained on the device. Still, organizations should define central visibility requirements. If security teams need consolidated reporting across multiple FortiGates, centralized management and logging may be more practical than reviewing each branch independently. For VPN design, avoid overlapping private IP ranges between sites because they complicate routing and troubleshooting. Create a repeatable address plan, naming standard and policy template before rolling out additional branches.
Uganda procurement should separate appliance, subscription, support and implementation costs. Verify the exact entitlement term and renewal process, and avoid assuming that every advertised security feature is available without the relevant service. Confirm the physical ISP presentation at the installation site and whether SFP optics are needed. Include UPS protection and secure equipment placement in the project scope, especially for sites where power interruptions could affect connectivity. A useful quotation request specifies user/device count, primary and secondary internet speeds, number of VPN peers, applications crossing those tunnels, security inspection requirements, existing VLANs and target go-live date. FourTeck Uganda provides a regional route for wider IT solution context, while the Tanzania team can coordinate requirements where a customer operates across both markets. Cross-border consistency is most valuable when documentation, administrator roles and renewal dates are standardized as carefully as the hardware.
FortiGate 81F Kampala
Kampala offices often combine wired users, corporate Wi-Fi, guest access, VoIP, cloud applications, CCTV and remote connectivity in one site. An FG-81F project should therefore begin by identifying trust zones and application dependencies. Employee devices may require access to internal servers and cloud services, while guest wireless should normally be restricted to internet access. Cameras and IoT-style devices can be isolated from user networks, and management interfaces can be placed in a more restricted segment. These controls depend on coordinated switch VLANs and firewall policy, so configuration should be designed across the LAN rather than only at the internet edge.
Kampala buyers with dual ISP links should decide what redundancy actually means for their business. Some organizations simply need internet browsing to continue; others need VPN tunnels, cloud voice or published services to remain available. Those objectives affect SD-WAN policy, DNS, public addressing and failover testing. When VPN connects a Kampala office to other branches, document bandwidth expectations for file transfers, ERP, voice or remote desktop because the mix influences capacity planning. Security inspection should be sized with headroom for future bandwidth upgrades rather than only today’s package.
Procurement should compare like-for-like bundles. Confirm FG-81F hardware, FortiGuard services, FortiCare level, entitlement duration, implementation, training and any optics or mounting accessories. The model’s 128GB onboard storage supports local logs, but retention targets and administrator review procedures remain separate decisions. Before cutover, export the existing firewall configuration and create a rule-migration worksheet instead of copying obsolete rules blindly. After deployment, test DNS, internet, VPN, voice, guest Wi-Fi, inbound services and critical cloud applications. A Kampala quotation request should include current firewall make/model, ISP speeds, VLANs, number of users, remote-access demand and desired security functions. This lets the supplier assess fit and migration complexity rather than responding with a price that omits the work needed to make the firewall operational.
FortiGate 81F Arua
For Arua deployments, the value of a firewall project often depends on reliability and remote manageability as much as on feature count. A branch may have fewer local IT resources, making clear documentation, secure remote administration and resilient connectivity important. The FG-81F can be assessed for this role when its performance aligns with the site’s internet bandwidth and enabled security services. Begin by recording the ISP connection type, typical and peak throughput, backup connectivity options, user/device count and which business applications must remain available during a WAN problem.
If the Arua site is connected to a headquarters, site-to-site VPN should be built around a documented addressing plan and restricted policies. Decide whether internet traffic exits locally or travels through headquarters, because that choice changes bandwidth and security design. If two WAN links exist, SD-WAN can select paths based on policy and health checks, but test the failover behavior of critical applications. Local services such as printers, cameras or file servers should continue to function appropriately even when the internet is unavailable, which requires sensible LAN design rather than placing every dependency in the cloud without contingency.
The FG-81F’s 128GB onboard storage can retain local logs, helping troubleshooting and event review, but administrators should decide how backups and longer-term records are handled. Secure management should use restricted sources and strong authentication, with configuration backups stored away from the appliance. Physical installation needs stable power and a UPS sized for the firewall plus essential upstream/downstream equipment. When buying for Arua, request an itemized proposal: appliance, FortiCare/FortiGuard bundle, subscription period, accessories, configuration and support. Provide details of existing routers, switches, IP ranges and VPN peers. This makes remote deployment planning more predictable and helps avoid a situation where the appliance arrives without the entitlement, optics, power protection or configuration information required to put it into service.
FortiGate 81F Mbarara
Mbarara businesses considering the FortiGate 81F may be replacing an ISP router, upgrading from a smaller firewall or standardizing security across several branches. Each scenario requires a different migration plan. Replacing an ISP router may require coordination for public addressing and bridge mode. Replacing an existing firewall requires a review of NAT, VPNs, VLANs and inbound rules. Standardizing branches requires templates but also site-specific checks for bandwidth, addressing and local applications. Treating these scenarios as identical increases the chance of unexpected downtime.
A useful design exercise is to classify traffic into critical, normal and restricted groups. Critical traffic might include ERP, payment, voice or branch VPN. Normal traffic includes general cloud and web access. Restricted groups may include guest Wi-Fi, cameras or unmanaged devices that should have limited reach into the business network. The FG-81F can enforce policies between these zones when switches and access points are configured consistently. If dual WAN is available, SD-WAN rules can give priority to business-critical traffic while keeping a backup path available, subject to the characteristics of each ISP service.
For procurement in Mbarara, do not evaluate only purchase price. Clarify subscription length, renewal cost expectations, support coverage, implementation scope and ownership of the Fortinet account. The 128GB onboard storage is a concrete hardware advantage of the 81F over the base 80F for local logging use, but it does not eliminate the need for a log-retention policy. Include UPS protection, rack placement and labeled cabling in the deployment plan. Ask the installer to provide a configuration backup and a simple network diagram after handover. When requesting a quotation, include the exact FG-81F model, internet bandwidth, number of users and devices, VLAN requirements, VPN destinations, remote-access needs and any existing Fortinet equipment. These details make it easier to determine whether the FG-81F is appropriately sized and what supporting services belong in the project.
FortiGate 81F Gulu
Gulu deployments can benefit from a firewall architecture that is simple to operate, easy to recover and well documented. For an office or branch, start by identifying the minimum services that must work after any change: internet access, DNS, cloud applications, VPN, voice, remote support and access to local servers. Build a test checklist around these services before migrating to the FG-81F. This reduces troubleshooting time because the team knows exactly what must be validated rather than relying on users to discover problems after cutover.
Network segmentation can reduce the impact of compromised or poorly managed devices. Staff computers, guest Wi-Fi, CCTV, voice and infrastructure management can use separate VLANs with policies that permit only required communication. For example, cameras may need to reach a recorder and time/DNS services but not employee laptops. Guest clients may need internet access but no internal routes. The exact policy depends on the environment, but defining these flows in plain language before configuring the firewall produces cleaner rules. If the Gulu site connects to another city, document VPN subnets and routing to avoid overlaps.
Connectivity resilience should be planned realistically. A second WAN path is useful only if it is available when the primary fails and has enough capacity for priority applications. SD-WAN health checks and policy can automate path decisions, but periodic failover tests remain important. The FG-81F’s local storage can assist troubleshooting by keeping logs on the appliance; administrators should still back up configurations and decide whether centralized logging is required. For a Gulu purchase, request the firewall and security/support entitlement as separate visible line items, along with any SFPs, rack accessories and configuration service. Provide the ISP handoff, bandwidth, current addressing, user count and required VPNs. A documented, itemized project is easier to support over time than a hardware-only purchase whose licensing and configuration assumptions are unclear.
FortiGate 81F Kenya
Kenya buyers comparing FortiGate 81F offers should first ensure every supplier is quoting the same model and service bundle. FG-81F is the base 81F appliance with 128GB onboard storage; it should not be confused with PoE or wireless variants. Hardware specifications are only one part of the total solution. FortiGuard subscriptions determine access to relevant security services, while FortiCare defines support entitlements. Compare identical terms and support levels before drawing conclusions from price differences.
For Nairobi or regional branch networks, sizing should consider high-speed fiber connections, cloud application usage and encrypted traffic. If the organization expects to upgrade WAN bandwidth during the firewall’s lifecycle, include that future capacity in the design. Identify site-to-site VPN tunnels, remote users, public applications and the security functions that will run concurrently. If multiple internet links are available, define whether they are intended for simple backup, active use, application steering or business continuity. These goals affect SD-WAN policy and testing.
Kenya deployments should also coordinate the firewall with managed switches and wireless networks. Segmentation is most effective when VLAN design is consistent from access ports and SSIDs through to the firewall. Keep guest, employee, server, voice and device networks separated according to business need, then document the allowed flows. The FG-81F’s onboard storage can support local logs, while centralized environments may use broader management and analytics tooling. Procurement requests should specify quantity, WAN speeds, number of sites, VPN design, FortiGuard/FortiCare term, optics, rack accessories and implementation scope. FourTeck Kenya offers regional IT solution context for customers operating there, while Tanzania-based organizations with Kenyan branches can standardize naming, policy templates and renewal tracking across both countries. Consistency should improve manageability without ignoring differences in each site’s connectivity and workload.
FortiGate 81F Kuwait
Kuwait organizations evaluating FG-81F should pay particular attention to internet bandwidth and security inspection because modern business circuits can be fast while a firewall’s effective throughput varies by enabled feature set. Start with current and expected WAN speeds, then identify whether IPS, application control, web filtering, malware protection, SSL inspection and VPN will be active. This produces a more useful sizing discussion than comparing raw firewall throughput alone. If requirements exceed the comfortable operating range, moving to a larger FortiGate can be more economical than running a smaller unit without headroom.
Branch and SMB deployments can use segmentation to separate staff, servers, voice, guest access and IoT-style devices. Where two internet links are installed, secure SD-WAN can apply health checks and policy-based path selection. However, business continuity also depends on ISP diversity, public addressing, DNS and the behavior of cloud or published applications during failover. Document these dependencies and test them after configuration. Site-to-site VPN should use a clear IP plan and restricted policies, especially when connecting offices across countries.
The FG-81F’s 128GB onboard storage provides local log capacity, but organizations with formal retention or monitoring requirements should define whether centralized logging is needed. Kuwait procurement should request exact Fortinet SKU/bundle references, subscription duration, support level, registration ownership and renewal terms. Confirm power accessories, rack tray and SFP optics where required, rather than assuming they are included. If migrating from another firewall, include policy review and configuration conversion in the project scope. A quotation request should state quantity, user/device count, internet speeds, VPN peers, public services and preferred support term. This allows the proposal to reflect the complete operational requirement and helps avoid comparing an appliance-only quote with a security bundle that includes services and support.
FortiGate 81F Ghana
Ghana businesses looking at FortiGate 81F may need a secure internet gateway for a head office, branch, professional-services environment, education site, retail operation or distributed organization. The model’s suitability should be determined from bandwidth and security workload rather than industry name. Gather the number of users and devices, internet speeds, VPN tunnels, cloud applications, remote-access demand and expected growth. Then identify which FortiGuard security services are required so performance and subscription scope can be assessed together.
For multi-site Ghana deployments, a repeatable network template can simplify support. Standardize VLAN names, IP ranges where practical, administrator roles, configuration backups and VPN naming. Avoid copying a configuration blindly from one branch to another because ISP details and local services differ. Secure SD-WAN can support dual-WAN designs, but each site should have appropriate health checks and application priorities. Critical systems should be tested during simulated WAN failure to confirm that the design delivers the continuity the business expects.
FG-81F includes 128GB onboard storage, making local logging a relevant purchasing consideration. Decide whether logs remain only on the appliance or are forwarded for centralized retention and analysis. Procurement teams should compare offers based on the same hardware and subscription term and ask suppliers to identify implementation and accessories separately. Physical deployment should include secure placement, appropriate UPS protection and labeled network connections. FourTeck Ghana provides a regional route for customers with Ghana operations, while organizations spanning Ghana and Tanzania can benefit from consistent firewall policy documentation and renewal tracking. A strong quote request includes the exact model, quantity, WAN bandwidth, number of branches, VPN requirements, target security services, existing firewall details and desired go-live window. This helps turn a product enquiry into a deployment plan rather than leaving important licensing and integration questions until installation day.
FortiGate 81F Nigeria
Nigeria buyers assessing the FortiGate 81F should plan for the actual mix of connectivity and security services at the target site. An office using multiple cloud platforms, VPN, voice, guest Wi-Fi and large file transfers can generate a different workload from a similarly sized branch using mainly web and email. Record primary and backup ISP speeds, user/device counts and peak traffic patterns. If bandwidth is expected to grow, include future capacity so the firewall is not selected at the edge of its practical requirement on day one.
Dual-WAN environments can use Fortinet secure SD-WAN features to monitor links and steer traffic according to policy. The design should identify applications that require stable public IPs, low latency or specific routing. A backup circuit may have lower bandwidth, so failover policy can prioritize essential traffic rather than allowing every application to compete equally. VPN links between Nigerian branches or international offices should be documented with subnets, routing and security policy. Network segmentation should separate guest, employee, server and device traffic according to operational need.
The FG-81F’s 128GB onboard storage supports local logging, which can help administrators investigate events and performance issues. Larger organizations may require centralized retention, alerting and reporting beyond what local storage alone provides. Procurement should clearly identify the FortiGuard/FortiCare bundle, duration, renewal process, implementation, optics and mounting accessories. Do not assume an advertised online price represents the final deployed cost or the same subscription package. FourTeck Nigeria can provide regional IT project context, while customers operating across Nigeria and Tanzania can standardize policy naming, documentation and lifecycle management. For a meaningful quotation, send the exact FG-81F model, quantity, WAN speeds, VPN count, remote users, public services, required security functions and preferred entitlement term. These inputs make it easier to confirm fit and prepare a transparent bill of materials.
FortiGate 81F Seychelles
Seychelles organizations considering FortiGate 81F may place a high value on resilient internet use, secure remote administration and carefully planned procurement because replacement logistics and specialist visits can be more consequential for island deployments. Begin by documenting the primary internet service, any backup path, user/device count and critical applications. If business operations depend on cloud systems, voice or remote connectivity, decide what must continue during an ISP problem and design SD-WAN or failover policy around that priority.
Hospitality, professional-services and distributed operations can also benefit from strong segmentation. Guest wireless should be isolated from administration and server networks; cameras and building devices can be restricted to required destinations; management interfaces should be accessible only to authorized administrators. The FG-81F can enforce these boundaries when the switch and wireless infrastructure are configured with matching VLANs. VPN may connect a Seychelles site to a regional office, cloud environment or remote support team. Define those routes and permissions narrowly and maintain configuration backups off the appliance.
The 128GB onboard storage provides local log capacity, useful when administrators need events retained even if upstream connectivity is disrupted. Longer-term retention and centralized analytics should still be assessed separately. Procurement should confirm the exact FG-81F hardware, FortiGuard/FortiCare entitlement, subscription period, support path, shipping scope and any compatible SFP modules or mounting accessories. Include UPS protection and spare planning appropriate to the site’s operational importance. For a quotation, provide internet speeds, number of users, VLANs, VPN requirements, security services and desired deployment timeline. If the firewall is replacing an existing gateway, include the current configuration and public-IP dependencies early. A well-documented Seychelles deployment reduces avoidable remote troubleshooting and makes future renewal, expansion or replacement decisions easier for both local staff and regional support teams.
Licensing, subscription and renewal guidance
FortiGate procurement commonly combines hardware with FortiCare support and FortiGuard security services. Exact bundle names and included services can change, so a buyer should request the current official Fortinet entitlement description for the proposed SKU instead of relying on an old product page or a generic statement that “UTM is included.” Confirm term length, support level, start/registration conditions and renewal ownership. Record the Fortinet account under which the appliance is registered and keep renewal dates in the organization’s asset register.
A hardware-only appliance may be appropriate in a specific architecture, but organizations expecting web filtering, advanced threat services or other subscription-backed capabilities should ensure the chosen bundle actually covers them. For multi-year budgets, ask for both initial acquisition and renewal planning. This helps procurement compare total lifecycle cost and avoids discovering at expiry that a critical service was not budgeted.
FG-81F quotation checklist
✓ Exact model and quantity
✓ Primary/backup ISP bandwidth
✓ Number of users and devices
✓ VLAN and network segments
✓ Site-to-site VPN peers
✓ Remote-access users
✓ Required FortiGuard services
✓ FortiCare/support term
✓ SFP/optics requirements
✓ Rack or wall mounting
✓ UPS/power requirements
✓ Migration/configuration scope
FortiGate 81F FAQs
What is the difference between FortiGate 80F and 81F?
Fortinet’s official ordering information lists the same basic eight GE RJ45 ports and two RJ45/SFP shared-media WAN ports for both base models, while FG-81F adds 128GB onboard storage. Buyers should still compare current official data sheets and bundle SKUs when ordering.
Does FG-81F include PoE?
The base FG-81F is not the FG-81F-POE variant. If PoE on firewall ports is required, confirm the exact PoE model or plan separate PoE switching. Do not assume PoE from the 81F name alone.
Can FortiGate 81F use two internet connections?
The series supports secure SD-WAN use cases and provides shared-media WAN interfaces. The final dual-WAN design depends on ISP handoffs, routing, addressing and desired failover or application-steering behavior.
How should I size an FG-81F?
Use internet bandwidth, expected growth, user/device count, VPN traffic and the security services that will be enabled. Advanced inspection can materially change effective throughput, so do not size from raw firewall throughput alone.
What information should I send for a Tanzania quote?
Send the exact FG-81F model, quantity, site, ISP bandwidth, number of users/devices, VPN requirements, VLANs, desired security services, preferred subscription term and whether installation or migration is required.
Decision recap
Choose FG-81F because its verified interface layout, FortiGate security platform and 128GB onboard storage fit a documented requirement—not simply because it is a familiar model. Validate bandwidth with the security services enabled, define VPN and segmentation, select the correct FortiGuard/FortiCare entitlement, and include power, optics, mounting and migration in the bill of materials.
For Tanzania projects, FourTeck can use your current internet speed, user/device count, branch connectivity, security requirements and existing network information to frame the quotation discussion. This approach also makes it easier to identify when a smaller or larger FortiGate would be more appropriate.
Consult FourTeck Tanzania about FortiGate 81F
Share your FG-81F quantity, internet bandwidth, number of users, VPN requirements, security-service expectations and deployment location. FourTeck Tanzania can use that information to discuss model fit, licensing, network integration and quotation scope without assuming stock, price or delivery timing.




Reviews
There are no reviews yet.