
FortiGate 40F (FG-40F) Tanzania
FortiGate 40F is a compact Fortinet next-generation firewall built for organizations that need security and WAN connectivity in a small desktop platform. For Tanzanian offices, shops, professional practices, clinics, hospitality sites and distributed branches, the FG-40F can provide a practical edge-security foundation where internet access, site-to-site connectivity and policy control need to be managed together. Fortinet positions the 40F family around converged NGFW and secure SD-WAN functions through FortiOS, with FortiGuard security services available through applicable subscriptions. FourTeck can help buyers translate those capabilities into a procurement plan covering appliance selection, subscription term, VPN requirements, WAN design and deployment scope.
Verified FG-40F hardware
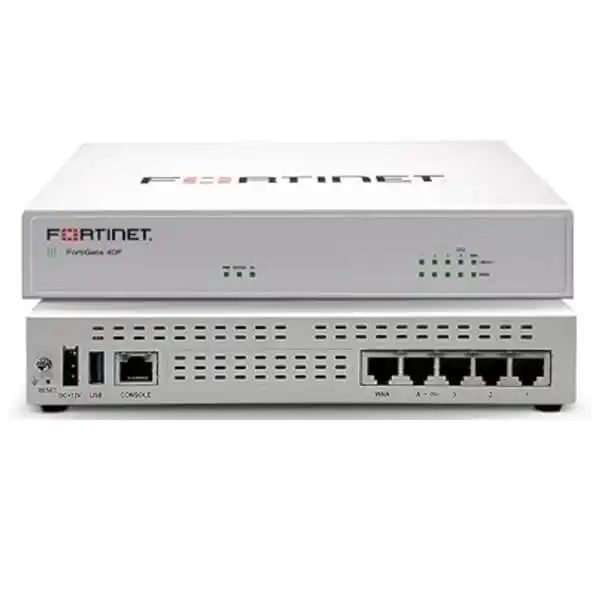
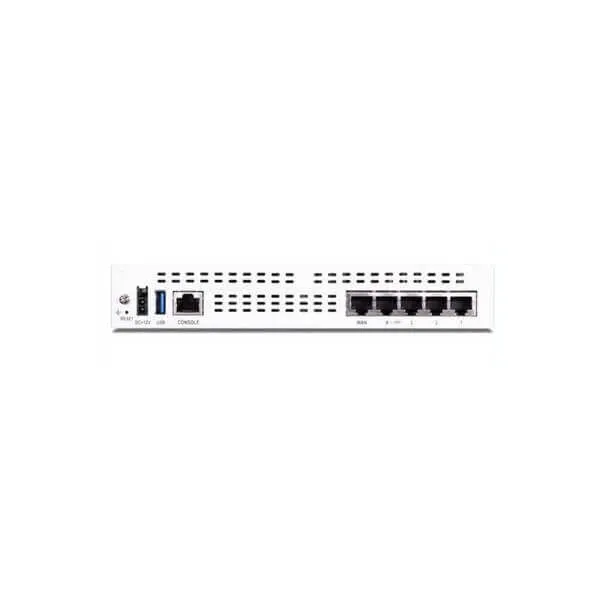
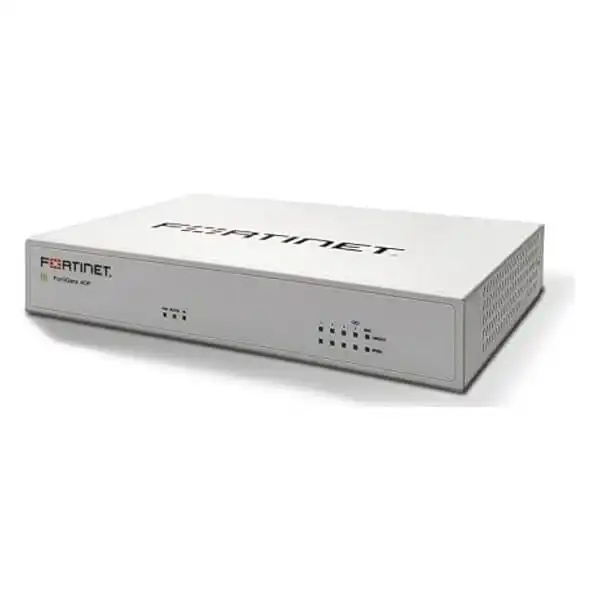
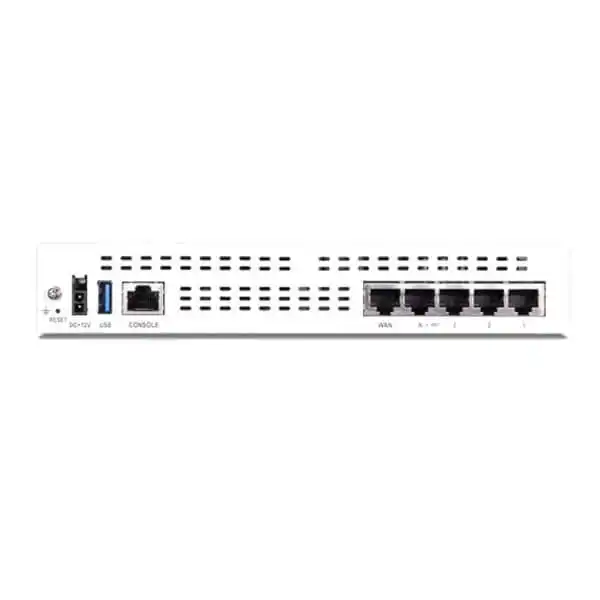
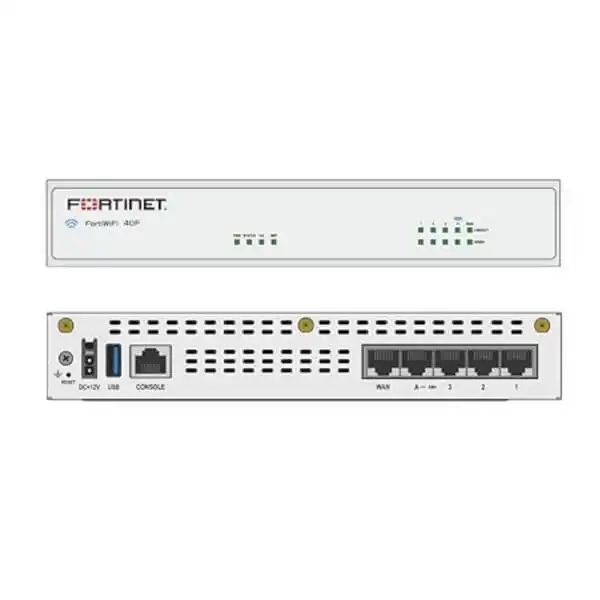
Fortinet lists the FG-40F with five Gigabit Ethernet RJ45 ports, including one WAN port and four internal switch ports. The appliance uses a desktop form factor and is fanless. Its compact format makes it suitable for sites where rack space is limited, although installation planning should still provide stable power, sensible cable management and adequate ventilation.
Security and networking
FortiOS brings firewalling and networking functions into one operating environment. Depending on configuration and licensed services, organizations can use the platform for security policy enforcement, VPN connectivity, application-aware controls, threat-prevention services and secure SD-WAN. Buyers should match subscriptions to the protection features they actually need rather than treating the appliance and security-service term as interchangeable items.
What the FortiGate 40F can solve
A small branch firewall is often expected to do more than block unwanted traffic. It may sit between an ISP circuit and the business LAN, terminate encrypted tunnels to headquarters, separate user and device networks, enforce outbound policies and provide a consistent security template across many locations. The FG-40F is designed for this kind of distributed-edge role. It can be particularly relevant when an organization wants FortiOS policy management at smaller sites while maintaining a common Fortinet architecture across the wider network.
Before purchasing, document internet bandwidth, expected encrypted traffic, number of local network segments, remote-access needs, site-to-site VPN requirements, application mix and required FortiGuard services. Published maximum throughput figures are laboratory measurements and should not be used alone for sizing. Real deployment performance depends on enabled inspection features, traffic characteristics, policy complexity, software version and architecture. A quotation should therefore specify both hardware and the security subscription or support term required for the intended design.
FortiGate 40F features and buying considerations
Compact branch edge
The desktop chassis suits smaller sites that need a dedicated security gateway without a large appliance footprint. Plan the physical location, power adapter placement and cable labeling before installation.
Secure SD-WAN
Fortinet positions the 40F series for converged security and SD-WAN. This is useful where branch connectivity needs policy-based path selection and security controls in the same platform.
VPN connectivity
FortiOS supports encrypted connectivity scenarios that can link branches and remote users. VPN design should account for identity, authentication, routing, address plans and security policy rather than being treated as a single checkbox.
FortiGuard services
Security services are subscription-dependent. Confirm the required bundle and term during procurement so web filtering, IPS, malware protection or other desired services are covered by the chosen entitlement.
FortiGate 40F technical snapshot
| Model | FortiGate 40F / FG-40F |
|---|---|
| Interfaces | 5 x GE RJ45, including 1 x WAN and 4 x internal switch ports |
| Form factor | Desktop |
| Cooling | Fanless, 0 dBA |
| Dimensions | 38.5 x 216 x 160 mm |
| Weight | 1 kg |
| Operating temperature | 0°C to 40°C |
FortiGate 40F Tanzania
Organizations searching for FortiGate 40F Tanzania commonly need more than a hardware-only quotation. The useful starting point is to identify what the firewall will protect and how the site connects to the rest of the organization. A small office may need one primary ISP, outbound security policies and remote-access VPN. A branch may require an encrypted tunnel to headquarters, segmentation between staff and guest networks, and standardized policies that mirror other locations. Retail and service locations may also need separation for point-of-sale, business systems, guest connectivity and managed devices. These differences influence configuration even when the same FG-40F hardware is selected.
For Tanzania procurement, prepare a short network brief before requesting pricing. Include internet circuit speeds, whether more than one WAN connection is planned, approximate device count, VLAN requirements, VPN peers, authentication needs and the security services expected from FortiGuard. If the site already uses Fortinet elsewhere, note the existing FortiOS environment and any centralized management requirements. This helps avoid receiving a device-only quote when the project actually requires a subscription bundle, support coverage or configuration work.
Environmental planning matters as well. The FG-40F is a fanless desktop appliance, so it is quiet and compact, but it should still be installed in a clean, ventilated position with stable power and documented cabling. For organizations operating multiple Tanzanian branches, standardizing interface names, VLAN IDs, VPN naming and policy templates can simplify support. Buyers comparing models should size around enabled security inspection and expected traffic rather than headline firewall throughput alone. FourTeck can discuss the FortiGate 40F alongside wider Tanzania network-security requirements and help structure a quotation around the actual deployment.
FortiGate 40F Dar es Salaam
A FortiGate 40F Dar es Salaam deployment can suit a compact corporate office, professional-services practice, retail outlet, hospitality location or branch that needs a dedicated security gateway at the internet edge. In a busy commercial environment, the buying question is usually not simply whether a firewall can pass traffic. The design should define which users and devices belong on separate networks, what applications require internet access, which services must be reachable over VPN, and how the business will respond if its primary WAN path becomes unavailable.
For a Dar es Salaam branch connected to a headquarters or cloud environment, the FG-40F can be planned as part of a site-to-site VPN design. Document local subnets, remote subnets, routing ownership and authentication before configuration. If a secondary ISP is expected, confirm interface availability and the desired failover or SD-WAN behavior. Security subscriptions should be chosen based on required inspection functions and renewal expectations. The appliance itself and the FortiGuard service entitlement are distinct procurement elements, so quotation requests should make the desired term clear.
Physical deployment should include a stable power source, cable labels and a location protected from dust, accidental disconnection and heat buildup. Maintain a configuration record covering WAN addressing, DNS, VLANs, VPN peers and administrative access. This becomes particularly valuable when ISP settings change or support is handed between teams. Dar es Salaam buyers can also review regional Fortinet options through FourTeck’s Fortinet specialist site when coordinating multi-country projects. For a Tanzania-focused requirement, the quotation should remain anchored to the actual local topology, subscription scope and implementation responsibilities rather than generic package descriptions.
FortiGate 40F Mwanza
For businesses evaluating FortiGate 40F Mwanza, a practical use case is a smaller site that needs consistent security controls while connecting to central applications, cloud services or another office. The FG-40F’s compact desktop design makes it appropriate to consider where there is no dedicated equipment rack, but the network plan should still be treated professionally. Identify the ISP handoff, internal switching layout, wireless access-point relationship and any VLAN boundaries before the firewall is installed.
A Mwanza branch may need encrypted connectivity to systems hosted elsewhere. In that case, document which traffic should cross the tunnel and which traffic should use local internet breakout. Define how DNS, routing and security policies will behave during tunnel or WAN failure. If the business expects a second connectivity path later, planning the addressing and SD-WAN policy in advance can reduce redesign. Fortinet positions the 40F family around converged security and SD-WAN, but the value of those capabilities depends on correct policy design and operational monitoring.
Procurement teams should request a quote that distinguishes the FG-40F appliance, FortiCare/support needs, FortiGuard service bundle and any installation or configuration scope. Avoid selecting a subscription only by bundle name; map required controls such as intrusion prevention, web security or malware protection to the current Fortinet offering and term. Where several branches are being standardized, document a repeatable baseline for administrator access, logging, VPN naming, VLANs and backup procedures. FourTeck can use this information to help frame a more precise product discussion. For broader African coordination, FourTeck Africa provides a regional path for multi-market technology enquiries while the Tanzania requirement remains focused on the Mwanza site’s real network design.
FortiGate 40F Arusha
A FortiGate 40F Arusha requirement may come from hospitality, travel, professional services, education, retail or a distributed organization operating a smaller branch. These environments often combine staff systems, guest or visitor connectivity, cloud applications and remote access. The firewall design should therefore start with segmentation. Separating business devices from guest traffic and other device classes can make policy control clearer and reduce unnecessary trust between networks.
For hospitality or customer-facing sites, continuity planning is also important. If two internet services are available, determine whether the goal is simple failover, traffic distribution or application-aware path selection. Secure SD-WAN capabilities can be relevant, but WAN behavior must be deliberately configured and tested. A backup connection that exists physically but has never been validated under failure conditions may not provide the resilience expected by the business. Likewise, VPN tunnels should be tested for routing, DNS and application access rather than judged only by tunnel status.
When requesting an FG-40F quotation for Arusha, include the desired security-service term and note whether configuration, migration or remote assistance is required. If replacing another firewall, provide current WAN details, VLANs, VPN peers and any inbound services that need to be recreated. Migration is an opportunity to remove obsolete rules rather than copy every legacy policy. Keep a clean rule base with meaningful names and documented business owners. The compact FG-40F can serve as the security edge, while switches and access points handle the local LAN and wireless layers. Buyers planning related network upgrades can discuss those dependencies at the same time so port, VLAN and addressing choices align with the firewall design.
FortiGate 40F Dodoma
For a FortiGate 40F Dodoma deployment, the central design question is whether the appliance fits the site’s security workload and connectivity pattern. A small administrative office or branch may need controlled internet access, encrypted links to another location, remote-user connectivity and separation between departments or device groups. Those requirements should be converted into a simple network diagram before procurement so that the firewall, switching and ISP design are considered together.
Organizations with formal governance requirements should also plan logging and administrative access. Decide who is allowed to manage the firewall, how credentials are protected, where configuration backups are retained and whether logs need to be forwarded to another platform. FortiGate deployments become easier to operate when policy names, objects and address groups use a consistent convention. For multi-site organizations, the same baseline can be adapted to each branch without making every location identical where business needs differ.
The FG-40F has five GE RJ45 interfaces in Fortinet’s published hardware specification, with one WAN and four internal switch ports. That physical interface count should be considered against the intended topology. Additional network segmentation can be carried using VLANs where the connected switching environment supports the design. Subscription selection is another key procurement step: confirm which FortiGuard services are required and how long the organization wants the entitlement to run. Do not assume a hardware purchase automatically includes every security service. A detailed Dodoma quote request should identify appliance quantity, term, VPN requirements, installation expectations and any need to integrate with an existing Fortinet environment.
FortiGate 40F UAE
The FortiGate 40F UAE market is relevant to businesses buying for compact offices, branches and regional rollout projects. When an organization operates sites across the Gulf and Africa, using a common firewall family can simplify policy standards and operational documentation. The FG-40F should still be sized per location, because a small sales office and a bandwidth-heavy branch may have very different inspection loads even if both appear similar by employee count.
UAE procurement discussions often involve appliance-only and subscription-bundle options. Buyers should state the intended FortiGuard services and term rather than requesting an ambiguous “licensed firewall.” They should also identify whether the device will be deployed locally or form part of a multi-country project. Configuration templates can standardize VPN naming, administrative controls, logging and SD-WAN policy while preserving local addressing and ISP differences. For current UAE-focused product enquiries, see FourTeck’s FortiGate 40F UAE page, which provides a regional enquiry route for the same model.
For a Tanzania organization sourcing through a wider regional project, maintain a clear asset and entitlement register by country and site. Record serial-number ownership after purchase, subscription dates, configuration backup location and responsible administrators. This operational discipline matters as much as the initial device selection. A FortiGate 40F can be a strong fit for the small-branch role, but the final design should account for traffic inspection, VPN use, redundancy expectations and growth rather than relying on a single headline performance figure.
FortiGate 40F Uganda
A FortiGate 40F Uganda deployment can support a small business site or branch that needs a Fortinet security edge with VPN and SD-WAN capabilities. For organizations connecting Uganda and Tanzania operations, consistent firewall policy structures can make cross-border IT operations easier. Start by documenting the applications that need inter-site access, the networks that should remain isolated and the traffic that can use direct internet breakout.
The appliance should be selected together with an appropriate security subscription. FortiGuard services are licensed according to the chosen offering and term, so procurement teams should confirm the current bundle contents at quotation time. If the branch needs only a basic gateway today but expects deeper inspection later, that future requirement should be included in sizing. Enabling additional security functions changes the processing workload, and actual results depend on configuration and traffic mix.
For Uganda-focused project coordination, FourTeck Uganda is the relevant regional enquiry path. A useful quote brief should include appliance quantity, WAN bandwidth, VPN peers, VLAN count, subscription duration and implementation expectations. If the same design will be repeated in Tanzania, Uganda and other markets, specify which elements must be standardized and which are site-specific. This reduces configuration drift and makes later troubleshooting easier. Keep network diagrams, firewall backups and entitlement records under controlled administrative ownership rather than leaving the deployment dependent on undocumented settings.
FortiGate 40F Kampala
Businesses looking for FortiGate 40F Kampala may be securing a head office department, satellite office, shop, clinic or professional branch. The FG-40F is most useful when its role is clearly defined: internet edge, branch VPN endpoint, segmented gateway, or a combination of these. Before installation, identify which internal networks exist and whether staff, guest, voice, camera, point-of-sale or management devices require separate policy zones.
Kampala sites with multiple connectivity options can evaluate secure SD-WAN as part of the design. Define the desired behavior for primary-path failure, recovery and application routing. Test failover with real applications because a route change alone does not guarantee that every session will recover seamlessly. For site-to-site VPN, coordinate address plans with remote offices to avoid overlapping subnets, a common source of unnecessary complexity in multi-branch deployments.
The purchase request should specify whether the requirement is hardware only or includes FortiGuard and FortiCare coverage. Security-service terms should align with organizational renewal planning, particularly when several firewalls are deployed at different dates. If Kampala is one site in an East African rollout, a common renewal calendar may simplify administration where commercially practical. The same configuration baseline can also define naming, logging, administrator controls and backup procedures. FourTeck’s Uganda regional channel can support project discussions, while the technical design should remain grounded in the actual bandwidth, users, devices, inspection functions and business-critical applications at the Kampala location.
FortiGate 40F Arua
A FortiGate 40F Arua project may involve a compact branch where dependable remote connectivity is central to daily work. In such a site, the firewall is not only a security boundary; it can also be the point where branch routing, VPN policy and WAN resilience come together. Document the applications hosted outside the branch and decide whether they should traverse an encrypted tunnel, access cloud services directly or follow different paths based on policy.
Where internet options vary, design for the connectivity actually available at the site. If a backup link is planned, confirm how it connects to the network and how failover will be detected. Keep monitoring and troubleshooting requirements in mind. A design that is simple to explain and document is usually easier to support than one with unnecessary policy complexity. The FG-40F’s compact hardware can fit smaller environments, but it should be protected by stable power and installed where cabling cannot be easily disturbed.
For procurement, include the subscription term, desired security services, VPN requirements and whether remote configuration assistance is part of the scope. If Arua connects to a central office, provide the remote firewall model and relevant addressing information so compatibility and tunnel design can be reviewed. FortiOS supports broad networking and security functions, but every deployment still needs deliberate configuration. Maintain a post-installation record of WAN settings, VLANs, VPN parameters, security policies, administrator access and backup location. That record is especially valuable for branches where on-site troubleshooting resources may be limited and remote support needs accurate information.
FortiGate 40F Mbarara
For FortiGate 40F Mbarara enquiries, buyers should begin with the branch’s operational priorities. A retail or service location may need separation between transactional systems and general user traffic. An office may prioritize VPN access to headquarters and cloud applications. A small institution may need web security and controlled access for different user groups. These are policy requirements, and they should drive the configuration rather than simply accepting default rules.
The FG-40F’s five GE RJ45 ports provide a straightforward physical interface layout for compact sites. VLAN-capable switching can extend logical segmentation beyond the number of physical internal interfaces where the architecture requires it. If wireless networks are present, coordinate SSIDs and VLAN assignments with firewall policies so guest and corporate traffic are handled appropriately. Keep management access restricted to authorized administrators and avoid exposing administrative interfaces unnecessarily.
Subscription planning should be explicit in the purchase request. State whether the organization requires a FortiGuard security bundle, the desired term and any support expectations. If the firewall is replacing an older gateway, inventory existing rules and VPNs before migration. Not every old policy should automatically be carried forward; validate business ownership and remove obsolete entries where appropriate. For a multi-branch Uganda environment, standard configuration documentation can make Mbarara easier to support alongside Kampala, Arua and Gulu. FourTeck can discuss the FG-40F as part of that broader regional architecture while keeping the final recommendation tied to measured bandwidth, enabled security functions and realistic growth expectations.
FortiGate 40F Gulu
A FortiGate 40F Gulu deployment can be planned for a smaller office that needs centralized security policy and encrypted connectivity without a large physical firewall. The first task is to map the local network. Identify ISP equipment, switches, access points, business servers or appliances, user devices and any separate guest or operational networks. This map helps determine where the FG-40F sits and which interfaces or VLANs need firewall policy.
For remote branches, VPN reliability and supportability often matter more than feature count. Use clear address objects and policy names, avoid overlapping branch subnets and document tunnel dependencies. If a secondary WAN path is introduced, test how VPN and application traffic behave when the preferred circuit fails. Secure SD-WAN can provide policy-driven WAN control, but it should be configured against business goals such as availability, path quality or application routing.
Gulu procurement should also distinguish hardware from recurring services. Confirm current FortiGuard bundle contents and FortiCare options during quotation because service packaging can change over time. Align renewal ownership with the team responsible for the firewall so protection does not depend on an undocumented subscription date. For organizations operating branches across East Africa, use a shared deployment checklist that covers firmware policy, configuration backup, administrator security, logging, WAN details and VPN testing. This creates a repeatable operational standard while allowing each site to retain the network settings it actually needs.
FortiGate 40F Kenya
FortiGate 40F Kenya searches often reflect demand for a compact Fortinet firewall for small offices and branches. For businesses that also operate in Tanzania, the model can be evaluated as part of a standardized East African branch architecture. Standardization can reduce support complexity, but only when each site is properly sized. A branch with heavy encrypted traffic or extensive security inspection may require a different appliance even if the employee count looks similar.
Create a branch template that defines VLAN structure, administrator controls, VPN naming, logging, DNS behavior and WAN monitoring. Then adapt the template to each Kenyan site’s addressing and ISP details. If dual connectivity is required, document the desired SD-WAN behavior and test failover. For VPN connectivity to Tanzania or another country, coordinate IP addressing early so networks do not overlap. This avoids complicated translation work later.
For Kenya-specific enquiries, FourTeck Kenya provides a regional project route. When requesting an FG-40F quote, state the required FortiGuard term, quantity and whether installation or configuration support is expected. Procurement teams should also maintain entitlement and renewal records across the fleet. The best purchasing outcome is not simply obtaining the appliance; it is obtaining the correct hardware, service entitlement and implementation scope for the branch’s security requirements. This is particularly important when a project spans Kenya, Tanzania and Uganda and needs a consistent operating model across countries.
FortiGate 40F Kuwait
A FortiGate 40F Kuwait requirement can arise from a compact branch, retail environment or distributed enterprise site that needs Fortinet NGFW and SD-WAN functions at the edge. Buyers should evaluate the firewall in the context of the site’s WAN bandwidth and security inspection profile. The FG-40F is compact, but physical size does not determine security capacity; configuration and enabled services materially affect workload.
For a regional company linking Kuwait with offices in Africa, site-to-site VPN design should use coordinated address plans and clearly documented routing. Decide which traffic needs to cross the corporate tunnel and which can break out locally. If more than one ISP is used, define health checks and failover behavior. Operational teams should also decide how configuration backups, firmware management and logs are handled across the fleet.
FourTeck’s Kuwait technology site is the relevant network link for Kuwait-focused procurement discussions. A quotation request should specify FG-40F quantity, security subscription term, support expectations and deployment responsibilities. If the firewall is one component of a larger branch build, include switch, wireless and IP addressing requirements in the planning conversation. This allows segmentation and VLAN design to be coordinated rather than added after the firewall has already been configured. Maintain a clean deployment record for each site so future renewals and support cases can be handled with accurate information.
FortiGate 40F Ghana
For FortiGate 40F Ghana deployments, the model can be considered for compact sites needing firewall policy, VPN connectivity and secure SD-WAN in a desktop appliance. A buyer should first identify whether the site is standalone or part of a larger organization. Standalone sites may prioritize internet security and remote-user access, while branches may need standardized tunnels, logging and policy controls connected to a central architecture.
Subscription selection should be tied to required security outcomes. Confirm the current FortiGuard services included in the proposed bundle and the desired subscription term. If web filtering, intrusion prevention or malware protection is required, ensure those functions are covered by the selected entitlement. Avoid comparing quotations solely by hardware price when the included service terms differ. Also clarify whether configuration, migration or ongoing support is part of the commercial scope.
For organizations coordinating Ghana and Tanzania locations, keep a common network documentation format. Record WAN circuits, addressing, VLANs, VPN peers, security policies, administrator ownership and renewal dates. Standard documentation makes remote troubleshooting more efficient and helps prevent configuration drift. If the site uses dual WAN connectivity, define and test failover behavior rather than assuming the backup path will work automatically. The FG-40F can provide the branch security platform, but reliable operation depends on disciplined design, correct licensing and maintained configuration records.
FortiGate 40F Nigeria
A FortiGate 40F Nigeria project may suit a smaller branch, professional office, retail site or distributed location where a compact security gateway is required. The appliance can combine firewall policy with VPN and secure SD-WAN capabilities through FortiOS, helping organizations avoid treating networking and security as entirely separate edge functions. The actual configuration should be based on the site’s traffic and risk profile.
Where connectivity resilience is important, document primary and secondary WAN services and the desired behavior during degradation or failure. SD-WAN policy can be designed around link health and application requirements, but it must be tested under realistic conditions. For branches connected to headquarters, coordinate address plans and tunnel routing before rollout. Clear standards are especially useful when many small sites are deployed by different teams.
Procurement should identify whether the quote includes only the FG-40F hardware or also FortiGuard and FortiCare services. Compare service term and scope alongside price. If migrating from an existing firewall, inventory active VPNs, inbound services and policy rules and validate which ones remain necessary. Keep post-deployment backups and an entitlement register. For cross-country organizations, this operational record can be shared with the team managing Tanzania and other African sites, making renewals, support and security reviews easier to coordinate without assuming every location has identical requirements.
FortiGate 40F Seychelles
FortiGate 40F Seychelles buyers may be securing a compact office, hospitality property, retail location or branch where space is limited but business connectivity is important. The fanless desktop design is convenient for smaller environments, yet the firewall should still be installed in a controlled position with stable power and sensible airflow. Cable labels and a simple port map can reduce troubleshooting time when ISP or LAN changes occur.
Hospitality and customer-facing environments often need clear separation between business systems and guest connectivity. Plan VLANs and firewall policies so guest traffic does not receive unnecessary access to internal resources. If the site connects to a central reservation, finance or corporate system over VPN, document tunnel routing and DNS dependencies. Where backup internet is available, define whether it is for failover only or should participate in SD-WAN policy during normal operation.
A Seychelles quotation request should specify appliance quantity, FortiGuard subscription needs, support term, VPN requirements and implementation scope. If the site is managed remotely from Tanzania or another country, agree on administrator access controls and configuration-backup procedures. Avoid leaving the firewall dependent on a single undocumented administrator account. The FG-40F can provide a consistent Fortinet edge for smaller locations, but procurement and deployment should remain tied to measured bandwidth, enabled inspection services, segmentation needs and realistic growth.
Deployment and configuration guidance
Start with a network diagram and a written policy objective. Record ISP addressing, internal networks, VLAN IDs, DHCP ownership, DNS behavior, VPN peers and required inbound services. Decide which administrative interfaces are permitted and restrict management access to trusted sources. Create named address objects and groups instead of relying on unclear rules. Use meaningful policy names that describe the business purpose.
For dual-WAN designs, define health checks and desired failover logic. For site-to-site VPN, verify routing in both directions and test applications, not only tunnel establishment. For remote access, align authentication and user-group design with organizational identity controls. Maintain configuration backups before and after major changes. Firmware updates should be planned against Fortinet guidance and business maintenance windows rather than applied casually to production systems.
FortiGuard licensing and renewal planning
FortiGate hardware and FortiGuard security services should be treated as related but distinct procurement components. Fortinet offers service bundles and support options whose names and contents can evolve. At quotation time, confirm the current bundle description, included services, term and support level. The right selection depends on which security controls the organization intends to enable and how the firewall will be operated.
Maintain a renewal register that records device identity, site, entitlement, start and expiry dates, responsible owner and renewal decision. Multi-site organizations can benefit from aligning renewal planning where practical, but should not sacrifice required coverage merely to create matching dates. Review the firewall’s role before renewal: changes in bandwidth, application use, inspection requirements or branch importance may justify reassessing the appliance or service bundle.
Related Fortinet and network-security planning
The firewall is one layer of the branch network. Switching determines how VLANs are delivered to wired devices, wireless infrastructure extends those segments to Wi-Fi users, and identity systems influence who receives access. Logging and centralized management may become more important as the number of sites grows. Buyers should therefore consider the FG-40F in the context of the complete branch design rather than as an isolated box.
For wider regional requirements, FourTeck’s UAE technology portal, Kenya site, Uganda site, Ghana site and Nigeria site can support region-specific project conversations. These links are useful when a Tanzania-led deployment forms part of a wider multi-country standardization exercise.
FortiGate 40F FAQ
Is the FortiGate 40F suitable for a small office?
Fortinet positions the 40F family for distributed enterprise sites and compact security deployments. Suitability depends on bandwidth, enabled security inspection, VPN use, traffic mix and growth. Size the appliance against the actual workload rather than employee count alone.
How many Ethernet ports does the FG-40F have?
Fortinet’s published specification lists five Gigabit Ethernet RJ45 ports: one WAN port and four internal switch ports.
Does FortiGate 40F support SD-WAN?
Yes. Fortinet positions the 40F series as a converged NGFW and secure SD-WAN platform. The practical result depends on WAN topology, policy configuration and monitoring design.
Do I need a FortiGuard subscription?
The appliance can be purchased in different commercial configurations, while FortiGuard services provide subscription-based security capabilities. Choose the service package according to required protection functions and confirm current bundle contents at quotation time.
Can the FG-40F connect branches by VPN?
FortiOS supports VPN use cases. A successful branch design requires coordinated IP addressing, routing, authentication, policy and testing at both ends of the tunnel.
What should I provide for a FortiGate 40F quotation?
Provide quantity, location, internet bandwidth, WAN count, VPN requirements, approximate network scope, required security services, subscription term and whether installation, migration or configuration assistance is expected.
Quotation checklist
For a useful FG-40F quote, share the number of appliances, deployment locations, primary and backup internet circuits, expected bandwidth, required VLANs, VPN peers, remote-access requirements, FortiGuard security-service needs, desired subscription term, current firewall model if this is a migration, and whether implementation assistance is required. For multi-country rollouts, also identify which configuration standards must be common across sites.
Decision recap
FortiGate 40F is a compact Fortinet NGFW designed for secure networking at smaller distributed sites. It provides five GE RJ45 ports in a fanless desktop chassis and operates with FortiOS, bringing firewall and networking capabilities together. The correct purchase decision should account for real inspection workload, WAN architecture, VPN requirements, subscription scope and operational support. For Tanzania deployments, prepare a site-specific network brief so the quotation reflects the required hardware, service entitlement and implementation scope.
Discuss your FortiGate 40F requirement
Share your Tanzania site details, connectivity, VPN requirements and preferred FortiGuard term with FourTeck. A clear requirement helps align the FG-40F hardware, subscription and deployment plan with the branch environment and avoids ambiguity between appliance-only and security-service quotations.




Reviews
There are no reviews yet.