
FORTINET NEXT-GENERATION FIREWALL
FortiGate 120G (FG-120G) Tanzania
FortiGate 120G is built for organizations that need high-speed firewalling, inspected application traffic, secure branch connectivity and room for network growth. Fortinet specifies firewall throughput of 39/39/28 Gbps for 1518/512/64-byte UDP packets, IPS throughput of 5.3 Gbps, NGFW throughput of 3.1 Gbps and threat-protection throughput of 2.8 Gbps. For Tanzanian IT teams, those figures are useful starting points, but a correct purchase decision should also account for encrypted traffic, FortiGuard services, VPN demand, internet bandwidth, interface requirements, high availability and future expansion.

FortiGate 120G Overview and Verified Hardware
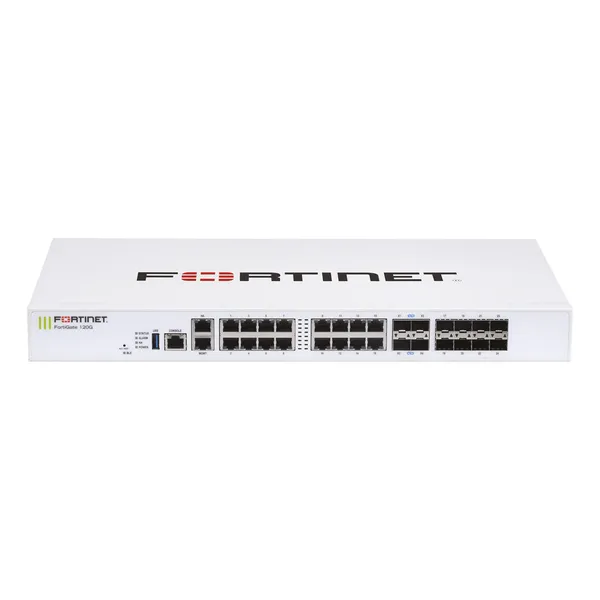
The FG-120G is a rack-mount 1RU security appliance in Fortinet’s 120G Series. Its port layout includes 18 GE RJ45 ports, comprising dedicated management and HA ports plus switch ports, eight GE SFP slots and four 10GE SFP+ slots. Fortinet identifies SP5 hardware acceleration and dual AC power supplies for the FG-120G. The related FG-121G adds onboard SSD storage, so procurement teams should not assume storage specifications from the 121G apply to the 120G. This distinction matters when preparing a bill of materials, comparing quotations or deciding whether external logging and centralized analytics will be used.
Maximum listed firewall throughput for 1518/512-byte UDP traffic; 28 Gbps at 64-byte packets.
Fortinet-listed IPS throughput for sizing intrusion-prevention workloads.
NGFW throughput reference for application control and IPS-enabled traffic profiles.
Threat-protection throughput reference for security-service planning.
What the FG-120G Solves
A modern firewall purchase is rarely only about blocking inbound connections. Organizations increasingly need one enforcement point for internet security, application policies, segmentation, site-to-site connectivity, remote access, WAN path selection and visibility into users and devices. FortiOS brings networking and security functions together, while FortiGuard services can extend protection with subscribed security capabilities. Secure SD-WAN is particularly relevant when a business has multiple internet circuits and wants policy-based path selection, resilience and centralized control rather than maintaining separate routing and security platforms.
The 120G can also fit Fortinet Security Fabric designs that combine FortiGate with switching, wireless, endpoint, management and analytics components. That does not mean every project requires the entire ecosystem. A sensible design starts with actual requirements: number and speed of WAN links, user population, expected encrypted traffic, published applications, VPN tunnels, VLAN count, routing needs, branch count, logging policy, compliance obligations and growth horizon. FourTeck can use those details to structure a quotation instead of treating the firewall model alone as the complete solution.
Interfaces, Deployment and High Availability Planning
The mix of copper GE, SFP and 10GE SFP+ connectivity makes the FG-120G useful where a firewall must connect to access switching, fiber uplinks, ISP handoffs, server networks or aggregation infrastructure. Before ordering optics or cables, confirm media type, distance, fiber mode, connector standard and the interface on the opposite device. The appliance includes dedicated HA and management connectivity, which supports cleaner operational designs where administrators separate management traffic and build resilient firewall pairs.
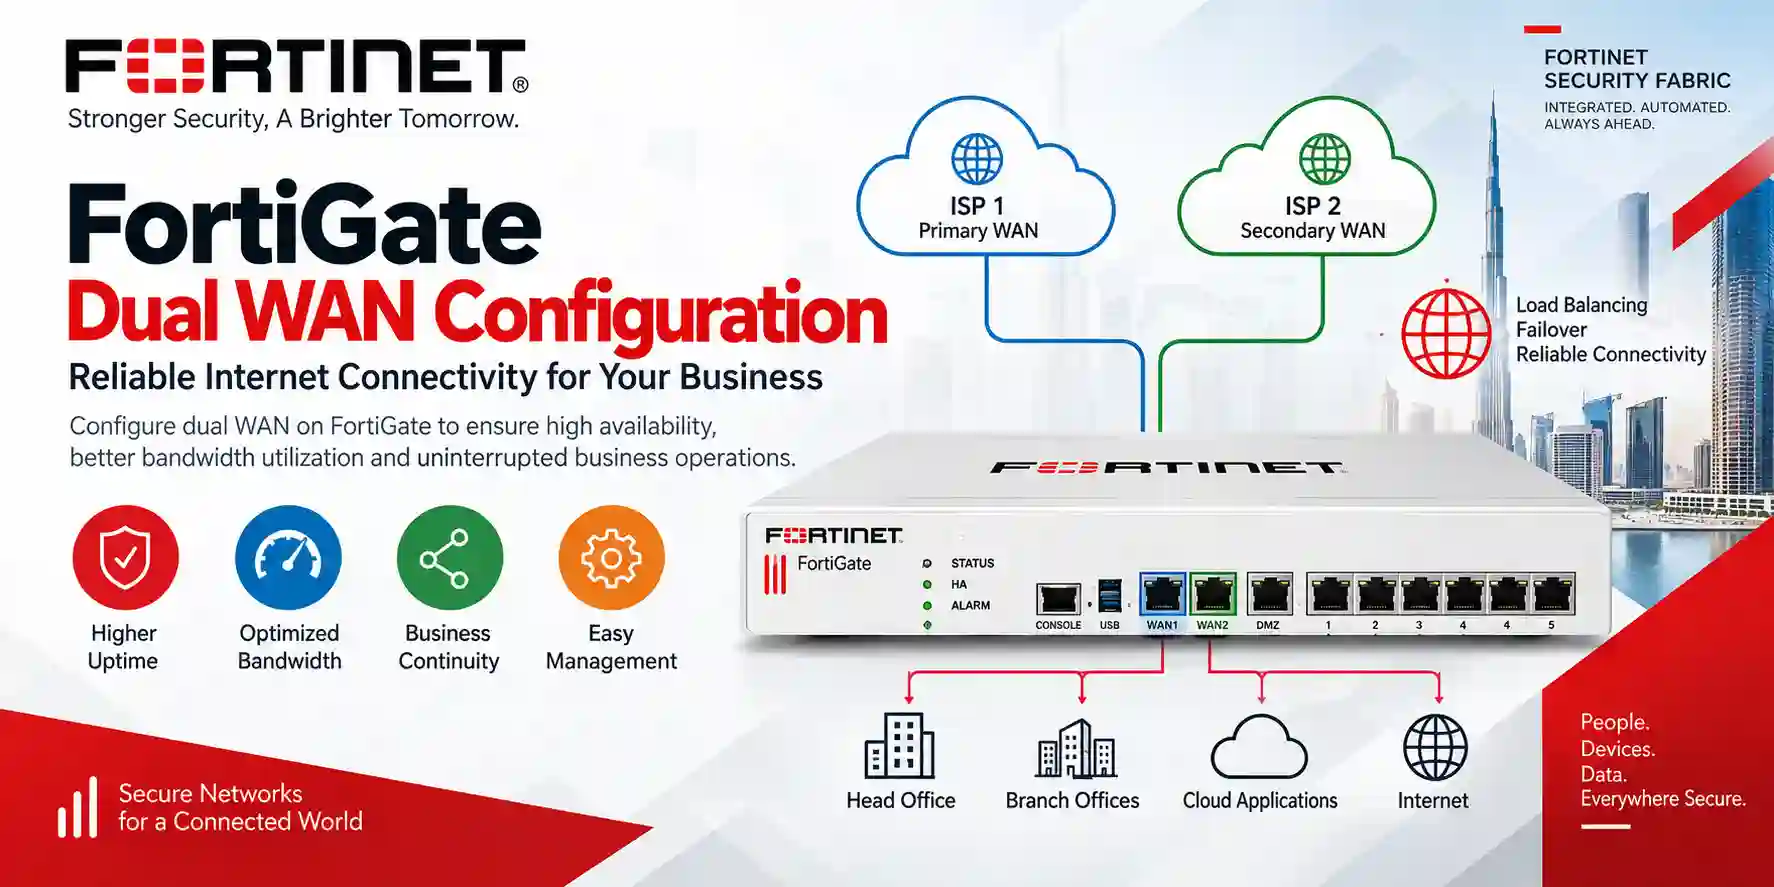
High availability should be considered during procurement, not after installation. A single firewall can protect a network, but an HA design may be appropriate where firewall downtime would interrupt critical services. An HA project also affects switch ports, rack space, power, cabling, licensing decisions, change windows and configuration testing. For dual-ISP environments, review FortiGate dual-WAN planning in Tanzania as a visual reference, while keeping final routing and failover policy aligned with the actual ISP design.

FortiGuard, FortiCare and Subscription Selection
Hardware and subscription requirements should be quoted separately and clearly. Fortinet offers security-service and support bundles for FortiGate platforms, and the appropriate term depends on the security functions the organization plans to use. Buyers should ask whether a quotation includes hardware only or includes FortiCare and FortiGuard services, which bundle is specified, the subscription duration, renewal date and registration requirements. Avoid comparing two prices until the included service level and term are known.
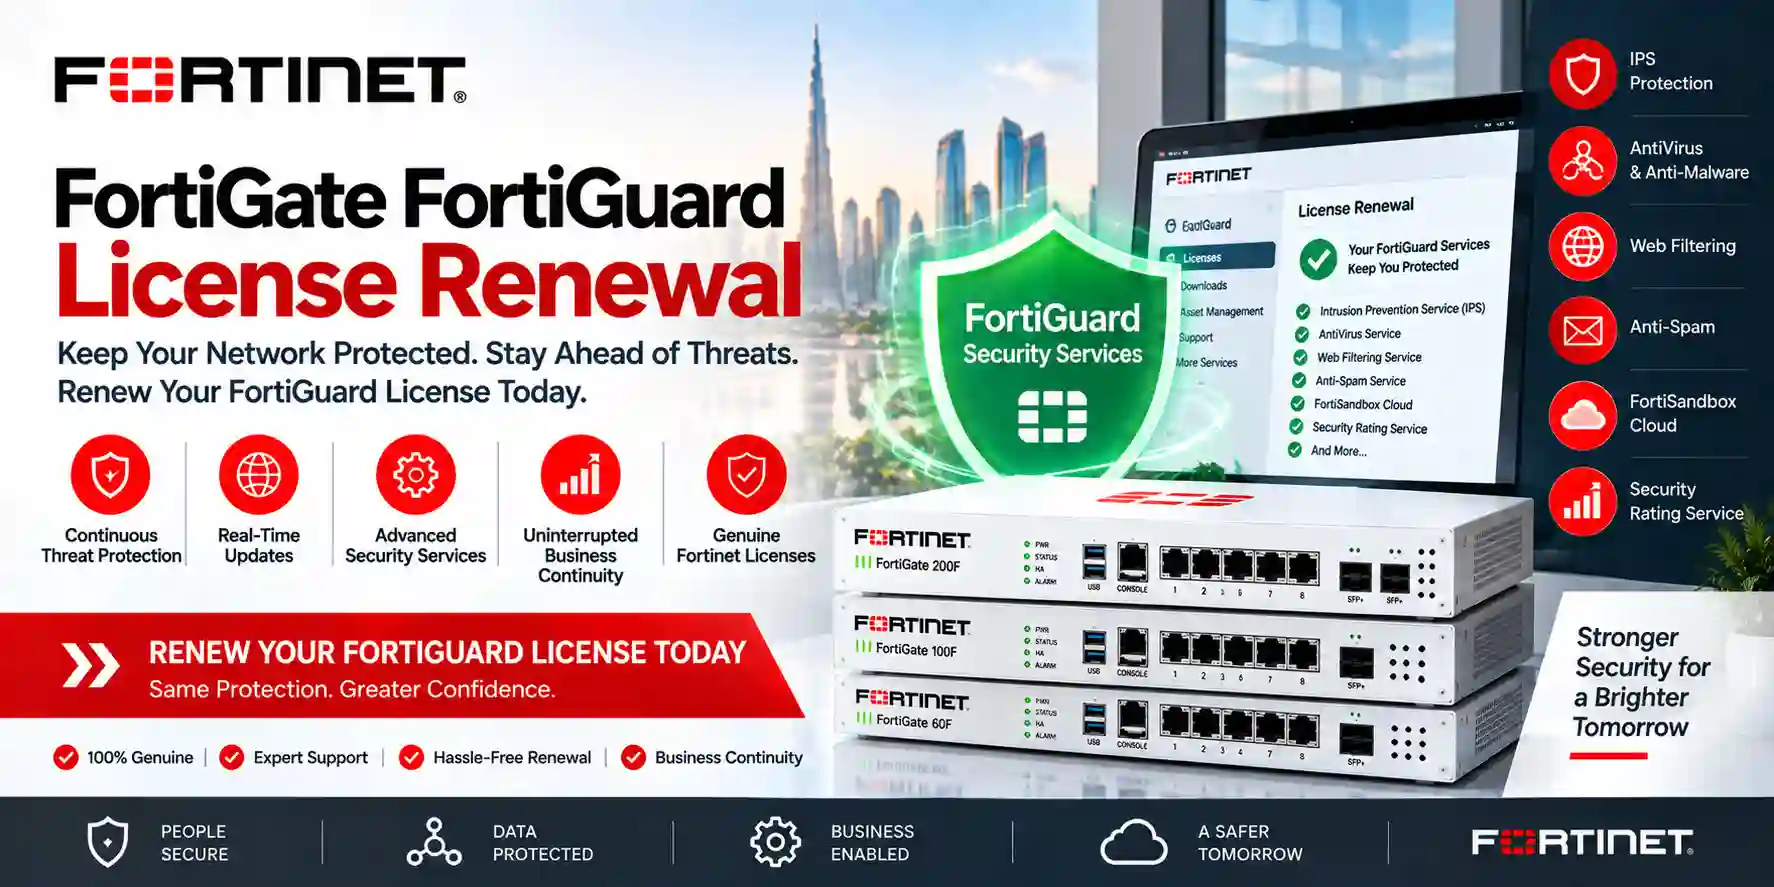
Renewal planning is equally important. Security services that depend on active subscriptions should be budgeted across the intended lifecycle. A three-year procurement may reduce annual purchasing administration compared with repeated one-year orders, while some organizations prefer shorter terms because of budget cycles. The right answer depends on policy and procurement constraints. For a related visual, see the supplied FortiGuard subscription renewal Tanzania reference.
FortiGate 120G Tanzania
Organizations searching for FortiGate 120G Tanzania are commonly trying to solve a practical procurement question: whether this model provides enough inspected-security capacity and connectivity for a head office, campus, large branch, hospitality property, education environment, healthcare network, warehouse, financial-services site or growing multi-site business. The best starting point is not the headline 39 Gbps firewall number alone. Tanzania deployments should be sized around the real internet circuit, east-west segmentation, SSL inspection policy, IPS usage, application control, VPN traffic and expected growth. Where several branch offices connect back to a central location, the design should also account for tunnel counts, routing, centralized policy administration and logging.
Procurement teams should document ISP handoff types and speeds, existing switches, VLANs, public IP requirements, server publishing, remote-user needs and whether a second ISP is planned. If business continuity is important, include an HA pair and redundant upstream/downstream paths in the architecture discussion. Power quality, UPS runtime, rack ventilation and structured cabling should be checked before installation. These items are not firewall specifications, but they determine whether the security appliance can be deployed cleanly and maintained without avoidable outages.
For Tanzania buyers requesting a FortiGate 120G price or quotation, provide the desired hardware quantity, subscription bundle and term, installation location, required optics, rack environment, VPN scope and whether migration from an existing firewall is required. If replacing an older FortiGate, configuration migration should still be reviewed rather than copied blindly, because interface naming, features and security policy objectives may have changed. For broader Fortinet options and regional coordination, the FourTeck Fortinet specialist site can help buyers compare related models and licensing approaches. A properly scoped FG-120G project gives Tanzanian organizations a clearer path from quotation through deployment than a hardware-only purchase based solely on model number.
FortiGate 120G Dar es Salaam
FortiGate 120G Dar es Salaam enquiries often come from organizations with dense office connectivity, multiple internet services, cloud applications, remote users and branch links. In a head-office design, the firewall may sit between ISP circuits and a core switching layer while also terminating IPsec VPNs, enforcing web and application policy and segmenting internal networks. The 120G’s copper, SFP and 10GE interfaces provide flexibility for mixed handoffs, but every port should be mapped before procurement so the bill of materials includes the correct transceivers and cables.
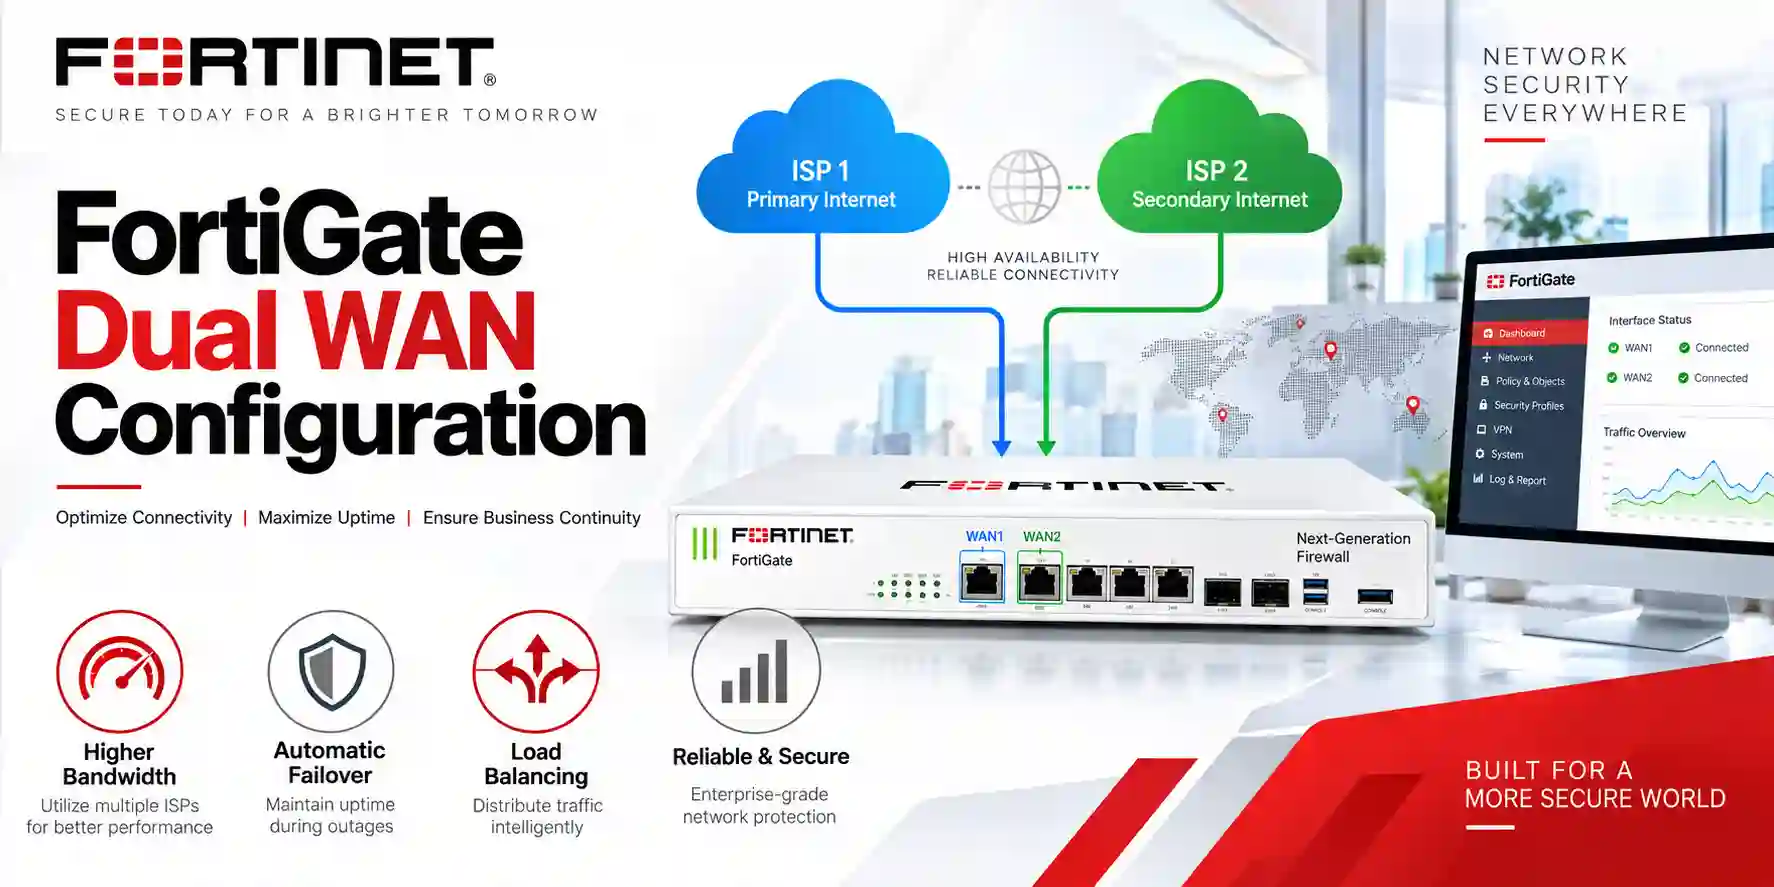
Dar es Salaam businesses planning dual-WAN should define what failover actually means. Some networks need simple backup connectivity; others want active-active path use, application steering or different policies for cloud, voice, guest and corporate traffic. FortiGate Secure SD-WAN can support policy-driven WAN decisions, but the configuration should reflect circuit quality, latency, packet loss and business priorities. See the supplied FortiGate internet load-balancing Tanzania visual for a related planning concept.
A quotation request should state current and planned bandwidth, number of sites, expected remote users, any public-facing servers, desired security subscriptions and whether high availability is required. Organizations moving from a smaller firewall should pay attention to encrypted-traffic inspection and not simply compare raw firewall throughput. Projects with compliance or audit requirements should also define log retention and reporting needs so FortiAnalyzer, FortiGate Cloud or another approved logging architecture can be considered where appropriate. FourTeck can help structure the commercial request around the appliance, subscription, accessories and deployment scope without assuming stock, price or delivery time until these are confirmed for the specific enquiry.
FortiGate 120G Mwanza
For FortiGate 120G Mwanza projects, network resilience can be as important as security inspection. Businesses connecting regional offices, warehouses, service locations or operational sites should map how internet and private connectivity are used today and how much disruption is acceptable if one path fails. The FG-120G can form the security and routing edge of a multi-WAN design, but resilient outcomes depend on the complete architecture: ISP diversity, physical path diversity, switching redundancy, UPS protection, DNS behavior and tested failover rules.
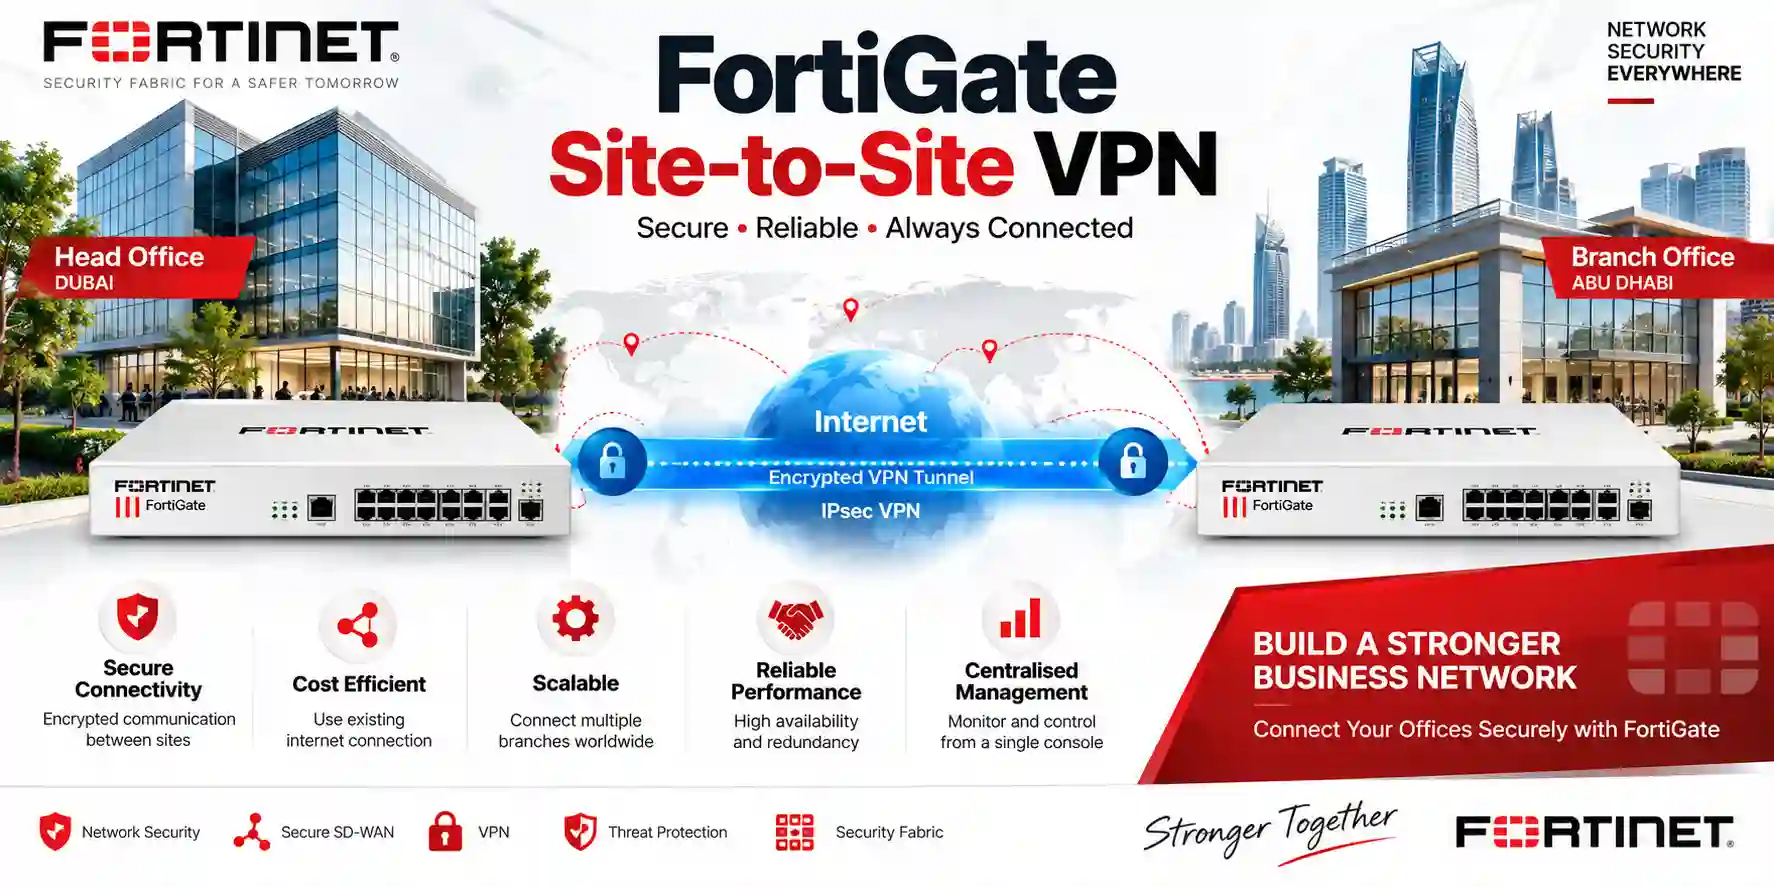
Organizations should separate user groups and systems according to business need rather than operating one large flat LAN. VLAN-based segmentation, firewall policies and controlled inter-zone access can reduce unnecessary exposure between departments, guest networks, servers, cameras, voice systems and management devices. The precise segmentation plan should follow the organization’s risk and operational requirements. When branches need secure access to central applications, IPsec site-to-site VPN is a common design option; the supplied FortiGate site-to-site VPN Tanzania visual illustrates the relevant solution area.
Mwanza buyers should request a quotation that distinguishes the FG-120G appliance from FortiGuard/FortiCare terms and optional transceivers. If a local site has limited on-premises IT staffing, operational simplicity should influence the design: consistent naming, documented interfaces, configuration backups, administrator access controls and centralized monitoring are valuable. Before final sizing, capture peak bandwidth and expected security features rather than average traffic alone. This provides a stronger basis for deciding whether the 120G has suitable headroom and whether an HA pair is justified for the site’s business-continuity requirements.
FortiGate 120G Arusha
FortiGate 120G Arusha deployments may serve hospitality, tourism, education, professional services, logistics and multi-site enterprises that need reliable internet security alongside guest, staff and operational networks. These environments often benefit from explicit segmentation because guest access, payment systems, administration, voice, IoT devices and internal servers have different trust requirements. The firewall can enforce policies between these zones while FortiOS provides a common platform for networking and security functions.
For properties or campuses with wireless networks, firewall sizing should consider internet traffic generated by both managed endpoints and guest devices. If FortiAP and FortiSwitch are part of the planned architecture, confirm the intended topology and management model before ordering. The FG-120G should be evaluated as part of the network, not as an isolated box. Uplink capacity, switching design, access-point density, authentication method and log requirements all affect the overall solution even when they do not change the firewall’s published hardware specifications.
Arusha procurement requests are more actionable when they include the current firewall model, user/device estimates, WAN speeds, number of VLANs, required VPN connections, public services, desired subscription term and target implementation window. Where remote administrators or third-party support teams need access, use controlled administrative methods and least-privilege principles instead of exposing management interfaces broadly. Buyers can also review FourTeck Africa technology coverage when planning cross-border standards. For a Tanzania-specific quotation, the final recommendation should remain grounded in the actual Arusha site design, including rack, power, cabling and security-policy requirements.
FortiGate 120G Dodoma
FortiGate 120G Dodoma enquiries can involve administrative offices, education networks, NGOs, professional organizations and distributed operations that require secure access to central or cloud-hosted systems. For these networks, procurement should begin with traffic flows and security objectives. Identify which users need internet access, which systems communicate between VLANs, which branches require tunnels and which applications need inbound publishing. This allows firewall policy and NAT requirements to be planned before installation rather than discovered during the cutover window.
If the organization depends on cloud collaboration, SaaS or centralized applications, WAN quality and failover deserve careful attention. A secondary circuit only improves resilience when routing, health checks, DNS dependencies and upstream design are tested. Secure SD-WAN policies can help steer traffic according to defined service objectives, while IPsec can protect site-to-site communications. The firewall’s dual power supplies can support resilient power design, but they should be connected according to the site’s electrical and UPS architecture rather than treated as a substitute for power planning.
For budgeting, ask suppliers to show the appliance, support/security subscription, term, accessories and professional services as identifiable line items. This makes comparisons more meaningful and reduces the chance of choosing a lower quotation that excludes required services. Dodoma IT teams should also plan configuration backup, firmware governance, administrator MFA where supported by the chosen design, logging and incident-response responsibilities. A FortiGate 120G purchase is strongest when these operational items are decided alongside the hardware. FourTeck can use a completed network requirement summary to prepare a more precise quotation and deployment discussion without making unsupported assumptions about local inventory or service coverage.
FortiGate 120G UAE
FortiGate 120G UAE buyers frequently compare hardware price, FortiGuard bundle, subscription duration, availability, installation scope and regional export requirements. The FG-120G’s 1RU form factor and mix of GE, SFP and 10GE interfaces make it relevant to head offices, enterprise branches and distributed networks where the firewall must connect to higher-speed switching or multiple WAN services. Fortinet’s published performance figures provide a baseline, but UAE projects should still be sized for the actual security stack and encrypted traffic profile.
Organizations operating across Dubai, Abu Dhabi and other Emirates may also standardize one FortiGate platform across multiple sites. Standardization can simplify templates, renewals, spares planning and centralized administration, but branch sizes can differ considerably. It is therefore better to select each model according to circuit speed, security services, users, tunnels and interface needs than to force every location onto the same appliance. Where the 120G is selected for a hub site, verify whether downstream branches, remote users and public applications materially increase inspection and VPN demand.
For UAE-specific product information, visit FourTeck’s FortiGate 120G UAE page. Cross-border customers sourcing for Tanzania or other African markets should confirm destination requirements, licensing registration, export documentation and delivery terms during quotation. Do not assume a UAE stock statement or price applies to Tanzania. A clear RFQ should specify destination, quantity, hardware model, subscription term, required accessories and whether configuration or migration services are expected, allowing the commercial team to respond to the actual project rather than a generic model enquiry.
FortiGate 120G Uganda
FortiGate 120G Uganda projects often involve organizations linking a main office to branches while maintaining secure internet access, VPN connectivity and centralized policy. The 120G can be evaluated for hub-and-spoke designs, secure SD-WAN and segmented enterprise networks, but the hub’s aggregate traffic is important. A central firewall may inspect traffic from several sites simultaneously, so sizing should account for combined throughput, tunnel traffic, security services and future branch additions rather than the head-office internet link alone.
Before procurement, document whether branches use broadband, fiber, mobile backup or private circuits and whether applications are centralized or cloud based. This affects routing and failover policy. If the organization wants consistent access control across sites, define reusable security zones and policy standards while allowing site-specific exceptions to be documented. Centralized management may be useful for larger estates, but the required Fortinet management and analytics components should be scoped separately instead of assumed to be included with the appliance.
Uganda buyers can use FourTeck Uganda for regional technology enquiries while coordinating Tanzania requirements through the Tanzania channel. A useful RFQ should state the deployment city, WAN speeds, current firewall, number of sites, VPN requirements, HA preference, FortiGuard term and required optics. For organizations comparing the FG-120G with smaller or larger FortiGate models, focus on inspected throughput and growth margin rather than raw firewall performance alone. This produces a decision that is easier to defend technically and financially.
FortiGate 120G Kampala
FortiGate 120G Kampala deployments can suit busy offices that need security inspection, multiple network zones, branch VPNs and resilient WAN connectivity. In a typical design, internet circuits terminate upstream of the FortiGate, while internal interfaces connect toward core or distribution switching. The exact physical design varies, so identify whether ISP handoffs are copper or fiber and whether 10GE connectivity is needed internally. This avoids last-minute transceiver purchases and ensures the chosen switch interfaces match the firewall.
Kampala organizations with hybrid work should define remote-access requirements separately from site-to-site VPN. User authentication, endpoint posture, MFA strategy, access to internal applications and logging all influence the remote-access design. Fortinet also positions ZTNA as part of its secure networking approach, so teams modernizing access can evaluate whether application-specific access is more suitable than broad network-level remote access for some users. The correct architecture depends on applications and identity systems, not only the firewall model.
For a quotation, specify whether the 120G is a new deployment, replacement or HA expansion. Include the desired subscription bundle and duration, because hardware-only and security-bundle quotations are not directly comparable. If a project is part of a multi-country rollout, standardize naming, policy templates, logging and renewal records so operations teams can manage the estate consistently. FourTeck’s Uganda channel can support regional enquiry routing, while Tanzania projects should retain their own destination and implementation details. This separation helps procurement teams avoid mixing pricing, delivery assumptions or service scopes between countries.
FortiGate 120G Arua
FortiGate 120G Arua requirements may be driven by regional offices, logistics operations, NGOs, education environments or organizations that need secure connectivity to a larger headquarters. In these deployments, link reliability and operational simplicity can be central design concerns. A firewall can support multiple WAN paths, but the project should define how each circuit is monitored and which applications move to backup connectivity during an outage. Critical traffic may deserve different failover behavior from guest or bulk traffic.
Site-to-site IPsec is useful where Arua offices need encrypted connectivity to Kampala, Tanzania or another hub. Plan addressing carefully so branch networks do not overlap, especially when several locations will eventually be connected. Define DNS, routing and identity dependencies as part of the VPN design. Segmentation should also separate corporate users, infrastructure management, guest access and specialized devices where appropriate. These design practices improve manageability and can limit unnecessary lateral access.
The FG-120G may provide more capacity than a small branch requires, so buyers should validate sizing rather than choosing the model purely because it is available in a standard catalog. Conversely, a regional aggregation point may justify additional headroom. Provide bandwidth, user/device estimates, expected security services and future site count to the pre-sales team. Ask for appliance and subscription details in writing, including term and accessories. Where power conditions are a concern, include UPS and rack-environment planning in the implementation scope. These steps turn an Arua firewall purchase into a complete network-security project rather than a standalone hardware transaction.
FortiGate 120G Mbarara
FortiGate 120G Mbarara projects should be evaluated against business traffic patterns, especially where a regional site connects to centralized ERP, cloud applications, voice, surveillance or branch services. The firewall’s role may include WAN edge, VPN termination, segmentation and security inspection. Map these functions before sizing so the project does not rely on a single throughput number. Application-control, IPS and threat-protection figures are more informative than raw firewall throughput when security services will be active.
For businesses with multiple ISP links, decide whether the goal is resilience, load distribution or application-aware path selection. Secure SD-WAN can provide policy-based routing and health checks, but success depends on realistic thresholds and testing. A backup link with insufficient capacity may preserve essential applications but not every user workload, so define traffic priorities in advance. Similarly, if an HA firewall pair is required, test failover for both firewall state and surrounding network dependencies.
Mbarara buyers should request the exact FG-120G model, subscription bundle, term, optics and services needed. If replacing another vendor, document current NAT rules, VPNs, routing, security zones and published services, then redesign policies where necessary rather than translating every legacy rule automatically. Remove obsolete objects and rules during migration when change control permits. A clean implementation improves long-term administration. For multi-country organizations, use consistent configuration documentation and renewal tracking while keeping each country’s commercial and delivery details separate. This makes later expansion and support easier for both local administrators and central IT teams.
FortiGate 120G Gulu
FortiGate 120G Gulu deployments can support organizations that require a secure regional edge with connectivity back to a central office or cloud environment. Where bandwidth is valuable, security policy should be designed to protect traffic without creating unnecessary complexity. Start by identifying business-critical applications, internet categories, inbound services and branch dependencies. Then define zones and policies that are understandable to administrators and auditable later. A smaller number of well-structured policies is generally easier to operate than years of accumulated exceptions.
Remote management should be planned securely. Restrict administrative access to trusted paths, use named administrator accounts and strong authentication, and maintain configuration backups. Firmware upgrades should be scheduled with release-note review, backups and rollback planning rather than applied casually to production systems. These operational practices are independent of the FG-120G’s performance but strongly influence the reliability of the deployed security service.
For Gulu procurement, include site connectivity, number of users and devices, VPN requirements, security subscription expectations and any need for HA. If the firewall will connect to fiber infrastructure, list required SFP/SFP+ media and distances so optics can be quoted correctly. Organizations should also decide who owns ongoing tasks such as policy changes, log review, license renewal and incident escalation. Clear ownership prevents a technically capable firewall from becoming poorly maintained after installation. FourTeck can use these requirements to frame a relevant product and licensing discussion without assuming a particular local stock position or delivery schedule.
FortiGate 120G Kenya
FortiGate 120G Kenya enquiries span enterprise branches, headquarters, education, healthcare, logistics, hospitality and other environments where security and WAN functions converge. Buyers should compare the 120G against actual inspected traffic and interface needs. If internet circuits are being upgraded, size for the planned service rather than today’s bandwidth. If SSL inspection, IPS, application control and other services will be used together, leave operational headroom for traffic growth and bursts.
Multi-site Kenyan organizations can use IPsec and Secure SD-WAN to connect branches and select WAN paths according to business policy. However, routing design should be documented, especially when networks use dynamic routing, overlapping address space or multiple hubs. Logging and analytics also deserve attention. Decide whether logs remain on the appliance, use cloud services or feed a dedicated analytics platform according to the organization’s operational and compliance requirements.
For Kenya-specific enquiries, visit FourTeck Kenya. A cross-border organization standardizing FortiGate between Kenya and Tanzania should coordinate subscription terms and policy templates while still obtaining country-specific quotations. Provide quantity, destination, appliance model, bundle duration, accessories, HA requirement and implementation scope. Where a migration is involved, include existing configuration complexity and required downtime window. This helps the supplier distinguish a straightforward hardware supply from a full migration project and produces a more useful commercial response.
FortiGate 120G Kuwait
FortiGate 120G Kuwait projects may require enterprise internet security, branch connectivity, segmentation and secure access to cloud or data-center applications. The appliance’s 1RU format and dual AC power supplies are relevant to rack-based infrastructure, while GE, SFP and 10GE interfaces support varied WAN and LAN connectivity. Buyers should verify the physical media and switch compatibility required for their particular deployment and include suitable optics in the bill of materials.
Security subscriptions should be chosen according to required services rather than simply selecting the lowest hardware price. Ask which FortiGuard and FortiCare components are included, the term and renewal conditions. For environments with strict operational controls, also document administrator access, configuration backup, change approval and logging. If the firewall will be deployed as an HA pair, confirm rack space, redundant power paths, upstream switch design and failover testing as part of the project.
Kuwait buyers working with regional teams can use FourTeck Kuwait for country-specific enquiries. If the same organization has Tanzania operations, avoid assuming that Kuwait pricing, availability or delivery terms transfer between markets. Standardize technical architecture where beneficial, but keep commercial terms and logistics destination-specific. A good RFQ states bandwidth, user/device count, security functions, VPNs, subscription duration and accessories. That information helps determine whether FG-120G is appropriate or whether another FortiGate model should be considered during sizing.
FortiGate 120G Ghana
FortiGate 120G Ghana can be considered for organizations that need a capable enterprise edge firewall with Secure SD-WAN, VPN, segmentation and advanced security services. A head office or regional hub may aggregate traffic from several branches, so sizing should include combined tunnel and inspection loads. For cloud-heavy environments, internet breakout policy and SaaS traffic may also influence the design. Published throughput figures are laboratory references; production planning should include the security features and traffic mix expected in the actual network.
Procurement teams should define whether the requirement is appliance-only, a security bundle, an HA pair or a wider Fortinet solution. If FortiSwitch, FortiAP, FortiManager or FortiAnalyzer are relevant, scope them as separate components with their own licensing and deployment considerations. This makes the quotation transparent and prevents assumptions about what the base firewall includes. For branch VPN designs, document addressing, routing and application dependencies before rollout.
For Ghana regional enquiries, FourTeck Ghana provides a dedicated channel. Organizations comparing Ghana and Tanzania deployments should use a common technical standard only where site requirements are genuinely similar. Bandwidth, ISP media, rack environment, local network size and security policy can vary substantially. Ask for a country-specific quote and verify subscription registration and logistics for the destination. A structured requirements sheet helps procurement compare like-for-like offers and gives technical teams a clearer implementation baseline after purchase.
FortiGate 120G Nigeria
FortiGate 120G Nigeria projects can involve high-traffic offices, distributed enterprises, financial and professional services, education, retail groups and other organizations that need secure internet and branch connectivity. The appliance offers substantial raw firewall capacity, but model selection should focus on the enabled security profile. IPS, application control, threat protection, SSL inspection, VPN and logging requirements can be more important to real-world sizing than basic stateful firewall throughput.
For organizations with branches across several cities, Secure SD-WAN and IPsec can provide a common framework for path selection and encrypted connectivity. A scalable design should use consistent addressing, security zones and naming conventions, while central management can be evaluated for larger estates. Resilience planning should consider dual ISPs, firewall HA, switching, power and application dependencies together. Redundancy at one layer does not eliminate single points of failure elsewhere.
Nigeria-specific procurement enquiries can be routed through FourTeck Nigeria. A buyer should state quantity, destination, desired FortiGuard/FortiCare term, interface accessories and whether professional services are required. For regional enterprises also operating in Tanzania, coordinate security policy standards and renewal records while requesting separate country-specific commercial terms. This approach supports consistent security operations without making unsupported assumptions about stock, pricing, customs or service availability in either market.
FortiGate 120G Seychelles
FortiGate 120G Seychelles deployments may be relevant to hospitality, professional services, public-facing businesses and multi-site organizations that depend heavily on internet connectivity and secure access to remote systems. In island environments, connectivity resilience can deserve particular planning attention. If multiple WAN services are available, define how failover and application steering should behave and which services receive priority when backup capacity is lower than the primary path.
Hospitality and guest-facing environments should separate guest traffic from business systems, administration and infrastructure management. Segmentation, application policy and controlled inter-zone access can reduce unnecessary exposure. Where remote support is required, secure administrator access and clear change-management processes are essential. VPNs to external offices or cloud networks should be designed with non-overlapping addressing and documented routing. The FG-120G provides a flexible interface set, but required fiber or copper accessories should be confirmed for the specific site.
Seychelles buyers should provide detailed destination and project information when requesting a quote because freight, commercial terms and implementation scope are project-specific. State whether the requirement is hardware only or includes FortiGuard/FortiCare subscriptions, and specify the desired term. If HA is needed, include two appliances and the surrounding infrastructure requirements in the design. For organizations with regional offices, a common FortiGate operating model can simplify administration, but each site’s bandwidth and security load should still be sized individually. FourTeck can use these details to prepare a more relevant quotation discussion without promising unverified inventory, delivery timing or local service coverage.
FortiGate 120G Buying and Sizing Checklist
Before requesting a final quotation, capture the information that changes model sizing and bill-of-material accuracy. This reduces repeated clarification and makes competing quotations easier to compare.
✓ Number of WAN circuits and handoff media
✓ User and device estimates
✓ VLANs and security zones
✓ IPS/application/SSL inspection requirements
✓ Public servers and NAT rules
✓ HA and business-continuity requirements
✓ SFP/SFP+ optics and cables
✓ Logging and management approach
✓ Migration and installation scope
Frequently Asked Questions
What is the firewall throughput of FortiGate 120G?
Fortinet lists firewall throughput of 39/39/28 Gbps for 1518/512/64-byte UDP packets. This is a reference performance figure; production sizing should also consider enabled security services and traffic characteristics.
What are the IPS, NGFW and threat-protection figures?
Fortinet lists 5.3 Gbps IPS throughput, 3.1 Gbps NGFW throughput and 2.8 Gbps threat-protection throughput for the 120G Series. Use the metric closest to the intended security profile when evaluating headroom.
What ports are on the FG-120G?
The official ordering information lists 18 GE RJ45 ports including management and HA ports, eight GE SFP slots and four 10GE SFP+ slots. Confirm the required transceivers and media for your network separately.
What is the difference between FG-120G and FG-121G?
The FG-121G variant includes 480 GB onboard SSD storage in Fortinet’s ordering information, while the FG-120G is the diskless model. Do not assume the storage specification applies to both variants.
Can FortiGate 120G be used for dual-WAN and SD-WAN?
Yes, Fortinet positions the series for Secure SD-WAN as part of its converged networking and security approach. The actual design should define circuit health checks, traffic priorities, failover behavior and application steering.
How should I request a FortiGate 120G Tanzania quotation?
Provide the model and quantity, destination, WAN bandwidth, security requirements, subscription term, HA requirement, optics and implementation scope. This gives the sales and technical teams enough information to prepare a more relevant offer.
Decision Recap
FortiGate 120G is a strong candidate when a network needs more than basic branch firewalling: multi-gigabit inspected-security performance, flexible GE and 10GE connectivity, Secure SD-WAN, VPN, segmentation and integration with Fortinet’s wider security platform. The right decision still depends on measured requirements. Compare the 120G against bandwidth, security services, encrypted traffic, interfaces, HA, logging and growth rather than purchasing from the model name alone.
For procurement, request a complete bill of materials that separates hardware, subscriptions, accessories and professional services. For deployment, document routing, VLANs, NAT, VPNs, administrator access, logging, backup and rollback before the change window. These steps improve both commercial clarity and operational outcomes.
FortiGate 120G Consultation and Quotation
Contact FourTeck with your current firewall model, internet speeds, number of users/sites, required FortiGuard services, VPN needs and preferred subscription duration. The team can use those details to discuss FG-120G sizing, licensing, accessories and migration scope for Tanzania and coordinated regional projects. Pricing, stock, delivery and service coverage should be confirmed for the specific request rather than assumed from another country or previous quotation.




Reviews
There are no reviews yet.