
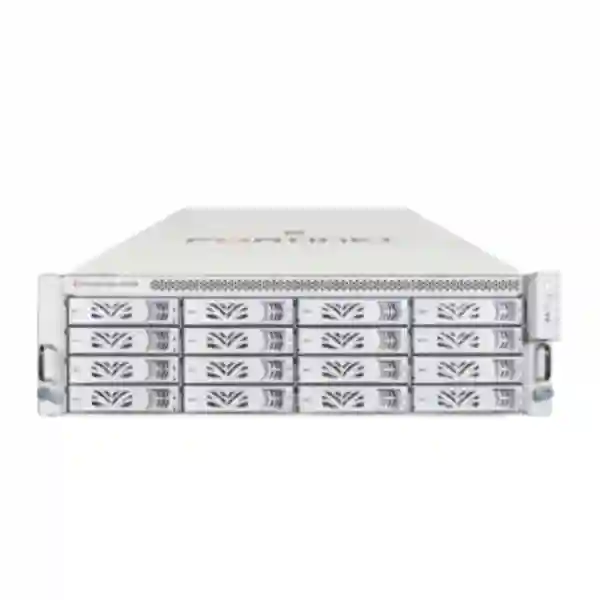
FortiGate 3000G Series
FortiGate 3000G Series is a high-end next-generation firewall platform designed for demanding data-center, enterprise-core and high-capacity network-security roles. The family documented by Fortinet includes FG-3000G and FG-3001G, with AC and DC variants covered by the current quick-start documentation. For organizations evaluating a Fortinet firewall in Tanzania, the important question is not simply headline throughput: sizing should consider inspected traffic, encrypted traffic, VPN demand, segmentation, interface architecture, resilience, subscriptions, operational management and expected growth.

FortiGate 3000G performance and platform overview
Fortinet’s current product matrix reports firewall throughput of 397/394/234 Gbps for 1518/512/64-byte UDP traffic, 105 Gbps IPsec VPN throughput, 90 Gbps IPS throughput, 85 Gbps NGFW throughput and 80 Gbps threat-protection throughput for the FG-3000G. These figures are vendor laboratory measurements and real results vary with configuration, traffic, enabled security services and network conditions. The 3000G belongs to Fortinet’s high-end data-center class, making it relevant where organizations need substantial inspection capacity while consolidating firewalling, segmentation, VPN and advanced security controls on FortiOS.
Vendor-listed enterprise-mix IPS throughput for capacity planning.
Vendor-listed NGFW throughput under Fortinet test methodology.
High-capacity encrypted site connectivity for suitable designs.
Vendor-listed figure combining specified security functions.
The platform is most appropriately evaluated as part of an architecture rather than as an isolated appliance. Teams should document north-south internet traffic, east-west segmentation, application flows, TLS inspection expectations, remote and site-to-site VPN, availability requirements and logging before selecting the final appliance, licenses and adjacent switching. Explore FourTeck Tanzania’s integrated technology services for project planning and the business technology shop for related infrastructure guidance.
Deployment, integration and buying guidance
A high-end firewall purchase should begin with a traffic and security-policy baseline. Record current and projected WAN bandwidth, internal high-speed links, peak sessions, application mix, encrypted traffic, inspection profiles, public services, data-center segmentation, VPN topology and failover objectives. Interface speed alone does not establish a correct design; optics, switches, routing, cabling, rack power, cooling and redundancy all matter. FortiGate also operates as part of the wider Fortinet Security Fabric, so buyers may consider centralized management, analytics, switching, wireless and endpoint integrations where those components fit the operational model.
Licensing deserves equal attention. The required FortiGuard services and FortiCare coverage should be selected according to the controls the organization intends to use and its support expectations. Procurement teams should request an exact bill of materials rather than treating the hardware name as the complete solution. For adjacent infrastructure, review FourTeck Tanzania’s firewall, network, server and infrastructure portfolio, network-security service guidance, network switch and server buying guidance, and Tanzania project enquiry page. These pages help connect firewall sizing with switching, server, rack, power and support requirements.
FortiGate 3000G Series Tanzania
Organizations searching for FortiGate 3000G Series Tanzania are usually planning a high-capacity security layer rather than a small office firewall. Relevant environments include enterprise data centers, service-provider networks, large campuses, financial platforms, cloud-connected estates and organizations consolidating multiple security zones. In Tanzania, procurement should start with the actual traffic paths that require inspection. Internet capacity is only one input: data-center traffic can move internally at much higher rates, and segmentation between server tiers, user networks, partner environments and hosted services may create significant east-west demand. The 3000G’s vendor-listed performance gives architects substantial headroom, but the final design should still be validated against enabled inspection features and real application patterns.
For a Tanzania deployment, document the number and speed of uplinks, routing design, high-availability requirement, VPN peers, remote users, public-facing applications, logging destination and change-management process. If the firewall will sit between high-speed switching domains, confirm transceiver types and link standards before ordering. Power resilience and cooling should also be reviewed as part of the rack design. Where two appliances are proposed for availability, the failover design should include upstream and downstream dependencies so the firewall pair is not made redundant while another single device remains a critical failure point.
Security subscriptions should be selected according to policy objectives, not simply bundled without review. Clarify whether IPS, application control, web filtering, malware protection and other FortiGuard capabilities are required and how encrypted traffic will be handled. Operational teams should also decide how configurations, firmware, logs and alerts will be managed. FourTeck Tanzania’s services overview explains the integrated approach to firewalls, networks, servers and infrastructure, while the contact page provides a route for model, quantity and project discussions. A useful quotation request should include current bandwidth, expected growth, security services, interface needs, HA expectations and required subscription term.
FortiGate 3000G Series Dar es Salaam
FortiGate 3000G Series Dar es Salaam searches commonly align with enterprise headquarters, data-center environments, financial services, hosting, telecom-related infrastructure and large organizations that need strong perimeter and segmentation capacity. For a Dar es Salaam project, the purchasing conversation should focus on the complete traffic architecture. A high-speed internet circuit may be important, but the firewall may also protect application tiers, server networks, DMZs, branch VPNs, partner connections and cloud-bound traffic. Each path can have a different inspection policy, so a single bandwidth number is not enough to size the environment responsibly.
Before requesting a quote, map existing core switches, WAN routers, upstream providers, server VLANs and any current firewall cluster. Record physical interface requirements and whether links are copper, fiber or high-speed optical connections. If migration is from an older security platform, configuration translation should not be treated as a blind copy exercise. Legacy policies often contain unused objects, broad rules or historical exceptions. A migration is an opportunity to review rule ownership, remove obsolete access and establish clearer segmentation while preserving business-critical connectivity.
Resilience planning is especially important for systems supporting always-on business operations. High availability should be designed with redundant power, switching paths and appropriate upstream architecture. Logging and monitoring also need a destination and retention plan. Teams should identify who will administer FortiOS, who approves policy changes, how backups are protected and how firmware maintenance will be scheduled. FourTeck Tanzania’s verified contact page lists Dar es Salaam among its office locations and invites firewall enquiries with internet speed, VPN requirements, branch connectivity and security-service expectations. Use the Dar es Salaam technology enquiry channel to provide these inputs so a quotation can address the actual deployment rather than only the appliance name.
FortiGate 3000G Series Mwanza
For FortiGate 3000G Series Mwanza requirements, the first step is to establish whether the site genuinely needs a high-end data-center firewall or whether the 3000G is intended to serve as a central security hub for multiple locations. Large industrial, logistics, education, healthcare, financial and multi-site organizations may have traffic patterns that justify centralized inspection, VPN aggregation and segmentation, but model selection should follow measured demand. Document present internet and private-WAN bandwidth, number of connected sites, server workloads, remote-access needs, public services and projected growth. This prevents both undersizing and unnecessary oversizing.
A Mwanza architecture may need to connect facilities with different circuit types and reliability characteristics. In that case, firewall planning should be coordinated with routing and WAN design. Secure SD-WAN capabilities within FortiOS may be relevant where multiple WAN paths are used, but the business objectives—resilience, application steering, path quality or branch consolidation—should be defined first. Site-to-site IPsec requirements should list peer locations, expected encrypted throughput and routing method. If remote users also connect, identity, authentication and access-policy requirements should be documented separately from branch tunnels.
Physical infrastructure matters for a platform in this class. Confirm rack space, power feeds, UPS strategy, cooling, optical modules, patching and switch-port availability. The security design should include management access controls and a plan for configuration backups, firmware updates and event monitoring. Procurement teams should request the exact hardware variant and subscription term, avoiding assumptions about licenses or accessories. For related infrastructure planning, the FourTeck Tanzania shop guidance covers firewalls, switches, servers, racks and cabling, while the quotation form can be used to submit the Mwanza site profile and required project scope.
FortiGate 3000G Series Arusha
FortiGate 3000G Series Arusha buyers may be evaluating security for large enterprises, hospitality groups, regional headquarters, institutions or multi-site environments where centralized firewalling must support substantial traffic and strict segmentation. The 3000G should be assessed against actual security workload rather than selected from the model name alone. Start with peak internet usage, internal data-center flows, VPN traffic, server publishing, cloud connectivity and the inspection services that will be enabled. Fortinet publishes separate firewall, IPS, NGFW and threat-protection figures because different security functions create different workloads; design decisions should therefore use the metric closest to the intended policy set.
Arusha organizations with several sites should also define how branches connect to the central environment. Some may use private circuits, others internet VPN, and some may use multiple links. The security architecture should establish routing, segmentation and failover behavior clearly. If guest, staff, operational technology, surveillance, voice and server networks coexist, VLAN and policy boundaries should be planned so the firewall supports intentional access rather than a flat network. This is particularly important when a central firewall becomes a control point for many departments or properties.
FourTeck Tanzania’s verified contact information identifies an Arusha office and provides a central route for technology enquiries. When requesting FortiGate 3000G pricing or project guidance, include the exact desired model if known, quantity, AC/DC preference if applicable, security subscription expectations, support term, HA requirement, interface speeds and deployment timeline. Also note existing switches and optics so compatibility can be checked. Review the Tanzania firewall and network service scope and use the Arusha enquiry route to start a requirements-based quotation.
FortiGate 3000G Series Dodoma
FortiGate 3000G Series Dodoma projects can involve central administration, large institutions, national organizations, enterprise campuses and data environments that need high-capacity inspection and controlled connectivity between security zones. A successful deployment begins with governance as much as hardware. Identify the networks that must communicate, the applications they use, the administrators responsible for policy, and the logging or audit requirements that apply. A high-performance firewall can enforce detailed segmentation, but only when the policy model reflects clear business ownership and documented access requirements.
Capacity planning should distinguish raw firewall traffic from traffic processed by advanced security controls. Fortinet’s published metrics provide a reference point, but production results depend on traffic mix and configuration. Estimate concurrent activity, encrypted application use, VPN load, server-to-user traffic and any east-west inspection between internal zones. If the 3000G will replace an existing firewall, export utilization information and identify peak periods before migration. This provides stronger evidence than relying only on circuit speed.
Deployment planning in Dodoma should also cover rack and power readiness, redundant paths, switch connectivity, optics and management access. If high availability is required, document failover objectives and test procedures. The operational handover should identify configuration backup routines, firmware policy, administrator roles and escalation contacts. FourTeck Tanzania’s verified contact page lists Dodoma as an office location and specifically asks firewall customers to share internet speed, VPN use, branch connectivity and expected security services. Buyers can review FourTeck Tanzania’s integrated security and infrastructure portfolio and submit the project through the Dodoma quotation enquiry page.
FortiGate 3000G Series UAE
FortiGate 3000G Series UAE requirements are relevant to data centers, cloud-connected enterprises, financial environments, large campuses, managed infrastructure and organizations with high-speed east-west and north-south traffic. Buyers should build a bill of materials around the architecture: appliance variant, HA quantity, transceivers, security subscriptions, support, management and logging requirements. The FG-3000G and FG-3001G names should not be treated interchangeably without confirming the intended hardware configuration, and AC/DC requirements should be stated explicitly when ordering.
For UAE data-center deployments, interface and topology planning can be as important as headline throughput. Identify the switching fabric, link speeds, routing protocols, segmentation model and whether the firewall will inspect internet, inter-zone, tenant, cloud or partner traffic. If TLS inspection is planned, validate capacity with the expected cipher and application mix. If the platform aggregates IPsec tunnels, document the number of sites and traffic profiles. High availability should include redundant upstream and downstream connections, not only a second firewall.
Operationally, define centralized administration, log retention, alerting, change control and firmware maintenance before go-live. Security subscriptions should map to required controls rather than being selected solely by package name. FourTeck’s UAE IT and network-security site provides regional context, while the specialist Fortinet UAE resource focuses on Fortinet solutions. These regional resources can support a procurement discussion alongside the Tanzania project when an organization operates across markets.
FortiGate 3000G Series Uganda
FortiGate 3000G Series Uganda searches often indicate a need for a central firewall with enough capacity to serve a large enterprise, data center or multi-branch environment. Buyers should begin by documenting traffic at the intended enforcement point. If the appliance will terminate branch VPNs, protect internet access and segment internal server networks simultaneously, each workload should be estimated. Fortinet’s published performance figures are useful references, but production sizing should account for enabled security services, encrypted traffic, policy complexity and growth.
Uganda organizations with distributed operations should pay particular attention to WAN architecture. Record each branch circuit, routing method, tunnel requirement and failover expectation. If multiple links are available, determine whether the objective is active/active utilization, resilience, application steering or a combination. Centralized logging and management should be considered early because a large firewall estate becomes easier to operate when configuration, visibility and policy processes are standardized.
Procurement should specify exact hardware, quantity, power variant where relevant, subscription bundle, support term, optics and accessories. Avoid assuming that a quoted appliance automatically includes every service needed for the project. Infrastructure readiness should cover rack space, power, UPS, cooling, fiber and switching. FourTeck’s Uganda technology site provides regional IT context, and organizations coordinating a Tanzania-Uganda architecture can use the Tanzania central project enquiry to describe the multi-country requirement and request a scoped discussion.
FortiGate 3000G Series Kampala
A FortiGate 3000G Series Kampala deployment is most likely to fit organizations with substantial security throughput, central data-center services or a hub role for many sites. Before choosing the model, collect firewall utilization from the current environment, WAN capacity, server traffic, VPN usage and expected growth. Security teams should list which traffic requires IPS, application control, web security or other inspection. This workload-based approach is more reliable than sizing solely from user count because a smaller number of users running data-intensive applications can create more traffic than a much larger office population.
Kampala projects may also need careful migration planning. Existing firewall rules should be reviewed for ownership and purpose. Duplicate, obsolete or overly broad policies can be cleaned before migration, while critical application dependencies should be tested. Establish a rollback plan and a controlled change window for production cutover. Where the firewall participates in dynamic routing or connects to redundant cores, test failover paths as part of acceptance rather than assuming redundancy works because the devices are physically duplicated.
For purchasing, provide the desired FG-3000G or FG-3001G variant, HA requirement, interfaces, subscription term and support expectations. Include any centralized management or analytics requirement. FourTeck Uganda already publishes Fortinet product content and broader technology services; visit the FourTeck Uganda platform for regional context. For a cross-border organization with Tanzania infrastructure, describe both environments through the FourTeck Tanzania enquiry page so sizing can reflect shared applications, VPN links and operational ownership.
FortiGate 3000G Series Arua
FortiGate 3000G Series Arua enquiries should first establish the role of the appliance. A high-end 3000G may be intended for a central facility serving remote locations, a data-heavy institution, a service environment or an organization standardizing on a powerful security platform. If the local site itself has modest bandwidth, the design may be driven by aggregated VPN, internal segmentation or future consolidation rather than internet speed. Document those reasons so the final bill of materials matches the architecture.
Connectivity resilience can be particularly important for distributed operations. If more than one WAN service is available, define failover behavior and application priorities. IPsec tunnels should be designed with routing, authentication, encryption policy and monitoring in mind. Remote administration must be secured and limited to trusted management paths. For organizations without a large local security team, centralized management and documented operating procedures can reduce configuration inconsistency across sites.
The physical installation should be checked before shipment: rack capacity, power and UPS, cooling, fiber type, optical modules and switch interfaces. A quotation request should state whether one or two appliances are needed, the exact model variant, required subscription period and any accessories. Buyers should not infer stock or delivery times from a product page; those should be confirmed in a current quotation. FourTeck’s Uganda IT solutions site can provide the regional contact context, while FourTeck Tanzania’s integrated service guidance is useful when the firewall must coordinate with servers, switching, Wi-Fi or other infrastructure.
FortiGate 3000G Series Mbarara
For FortiGate 3000G Series Mbarara, a requirements-led evaluation should determine whether the platform will protect a large campus, data center, enterprise hub or aggregated multi-site network. Security capacity should be estimated from traffic that will actually cross inspection boundaries. Include internet, server, branch, partner and cloud flows, then identify which policies require deeper inspection. This provides a defensible sizing basis and helps the organization compare the 3000G with adjacent FortiGate models without relying on model-number assumptions.
Segmentation is another design priority. Large organizations frequently need separate zones for users, servers, guest access, surveillance, voice, management and specialized systems. The firewall policy should permit only the necessary communication between these zones and make administrative ownership clear. If existing networks are flat, the project may require switch and VLAN changes as well as the firewall itself. Those dependencies should be included in the implementation plan and budget.
Mbarara buyers should prepare a quotation checklist covering appliance variant, quantity, HA, security subscriptions, support duration, optics, management, logging and implementation scope. Power and rack requirements should be verified against the final hardware documentation before installation. Firmware and configuration backup procedures should be agreed before handover. Regional procurement questions can be directed through the FourTeck Uganda site; organizations managing a broader East African network can also use the Tanzania contact page to describe shared infrastructure and cross-site VPN requirements.
FortiGate 3000G Series Gulu
FortiGate 3000G Series Gulu planning should connect security performance to the organization’s operational model. A platform in this class can make sense where the firewall is a central aggregation point, protects substantial server infrastructure or must inspect high-volume traffic. Start by measuring current peak utilization and identifying expected expansion. If new applications, data-center services or additional sites will be introduced, include them in the forecast. Avoid sizing from average traffic alone because security infrastructure must handle busy periods without becoming the bottleneck.
For multi-site connectivity, list all VPN peers, circuit speeds and routing requirements. Consider what happens when a primary link fails and whether applications need automatic path selection. Security policy should distinguish trusted management traffic from user and application flows. Administrator access should use controlled accounts and appropriate authentication, and configuration changes should be logged. Central monitoring is particularly valuable when local sites depend on a shared firewall hub.
The procurement document should state the exact FortiGate model, power option where relevant, required quantity, support and security service term, and interface accessories. The implementation scope should clarify whether the project includes migration, policy review, VPN configuration, routing, HA testing and documentation. The FourTeck Uganda regional site can support Uganda-focused enquiries, while FourTeck Tanzania’s technology buying guidance provides useful reminders about compatibility, capacity, infrastructure, management and lifecycle considerations for firewalls and related network equipment.
FortiGate 3000G Series Kenya
FortiGate 3000G Series Kenya buyers may be planning data-center security, high-capacity enterprise perimeter protection, campus segmentation or a regional hub connecting many offices. The evaluation should begin with traffic classification. Separate internet-bound traffic from data-center east-west flows, VPN aggregation, cloud connections and partner links. Then map security controls to each flow. Fortinet’s vendor metrics show substantial capacity, but correct sizing still depends on which inspection functions are active and how much encrypted traffic is processed.
For organizations with Nairobi or other Kenyan facilities linked to Tanzania, routing and VPN design should be planned as one regional architecture. Decide whether each country site accesses the internet locally or through a central hub, how cloud applications are reached, and what happens during WAN failures. Consistent policy naming, address objects and logging conventions make cross-country operations easier. Where regulatory or organizational policy requires traffic separation, those boundaries should be documented before implementation.
A Kenya quotation should include exact appliance model, quantity, HA expectation, security subscriptions, FortiCare term, optics and implementation services if needed. Confirm availability and commercial terms at quotation time rather than relying on generic product statements. FourTeck’s Kenya IT and firewall solutions site provides regional context for network-security projects. Multi-country organizations can pair that resource with the FourTeck Tanzania project enquiry to describe shared data centers, cross-border VPNs, branch counts and operational responsibilities.
FortiGate 3000G Series Kuwait
FortiGate 3000G Series Kuwait projects can suit enterprises and data-center environments that need high-throughput firewalling with advanced inspection, VPN and segmentation. Procurement teams should treat the 3000G as part of a complete security architecture. Document current and planned circuits, internal high-speed switching, server zones, cloud connections, VPNs and the FortiGuard services expected to run. If the firewall will protect latency-sensitive or high-volume applications, test and migration criteria should be defined before production cutover.
Data-center deployment also requires physical planning. Confirm rack location, power feeds, UPS, cooling, optical modules and cabling. If HA is required, upstream and downstream switching should provide appropriate redundant paths. Operations teams should define management networks, administrator roles, backup schedules, logging and firmware procedures. These controls matter because a powerful firewall still depends on disciplined administration to maintain a secure configuration over time.
When requesting a Kuwait quote, state whether the requirement is FG-3000G or FG-3001G, the desired quantity, power variant, subscription term, support requirement and interface accessories. If replacing another platform, include current throughput and policy information so migration effort can be estimated. FourTeck’s Kuwait IT solutions site provides regional technology context. Organizations that also operate in Tanzania can coordinate requirements through the Tanzania project enquiry page, particularly when the same security standards or VPN architecture will span both markets.
FortiGate 3000G Series Ghana
FortiGate 3000G Series Ghana requirements may arise in financial services, large enterprises, data centers, telecom-related environments, hosting and organizations that aggregate traffic from many branches. The platform should be sized from inspected workload rather than from internet bandwidth alone. Document server and application traffic, VPN demand, public services, cloud access and segmentation. If advanced inspection is enabled broadly, use the relevant NGFW or threat-protection figures as planning references rather than raw firewall throughput.
A Ghana deployment may also need a structured migration plan. Inventory current rules, NAT, VPNs, routing, address objects and certificates. Identify application owners who can validate connectivity after cutover. Where old rules have accumulated over years, clean-up should be controlled and documented rather than simply copied. For HA designs, perform failover testing and verify that connected switches, routers and WAN paths behave as expected. Logging should be retained according to organizational policy and operational needs.
The purchasing request should specify model, quantity, AC/DC needs, support and subscription term, optics and implementation scope. Do not assume pricing, stock or delivery from general web content; request current commercial confirmation. FourTeck’s Ghana IT solutions platform covers firewalls, servers and networking within a broader business technology portfolio. For enterprises with Tanzania operations, the FourTeck Tanzania services page can help frame integration dependencies and the contact page can capture a multi-region project brief.
FortiGate 3000G Series Nigeria
FortiGate 3000G Series Nigeria evaluations are relevant where enterprises need a high-capacity NGFW for data centers, regional hubs, large campuses or service environments. Start with a baseline of peak traffic, not only contracted circuit capacity. Include internal data-center traffic, VPN aggregation, cloud connectivity and traffic crossing segmentation boundaries. Define which flows require IPS, application control and other security inspection. This workload model gives procurement and engineering teams a clearer basis for selecting the 3000G and its subscriptions.
Large Nigerian deployments can involve complex redundancy and multiple carriers. Document routing, failover and asymmetric-path considerations before inserting a firewall into the architecture. Where applications are distributed across data centers and clouds, identify dependencies so policies do not inadvertently interrupt service. If remote branches use IPsec, standardize tunnel naming, routing and monitoring. Centralized management and consistent configuration practices become increasingly important as the number of sites grows.
For procurement, request the exact model variant, quantity, support term, FortiGuard service package and required transceivers. Confirm installation requirements against current Fortinet hardware documentation. A production handover should include configuration backup, administrative access, logging, firmware procedures and tested recovery steps. Visit the FourTeck Nigeria IT solutions site for regional technology context. Enterprises operating between Nigeria and East Africa can use the Tanzania contact channel to describe cross-region VPN, application and security-standard requirements.
FortiGate 3000G Series Seychelles
FortiGate 3000G Series Seychelles requirements should be evaluated carefully because a high-end data-center firewall is designed for substantial workloads. It may fit a large centralized environment, service platform, financial organization, hospitality group hub or enterprise that aggregates many networks, but buyers should validate demand with measured traffic and growth forecasts. Internet speed alone may not show the full requirement when the firewall also handles internal segmentation, VPNs and server traffic.
Island connectivity and distributed properties can make WAN resilience an important design topic. If multiple circuits or remote sites are involved, document path selection, failover and VPN requirements. Consider whether applications are hosted locally, in another country or in public cloud services, because these traffic patterns influence where inspection should occur. Management access should remain protected, and operational procedures should account for remote troubleshooting without exposing administrative interfaces unnecessarily.
Before ordering, confirm exact hardware variant, quantity, subscription and support terms, optical modules, rack readiness, power and cooling. If the deployment requires HA, ensure the surrounding network supports genuine path redundancy. Procurement teams should request current availability and shipping information rather than relying on assumptions. For a regional organization with Tanzania infrastructure, FourTeck Tanzania’s integrated IT and security overview, infrastructure buying guidance and project enquiry page provide a structured way to document firewall, switching, server, rack and cross-site connectivity requirements.
Related Tanzania infrastructure and internal resources
Firewall and security planning
Use the FourTeck Tanzania services catalogue to connect firewall design with network, server, infrastructure and lifecycle requirements.
Switching and infrastructure
The Tanzania business technology shop explains selection considerations for switches, servers, racks, cabling and firewalls.
Integrated solution portfolio
Review the FourTeck Tanzania solution portfolio when the 3000G project must integrate with Wi-Fi, switching, servers, surveillance or business systems.
Project and quotation contact
Use the verified FourTeck Tanzania contact page to provide bandwidth, VPN, security-service, quantity and site details.
FortiGate 3000G Series FAQ
What models are in the FortiGate 3000G Series?
Fortinet’s current quick-start documentation covers FG-3000G and FG-3001G and also references AC and DC variants. The exact orderable configuration should be confirmed in the current quotation and Fortinet documentation.
What is FortiGate 3000G threat-protection throughput?
Fortinet’s current product matrix lists 80 Gbps threat-protection throughput for FG-3000G under its defined test methodology. Actual production performance varies with configuration, traffic and enabled services.
Is FortiGate 3000G suitable for a data center?
Fortinet categorizes the FortiGate 3000G in its high-end data-center range. Suitability for a particular data center still depends on traffic, interfaces, security services, segmentation, VPN and resilience requirements.
What should I provide for a FortiGate 3000G quotation?
Provide the desired model, quantity, current and planned bandwidth, interface requirements, HA requirement, VPN profile, expected security services, subscription term, support requirement, existing network equipment and target deployment timeline.
Quotation checklist and decision recap
A complete FortiGate 3000G request should identify the exact appliance variant, quantity, HA design, power requirement, interfaces and optics, WAN and internal traffic, VPN load, segmentation objectives, security services, subscription duration, support term, management and logging, rack and power readiness, migration scope and expected growth. The core decision is whether the 3000G’s high-end capacity and interface architecture align with the real inspected workload and operational model. FourTeck can use these inputs to move the discussion from a model-name request toward a deployment-ready bill of materials.
Discuss your FortiGate 3000G requirement
Share your site, bandwidth, VPN, HA, security-service and interface requirements with FourTeck Tanzania. The verified contact page supports product-selection and quotation enquiries and explains the practical information that helps build a meaningful technology proposal.



Reviews
There are no reviews yet.