
FortiGate 4200F (FG-4200F) Tanzania
The FortiGate 4200F is designed for organizations that need very high firewall capacity, dense high-speed interfaces and advanced security inspection at a data-center, campus-core or major internet edge. It combines Fortinet Security Processing Units with FortiOS and FortiGuard security services so networking and security controls can be operated on one platform. For Tanzanian enterprises planning large WAN hubs, internet gateways, segmentation projects, data-center refreshes or encrypted inter-site connectivity, the important question is not simply maximum firewall throughput: sizing must account for inspected traffic, SSL inspection, VPN demand, session scale, interface design, redundancy and the security subscriptions that will actually be enabled.

FortiGate 4200F overview and verified performance
Fortinet positions the FortiGate 4200F Series in its high-end firewall range. The current manufacturer datasheet lists 52 Gbps IPS throughput, 47 Gbps NGFW throughput and 45 Gbps threat-protection throughput for the series. It also lists firewall throughput of up to 800 Gbps for 1518-byte UDP traffic, 210 Gbps IPsec VPN throughput, 16 Gbps SSL-VPN throughput and 50 Gbps SSL inspection throughput using the vendor’s stated test conditions. These figures are laboratory maximums and should be interpreted with Fortinet’s test notes: actual results vary with configuration, traffic mix, enabled inspection, logging, cipher suites and policy design.
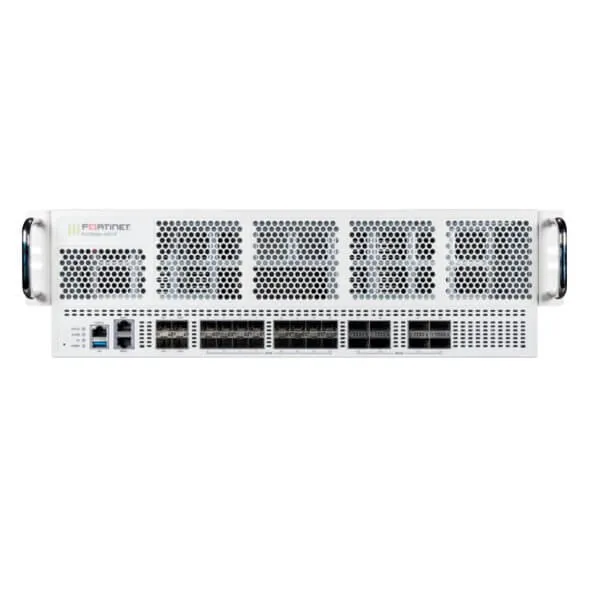
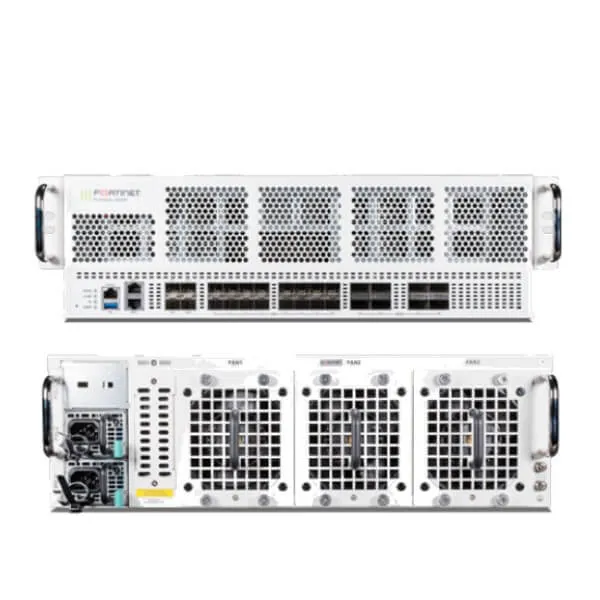
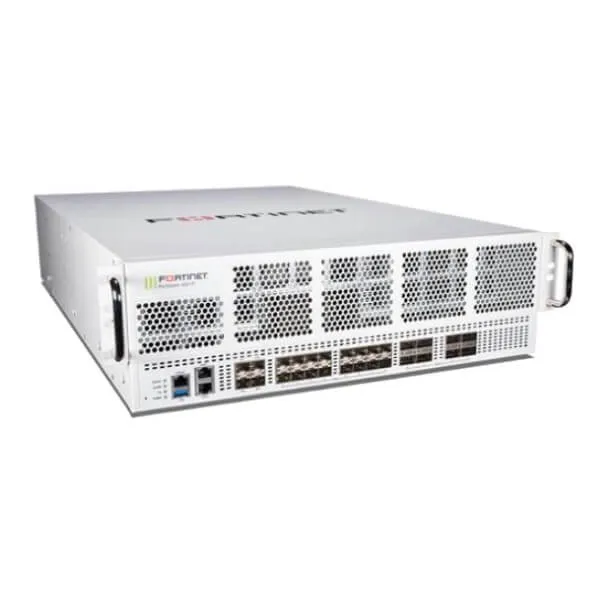
The FG-4200F provides eight hardware-accelerated 100GE QSFP28 / 40GE QSFP+ slots, sixteen hardware-accelerated 25GE SFP28 / 10GE SFP+ / GE SFP slots, two 25GE-class HA slots and two AUX slots, plus two GE RJ45 management ports. Fortinet lists two included 10GE SFP+ SR transceivers. The chassis is 3RU, uses redundant hot-swappable power supplies by default and supports front-to-back airflow. These physical details matter in real deployments because rack space, optics, fiber type, upstream switch interfaces, airflow direction, power feeds and UPS capacity all need to be included in the implementation bill of materials.
Where the FG-4200F fits
Data-center edge
High-speed north-south inspection, internet-edge policy enforcement, public-service protection and encrypted connectivity can place sustained demand on firewall resources. The 4200F’s high-speed interfaces and large session capacity make it a candidate for environments where smaller appliances would constrain future bandwidth plans.
Internal segmentation
Organizations can use firewall policy between security zones, server networks, user segments and other trust boundaries. Segmentation design should begin with applications and permitted flows rather than creating rules after VLANs have already been deployed.
Large VPN and WAN hub
The platform can support large IPsec environments, SD-WAN architectures and high-capacity branch aggregation. Tunnel count, encrypted throughput, routing, failover behavior and provider diversity should be modeled before final sizing.
Technical specifications for procurement planning
| Form factor | 3RU rack mount |
| 100GE / 40GE slots | 8 × QSFP28 / QSFP+ |
| 25GE / 10GE / GE slots | 16 × SFP28 / SFP+ / SFP, plus dedicated HA and AUX interfaces |
| Concurrent TCP sessions | 210 million; higher licensed hyperscale figure is separately identified by Fortinet |
| New TCP sessions/sec | 1 million; higher licensed hyperscale figure is separately identified by Fortinet |
| Virtual domains | 10 default / 500 maximum |
| High availability | Active-active, active-passive and clustering |
| FG-4200F onboard storage | No onboard storage listed for FG-4200F; the related FG-4201F is the storage-equipped variant |
Licensing, FortiGuard services and lifecycle planning
A firewall purchase should separate the hardware appliance from the security services and support term required by the organization. FortiGuard service bundles can add functions such as intrusion prevention, malware protection, application control, web or DNS security and other services depending on the selected bundle and current Fortinet offering. FortiCare support also needs to be matched to the operational requirement. Buyers should request an itemized quotation that identifies the appliance, subscription bundle, support term, optics, accessories and implementation scope rather than comparing only a headline hardware price.
For an existing FortiGate estate, migration planning should capture current interfaces, routing, VPNs, objects, policies, NAT, authentication, certificates, SD-WAN rules and logging destinations. A change window should include configuration backup, rollback criteria and validation tests. See FourTeck Tanzania’s integrated Tanzania IT and security portfolio for the broader infrastructure context, including firewall, switching, wireless, server and cabling dependencies.
Related infrastructure for a complete deployment
Review policy design, segmentation, VPN and inspection requirements around the FG-4200F deployment.
Network switching and LAN infrastructurePlan compatible high-speed switching, VLANs, fiber uplinks and resilient core connectivity.
Business Wi-FiCoordinate staff, guest and device wireless segmentation with firewall policies.
Servers and storageMap protected application networks, backup traffic and data-center flows before policy migration.
Fiber, racks and UPSInclude optics, rack space, cooling, fiber paths, redundant power and UPS capacity in the project.
IT services and deploymentConnect product procurement with configuration, testing, documentation and lifecycle support.
Tanzania technology shopExplore related business technology and infrastructure products for the overall solution.

FortiGate 4200F (FG-4200F) Tanzania
For Tanzania, the FG-4200F is most relevant where the firewall is expected to sit at a major concentration point rather than a small branch edge. Large enterprises, financial organizations, telecom environments, public institutions, universities, service providers and data-center operators may have multiple high-capacity internet or private circuits, extensive server networks and a requirement to inspect traffic without turning the security layer into a bottleneck. A Tanzanian procurement team evaluating the FortiGate 4200F should therefore start with measured traffic and architecture. Record current and planned WAN capacity, east-west flows that will traverse the firewall, VPN demand, encrypted application ratios, session peaks and the number of security zones. That information provides a better sizing foundation than user count alone.
The physical environment also deserves attention. The appliance is a 3RU system with front-to-back airflow and redundant hot-swappable power. A deployment plan should confirm rack depth and available rack units, A/B power feeds where required, UPS capacity, cooling, fiber patching and the optics needed to connect 100GE, 40GE, 25GE or 10GE infrastructure. Where a site is upgrading from lower-speed switching, the firewall project may expose a need to refresh aggregation or core links at the same time. FourTeck Tanzania’s networking, server, structured-cabling and UPS planning can be considered alongside the firewall so that high-speed ports are useful from day one rather than waiting for surrounding infrastructure changes.
For organizations with branches across Tanzania, the 4200F can also be assessed as a central VPN or SD-WAN hub. The design should identify branch tunnel counts, routing behavior, failover expectations and how internet breakout is handled at each location. Security subscriptions should be quoted for the desired term, and procurement documents should distinguish hardware, FortiGuard services, FortiCare, optics and professional services. Buyers looking for a FortiGate 4200F supplier in Tanzania, FG-4200F quotation, enterprise firewall upgrade or Fortinet data-center firewall should request a configuration-led proposal. This makes it easier to compare quotations on equal scope and avoids discovering after purchase that a required subscription, transceiver or implementation task was omitted.
FortiGate 4200F (FG-4200F) Dar es Salaam
Dar es Salaam organizations often concentrate headquarters, data-center, cloud connectivity and external service access in the same metropolitan environment. For a large corporate campus, bank, logistics operator, service provider or enterprise hosting business applications, the FG-4200F can be evaluated as a high-capacity security gateway between internet circuits, internal zones and hosted services. The practical starting point is a traffic map. Identify which links terminate at the firewall, which public services are published, where remote-access users connect, which applications cross security zones and how much encrypted traffic is inspected. This reveals whether the project is primarily an internet-edge refresh, segmentation program, VPN consolidation project or a combination of these requirements.
A Dar es Salaam deployment may also involve diverse carrier links and multiple physical facilities. Redundancy should be designed end to end: dual power supplies do not create resilience if both are connected to one unprotected source, and two WAN circuits do not provide useful diversity if they share the same upstream failure point. Procurement teams should ask network providers about handoff media and speeds, then match those details to the correct QSFP28, QSFP+, SFP28 or SFP+ optics. High-speed firewall ports can simplify architecture, but only when the adjacent switching platform and fiber plant support the intended rates. Rack airflow, environmental monitoring and cable management are equally important in a dense equipment room.
Organizations migrating an existing firewall in Dar es Salaam should treat configuration conversion as a controlled project. Inventory policies, NAT, routes, VPNs, address objects, authentication sources, certificates, SD-WAN rules and logging integrations. Remove obsolete rules before migration where change governance allows, then test critical business services after cutover. If the 4200F will protect public applications, coordinate the change with application owners so inbound NAT, DNS, certificates and monitoring are validated. For procurement, request the exact FG-4200F appliance, required FortiGuard and FortiCare term, transceivers, installation scope and migration deliverables. A clear bill of materials makes an enterprise firewall quotation easier to review and reduces ambiguity between competing offers.
FortiGate 4200F (FG-4200F) Mwanza
In Mwanza, a FortiGate 4200F project is likely to be driven by a large regional hub, industrial operation, institution, multi-site organization or infrastructure environment where many users and systems converge on a central network. Rather than assuming that a high-end firewall is automatically the correct choice, IT teams should document the role the appliance will play. If the requirement is to aggregate branch VPNs, inspect data-center traffic, segment server networks and secure large internet circuits simultaneously, the 4200F’s high session capacity and high-speed interfaces become relevant. If the environment is smaller, the same analysis may show that a different FortiGate model is more economical. Correct sizing is part of responsible procurement.
Connectivity resilience can be particularly important for operations that depend on cloud platforms, ERP, remote collaboration or centralized applications. The firewall can participate in multi-WAN and SD-WAN designs, but successful failover depends on circuit diversity, health checks, routing and application behavior. Before implementation, list every critical application and define what should happen when the primary circuit fails. Some services can move automatically, while others may depend on public IP addresses, upstream routing or external allowlists. Testing these dependencies during commissioning is more valuable than simply confirming that a secondary link shows as online.
Mwanza deployments should also account for the equipment-room environment. The FG-4200F is a substantial 3RU appliance; rack depth, airflow, cooling and redundant power need to be checked before delivery. Fiber paths and optics should be specified against the exact switch ports and distances. For distributed organizations, central logging and configuration management can improve operational visibility, while documented network diagrams make future troubleshooting faster. Buyers searching for Fortinet FG-4200F in Mwanza should provide current firewall model, internet speeds, interface requirements, VPN counts, expected growth and desired security services when requesting a quotation. That information helps turn a product inquiry into a deployment-ready bill of materials instead of an isolated hardware price.
FortiGate 4200F (FG-4200F) Arusha
Arusha enterprises may operate headquarters, hospitality groups, institutions, NGOs, regional offices or multi-site environments that connect users to cloud services and centralized applications. The FG-4200F is aimed at substantially larger security edges than a normal office firewall, so its value is strongest when there is a genuine requirement for high throughput, large session scale, dense high-speed connectivity or consolidation of multiple security functions. A design workshop should separate internet traffic, data-center traffic, branch VPN traffic and internal segmentation traffic because each can create a different load profile. Encrypted inspection and advanced threat services should be included in capacity planning rather than relying only on basic firewall throughput.
For a multi-site Arusha organization, standardization can be a major operational benefit. The 4200F may serve as a central hub while smaller FortiGate appliances protect remote sites. Consistent address plans, VPN templates, VLAN conventions and security policies can reduce troubleshooting effort. If SD-WAN is used, link quality measurements and application steering rules should reflect the actual circuits available at each site. Critical SaaS, voice, video and transactional applications may need different priorities. Centralized management and logging can help teams see events across the estate, but retention and reporting requirements should be defined before selecting supporting systems.
The procurement package for Arusha should include more than the chassis. Confirm whether the project needs 100GE, 40GE, 25GE or 10GE optics, redundant upstream switching, new fiber patch cords, rack changes or UPS expansion. Define the FortiGuard security bundle and FortiCare term required by policy. If replacing an older firewall, include migration, change-window support, validation and documentation. Organizations searching for an FG-4200F supplier in Arusha can accelerate quotation by sharing a sanitized topology, interface list, bandwidth figures and desired contract period. This enables a more meaningful proposal and helps avoid both undersizing and unnecessary oversizing.
FortiGate 4200F (FG-4200F) Dodoma
Dodoma organizations considering the FortiGate 4200F may include large institutions, public-sector environments, national organizations, universities and enterprises with centralized services or extensive branch connectivity. For these environments, security procurement often needs to balance performance with governance. The firewall architecture should clearly identify trust zones, administrative access, logging, change control and high-availability behavior. Fortinet lists active-active, active-passive and clustering options for the 4200F Series, but the appropriate design depends on routing, state synchronization, maintenance expectations and the failure scenarios the organization intends to tolerate.
A useful sizing exercise begins with evidence from the existing network: peak bandwidth, session counts, VPN usage, application mix and projected growth. If TLS inspection will be enabled broadly, include that in performance planning. If the appliance will act as a central gateway for many remote sites, map the number and type of IPsec tunnels and determine whether routing is static, dynamic or SD-WAN driven. Security policies should be designed around business services and least-privilege access, with administrative interfaces placed on controlled management networks. This is especially important in environments where several teams or contractors participate in operations.
For Dodoma procurement, technical compliance documents should distinguish manufacturer specifications from project-specific commitments. Fortinet’s published throughput figures are vendor test results, not guarantees for every production configuration. The quotation should separately identify hardware, subscription and support terms, optics, implementation, training or documentation where required. Rack, power and cooling requirements should be checked early because the 3RU platform is intended for enterprise infrastructure rooms rather than small wall cabinets. Buyers requesting a FortiGate 4200F quote in Dodoma can improve accuracy by supplying the required interface speeds, redundancy design, existing firewall details and target security services.
FortiGate 4200F (FG-4200F) UAE
For UAE enterprises, the FG-4200F can be evaluated for high-capacity data-center edges, campus cores, service-provider environments and regional hubs that aggregate significant encrypted traffic. Organizations operating between Tanzania and the UAE may also want consistent Fortinet architecture across locations while selecting different appliance sizes for each site. The UAE requirement should be assessed independently: record internet and private-circuit speeds, data-center interconnects, public application exposure, VPN scale and segmentation requirements. The 4200F’s high-speed 100GE, 40GE, 25GE and 10GE interfaces can support dense connectivity, but the final design must align with switch platforms, transceiver standards and fiber infrastructure.
Regional headquarters often connect multiple branches and cloud environments. In that role, the firewall can become a central policy and VPN point, making high availability and operational management essential. Maintenance windows, firmware policy, configuration backup, logging and incident response should be agreed before production deployment. If the UAE site is a disaster-recovery counterpart to a Tanzania data center, routing and failover should be tested from the application perspective, not just at the network layer. DNS, public addressing, certificates and external allowlists can affect recovery behavior.
FourTeck’s Fortinet UAE specialist site and FourTeck UAE IT solutions site provide regional context for organizations coordinating requirements across markets. Procurement should still confirm the exact appliance, security bundle, FortiCare term, optics and services for each location. Avoid assuming that a configuration quoted for one country automatically matches another site’s carriers, rack environment, compliance process or operational model. A shared design standard with site-specific bills of materials is usually easier to support than forcing identical hardware everywhere.
FortiGate 4200F (FG-4200F) Uganda
Ugandan organizations evaluating the FortiGate 4200F should focus on whether their central security edge genuinely needs high-end throughput and interface density. A large bank, telecom environment, national enterprise, data center or major multi-site organization may need to aggregate many circuits and tunnels while applying IPS, application control and malware protection. The 4200F provides substantial headroom, but capacity should be mapped against enabled services. Basic firewall throughput alone is not a useful proxy for real-world inspected traffic, so project documentation should state the expected security profile and encrypted traffic ratio.
For cross-border organizations with operations in Tanzania and Uganda, consistent policy naming, VPN design and management standards can simplify support. The central firewall may terminate site-to-site IPsec tunnels and enforce segmentation between business systems, user networks and shared services. Routing design should account for failover and asymmetric paths. If multiple internet providers are used, test health-check behavior and confirm which applications can tolerate a change of public IP. High availability should also include upstream switches, power and carrier paths rather than stopping at a second firewall node.
The FourTeck Uganda technology site can support regional coordination, while Tanzania requirements can remain anchored to the Tanzania project scope. A complete FG-4200F request should specify appliance quantity, HA requirement, subscription bundle and term, FortiCare, transceivers, rack and power constraints, migration scope and documentation. This makes procurement comparisons clearer and helps technical teams understand what is included before an order is approved.
FortiGate 4200F (FG-4200F) Kampala
Kampala is a natural location for regional headquarters, data centers and major enterprise connectivity hubs, making high-end firewalls relevant for organizations with substantial traffic concentration. An FG-4200F assessment should begin by defining the security boundary. Is the appliance protecting internet access, public-facing services, internal data-center segments, branch VPNs or all of these? Combining roles can be efficient, but it increases the importance of policy organization, interface capacity and change control. Virtual domains may be useful where administrative or network separation is required, subject to the organization’s design and licensing requirements.
Interface planning deserves particular attention. Fortinet provides multiple 100/40GE and 25/10GE-class slots, so the platform can connect to high-capacity core or aggregation networks without relying entirely on lower-speed links. Procurement teams should identify the exact optics and fiber standard for each connection, including link distance. HA links, management networks and out-of-band access should be planned separately from production traffic. The rack must accommodate a 3RU chassis with front-to-back airflow, and redundant power should connect to appropriately protected feeds.
For a Kampala migration, create a pre-cutover test matrix covering internet access, published services, DNS, VPNs, critical SaaS, authentication and monitoring. Back up the original configuration and define rollback triggers. After cutover, validate logs and security inspection as well as basic connectivity. Buyers searching for FortiGate 4200F Kampala pricing should treat public reseller prices cautiously because they may exclude FortiGuard subscriptions, support, optics, taxes, freight or implementation. An itemized quotation tied to the required architecture is more useful for enterprise procurement.
FortiGate 4200F (FG-4200F) Arua
For Arua, the FG-4200F would normally be considered in a specialized large-scale environment rather than as a standard office firewall. Organizations should first determine whether the site is a regional aggregation point, data center, large institution or network hub with unusually high bandwidth and session requirements. If the site primarily hosts a modest office, a smaller FortiGate may be more appropriate. This distinction matters because good security design is about matching capacity and features to the requirement, not simply choosing the largest appliance available.
Where Arua forms part of a distributed network, the 4200F may instead reside at a central hub while the local site uses an appropriately sized branch model. In that architecture, the Arua design still needs reliable WAN links, IPsec tunnels, route failover and clearly defined access to central applications. Network teams should document the applications that must remain available during circuit failure and confirm whether backup links have sufficient capacity. Security policies should minimize unnecessary branch-to-branch or branch-to-server access and use segmentation that reflects business roles.
If an FG-4200F is justified locally, plan the physical installation carefully. The appliance requires proper rack space, cooling and protected power, and high-speed fiber interfaces need compatible optics. A quotation should state whether transceivers and subscriptions are included and whether configuration or migration is part of the scope. For organizations spanning Arua, Kampala and Tanzania, standardized templates for naming, VPNs, logging and documentation can make support more predictable even when different firewall models are deployed at different sites.
FortiGate 4200F (FG-4200F) Mbarara
Mbarara businesses considering an FG-4200F should evaluate the firewall in the context of their entire network rather than as a standalone security appliance. A large campus, enterprise hub or service environment may have high-capacity server traffic, multiple WAN providers and extensive VPN requirements. In such cases, a high-end platform can provide room for security inspection and growth. The design team should capture peak throughput in both directions, concurrent session behavior, internal segmentation traffic and expected increases over the procurement lifecycle.
Operational simplicity is also important. Large firewalls can accumulate thousands of policies and objects over time, so naming conventions, rule ownership and review procedures should be defined early. Administrative access should be restricted to management networks and approved personnel. Logging destinations, time synchronization and configuration backups should be included in commissioning. If the organization uses multiple FortiGate sites, centralized management can help maintain standards, while local documentation remains essential for incident response.
Mbarara procurement teams should request a bill of materials that exposes dependencies: FG-4200F hardware, selected FortiGuard services, FortiCare term, required optics, high-availability components, rack and power work, migration and testing. Public online prices from other countries are not reliable indicators of a complete local project because bundle contents and commercial conditions differ. Providing a topology and bandwidth plan when requesting a quote allows the supplier to validate whether the 4200F is the right model and identify surrounding network upgrades before purchase.
FortiGate 4200F (FG-4200F) Gulu
In Gulu, a FortiGate 4200F requirement should be tied to a clearly defined large-scale use case. The platform is designed for high-end environments, so a procurement review should compare the expected inspected traffic and interface needs with the capabilities of the broader FortiGate portfolio. A regional institution with many remote sites, a large hosting environment or a major network hub may justify this class of appliance; a conventional office may not. Documenting the use case protects budget and ensures that security capacity is placed where it provides operational value.
For distributed operations, resilient connectivity is often more important than headline throughput. The firewall architecture should include primary and secondary circuits, routing behavior, tunnel monitoring and application-level tests. If central services are hosted elsewhere, identify which services must survive a WAN failure and whether local fallback is required. VPN encryption, authentication and key management should follow a documented standard. Where internet access breaks out locally, branch security policies should remain consistent with the organization’s central controls.
If the FG-4200F is installed in Gulu, ensure the equipment room supports a 3RU enterprise appliance with correct airflow and power protection. High-speed optical links should be specified against actual switch interfaces and fiber distances. The final quotation should avoid vague descriptions such as “FortiGate with license”; it should list the exact model, subscription package, term, support level and accessories. This level of detail is particularly useful for organizations coordinating procurement between Gulu, Kampala and Tanzania because it creates a repeatable technical baseline while allowing each site’s network capacity to differ.
FortiGate 4200F (FG-4200F) Kenya
Kenyan enterprises with large data centers, regional headquarters or service-provider networks may evaluate the FG-4200F where high throughput, large session scale and 100GE/40GE/25GE connectivity are required. For an East African organization operating in both Kenya and Tanzania, the firewall strategy can use common security principles without forcing identical hardware at every site. Start by comparing each location’s internet circuits, private links, user and server traffic, VPN role and growth forecast. A Nairobi hub, for example, may have a different traffic profile from a Tanzania production site even when the same applications are used.
Cross-border connectivity should be designed with routing and application behavior in mind. Site-to-site IPsec can secure traffic between locations, but performance depends on both endpoints and the underlying circuits. If cloud applications are accessed locally, SD-WAN policies can steer traffic according to link quality. If traffic is centralized through a regional data center, the hub must be sized for aggregate demand and failure scenarios. Logging, incident response and policy ownership should be standardized so teams can investigate events consistently across countries.
The FourTeck Kenya IT solutions site provides a regional point of reference for Kenyan requirements. For an FG-4200F quotation, procurement teams should state whether the requirement is hardware-only or includes FortiGuard services, FortiCare, optics, installation and migration. A common technical template for Kenya and Tanzania can reduce procurement ambiguity while still allowing country-specific commercial terms and implementation schedules.
FortiGate 4200F (FG-4200F) Kuwait
Kuwait organizations evaluating the FG-4200F may be looking for a high-capacity perimeter firewall, data-center segmentation platform or regional VPN hub. The same manufacturer specifications apply, but the project design should reflect the local network, carrier handoffs and operational policies. A useful discovery process records WAN speeds, internal uplink rates, expected encrypted inspection, public services, VPN counts and high-availability requirements. These details determine whether the platform’s 100GE, 40GE, 25GE and 10GE connectivity can be used effectively.
Data-center deployments should also consider change management. A high-end firewall often sits in the path of many critical applications, so migrations need application-owner participation and a rollback plan. Test not only internet browsing but inbound services, DNS, authentication, partner connections, monitoring, backups and inter-site applications. If security policies are being redesigned during migration, separate necessary cleanup from unrelated changes so troubleshooting remains manageable.
Organizations coordinating Kuwait and Tanzania infrastructure can use shared standards for firewall naming, policy structure, VPN encryption, logging and documentation. The FourTeck Kuwait regional site can be referenced for Kuwait requirements, while the Tanzania site remains the point for Tanzanian project planning. Quotations should list subscriptions, support, optics and services explicitly because the appliance alone does not define the complete security solution.
FortiGate 4200F (FG-4200F) Ghana
For Ghana, the FortiGate 4200F is relevant to large enterprises and network hubs that require substantial inspected throughput and high-speed interfaces. A security team should first establish the expected production traffic mix. IPS, application control, malware protection and SSL inspection consume different resources than basic stateful firewalling, so architecture decisions should use the vendor’s security-performance metrics and a growth margin appropriate to the organization. Session counts and connection rates can also matter for large public services or user populations.
High availability should be considered as a system property. Two firewall nodes are useful, but resilient design also considers upstream and downstream switching, power, WAN carriers and management access. For organizations with branches, test VPN failover and route convergence. If the 4200F will segment data-center networks, document allowed application flows before building policy so that security rules are understandable and auditable.
The FourTeck Ghana site can support regional technology coordination for Ghana-based requirements. Procurement teams comparing Ghana and Tanzania projects should keep commercial quotes separate but can standardize technical fields: appliance model, FortiGuard bundle, FortiCare term, optics, HA, migration, testing and documentation. This structure reduces the risk of comparing a hardware-only offer with a fully bundled security proposal.
FortiGate 4200F (FG-4200F) Nigeria
Nigeria’s large enterprise, financial, telecom and service-provider environments can generate the kind of traffic volumes that make high-end firewalls relevant. The FG-4200F should be evaluated using actual architecture data: internet capacity, data-center uplinks, public-service traffic, branch aggregation, VPN encryption and internal segmentation. Fortinet’s published 52 Gbps IPS, 47 Gbps NGFW and 45 Gbps threat-protection figures are particularly useful for security-service sizing because they are closer to an inspected workload than raw firewall throughput, though production results still depend on configuration and traffic.
A large Nigerian deployment may require multiple 100GE or 40GE links, making optics and switch compatibility an important procurement line item. Confirm transceiver type, fiber standard and distance rather than assuming all QSFP interfaces are interchangeable. The 3RU chassis also requires suitable rack space, airflow and redundant protected power. If deploying an HA pair, design the surrounding network to avoid single points of failure and document failover tests before acceptance.
For multi-country groups, the FourTeck Nigeria site can provide regional context while Tanzania requirements are handled through the Tanzania site. A strong quotation request should include desired security bundle and term, FortiCare, optics, migration scope and target implementation outcome. This is more useful than asking only for “FG-4200F price Nigeria,” because an enterprise firewall project is defined by the full licensed and connected solution.
FortiGate 4200F (FG-4200F) Seychelles
In Seychelles, the FG-4200F would normally suit a large centralized environment with substantial traffic rather than a typical office edge. Potential use cases include a major data center, large hospitality or financial group, service-provider environment or a central hub that aggregates multiple sites. Because high-end appliances carry significant capacity, sizing should confirm that the expected inspected throughput, session scale and interface requirements justify the model. Where a smaller appliance can meet the requirement with appropriate headroom, that may be the more efficient design.
Island connectivity and business-continuity planning can make WAN resilience especially important. If multiple circuits are available, the firewall design should define failover behavior and application priorities. Cloud services, voice, payment systems and remote management may have different tolerance for latency or circuit changes. Site-to-site VPNs should be tested under failure conditions, and external dependencies such as public DNS or IP allowlists should be included in continuity planning. A firewall cannot compensate for an untested upstream design.
Physical deployment requires the same discipline: suitable rack space for the 3RU appliance, controlled airflow, UPS-backed redundant power and correct optical components. Organizations coordinating Seychelles and Tanzania sites can standardize configuration principles, documentation and security policy while sizing each site separately. For quotation, provide interface speeds, WAN design, HA requirement, security services, contract term and migration needs so the proposed bill of materials reflects the complete operational requirement.
Selection, sizing and quotation checklist
Before requesting an FG-4200F quotation, collect the information below. It allows technical and procurement teams to compare the same scope and reduces later changes.
Frequently asked questions
What is the FortiGate 4200F designed for?
It is a high-end FortiGate platform suited to data centers, large enterprise edges, segmentation and high-capacity VPN or SD-WAN hub roles where substantial throughput and high-speed interfaces are required.
What are the published IPS, NGFW and threat-protection figures?
Fortinet’s current datasheet lists 52 Gbps IPS, 47 Gbps NGFW and 45 Gbps threat-protection throughput. These are vendor test results and actual production performance varies with configuration and traffic.
Does FG-4200F include local SSD storage?
Fortinet’s datasheet lists no onboard storage for FG-4200F. The related FG-4201F variant is listed with two 2 TB SSDs. Confirm the required model when ordering.
Should I buy hardware only or a FortiGuard bundle?
That depends on the security functions and support required. Ask for an itemized proposal showing hardware, FortiGuard services, FortiCare, term length, optics and implementation so the complete scope is visible.
Can the FG-4200F be deployed in high availability?
Yes. Fortinet lists active-active, active-passive and clustering configurations. The surrounding switches, WAN links and power should also be designed for resilience.
How do I request a FortiGate 4200F quote in Tanzania?
Provide bandwidth, interface speeds, HA requirement, VPN scale, desired security services and support term. Include existing firewall details if migration is required. This enables a more accurate bill of materials.
Decision recap
The FortiGate 4200F is a high-end firewall platform for environments that need substantial inspected throughput, very large session scale and dense high-speed connectivity. Its published capabilities are strong, but the purchasing decision should be based on the production traffic mix, security services, interface plan, VPN role, HA design and expected growth. The surrounding switching, fiber, power, cooling and management architecture should be treated as part of the firewall project.
Consultation panel
FourTeck Tanzania can use your topology, bandwidth requirements and security objectives to structure an FG-4200F bill of materials and deployment discussion. For multi-country requirements, the FourTeck network also includes FourTeck IT Solutions Africa, supporting a consistent regional technology conversation while each country’s scope remains specific to its network.




Reviews
There are no reviews yet.